Containers
Category: *Post Types
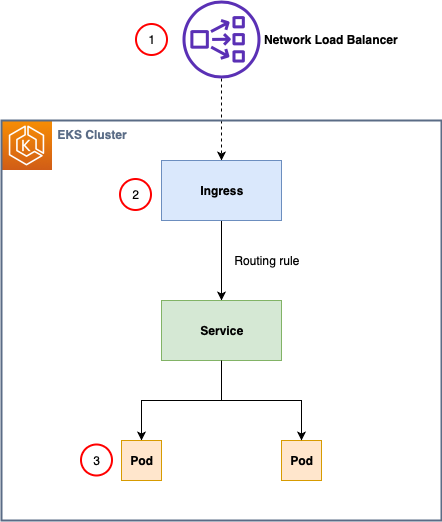
Setting up end-to-end TLS encryption on Amazon EKS with the new AWS Load Balancer Controller
In this blog post, I’ll show you how to set up end-to-end encryption on Amazon Elastic Kubernetes Service(Amazon EKS). End-to-end encryption in this case refers to traffic that originates from your client and terminates at an NGINX server running inside a sample app. I work with regulated customers who need to satisfy regulatory requirements like […]

Advertising click-prediction modeling on Amazon EKS
In digital advertising, the ad click-through rate (CTR) model predicts the probability of a click given the ads and context x (for example, shopping query, time of the day, device). The output of a CTR model can be seen as a conditional probability p(y = click|x). A precise estimation of this probability influences our ability […]

Amazon ECR’s credential helper now supports Amazon ECR Public
amazon-ecr-credential-helper is a credential helper for the Docker daemon that makes it easier to use Amazon Elastic Container Registry (ECR). Once configured, ECR credential helper automatically uses the same credentials as the AWS CLI and the AWS SDKs to first retrieve an ECR authentication token for secure access to repositories, then lets the Docker daemon […]

New look for Amazon ECS in the AWS Management Console
Recently we launched a new look and experience for Amazon ECS in the AWS Management Console. Since its launch in 2014, Amazon Elastic Container Service (Amazon ECS) has served as a simple way for customers to run production grade container workloads on AWS. Customers such as Disney+, Vanguard, Okta, Fidelity, and UbiSoft trust Amazon ECS […]
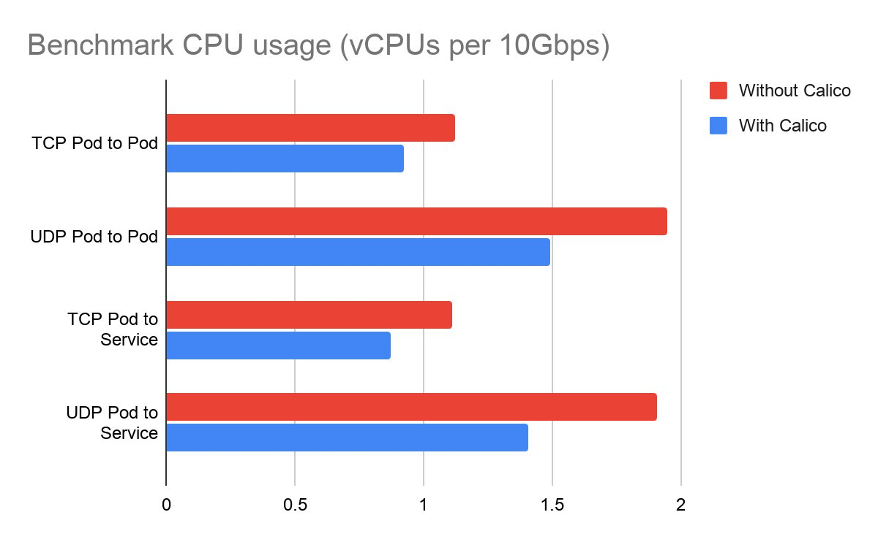
Turbocharging EKS networking with Bottlerocket, Calico, and eBPF
This post is co-authored by Alex Pollitt, Co-founder and CTO at Tigera, Inc. Recently Amazon announced support for Bottlerocket on Amazon Elastic Kubernetes Service (Amazon EKS). Bottlerocket is an open source Linux distribution built by Amazon to run containers focused on security, operations, and manageability at scale. You can learn more about Bottlerocket in this […]
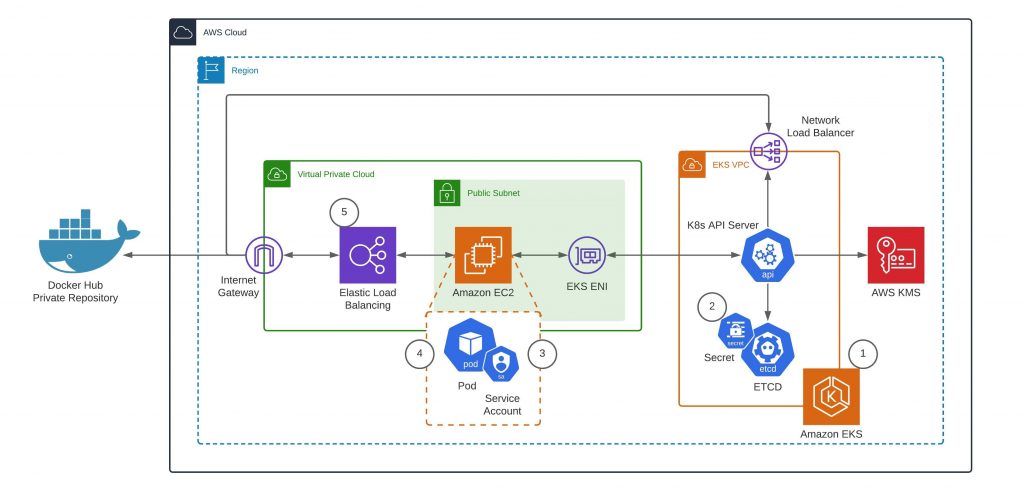
Authenticating with Docker Hub for AWS Container Services
Docker Hub has recently updated its terms of service to introduce rate limits for container image pulls. While these limits don’t apply to accounts under a Pro or Team plan, anonymous users are limited to 100 pulls per 6 hours per IP address, and authenticated free accounts are limited to 200 pulls per 6 hours. […]
Using EBS Snapshots for persistent storage with your EKS cluster
Originally, containers were a great fit for stateless applications. However, for many use cases there is a need for persistent storage, without which stateful workloads are not possible. Kubernetes first introduced support for stateful workloads with in-tree volume plugins, meaning that the plugin code was part of the core Kubernetes code and shipped with the […]

Latest updates to AWS Fargate for Amazon ECS
Recently, we announced features to improve the configuration and metric gathering experience of your tasks deployed via AWS Fargate for Amazon ECS. Based off of customer feedback, we added the following features: Environment file support Deeper integration with AWS Secrets Manager using secret versions and JSON keys More granular network metrics, as well as additional […]

Ship and visualize your Istio virtual service traces with AWS X-Ray
AWS X-Ray is a managed distributed tracing system that helps customers gain end-to-end visibility of requests and provides rich visualization of connected services. This post will show how customers can integrate AWS X-Ray as a backend for Zipkin traces generated from services in a Istio service mesh.

Introducing AWS Step Functions integration with Amazon EKS
This is my first post on AWS Container Blog since I joined AWS and I could not be more excited to talk about two technologies now working together: Serverless and Kubernetes, or more specifically AWS Step Functions and Amazon Elastic Kubernetes Service. In my previous role, I envisioned to build a web application that would […]