Containers
Category: Technical How-to

Introducing Amazon ECS Exec to access your Windows containers on Amazon EC2 and AWS Fargate
Today, we are launching the Amazon ECS Exec functionality for Amazon Elastic Container Service (Amazon ECS) customers running Windows containers on Amazon Elastic Compute Cloud (Amazon EC2), AWS Fargate or Amazon ECS Anywhere. This feature enables you to run commands in or get a shell to a container. In this blog post, we will walk […]

Amazon EBS CSI driver is now generally available in Amazon EKS add-ons
Introduction To provide workloads with optional persistent storage, Kubernetes implements volume lifecycle operations and supports various types of storage for use with these operations. Currently, storage provider–specific code is kept in the Kubernetes project source code, which is referred to as in-tree. This code is complex to maintain and release, and is tied to the […]

Managing Pod Scheduling Constraints and Groupless Node Upgrades with Karpenter in Amazon EKS
Feb 2024: This blog has been updated for Karpenter version v0.33.1 and v1beta1 specification. About Karpenter Karpenter is an open-source node lifecycle management project built for Kubernetes. It observes the aggregate resource requests of unschedulable pods and makes decisions to launch new nodes and terminate them to reduce scheduling latencies and infrastructure costs sending commands to […]
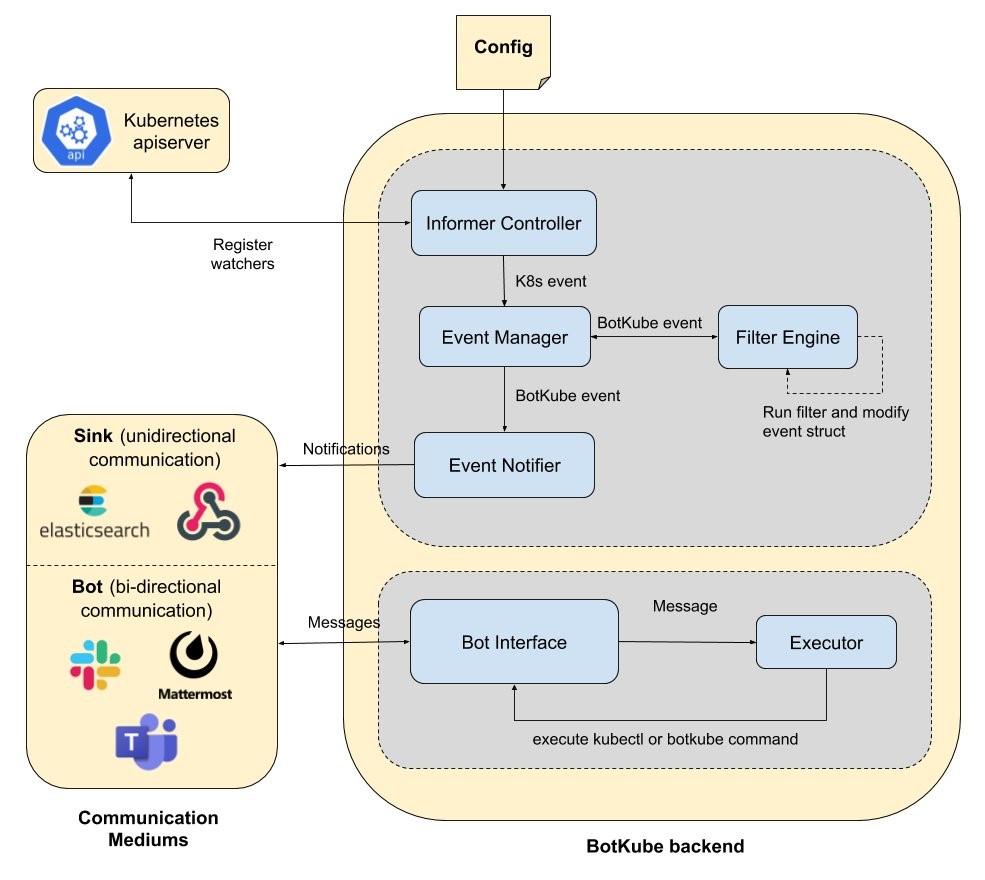
Streaming Kubernetes Events in Slack
IT operations teams know that detecting an issue early on can help them avert downtime and cascading failures. Many teams stay on top of infrastructure events by using built-in alert management capabilities in monitoring tools such as Prometheus and Amazon CloudWatch. However, these alert rules are configured centrally in monitoring tools, and engineers often receive […]
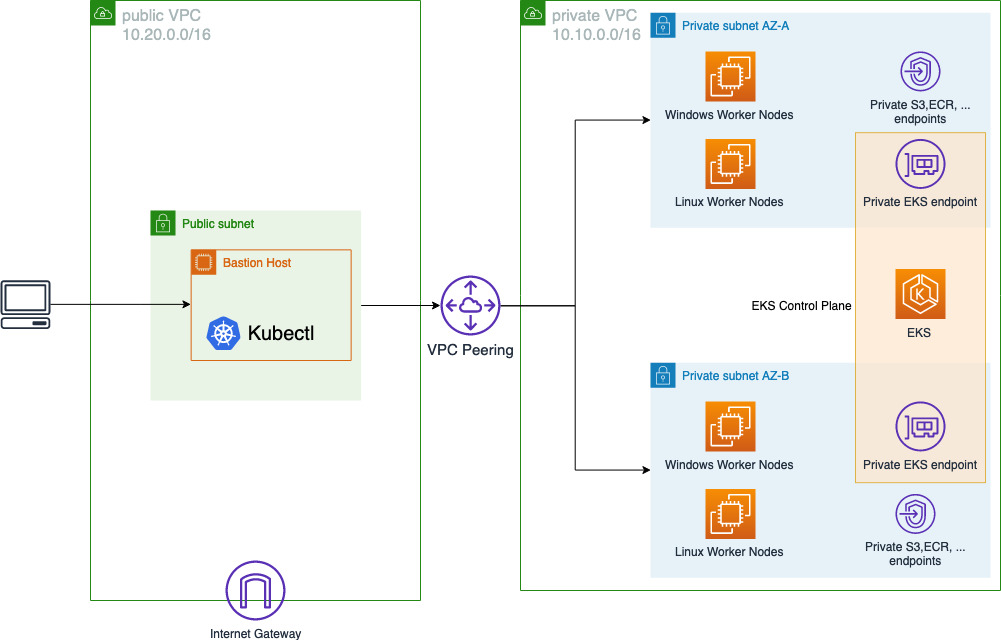
Running Windows workloads on a private EKS cluster
Legacy applications in the automotive industry tend to run on Windows. Customers want to scale these workloads on Kubernetes alongside their Linux workloads. The automotive industry has a particularly high standard on security, and an Amazon Elastic Kubernetes Service (Amazon EKS) cluster with private endpoint is applicable to run their workloads. This blog post shows […]

How to route UDP traffic into Kubernetes
Since its release, Amazon Elastic Kubernetes Service (Amazon EKS) has been helping customers to run their applications reliably and at scale. UDP, or User Datagram Protocol, is a low-latency protocol that is ideal for workloads such as real-time streaming, online gaming, and IoT. The Network Load Balancer (NLB) is designed to handle tens of millions […]

How To Expose Multiple Applications on Amazon EKS Using a Single Application Load Balancer
Introduction Microservices architectures are default for cloud-native applications. Greater granular scalability, isolation of functions, and the possibility of having independent teams working on specific application functionalities are just some of the reasons that such an architectural pattern has been widely adopted. Together with the fact that new applications are being borne in the cloud, you […]

Deploy Python Application using AWS App Runner
It takes a village to design, develop, and host an application. It all starts with a business use case that gets translated to requirements and design and is then handed over to the developers for development. The developers create the application, test it in their local environments, and hand it over to the operations team […]

Continuous Delivery of Amazon EKS Clusters Using AWS CDK and CDK Pipelines
This blog is no longer up to date and we recommend reviewing the Amazon EKS Blueprints for CDK Pipeline SDK module which makes it easier to create infrastructure Continuous Delivery pipelines via AWS CodePipeline. Customers are looking for ways to automate the deployment of their Amazon EKS clusters across different versions, environments, accounts, and Regions. […]

Protect Kubernetes workloads from Apache Log4j vulnerabilities
Log4j is among the most popular and highly used logging frameworks in Java-based applications. On December 9, 2021, the world became aware of zero-day vulnerabilities CVE-2021-44228 and CVE-2021-45105 affecting the popular Apache package. Any attacker who can control log messages or log message parameters can execute arbitrary code loaded from malicious LDAP servers when message […]