Containers

Author: Michael Hausenblas
Michael works in the AWS open source observability service team where he is a Solution Engineering Lead and owns the AWS Distro for OpenTelemetry (ADOT) from the product side.

Results of the 2019 AWS Container Security Survey
Security is a top priority in AWS, and in our service team we naturally focus on container security. In order to better assess where we stand, we conducted an anonymous survey in late 2019 amongst container users on AWS. Overall, we got 68 responses from a variety of roles, from ops folks and SREs to […]

Securing EKS Ingress With Contour And Let’s Encrypt The GitOps Way
This is a guest post by Stefan Prodan of Weaveworks. In Kubernetes terminology, Ingress exposes HTTP(S) routes from outside the cluster to services running within the cluster. An Ingress can be configured to provide Kubernetes services with externally-reachable URLs while performing load balancing and SSL/TLS termination. Kubernetes comes with an Ingress resource and there are several controllers that […]

Autoscaling EKS on Fargate with custom metrics
NOTICE: October 04, 2024 – This post no longer reflects the best guidance for configuring a service mesh with Amazon EKS and its examples no longer work as shown. Please refer to newer content on Amazon VPC Lattice. ——– This is a guest post by Stefan Prodan of Weaveworks. Autoscaling is an approach to automatically scale […]
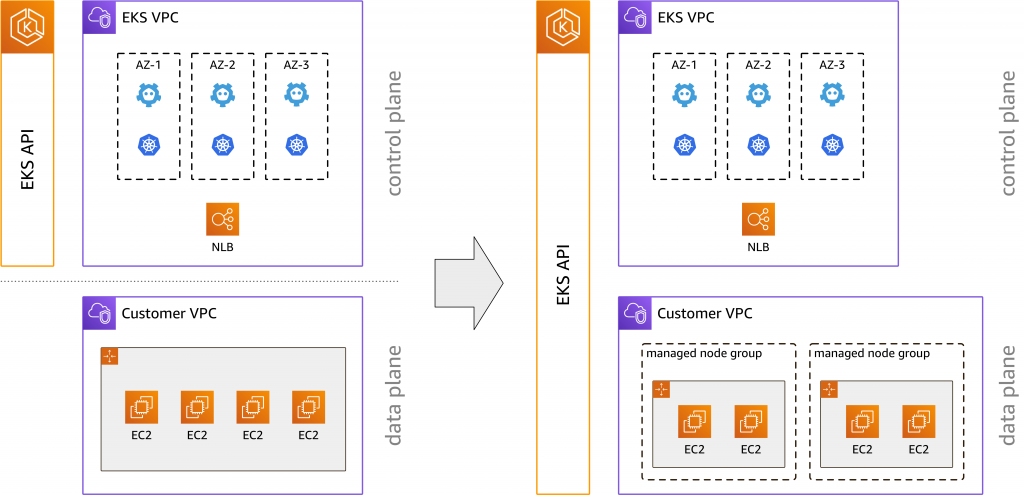
Extending the EKS API: Managed Node Groups
By Raghav Tripathi, Michael Hausenblas, and Nathan Taber From our first conversations with customers, our vision has always been that Amazon Elastic Kubernetes Service (EKS) should provide the best managed Kubernetes experience in the cloud. When we launched EKS, our first step was to provide a managed Kubernetes control plane, but we never intended to stop […]

Native Container Image Scanning in Amazon ECR
By Richard Nguyen and Michael Hausenblas Container security comprises a range of activities and tools, involving developers, security operations engineers, and infrastructure admins. One crucial part in the cloud native supply chain is to scan container images for vulnerabilities and being able to get actionable insights from it. We learned in Issue 17 of the […]