Containers

Author: Paavan Mistry
Paavan is a Senior Manager leading AI Security and Compliance Initiatives at AWS, with over 10 years of experience driving enterprise-scale security solutions in cloud and AI environments. He has built and scaled high-performing teams across Developer Advocacy, Solutions Architecture, and Security Engineering, delivering critical AI safety frameworks and compliance programs that protect millions of AWS customers. His expertise spans AI threat modeling, ML security architecture, and regulatory compliance for emerging AI technologies. Paavan combines deep technical knowledge with strategic leadership, having partnered with C-suite executives to shape AWS's AI security roadmap and governance standards. Connect with him on Twitter [@98pm] and GitHub [@paavan98pm].

Introducing Kubernetes Resource View in Amazon EKS console
Amazon Elastic Kubernetes Service (Amazon EKS) is excited to introduce the Kubernetes resource view. You will now be able to see all Kubernetes API resource types running in your Amazon EKS cluster using the AWS Management Console for Amazon EKS, making it easier to visualize and troubleshoot your Kubernetes applications using Amazon EKS. Amazon EKS […]

Introducing The CIS Amazon EKS Benchmark
Today, we’re announcing a new Center for Internet Security (CIS) benchmark for Amazon Elastic Kubernetes Service (EKS). This new benchmark is optimized to help you accurately assess the security configuration of Amazon EKS clusters, including security assessments for nodes to help meet security and compliance requirements. Security is a critical consideration when configuring and maintaining […]

Introducing server-side encryption of ephemeral storage using AWS Fargate-managed keys in AWS Fargate platform version 1.4
This post was contributed by Yuling Zhou, Eduardo Lopez Biagi, and Paavan Mistry. Today, we introduced server-side encryption of ephemeral storage in AWS Fargate platform version 1.4. The ephemeral task storage is automatically encrypted with industry-standard AES-256 encryption algorithm using AWS Fargate-managed keys for the updated platform version. This feature requires no additional configuration from […]
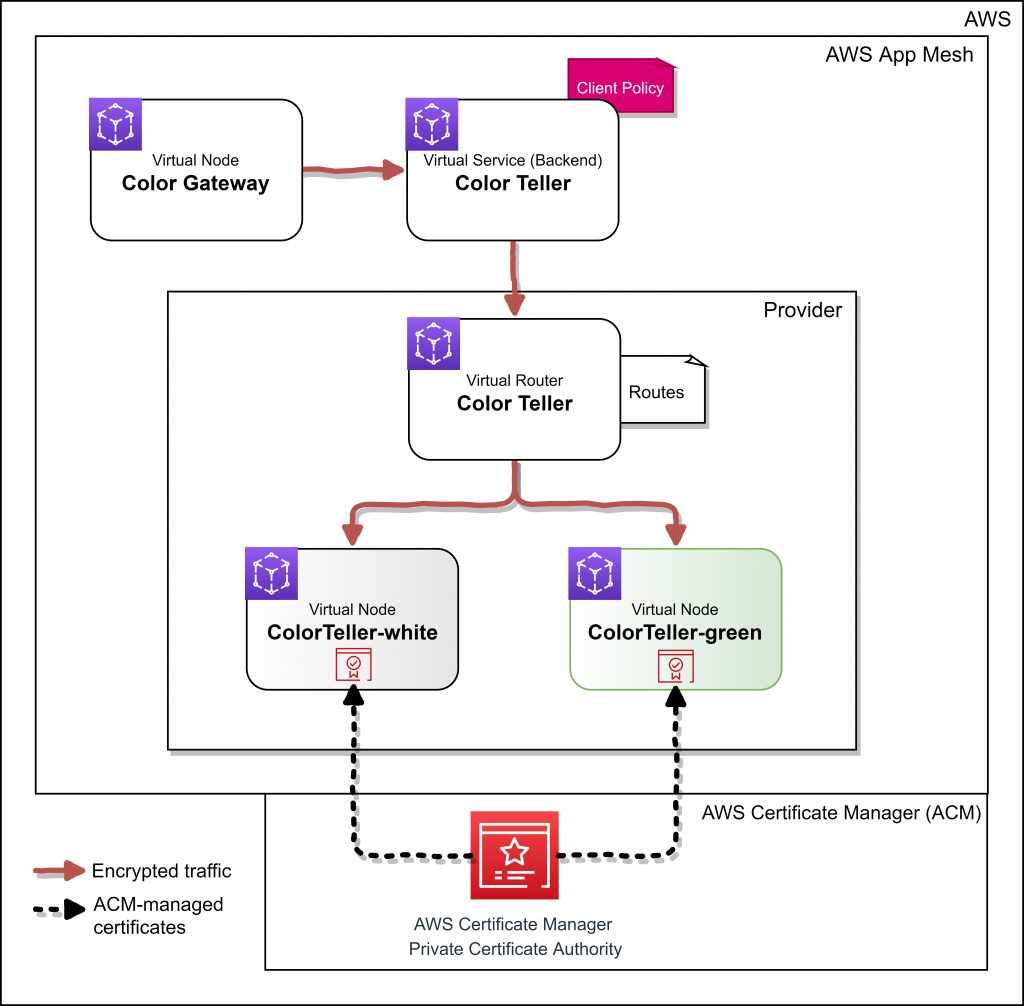
Enable traffic encryption between services in AWS App Mesh using AWS Certificate Manager or customer-provided certificates
NOTICE: October 04, 2024 – This post no longer reflects the best guidance for configuring a service mesh with Amazon ECS and Amazon EKS, and its examples no longer work as shown. For workloads running on Amazon ECS, please refer to newer content on Amazon ECS Service Connect, and for workloads running on Amazon EKS, […]