Networking & Content Delivery

Author: Jake Wells
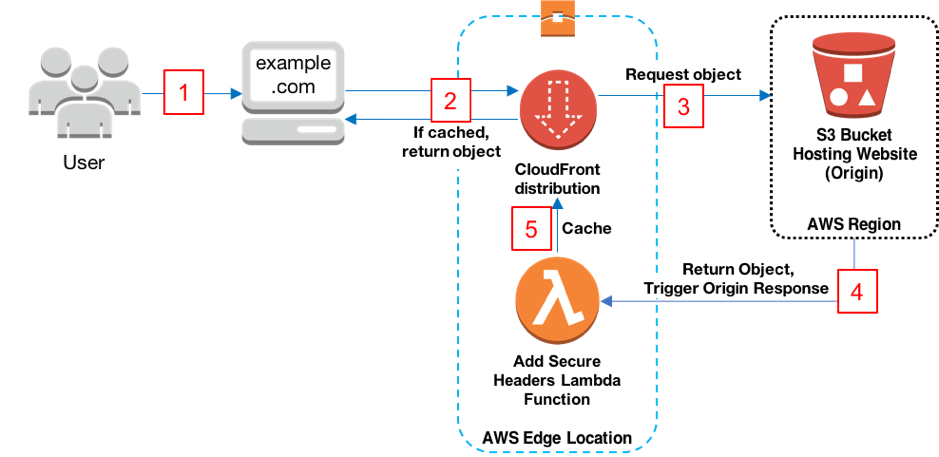
Adding HTTP Security Headers Using Lambda@Edge and Amazon CloudFront
Adding security response headers is often achievable by modifications to your application configuration. In this blog we will focus on how to achieve the same result when you have an application that can’t be modified at the origin (e.g., a web site hosted in Amazon S3).

Dynamically Route Viewer Requests to Any Origin Using Lambda@Edge
Today Lambda@Edge announces a new feature that allows you to do content-based routing. Now you can programmatically define the origin based on logic in your Lambda function. This enables you to route requests to different origins based on request attributes such as headers, query strings, and cookies. Read our blog post to learn about different use cases and how you can set this up within your own architecture.