AWS Security Blog
Category: Security, Identity, & Compliance

Best practices for cross-Region aggregation of security findings
AWS Security Hub enables customers to have a centralized view into the security posture across their AWS environment by aggregating your security alerts from various AWS services and partner products in a standardized format so that you can more easily take action on them. To facilitate that central view, Security Hub allows you to designate […]

Continuous compliance monitoring using custom audit controls and frameworks with AWS Audit Manager
French version For most customers today, security compliance auditing can be a very cumbersome and costly process. This activity within a security program often comes with a dependency on third party audit firms and robust security teams, to periodically assess risk and raise compliance gaps aligned with applicable industry requirements. Due to the nature of […]
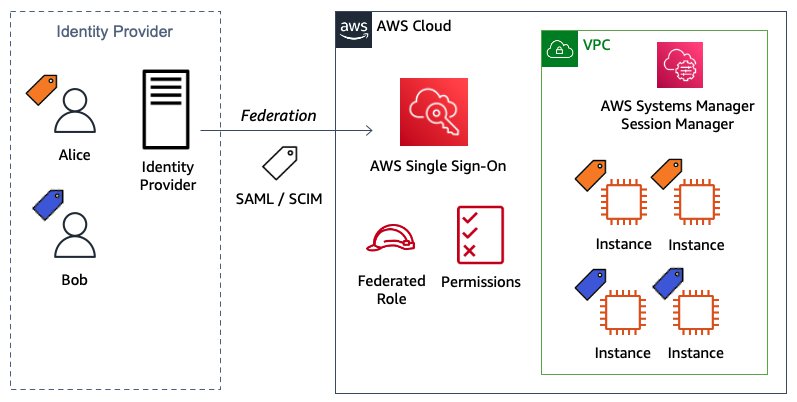
Configure AWS IAM Identity Center ABAC for EC2 instances and Systems Manager Session Manager
September 12, 2022: This blog post has been updated to reflect the new name of AWS Single Sign-On (SSO) – AWS IAM Identity Center. Read more about the name change here. In this blog post, I show you how to configure AWS IAM Identity Center to define attribute-based access control (ABAC) permissions to manage Amazon […]

Using AWS security services to protect against, detect, and respond to the Log4j vulnerability
April 21, 2022: The blog post has been updated to include information on the updated version of the hotpatch. See this security advisory for more details. Overview In this post we will provide guidance to help customers who are responding to the recently disclosed log4j vulnerability. This covers what you can do to limit the […]
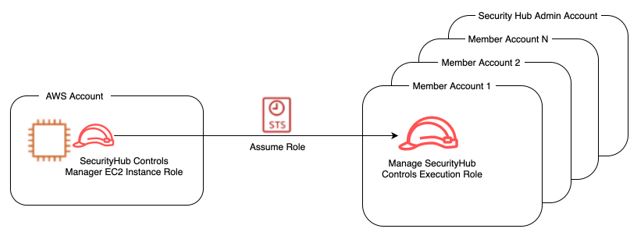
Disabling Security Hub controls in a multi-account environment
February 28, 2024: Security Hub now supports central configuration for security standards and controls across accounts. This new feature addresses many of the scenarios that are covered by the scripts in this blog post, reducing or eliminating the need to run these scripts. Before you use the scripts in this post, see Central configuration in […]

Automatically resolve Security Hub findings for resources that no longer exist
In this post, you’ll learn how to automatically resolve AWS Security Hub findings for previously deleted Amazon Web Services (AWS) resources. By using an event-driven solution, you can automatically resolve findings for AWS and third-party service integrations. Security Hub provides a comprehensive view of your security alerts and security posture across your AWS accounts. Security […]
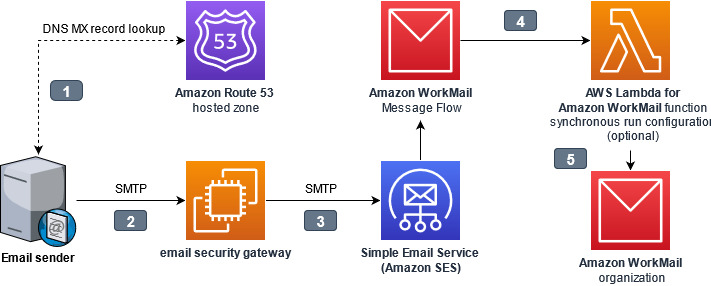
How to configure an incoming email security gateway with Amazon WorkMail
April 25, 2023: We’ve updated this blog post to include more security learning resources. This blog post will walk you through the steps needed to integrate Amazon WorkMail with an email security gateway. Configuring WorkMail this way can provide a versatile defense strategy for inbound email threats. Amazon WorkMail is a secure, managed business email […]

Simplify setup of Amazon Detective with AWS Organizations
Amazon Detective makes it easy to analyze, investigate, and quickly identify the root cause of potential security issues or suspicious activities by collecting log data from your AWS resources. Amazon Detective simplifies the process of a deep dive into a security finding from other AWS security services, such as Amazon GuardDuty and AWS SecurityHub. Detective […]
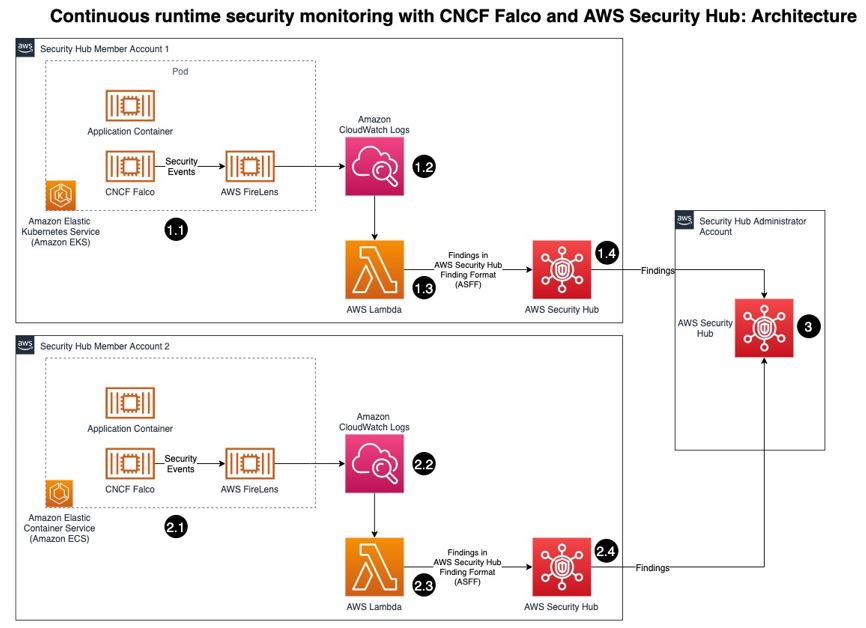
Continuous runtime security monitoring with AWS Security Hub and Falco
Customers want a single and comprehensive view of the security posture of their workloads. Runtime security event monitoring is important to building secure, operationally excellent, and reliable workloads, especially in environments that run containers and container orchestration platforms. In this blog post, we show you how to use services such as AWS Security Hub and […]

How to customize behavior of AWS Managed Rules for AWS WAF
AWS Managed Rules for AWS WAF provides a group of rules created by AWS that can be used help protect you against common application vulnerabilities and other unwanted access to your systems without having to write your own rules. AWS Threat Research Team updates AWS Managed Rules to respond to an ever-changing threat landscape in order […]