AWS Thai Blog
Secure your AI AgentCore with Dogwood Policy
จาก Cedar สู่ Dogwood: เพิ่ม Temporal Policy เพิ่มการควบคุม AI Agent ให้ปลอดภัยได้ดีกว่าเดิม
Cedar คืออะไร?
Cedar เป็น open-source policy language ที่ AWS พัฒนาขึ้นสำหรับเขียน authorization policy ใช้งานจริงใน Amazon Verified Permissions และ Amazon Bedrock AgentCore Policy โดย Cedar มีจุดเด่นคือ อ่านง่ายเหมือนภาษาอังกฤษ, วิเคราะห์ คล้ายใกล้เคียงกับ IAM Policy
ตัวอย่างการใช้งาน Cedar สามารถดูได้จากบทความก่อนหน้านี้ AgentCore Policy Link ของ คุณ Sithimai
แต่เมื่อ AI Agent เริ่มทำงานเป็น ลำดับขั้นตอน (sequence) หลาย tool call ต่อเนื่องกัน สิ่งที่ Cedar ทำไม่ได้คือ “มองย้อนกลับไปว่า agent เคยทำอะไรมาก่อนหน้าบ้าง” (เช่น Stateful (จำสถานะ) มีการบันทึก Log และวิเคราะห์ประวัติการทำงานย้อนหลัง)
Dogwood คืออะไร? Dogwood คืออะไร แตกต่างจาก Cedar ยังไง
Dogwood คือ governance language ที่สร้างขึ้นเพื่อควบคุม AI Agent โดยเฉพาะ เปิดตัวเมื่อสิงหาคม 2026 ภายใต้ Apache 2.0 license โดยทีม AWS ที่นำโดย Marc Brooker (VP & Distinguished Engineer) Dogwood (Stateful) สร้างต่อยอดจาก Cedar (Stateless) โดยเพิ่มความสามารถด้าน temporal condition ซึ่งสามารถ “จำสถานะ” ไปดู event ที่เกิดขึ้นก่อนหน้าได้ ทำให้สามารถเขียน policy ที่ควบคุมได้ว่า agent ต้องทำอะไรก่อน, ห้ามทำอะไรหลังจากทำบางอย่าง, หรือจำกัดจำนวนครั้งที่ทำได้ในช่วงเวลาหนึ่ง
สิ่งสำคัญ: Cedar policy เดิมสามารถใช้งานบน Dogwood ได้เลย โดยไม่ต้อง migration
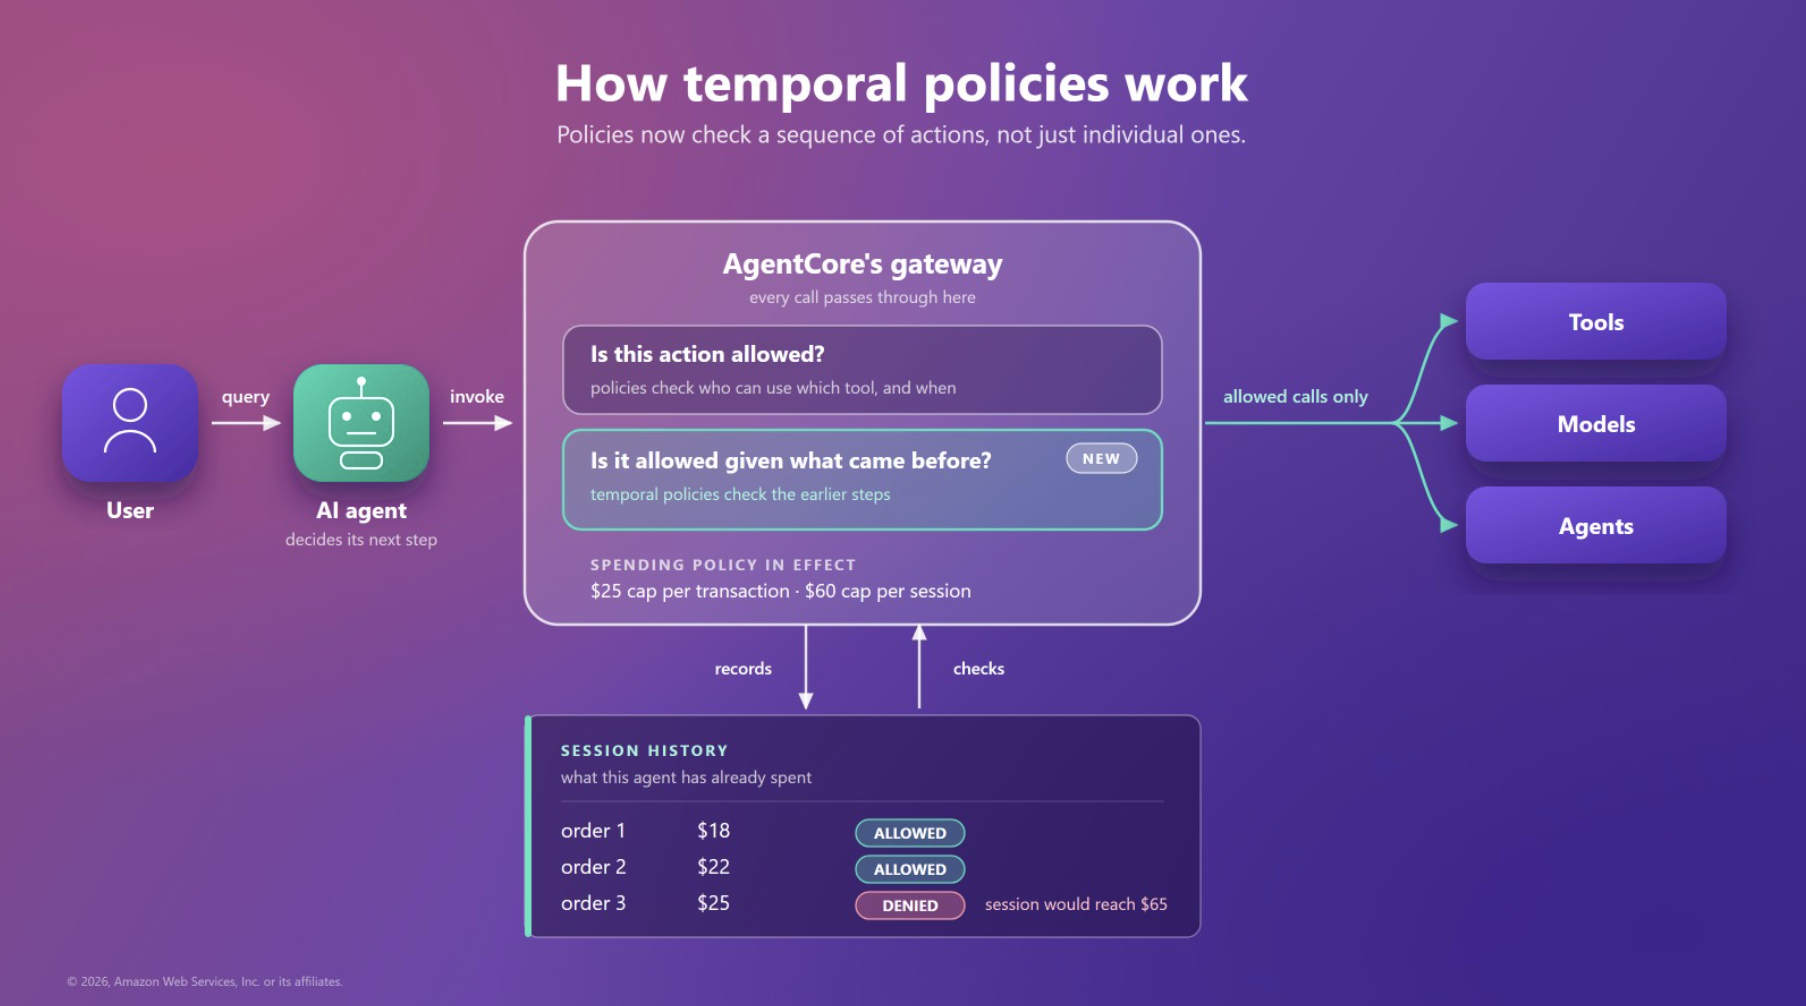
Dogwood ทำอะไรได้บ้าง? (ตัวอย่าง Temporal Operators)
Dogwood เพิ่ม clause ใหม่คือ when temporal { … } ที่สามารถอ้างอิง event ในอดีตได้ โดยมี operator หลักๆ ดังนี้
1. formerly — “เคยเกิดขึ้นมาก่อนไหม?”
ใช้ตรวจสอบว่ามี event บางอย่างเกิดขึ้นใน time window ที่กำหนด เช่น ต้องได้ approval ก่อนจึงจะขายหุ้นได้
permit ( principal, action == AgentCore::Action::"SellShares", resource )
when temporal {
    formerly within 1h AgentCore::Action::"ApproveSale"::response{
        input.stock:     context.input.stock,
        input.shares:    context.input.shares,
        output.approved: true
    }
};
Policy นี้หมายความว่า: “อนุญาตให้ขายหุ้นได้ ก็ต่อเมื่อมีการ approve สำหรับหุ้นตัวเดียวกันและจำนวนเท่ากัน ภายใน 1 ชั่วโมงที่ผ่านมา”
2. count_within — “เกิดขึ้นกี่ครั้งแล้ว?”
จำกัดจำนวนครั้งของ action ใน time window เช่น ห้ามโอนเกิน 5 ครั้งใน 1 ชั่วโมง
forbid ( principal, action == AgentCore::Action::"Transfer", resource )
when temporal {
    count_within(1h, AgentCore::Action::"Transfer"::request{ input.amount: _ }) > 5
};
3. sum_within — “รวมแล้วเกินไหม?”
จำกัดยอดรวมของ action เช่น ห้ามโอนเงินรวมเกิน $5,000 ใน 1 ชั่วโมง
forbid ( principal, action == AgentCore::Action::"Transfer", resource )
when temporal {
    sum_within(a, 1h, AgentCore::Action::"Transfer"::request{ input.amount: a }) > 5000
};
4. count_distinct_within — “กี่รายการที่ไม่ซ้ำกัน?”
จำกัดจำนวนค่าที่ไม่ซ้ำกัน เช่น ห้ามโอนเงินให้เกิน 3 คนที่แตกต่างกันใน 1 ชั่วโมง
นอกจากนี้ยังสามารถ ผสม Cedar condition กับ temporal condition ในตัวเดียวกันได้ เช่น “ขายหุ้นได้ก็ต่อเมื่อจำนวนไม่เกิน 100 หุ้น และ ได้ approval มาแล้วภายใน 1 ชั่วโมง”
การใช้งาน Dogwood มี 2 ช่องทาง
1.ใช้ผ่าน Amazon Bedrock AgentCore Policy — หากคุณใช้ AgentCore อยู่แล้ว สามารถเพิ่ม Dogwood temporal policy เข้าไปได้เลย โดย Cedar policy เดิมยังทำงานได้ตามปกติ ไม่ต้อง migrate
2.ใช้ผ่าน open source — Dogwood เปิดให้ใช้งานบน GitHub (github.com/dogwood-policy/dogwood) ภายใต้ Apache 2.0 พร้อม parser, validator, และ reference interpreter สำหรับทดสอบ policy ก่อน deploy
Reference:
Introducing Dogwood: runtime verification for AI agents: Link
Control agent behaviors and cost beyond a single action: new capabilities in Amazon Bedrock AgentCore: Link
Authoring Dogwood policies from natural language in Amazon Bedrock AgentCore: Link
AWS launches Dogwood, a temporal policy language for AI agent authorization, integrated into Amazon Bedrock AgentCore: Link
Secure Your AI Agents on AWS (Part 1): Inputs, Identity, and Human Oversight: Link
AWS Workshop-Cedar policy language in action: Link
Cedar Playground: Link