AWS Security Blog

AWS CSA Consensus Assessment Initiative Questionnaire version 4 now available
Amazon Web Services (AWS) has published an updated version of the AWS Cloud Security Alliance (CSA) Consensus Assessment Initiative Questionnaire (CAIQ). The questionnaire has been completed using the current CSA CAIQ standard, v4.0.2 (06.07.2021 update), and is now available for download. The CSA is a not-for-profit organization dedicated to “defining and raising awareness of best […]
AWS Security Profile: CJ Moses, CISO of AWS
In the AWS Security Profile series, I interview the people who work in Amazon Web Services (AWS) Security and help keep our customers safe and secure. This interview is with CJ Moses—previously the AWS Deputy Chief Information Security Officer (CISO), he began his role as CISO of AWS in February of 2022. How did you […]

When and where to use IAM permissions boundaries
Customers often ask for guidance on permissions boundaries in AWS Identity and Access Management (IAM) and when, where, and how to use them. A permissions boundary is an IAM feature that helps your centralized cloud IAM teams to safely empower your application developers to create new IAM roles and policies in Amazon Web Services (AWS). […]
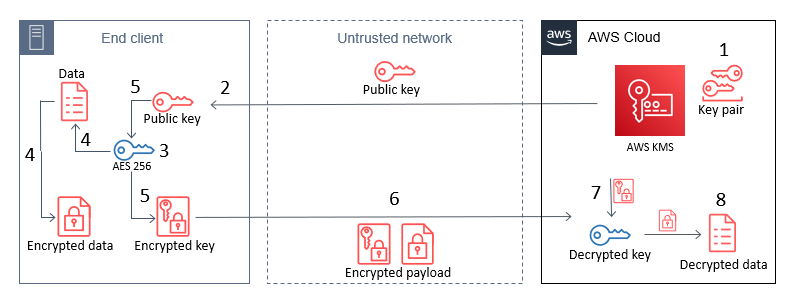
How to use AWS KMS RSA keys for offline encryption
October 28, 2022: This blog post has been updated to reflect that CBC has changed to CTR, as well as a few more modifications. This blog post discusses how you can use AWS Key Management Service (AWS KMS) RSA public keys on end clients or devices and encrypt data, then subsequently decrypt data by using […]

How to use regional SAML endpoints for failover
August 10, 2022: This blog post has been updated to reflect the new name of AWS Single Sign-On (SSO) – AWS IAM Identity Center. Read more about the name change here. Many Amazon Web Services (AWS) customers choose to use federation with SAML 2.0 in order to use their existing identity provider (IdP) and avoid […]

Choosing the right certificate revocation method in AWS Private CA
June 25, 2025: As of Sept 28, 2022, AWS has changed the name of ACM Private CA to AWS Private CA. This post has been updated to reflect this change. AWS Private Certificate Authority (AWS Private CA) is a highly available, fully managed private certificate authority (CA) service that allows you to create CA hierarchies […]

Build a strong identity foundation that uses your existing on-premises Active Directory
September 12, 2022: This blog post has been updated to reflect the new name of AWS Single Sign-On (SSO) – AWS IAM Identity Center. Read more about the name change here. This blog post outlines how to use your existing Microsoft Active Directory (AD) to reliably authenticate access to your Amazon Web Services (AWS) accounts, […]

Getting started with AWS IAM Identity Center delegated administration
April 24, 2026: We’ve updated this post to reflect the guidance on managing access to the AWS Organizations management account. September 12, 2022: This blog post has been updated to reflect the new name of AWS Single Sign-On (SSO) – AWS IAM Identity Center. Read more about the name change here. AWS launched the ability […]
Establishing a data perimeter on AWS: Overview
August 28, 2025: This post has been updated to reflect the usage of the aws:VpceOrgID condition key to scale your network perimeter implementation. November 13, 2024: This post has been updated with guidance on how to use resource control policies (RCPs) and the aws:SourceOrgID condition key to establish your organization’s data perimeter. November 23, 2022: […]
How to use new Amazon GuardDuty EKS Protection findings
If you run container workloads that use Amazon Elastic Kubernetes Service (Amazon EKS), Amazon GuardDuty now has added support that will help you better protect these workloads from potential threats. Amazon GuardDuty EKS Protection can help detect threats related to user and application activity that is captured in Kubernetes audit logs. Newly-added Kubernetes threat detections […]