AWS Quick: AI you can trust on the security foundation you already have
With AWS Quick, govern what AI can do before it reaches your users, keep your data in your environment, and scale with the security and compliance controls you already use.
Enterprise trust isn't bolted on, it's where Quick starts
Built-in controls for identity, data, network, and AI help you govern what AI can do, protect your data, and scale on the security you already trust.
Govern what AI can do before it reaches your users
- Deny by default: New AI capabilities ship in a restricted state until administrators enable them.
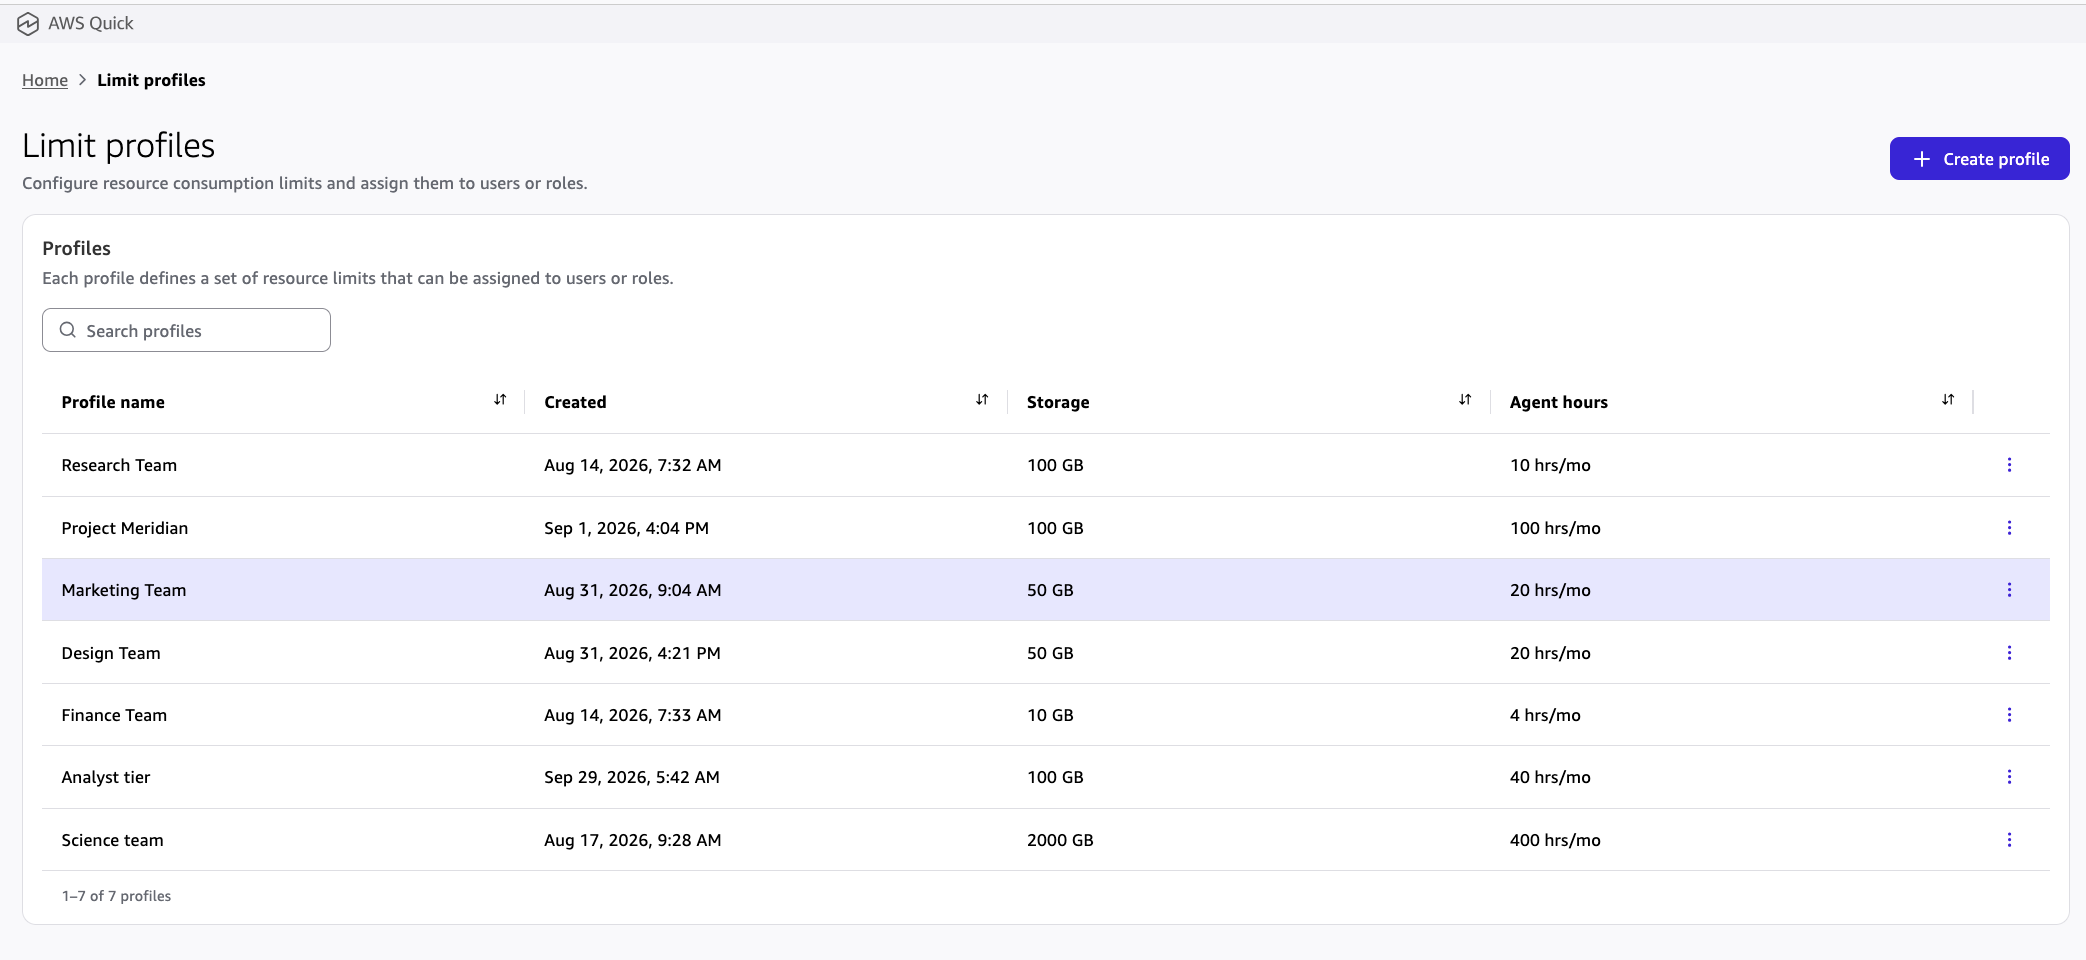
- Custom permissions: Assign profiles at the user, role, or account level.
- Approval workflows: Designated approvers sign off before knowledge bases, spaces, agents, or flows are shared.
- Connector controls: Choose which connectors are enabled, how they authenticate, and who can use them.
Protect your data with layered controls
- AWS does not use your data to train models in any AWS Quick plan.
- AWS Quick enforces your existing access permissions at query time.
- Microsoft Purview sensitivity labels are checked before content enters AWS Quick.
- AES-256 encryption at rest, TLS in transit, and customer-managed AWS KMS keys
- AWS PrivateLink keeps sensitive data off the public internet.
Scale on the security you already trust
- Run regulated workloads in AWS GovCloud (US-West), an isolated, FedRAMP-authorized environment that supports DoD SRG Impact Levels 4 and 5, ITAR, CJIS, and FIPS 140-3.
- Choose your AWS Region at account creation, and your data is stored and processed in that Region.
- Every sign-in, sharing action, and approval is recorded in AWS CloudTrail.
- Permissions in AWS Lake Formation and IAM are enforced automatically.
- No separate identity system: Connect the identity provider you already use.
New AI capabilities are available at your own pace
With deny by default, new AI capabilities ship in a restricted state. Test them before launch, follow your internal approval process, and prepare your users before rollout. Every enablement decision is captured in AWS CloudTrail.
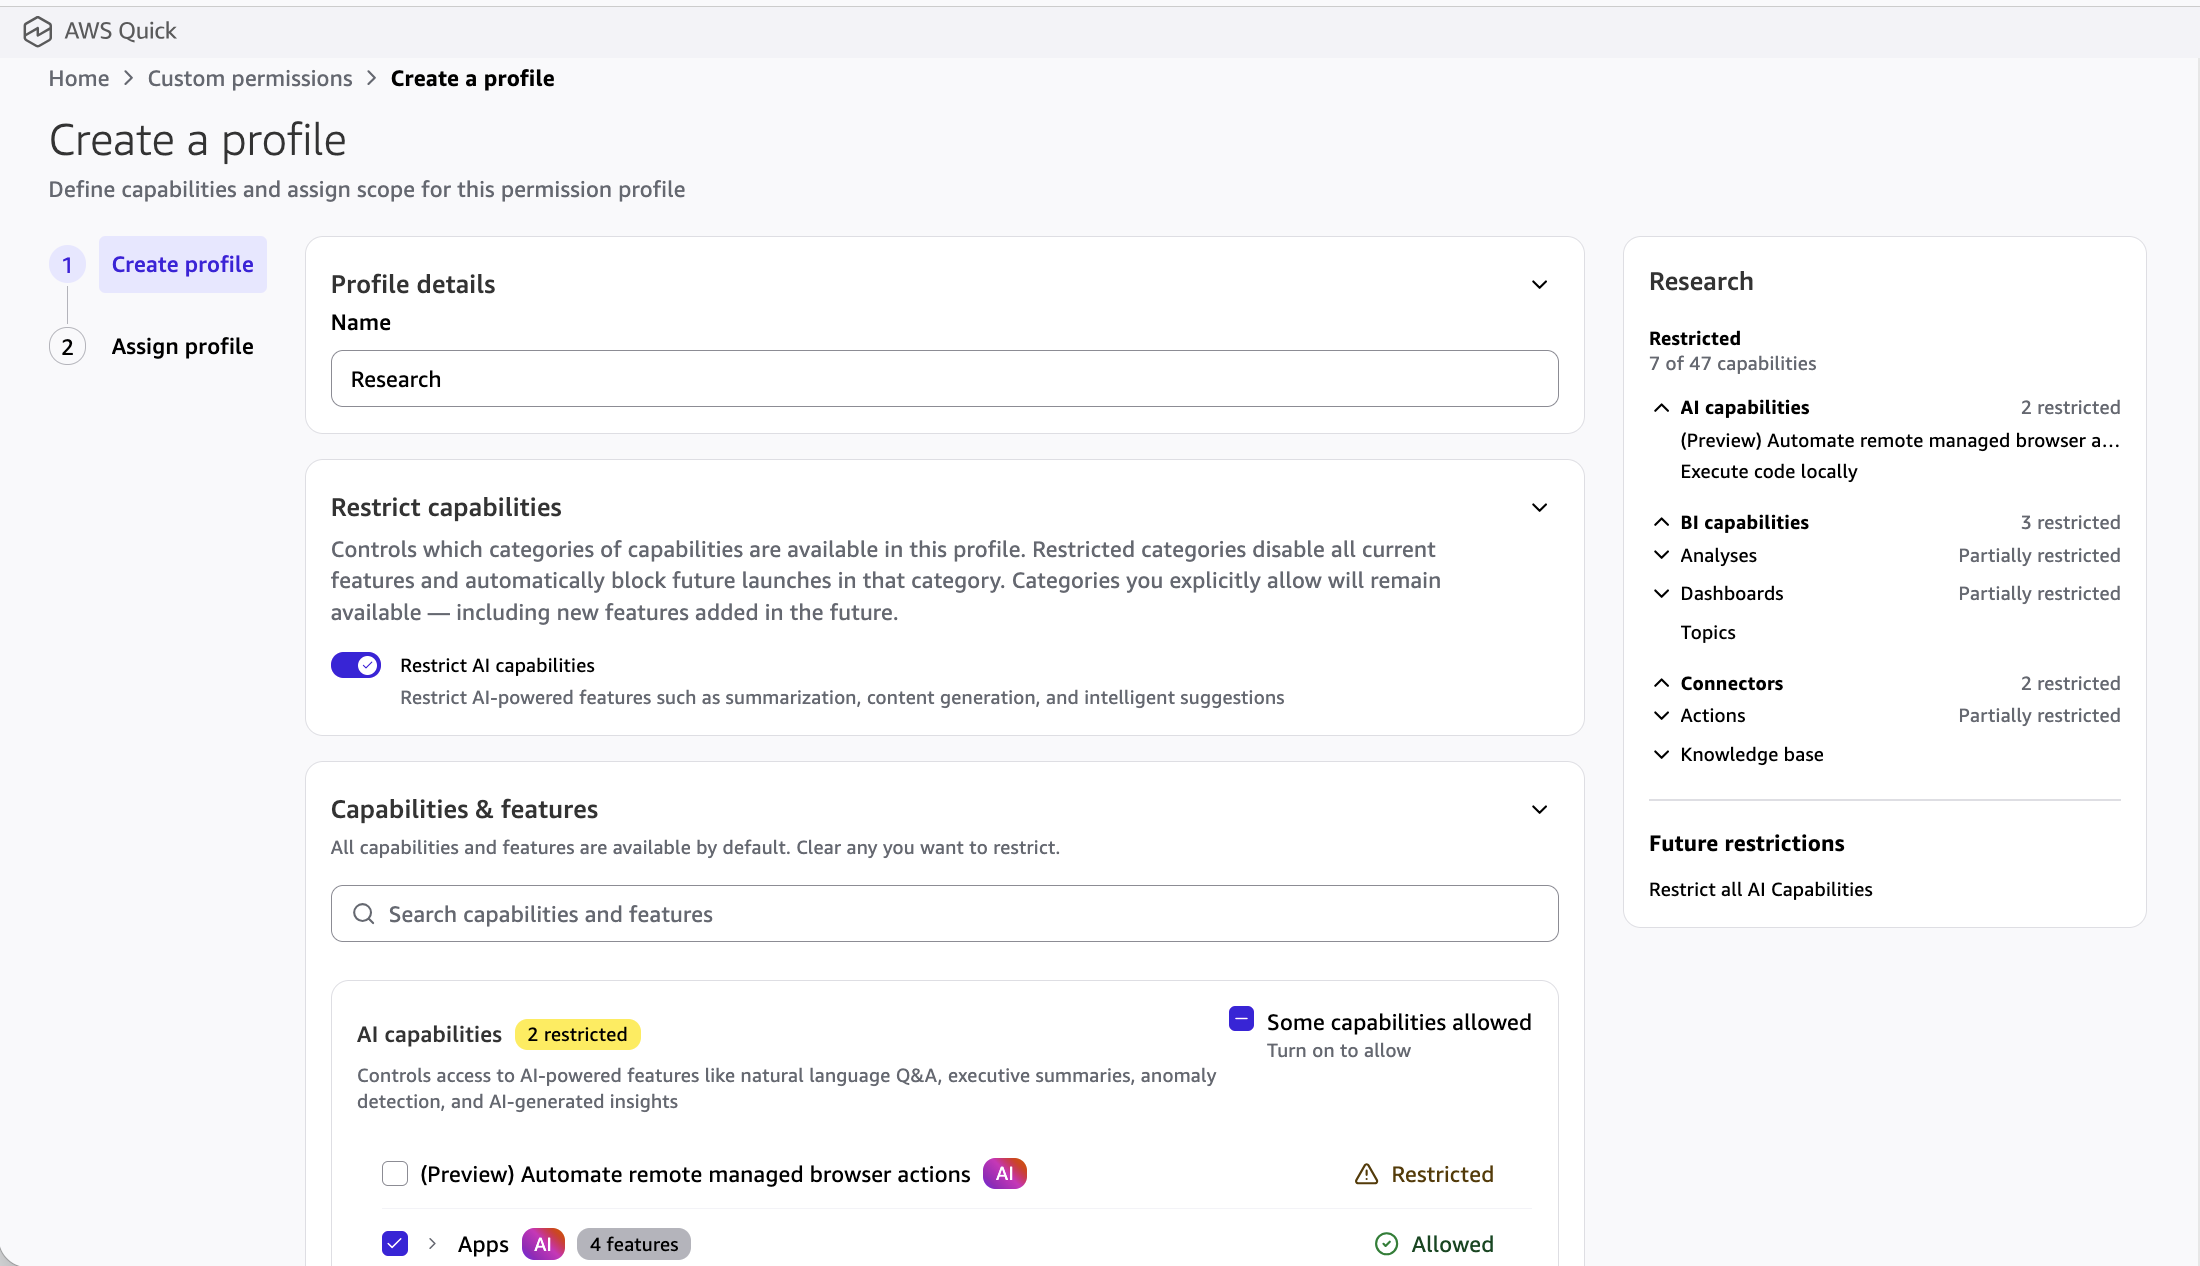
Extend your Microsoft Purview policies to AWS Quick
AWS Quick is integrated with Microsoft Purview, so the sensitivity labels you already use are enforced across Quick chat, spaces, and knowledge bases. Labels are checked at upload or indexing, before content enters AWS Quick. Sensitive content is blocked, not just flagged, and confidential content can be allowed with a warning and an audit trail.
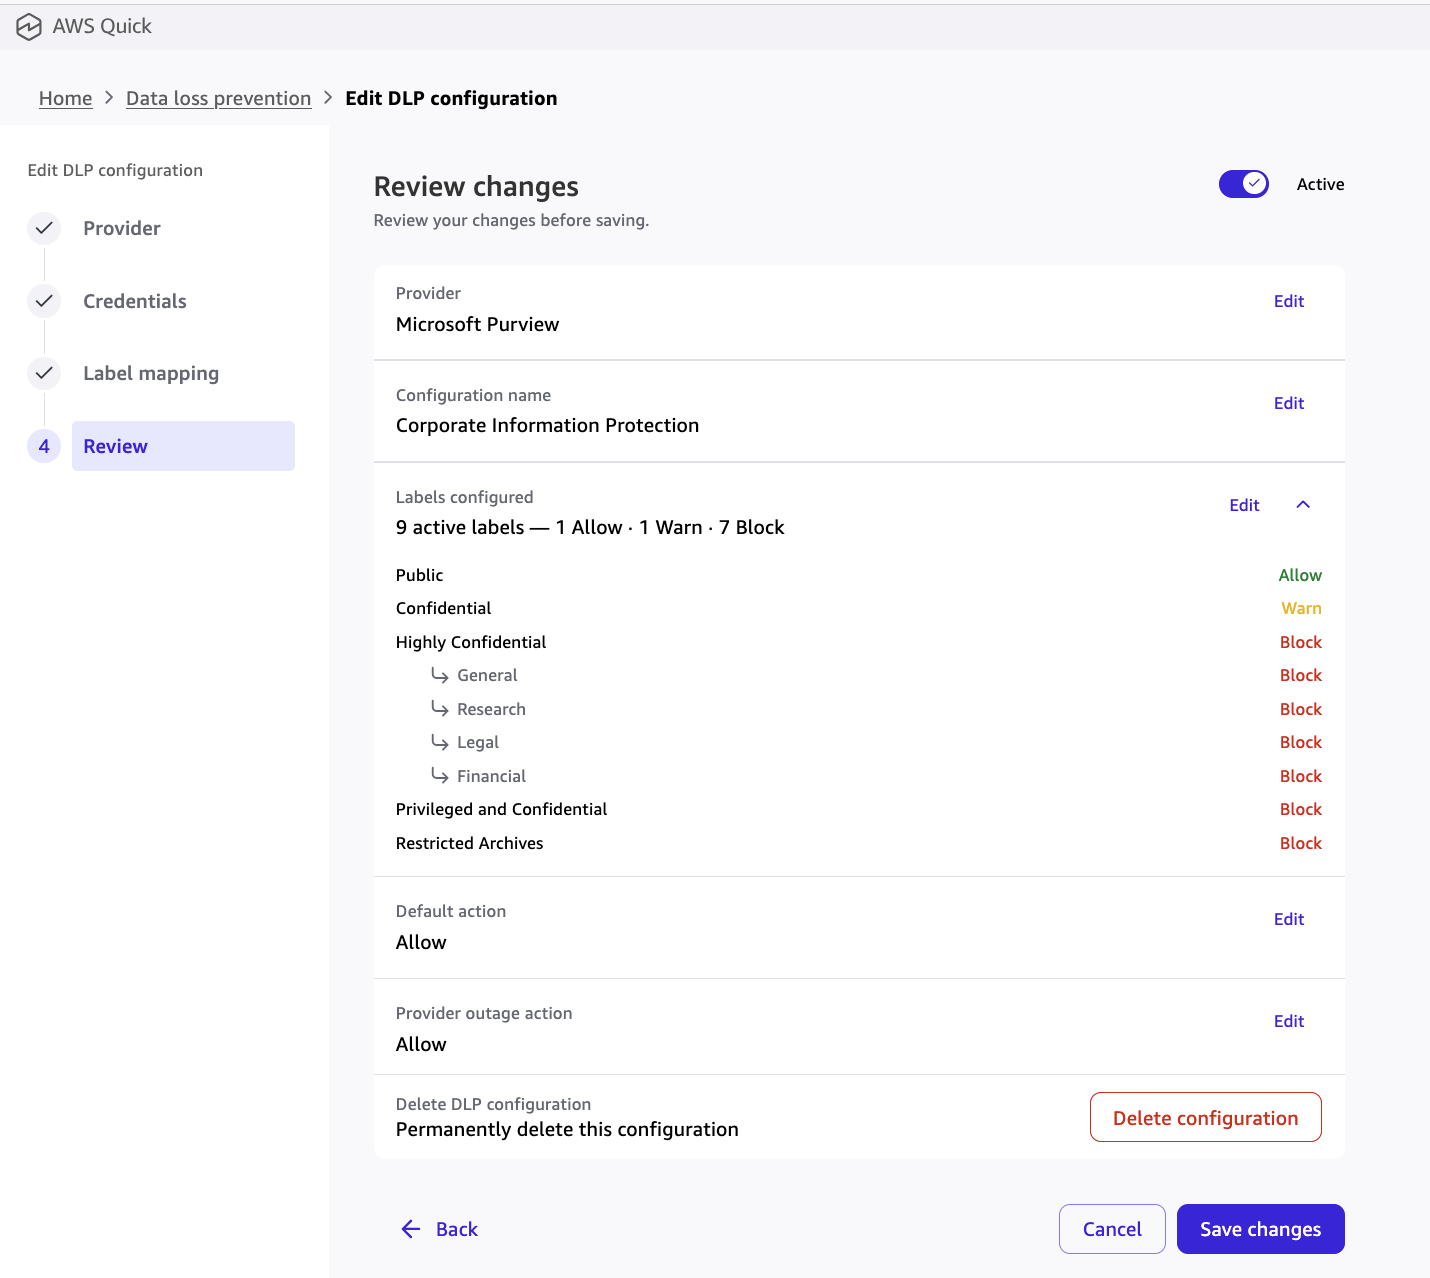
Designed with Zero Trust principles
Every request is authenticated through IAM or SSO. Data access is enforced per user with row-level and column-level security, network traffic is isolated with AWS PrivateLink, and approval policies enforce least-privilege sharing.
Meet your regulatory compliance requirements with AWS Quick
AWS Quick is HIPAA eligible, FedRAMP authorized, SOC 1/2/3 audited, PCI DSS compliant, and ISO certified, backed by the 143 security standards and compliance certifications AWS supports.
SOC 1/2/3 · ISO 27001 · ISO 27018 · HIPAA eligible · FedRAMP · PCI DSS
Allianz Technology scaled AI innovation with governed enterprise adoption
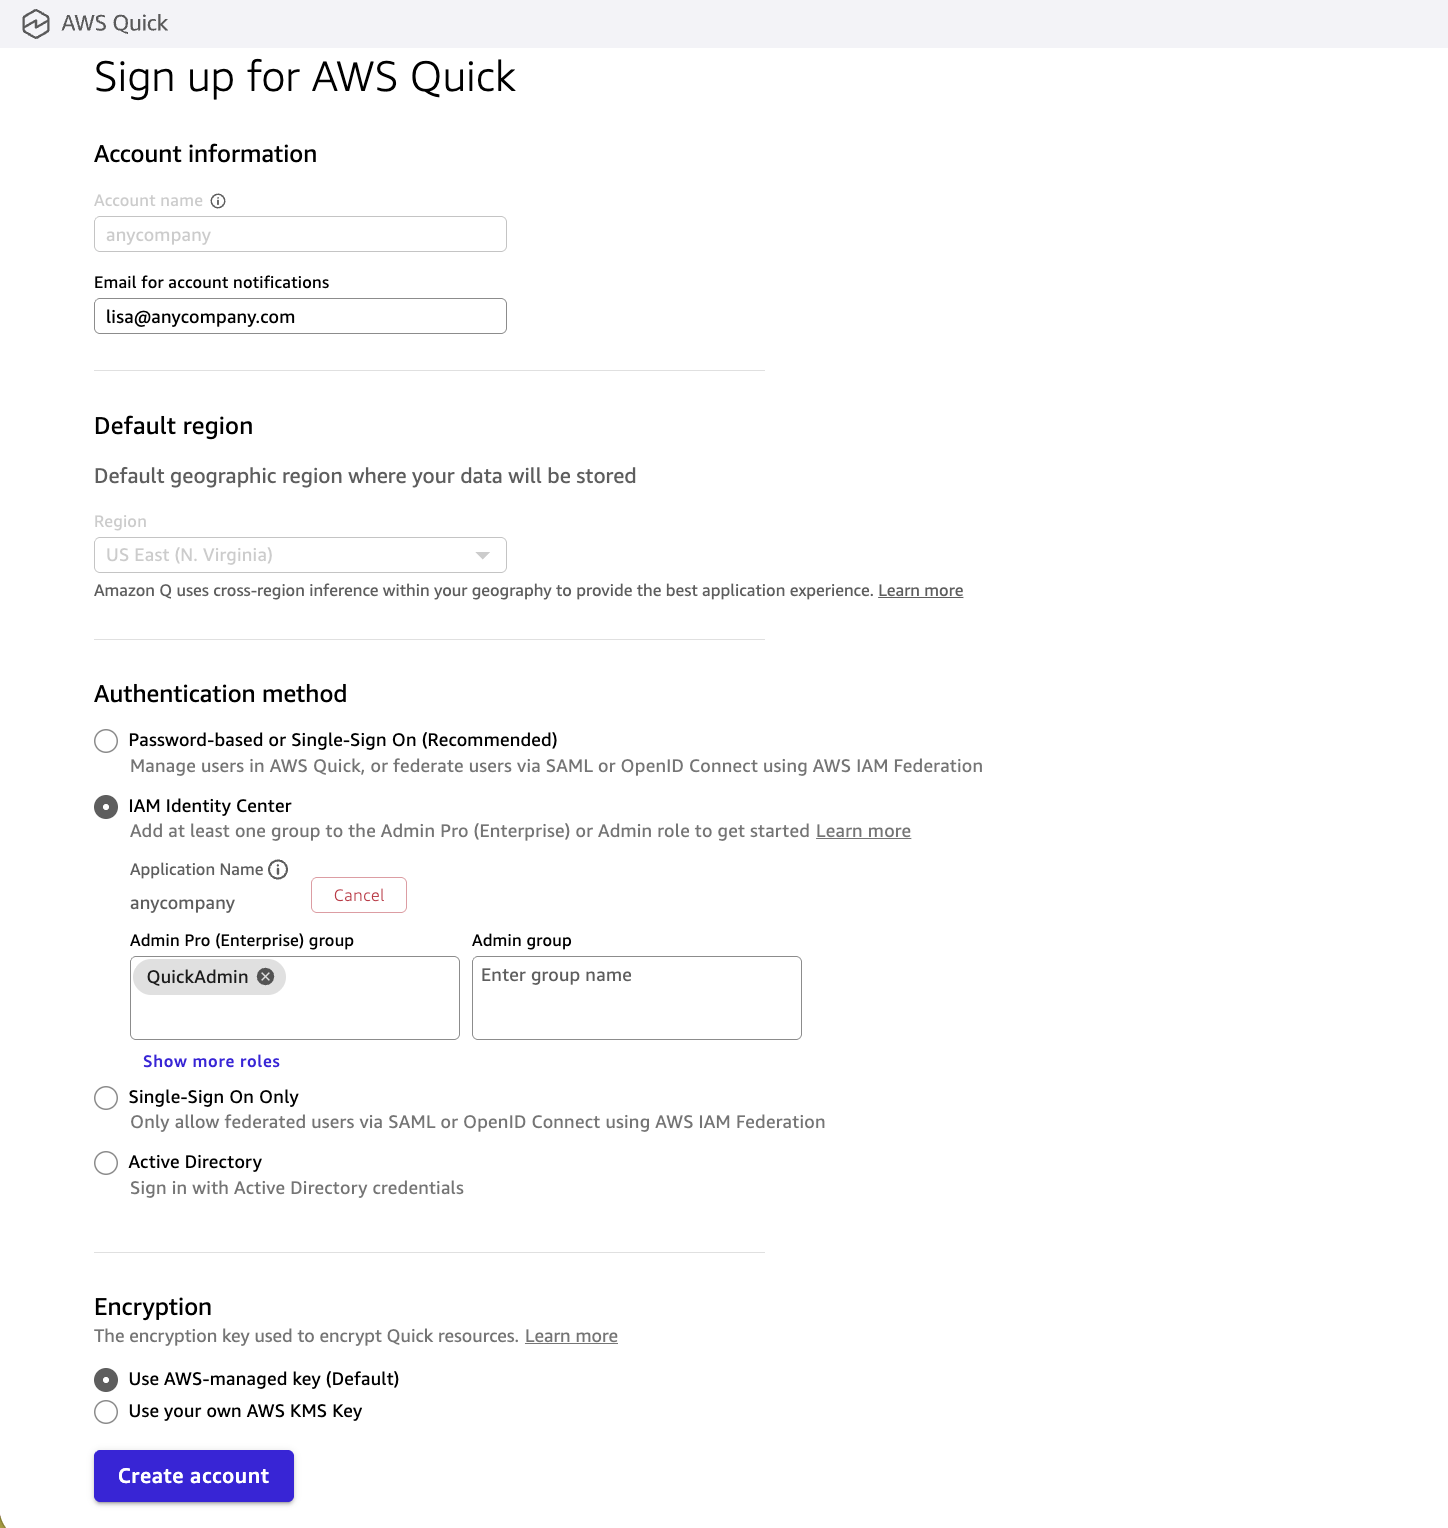
Deploy and manage AWS Quick from a single admin console
Works with your identity provider
Connect through SAML 2.0, IAM Identity Center, Okta, or Azure AD. Existing role-based permissions are honored, with MFA and session timeout controls.
No infrastructure to manage
AWS Quick is fully serverless. There are no servers to provision, patch, or harden, and no maintenance windows.
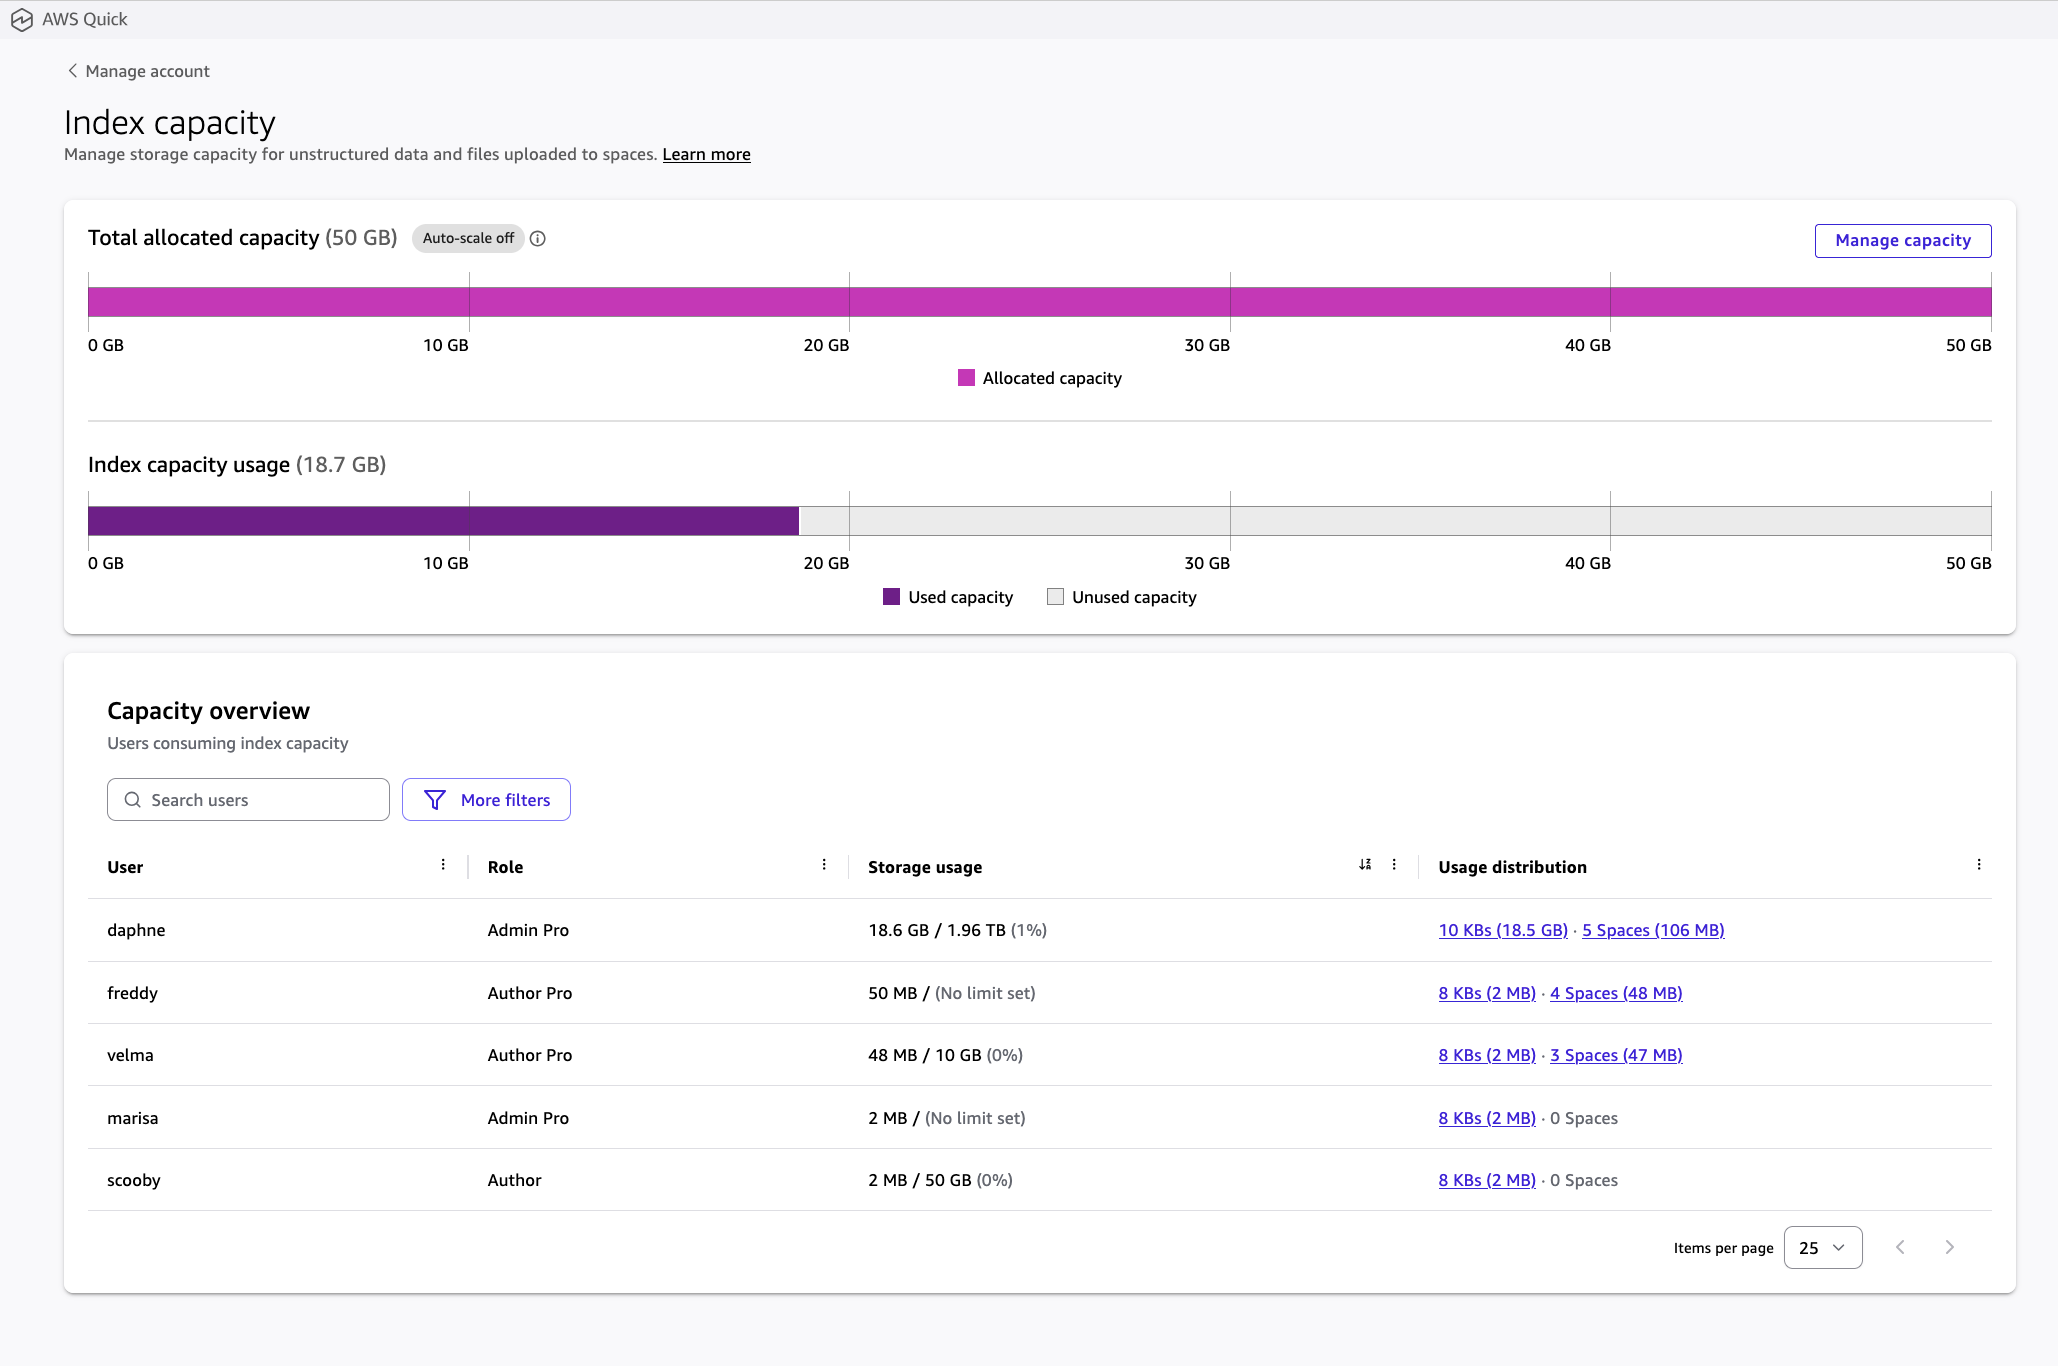
Predictable AI consumption
Set caps on index storage and agent hours by user, role, or account. When a limit is reached, existing content is preserved.
Watch the webinar: Deploying, securing, and governing AI assistants at enterprise scale
Resources for your security review
Documentation and compliance reports to support your evaluation of AWS Quick.
Frequently asked questions
No. AWS does not use your data to train models in any AWS Quick plan, free or paid. Prompt data and generated responses are not shared across customers.
AWS Quick ships every new capability in a restricted state by default. When an administrator enables deny by default on a custom permissions profile, new agentic features in the restricted category are automatically denied on launch day. Administrators evaluate each capability and allow it when ready. Every decision is captured in AWS CloudTrail.
AWS Quick is integrated with Microsoft Purview to enforce your existing sensitivity labels across Quick chat, spaces, and knowledge bases. Admins configure enforcement per label: block, warn, or allow. A provider outage action governs files even when Purview is temporarily unavailable.
AWS Quick is HIPAA eligible, FedRAMP authorized including in AWS GovCloud (US-West), SOC 1/2/3 audited, PCI DSS compliant, and ISO 9001, 27001, 27018, and 27019 certified. In AWS GovCloud (US-West), AWS Quick supports agency Authority to Operate requirements, including DoD SRG Impact Levels 4 and 5, ITAR, CJIS, and FIPS 140-3.
AWS Quick is fully serverless and managed by AWS. There are no servers to provision, patch, or harden, and no patch windows. Infrastructure security shifts to AWS under the shared responsibility model.
Scale AI across every team with AWS Quick
Bring AWS Quick to your organization with the governance you already have.
Explore Quick for enterpriseDid you find what you were looking for today?
Let us know so we can improve the quality of the content on our pages