AWS Security Blog
Category: Uncategorized

An easier way to control access to AWS resources by using the AWS organization of IAM principals
AWS Identity and Access Management (IAM) now makes it easier for you to control access to your AWS resources by using the AWS organization of IAM principals (users and roles). For some services, you grant permissions using resource-based policies to specify the accounts and principals that can access the resource and what actions they can […]

How to Use AWS Config to Monitor for and Respond to Amazon S3 Buckets Allowing Public Access
AWS Config enables continuous monitoring of your AWS resources, making it simple to assess, audit, and record resource configurations and changes. AWS Config does this through the use of rules that define the desired configuration state of your AWS resources. AWS Config provides a number of AWS managed rules that address a wide range of […]

How to centralize DNS management in a multi-account environment
Note from June 5, 2019: The approach and architecture in this post is recommended if you prefer more control over DNS servers or prefer to use AWS Managed Active Directory for DNS resolution, however there are some limitations to this approach and we added a “Limitations and additional considerations” section to this post to describe […]

Understanding AWS CloudHSM Cluster Synchronization
Feb 17, 2025: This blog post references AWS CloudHSM Client SDK 3, which is no longer the recommended version. AWS recommends that you use the latest version, AWS CloudHSM Client SDK 5, which provides updated functionality and commands. We are currently working on an updated blog post for CloudHSM Client SDK 5. See the AWS […]

Rotate Amazon RDS database credentials automatically with AWS Secrets Manager
August 31, 2021: AWS KMS is replacing the term customer master key (CMK) with AWS KMS key and KMS key. The concept has not changed. To prevent breaking changes, AWS KMS is keeping some variations of this term. More info. Recently, we launched AWS Secrets Manager, a service that makes it easier to rotate, manage, […]

Classify sensitive data in your environment using Amazon Macie
June 15, 2020: This blog is out of date. Please refer here for the updated info: https://aws.amazon.com/blogs/aws/new-enhanced-amazon-macie-now-available/ In this post, I’ll show you how to create a sample dataset for Amazon Macie, and how you can use Amazon Macie to implement data-centric compliance and security analytics in your Amazon S3 environment. I’ll also dive into […]

AWS Key Management Service now offers FIPS 140-2 validated cryptographic modules enabling easier adoption of the service for regulated workloads
May 24, 2023: As of May 2023, AWS KMS is now certified at FIPS 140-2 Security Level 3. AWS Key Management Service (KMS) now uses FIPS 140-2 validated hardware security modules (HSM) and supports FIPS 140-2 validated endpoints, which provide independent assurances about the confidentiality and integrity of your keys. Having additional third-party assurances about […]
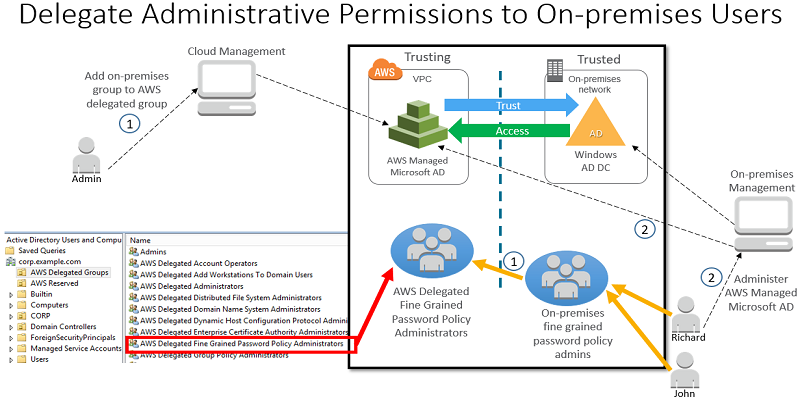
How to Delegate Administration of Your AWS Managed Microsoft AD Directory to Your On-Premises Active Directory Users
You can now enable your on-premises users administer your AWS Directory Service for Microsoft Active Directory, also known as AWS Managed Microsoft AD. Using an Active Directory (AD) trust and the new AWS delegated AD security groups, you can grant administrative permissions to your on-premises users by managing group membership in your on-premises AD directory. […]

How to Use Bucket Policies and Apply Defense-in-Depth to Help Secure Your Amazon S3 Data
Amazon S3 provides comprehensive security and compliance capabilities that meet even the most stringent regulatory requirements. It gives you flexibility in the way you manage data for cost optimization, access control, and compliance. However, because the service is flexible, a user could accidentally configure buckets in a manner that is not secure. For example, let’s […]

How AWS Managed Microsoft AD Helps to Simplify the Deployment and Improve the Security of Active Directory–Integrated .NET Applications
Companies using .NET applications to access sensitive user information, such as employee salary, Social Security Number, and credit card information, need an easy and secure way to manage access for users and applications. For example, let’s say that your company has a .NET payroll application. You want your Human Resources (HR) team to manage and […]