AWS Security Blog
Your AWS Security, Identity, and Governance guide to re:Invent 2026
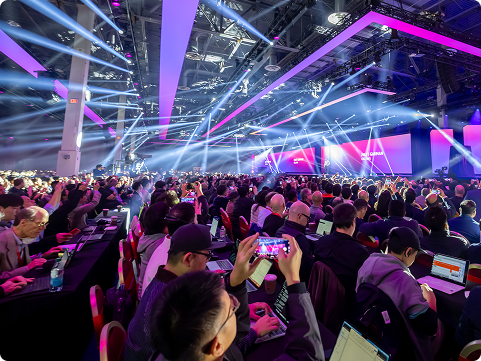
The AWS Security, Identity, and Governance team invites you to join us at re:Invent in Las Vegas from November 30 to December 4, 2026. You know all too well that AI agents now act on their own across the systems you run, and that changes what identity, detection, network protection, and governance have to cover. re:Invent is the week to see how AWS is building security for that shift and to talk it through with the people building it.
Security sessions run every day of the week, nearly 120 of them across breakouts, chalk talks, workshops, code talks, builders’ sessions, and lightning talks. On Thursday, December 3, the Wynn hosts a full day of advanced security sessions in one venue. The sessions are built around five themes this year. They cover securing the agentic enterprise, building securely at the speed you ship, running one security operating model everywhere you run, regulatory confidence and digital sovereignty, and building a culture of security.
Keynotes
AWS leaders use the keynotes to announce new services, launches, and updates that will shape the year ahead in cloud. Many security launches debut during keynote week, and the keynotes set the context for the sessions you’ll attend in the security track. The Thursday keynote runs from 8:30 to 10:00 AM at The Venetian and is also streamed online.
Thursday, December 3: A full day of security deep dives at the Wynn
Security sessions start Monday morning and run through Friday. Thursday is different. 78 security sessions, most of them at the 300 level or above, fill the Wynn from 8:00 AM to 5:30 PM, so you can spend the whole day in one building without crossing the Strip. Rooms are on the Convention Promenade, the Upper and Lower Convention Promenades, and Level 1, and the Cristal 2 Content Hub runs lightning talks and theater sessions all day. The day includes 12 workshops, 11 builders’ sessions, and 22 chalk talks, so most of it is hands-on or interactive.
Three main stage talks from AWS security leaders run through the day in Bandol 1.
| Time | Talk | Speaker |
| 11:00 AM | The Future of Security | Chet Kapoor, AWS VP of Security, Search, and Observability |
| 1:00 PM | The Old Security Playbook Is Dead | Amy Herzog, AWS Chief Information Security Officer |
| 3:00 PM | Operationalizing security for the future with best practices today | Eric Brandwine, VP/Distinguished Engineer, AWS Security |
Chet opens with how AWS is building security for a time when systems and threats both move at machine speed, and how customers secure their agent workloads. Amy follows with what happens when the window between a vulnerability existing and being exploited shrinks from years to minutes. She shares how AWS changed its own practices to stop AI-enabled threat actors and what you can change in your own operations. Eric closes the day by showing how to take the latest AWS security innovations from announcement to adoption across your organization, with the architectural patterns, operational practices, and mental models AWS teams use to raise their security bar.
Between sessions, stop by the Security Lounge in the Convention Lounge at the Wynn to recharge, meet other security practitioners, and visit kiosks from select AWS security partners.
Security sessions all week
You don’t have to wait for Thursday. Security sessions run every day, with 12 on Monday, 16 on Tuesday, 9 on Wednesday, and 3 on Friday, not counting repeats. Monday and Friday sessions are all at the Wynn. Tuesday and Wednesday sessions are spread across the Wynn, MGM Grand, and Caesars Palace, so check the venue when you build your agenda.
Sessions for every security domain
Whatever part of security you work in, the catalog has sessions for it. Here are a few to start with in each domain, and the full list can be found in the session catalog.
Application security and AWS Continuum
AWS Continuum runs through the application security sessions this year.
- SEC427 is a Monday 12:00 PM code talk that threat models an agentic development workflow from user story to deployment with AWS Continuum.
- SEC312 is a Tuesday 3:30 PM workshop where you run an on-demand penetration test against a live application with AWS Continuum.
- SEC311 is a Thursday 1:00 PM builders’ session that wires AWS frontier agents into an automated find-and-fix security loop.
- SEC384 is a Thursday 2:30 PM breakout on how AWS Continuum discovers, validates, and fixes code vulnerabilities in one workflow. SEC304 and SEC426 go deeper on AWS Continuum on Tuesday and Thursday.
Threat detection and incident response
- SEC323 is a Tuesday 3:30 PM workshop where you recover from a simulated ransomware event and prove the restore is clean.
- SEC405 is a Thursday 12:00 PM builders’ session that takes a vulnerable application from discovery to fix with Amazon Inspector, AWS Continuum, and Amazon GuardDuty.
- SEC501 is a Thursday 1:00 PM breakout that goes inside the research behind the GuardDuty detection engine.
- SEC390 is a Thursday 4:00 PM breakout on how Woodside handed SOC monitoring to AWS Security Incident Response to focus on threat hunting.
Identity and access management
- SEC388 is a Monday 10:00 AM breakout where the National Institutes of Health shares how it manages identity lifecycle across clouds.
- SEC424 is a Tuesday 2:30 PM chalk talk on how IAM evaluates your policies on every request.
- SEC362 is a Thursday 8:00 AM workshop where you build authentication, authorization, and audit for AI agents.
- SEC419 is a Thursday 11:30 AM chalk talk on OAuth delegation patterns for agents with Amazon Bedrock AgentCore Identity.
Cloud governance
- SEC302 is a Monday 10:00 AM breakout on building a governance foundation for AI workloads that grows with autonomous agents.
- SEC349 is a Thursday 8:30 AM workshop where you build a layered controls stack for a fleet of agents.
- SEC374 is a Thursday 1:30 PM breakout on how Moeve turned natural language into enforced governance controls.
- SEC351 is a Friday 9:00 AM breakout on running governance across AWS and other clouds as one operation.
Network and application protection
- SEC364 is a Tuesday 1:00 PM breakout on how Coupang secures its software and AI supply chains with AWS Network Firewall.
- SEC303 is a Wednesday 10:00 AM breakout on the network security capabilities AWS built for agentic workloads.
- SEC363 is a Thursday 12:00 PM breakout on what’s new in Amazon Route 53 Resolver DNS Firewall.
- SEC313 is a Thursday 2:30 PM builders’ session where you set up the AWS Network Firewall proxy for secure egress.
Data protection
- SEC206 is a Thursday 1:00 PM breakout on meeting digital sovereignty requirements with the AWS European Sovereign Cloud.
- SEC207 is a Thursday 2:30 PM lightning talk where Capital One explains how it runs payment cryptography in the cloud.
- SEC316 is a Thursday 4:00 PM builders’ session where teams race through post-quantum migration challenges.
- SEC204 is a Friday 11:30 AM breakout where AWS and DXC Technology share how to prepare for post-quantum cryptography at scale.
AI security
- SEC328 is a Tuesday 11:30 AM chalk talk on enforcing AI guardrails across your organization without slowing teams down.
- SEC237 is a Thursday 8:30 AM breakout on how AWS foundational security extends into AI services.
- SEC343 is a Thursday 12:00 PM builders’ session where you watch an MCP tool poisoning attack and build the defenses against it.
- SEC341 is a Thursday 3:00 PM workshop where you layer defenses for an AI agent from the prompt to tool execution.
Culture of security
Three sessions focus on how security teams work in the agentic era.
- SEC425 is a Wednesday 9:00 AM breakout on how AWS uses automated reasoning and neurosymbolic AI to prove security properties.
- SEC342 is a Thursday 11:30 AM breakout on the lessons the AWS Office of the CISO learned from Project Glasswing.
- SEC350 is a Thursday 4:00 PM chalk talk on building trust between people when agents work on your behalf.
Session types
Sessions come in several formats, and most security sessions sit under the Security, Identity, and Compliance (SEC) topic in the event catalog. If you attend in person, lightning talks are walk-up only. For every other format, you can reserve a seat in the event portal (login required) or join as a walk-up based on availability.
| Format | What to expect |
| Breakout sessions | 60-minute presentations led by AWS security experts and customers |
| Chalk talks | 60-minute interactive sessions where AWS experts whiteboard and take your questions |
| Code talks | 60-minute sessions built around live coding and technical implementation |
| Builders’ sessions | 60-minute small-group sessions where you build alongside an AWS expert |
| Workshops | 120-minute hands-on sessions where you work directly with AWS services |
| Lightning talks | 20-minute talks on a single focused topic |
Security, Identity, and Governance track sessions
You can find all of the Security, Identity, and Governance track sessions listed on the agenda page. Dates and venues can change, so check the event portal for the latest details.
Beyond the sessions
Security kiosks in the AWS Village
If you’d like to speak to AWS experts on something you’re working on, or find out the ins and outs of a specific AWS security service, find the security kiosks in the AWS Village in the Expo. Here you can talk with AWS experts about identity and access management, threat detection and response, governance and compliance, application security, and network security. The Expo opens Monday, November 30 at 4:00 PM and runs daily through Thursday, December 3.
Security meetups
Join a security meetup on Tuesday, Wednesday, or Thursday, most of them at the Wynn. Meetups are small-group conversations with AWS experts, with no slides, on topics such as detection and response at machine speed, data protection and the post-quantum shift, and identity for humans, workloads, and AI agents.
Receptions
There are several Security, Identity & Governance receptions over the course of the week so be sure to speak with you AWS account manager and ask for the details. Most of these events require pre-registration so don’t wait!
First time at re:Invent?
For those of you that have never attended a re:Invent before, these four tips will help.
- Pick up your badge on Sunday if you can, since badge pickup opens before the first sessions.
- Download the AWS Events mobile app to build your agenda.
- While the vast majority of Security sessions are located at the Wynn, plan your route between venues, since walking between hotels on the Strip takes longer than it looks.
- On Thursday, plan to spend your day at the Wynn, where every security session that day takes place.
See you in Las Vegas
Start building your security agenda today in the re:Invent security catalog. Recordings of many breakout sessions will be posted on the AWS Events YouTube channel after the event.
See you in Las Vegas.
If you have questions about this post, contact AWS Support or start a new thread on AWS re:Post.