AWS Security Blog

Author: Craig Liebendorfer
I write for and work with other authors who write for the AWS Database Blog. I previously owned and edited the AWS Security Blog for 3+ years.

A New AWS Government, Education, and Nonprofits Blog Post: “AWS Achieves Full Empanelment for the Delivery of Cloud Services by India’s Ministry of Electronics and Information Technology”
AWS recently announced that Amazon Internet Services Private Limited (AISPL), an Indian subsidiary of the Amazon Group that undertakes the resale and marketing of AWS Cloud services in India, has achieved full Cloud Service Provider (CSP) empanelment and successfully completed the Standardization Testing and Quality Certification (STQC) audit from the Indian Ministry of Electronics and […]

AWS HIPAA Program Update – Dedicated Instances and Hosts Are No Longer Required
Over the years, we have seen tremendous growth in the use of the AWS Cloud for healthcare applications. Our customers and AWS Partner Network (APN) Partners who offer solutions that store, process, and transmit Protected Health Information (PHI) sign a Business Associate Addendum (BAA) with AWS. As part of the AWS HIPAA compliance program, customers and […]

Now Available: Use Resource-Level Permissions to Control Access to and Permissions on Auto Scaling Resources
As of May 15, 2017, you can define AWS Identity and Access Management policies to control which Auto Scaling resources users can access and the actions users are permitted to perform on those resources. Auto Scaling helps you maintain application availability and allows you to scale your Amazon EC2 capacity up or down automatically according to conditions you […]

Amazon QuickSight Now Supports Audit Logging with AWS CloudTrail
Amazon QuickSight democratizes business intelligence, making it easier and cheaper for you to provide advanced business analytics capabilities to everyone in your organization. Amazon QuickSight also enables you to understand your business better and helps you make data-driven decisions more quickly. However, determining who has access to which data in your organization can still be […]

Manage Access to Your Amazon RDS for MySQL and Amazon Aurora Databases Using AWS IAM
Starting today, Amazon RDS enables you to use AWS Identity and Access Management (IAM) to manage database access for Amazon RDS for MySQL database instances and Amazon Aurora database clusters. By using IAM, you can manage user access to all AWS resources from a single location, without needing to manage users in the database. This includes expanding […]

Easily Tag Amazon EC2 Instances and Amazon EBS Volumes on Creation
In 2010, AWS launched resource tagging for Amazon EC2 instances and other EC2 resources. Since that launch, we have raised the allowable number of tags per resource from 10 to 50 and made tags more useful with the introduction of resource groups and Tag Editor. AWS customers use tags to track ownership, drive their cost accounting […]
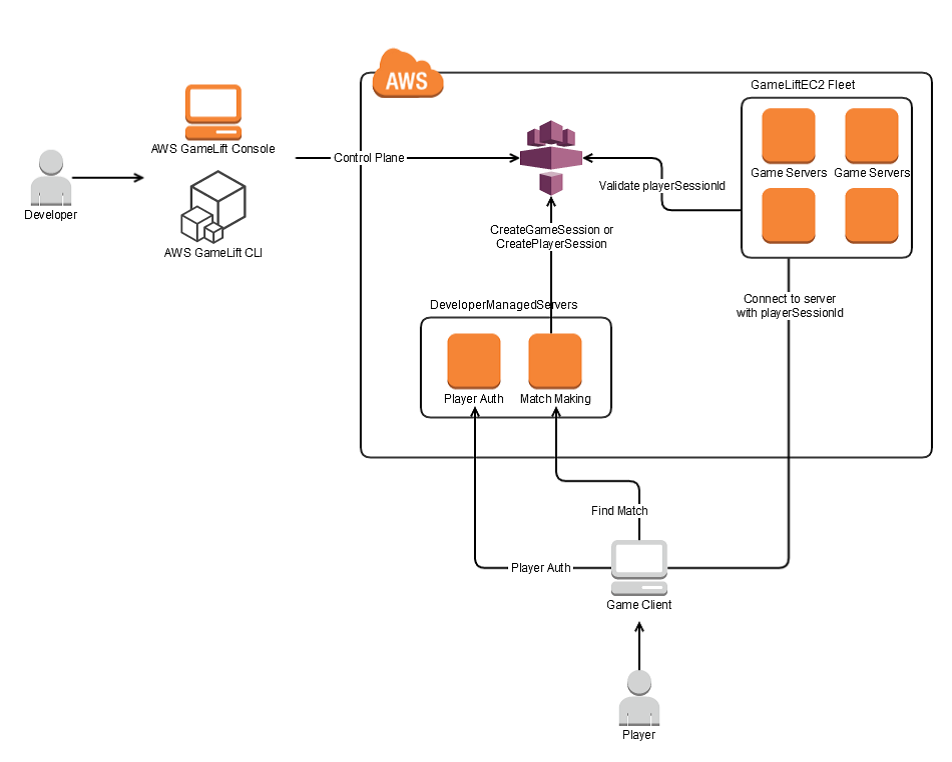
New Amazon GameDev Blog Post: Protect Multiplayer Game Servers from DDoS Attacks by Using Amazon GameLift
In online gaming, distributed denial of service (DDoS) attacks target a game’s network layer, flooding servers with requests until performance degrades considerably. These attacks can limit a game’s availability to players and limit the player experience for those who can connect. Today’s new Amazon GameDev Blog post uses a typical game server architecture to highlight […]

Thursday, December 1: Security and Compliance Sessions Today at re:Invent
Today, the following security and compliance sessions will be presented at AWS re:Invent 2016 in Las Vegas (all times local). See the re:Invent Session Catalog for complete information about every session. You can also download the AWS re:Invent 2016 Event App for the latest updates and information. If you are not attending re:Invent 2016, keep […]
Tuesday, November 29: Security and Compliance Sessions Today at re:Invent
Today, the following security and compliance sessions will be presented at AWS re:Invent 2016 in Las Vegas. All times are local. See the re:Invent Session Catalog for complete information about every session. You can also download the AWS re:Invent 2016 Event App for the latest updates and information. If you are not attending re:Invent 2016, […]

New AWS Compute Blog Post: Help Secure Container-Enabled Applications with IAM Roles for ECS Tasks
Amazon EC2 Container Service (ECS) now allows you to specify an IAM role that can be used by the containers in an ECS task, as a new AWS Compute Blog post explains. When an application makes use of the AWS SDK or CLI to make requests to the AWS API, it must sign each request with valid AWS access […]