AWS Security Blog
Category: AWS Identity and Access Management (IAM)

New! Attach an AWS IAM Role to an Existing Amazon EC2 Instance by Using the AWS CLI
AWS Identity and Access Management (IAM) roles enable your applications running on Amazon EC2 to use temporary security credentials that AWS creates, distributes, and rotates automatically. Using temporary credentials is an IAM best practice because you do not need to maintain long-term keys on your instance. Using IAM roles for EC2 also eliminates the need […]

Now Create and Manage Users More Easily with the AWS IAM Console
Today, we updated the AWS Identity and Access Management (IAM) console to make it easier for you to create and manage your IAM users. These improvements include an updated user creation workflow and new ways to assign and manage permissions. The new user workflow guides you through the process of setting user details, including enabling […]
How to Assign Permissions Using New AWS Managed Policies for Job Functions
Today, AWS Identity and Access Management (IAM) made 10 AWS managed policies available that align with common job functions. AWS managed policies enable you to set permissions using policies that AWS creates and manages, and with a single AWS managed policy for job functions, you can grant the permissions necessary for network or database administrators, […]

How to Enable MFA Protection on Your AWS API Calls
Multi-factor authentication (MFA) provides an additional layer of security for sensitive API calls, such as terminating Amazon EC2 instances or deleting important objects stored in an Amazon S3 bucket. In some cases, you may want to require users to authenticate with an MFA code before performing specific API requests, and by using AWS Identity and […]
IAM Service Last Accessed Data Now Available for the Asia Pacific (Mumbai) Region
In December, AWS Identity and Access Management (IAM) released service last accessed data, which helps you identify overly permissive policies attached to an IAM entity (a user, group, or role). Today, we have extended service last accessed data to support the recently launched Asia Pacific (Mumbai) Region. With this release, you can now view the […]

Enable Your Federated Users to Work in the AWS Management Console for up to 12 Hours
AWS Identity and Access Management (IAM) supports identity federation, which enables external identities, such as users in your corporate directory, to sign in to the AWS Management Console via single sign-on (SSO). Now with a small configuration change, your AWS administrators can allow your federated users to work in the AWS Management Console for up […]

How to Control Access to Your Amazon Elasticsearch Service Domain
September 9, 2021: Amazon Elasticsearch Service has been renamed to Amazon OpenSearch Service. See details. With the recent release of Amazon Elasticsearch Service (Amazon ES), you now can build applications without setting up and maintaining your own search cluster on Amazon EC2. One of the key benefits of using Amazon ES is that you can […]
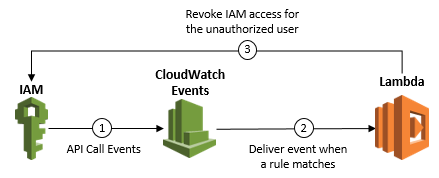
How to Detect and Automatically Revoke Unintended IAM Access with Amazon CloudWatch Events
Update on October 24, 2018: Note that if you do not author the Lambda function correctly, this setup can create an infinite loop (in this case, a rule that is fired repeatedly, which can impact your AWS resources and cause higher than expected charges to your account). The example Lambda function I provide in Step […]

How to Record and Govern Your IAM Resource Configurations Using AWS Config
AWS Config recently added the ability to record changes to the configuration of your AWS Identity and Access Management (IAM) users, groups, and roles (collectively referred to as IAM entities) and the policies associated with them. Using this feature, you can record configuration details for these IAM entities, including details about which policies are associated […]

Remove Unnecessary Permissions in Your IAM Policies by Using Service Last Accessed Data
As a security best practice, AWS recommends writing AWS Identity and Access Management (IAM) policies that adhere to the principle of least privilege, which means granting only the permissions required to perform a specific task. However, verifying which permissions an application or user actually needs can be a challenge. To help you determine which permissions […]