AWS Security Blog
Category: AWS Identity and Access Management (IAM)

IAM Policies and Bucket Policies and ACLs! Oh, My! (Controlling Access to S3 Resources)
September 11, 2023: This post has been updated. Updated on July 6, 2023: This post has been updated to reflect the current guidance around the usage of S3 ACL and to include S3 Access Points and the Block Public Access for accounts and S3 buckets. Updated on April 27, 2023: Amazon S3 now automatically enables […]

Temporary elevated access management with IAM Identity Center
AWS recommends using automation where possible to keep people away from systems—yet not every action can be automated in practice, and some operations might require access by human users. Depending on their scope and potential impact, some human operations might require special treatment. One such treatment is temporary elevated access, also known as just-in-time access. […]

How to monitor and query IAM resources at scale – Part 2
In this post, we continue with our recommendations for using AWS Identity and Access Management (IAM) APIs. In part 1 of this two-part series, we described how you could create IAM resources and use them soon after for authorization decisions. We also described options for monitoring and responding to IAM resource changes for entire accounts. […]
How to monitor and query IAM resources at scale – Part 1
March 7, 2023: We’ve fixed a typo in the blog post. In this two-part blog post, we’ll provide recommendations for using AWS Identity and Access Management (IAM) APIs, and we’ll share useful details on how IAM works so that you can use it more effectively. For example, you might be creating new IAM resources such as roles […]

How to use AWS Private Certificate Authority short-lived certificate mode
AWS Private Certificate Authority (AWS Private CA) is a highly available, fully managed private certificate authority (CA) service that you can use to create CA hierarchies and issue private X.509 certificates. You can use these private certificates to establish endpoints for TLS encryption, cryptographically sign code, authenticate users, and more. Based on customer feedback for […]
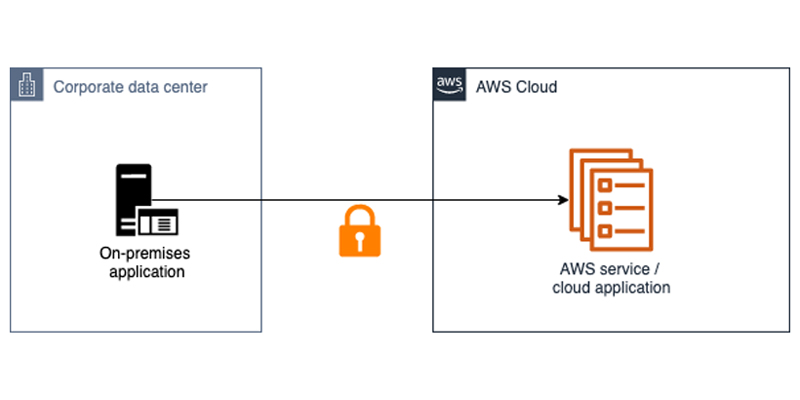
Approaches for authenticating external applications in a machine-to-machine scenario
December 8, 2022: This post has been updated to reflect changes for M2M options with the new service of IAMRA. This blog post was first published November 19, 2013. August 10, 2022: This blog post has been updated to reflect the new name of AWS Single Sign-On (SSO) – AWS IAM Identity Center. Read more […]

How to use trust policies with IAM roles
June 20 2023: The wording in this post has been updated to avoid confusion around the use of wildcards in the principal element of an AWS Identity and Access Management (IAM) trust policy statement. November 3, 2022: We updated this post to fix some syntax errors in the policy statements and to add additional use […]
IAM Access Analyzer makes it simpler to author and validate role trust policies
AWS Identity and Access Management (IAM) Access Analyzer provides many tools to help you set, verify, and refine permissions. One part of IAM Access Analyzer—policy validation—helps you author secure and functional policies that grant the intended permissions. Now, I’m excited to announce that AWS has updated the IAM console experience for role trust policies to […]

Announcing an update to IAM role trust policy behavior
April 16, 2024: Updated with information on AWS CloudTrail logging for roles that are still using the implicit trust behavior, and additional sample queries to find these roles. June 15, 2023: Enforcement has changed from a fixed date to an automated process starting June 30, 2023 that removed roles based on observed role assumption behavior. […]

Extend AWS IAM roles to workloads outside of AWS with IAM Roles Anywhere
AWS Identity and Access Management (IAM) has now made it easier for you to use IAM roles for your workloads that are running outside of AWS, with the release of IAM Roles Anywhere. This feature extends the capabilities of IAM roles to workloads outside of AWS. You can use IAM Roles Anywhere to provide a […]