AWS Security Blog
Category: Storage
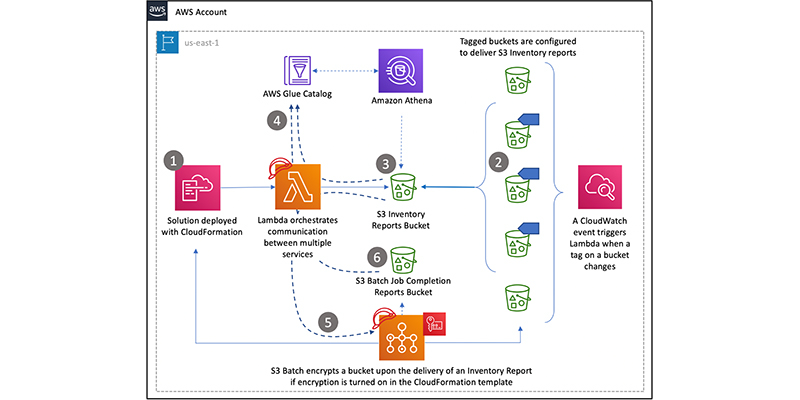
How to retroactively encrypt existing objects in Amazon S3 using S3 Inventory, Amazon Athena, and S3 Batch Operations
February 5, 2026: Amazon S3 now supports the UpdateObjectEncryption API so you can atomically update the server-side encryption type of existing encrypted objects from server-side encryption with S3 managed encryption (SSE-S3) to server-side encryption with AWS Key Management Service (AWS KMS) encryption keys (SSE-KMS). Read the documentation. November 1, 2021: AWS KMS is replacing the […]

Tighten S3 permissions for your IAM users and roles using access history of S3 actions
September 28, 2023: IAM is incrementally adding support for actions from more services. For a list of services that report action last accessed information, see IAM action last accessed information services and actions. Customers tell us that when their teams and projects are just getting started, administrators may grant broad access to inspire innovation and […]

Continuously monitor unused IAM roles with AWS Config
February 19, 2024: You can now use IAM Access Analyzer to easily identify unused roles. Read this blog post to learn more. January 6, 2021: We updated this post to fix a bug related to allow listing noncompliant roles. January 6, 2020: We updated this post to reflect a valid STS session duration if configured […]

Now You Can Create Encrypted Amazon EBS Volumes by Using Your Custom Encryption Keys When You Launch an Amazon EC2 Instance
October 29, 2021: AWS KMS is replacing the term customer master key (CMK) with AWS KMS key and KMS key. The concept has not changed. To prevent breaking changes, AWS KMS is keeping some variations of this term. More info. Amazon Elastic Block Store (EBS) offers an encryption solution for your Amazon EBS volumes so […]

How to Use Bucket Policies and Apply Defense-in-Depth to Help Secure Your Amazon S3 Data
Amazon S3 provides comprehensive security and compliance capabilities that meet even the most stringent regulatory requirements. It gives you flexibility in the way you manage data for cost optimization, access control, and compliance. However, because the service is flexible, a user could accidentally configure buckets in a manner that is not secure. For example, let’s […]

How to Patch, Inspect, and Protect Microsoft Windows Workloads on AWS—Part 1
Most malware tries to compromise your systems by using a known vulnerability that the maker of the operating system has already patched. To help prevent malware from affecting your systems, two security best practices are to apply all operating system patches to your systems and actively monitor your systems for missing patches. In case you […]

AWS Earns Department of Defense Impact Level 5 Provisional Authorization
The Defense Information Systems Agency (DISA) has granted the AWS GovCloud (US) Region an Impact Level 5 (IL5) Department of Defense (DoD) Cloud Computing Security Requirements Guide (CC SRG) Provisional Authorization (PA) for six core services. This means that AWS’s DoD customers and partners can now deploy workloads for Controlled Unclassified Information (CUI) exceeding IL4 […]

How to Facilitate Data Analysis and Fulfill Security Requirements by Using Centralized Flow Log Data
I am an AWS Professional Services consultant, which has me working directly with AWS customers on a daily basis. One of my customers recently asked me to provide a solution to help them fulfill their security requirements by having the flow log data from VPC Flow Logs sent to a central AWS account. This is […]

Easily Tag Amazon EC2 Instances and Amazon EBS Volumes on Creation
In 2010, AWS launched resource tagging for Amazon EC2 instances and other EC2 resources. Since that launch, we have raised the allowable number of tags per resource from 10 to 50 and made tags more useful with the introduction of resource groups and Tag Editor. AWS customers use tags to track ownership, drive their cost accounting […]

How to Detect and Automatically Remediate Unintended Permissions in Amazon S3 Object ACLs with CloudWatch Events
Update on October 24, 2018: Note that if you do not author the Lambda function correctly, this setup can create an infinite loop (in this case, a rule that is fired repeatedly, which can impact your AWS resources and cause higher than expected charges to your account). The example Lambda function I provide in Step […]