AWS Security Blog

How to seamlessly domain join Amazon EC2 instances to a single AWS Managed Microsoft AD Directory from multiple accounts and VPCs
You can now share a single AWS Directory Service for Microsoft Active Directory (also known as an AWS Managed Microsoft AD) with multiple AWS accounts within an AWS Region. This capability makes it easier and more cost-effective for you to manage directory-aware workloads from a single directory across accounts and Amazon Virtual Private Clouds (Amazon […]

Use YubiKey security key to sign into AWS Management Console with YubiKey for multi-factor authentication
April 25, 2023: We’ve updated this blog post to include more security learning resources. Update on October 8, 2018: After we launched support for security devices manufactured by Yubico on September 25, 2018, we received feedback from customers to support other U2F security key providers, as well. Starting October 8, 2018, you can now enable […]

AWS Organizations now requires email address verification in order to invite accounts to an organization
AWS Organizations, the service for centrally managing multiple AWS accounts, enables you to invite existing accounts to join your organization. To provide additional assurance about your organization’s identity to AWS accounts that you invite, AWS Organizations is adding a new feature. Beginning on September 27, 2018, you’ll need to verify the email address associated with […]

Visualizing Amazon GuardDuty findings
September 9, 2021: Amazon Elasticsearch Service has been renamed to Amazon OpenSearch Service. See details. Amazon GuardDuty is a managed threat detection service that continuously monitors for malicious or unauthorized behavior to help protect your AWS accounts and workloads. Enable GuardDuty and it begins monitoring for: Anomalous API activity Potentially unauthorized deployments and compromised instances […]

How to use AWS Secrets Manager to rotate credentials for all Amazon RDS database types, including Oracle
August 31, 2021: AWS KMS is replacing the term customer master key (CMK) with AWS KMS key and KMS key. The concept has not changed. To prevent breaking changes, AWS KMS is keeping some variations of this term. More info. You can now use AWS Secrets Manager to rotate credentials for Oracle, Microsoft SQL Server, […]

How to automate the import of third-party threat intelligence feeds into Amazon GuardDuty
Amazon GuardDuty is an AWS threat detection service that helps protect your AWS accounts and workloads by continuously monitoring them for malicious and unauthorized behavior. You can enable Amazon GuardDuty through the AWS Management Console with one click. It analyzes billions of events across your AWS accounts and uses machine learning to detect anomalies in […]
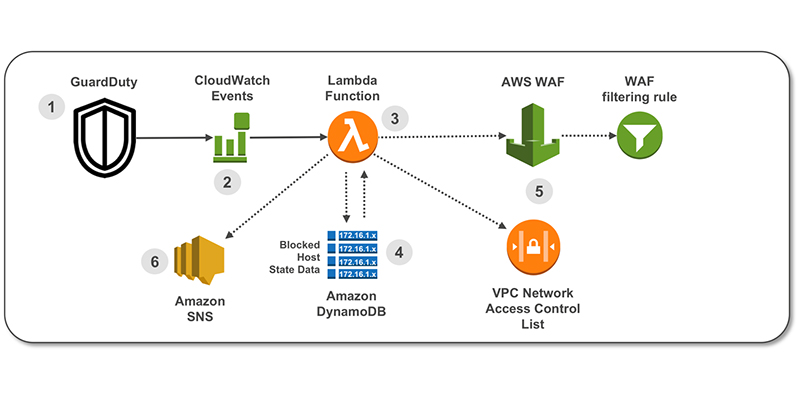
How to use Amazon GuardDuty and AWS Web Application Firewall to automatically block suspicious hosts
April 25, 2023: We’ve updated this blog post to include more security learning resources. When you’re implementing security measures across your AWS resources, you should use a holistic approach that incorporates controls across multiple areas. In the Cloud Adoption Framework (CAF) Security perspective whitepaper, we define these controls across four categories. Directive controls. Establish the […]

Amazon ElastiCache for Redis now PCI DSS compliant, allowing you to process sensitive payment card data in-memory for faster performance
Amazon ElastiCache for Redis has achieved the Payment Card Industry Data Security Standard (PCI DSS). This means that you can now use ElastiCache for Redis for low-latency and high-throughput in-memory processing of sensitive payment card data, such as Customer Cardholder Data (CHD). ElastiCache for Redis is a Redis-compatible, fully-managed, in-memory data store and caching service […]

U.K. National Health Services IGToolkit Assessment report now available
We know that customers often seek out third-party tools to allow for the baselining and benchmarking of their environment. Additionally, healthcare and life sciences customers (HCLS) have specific needs, which is why we continually strive to meet relevant global standards validating our security and compliance. Today, we’d like to take a look at a new […]

Accept a BAA with AWS for all accounts in your organization
I’m excited to announce to our healthcare customers and partners that you can now accept a single AWS Business Associate Addendum (BAA) for all accounts within your organization. Once accepted, all current and future accounts created or added to your organization will immediately be covered by the BAA. Our team is always thinking about how […]