AWS Security Blog

New! Attach an AWS IAM Role to an Existing Amazon EC2 Instance by Using the AWS CLI
AWS Identity and Access Management (IAM) roles enable your applications running on Amazon EC2 to use temporary security credentials that AWS creates, distributes, and rotates automatically. Using temporary credentials is an IAM best practice because you do not need to maintain long-term keys on your instance. Using IAM roles for EC2 also eliminates the need […]

How to Remediate Amazon Inspector Security Findings Automatically
May 31, 2022: The updated blog post is available here. June 18, 2020: This solution no longer works, and the Lambda runtime this code is relying on has been deprecated. When we have an updated blog, we’ll add a link to it here. Updated on November 27, 2018: We added a policy to the instructions […]
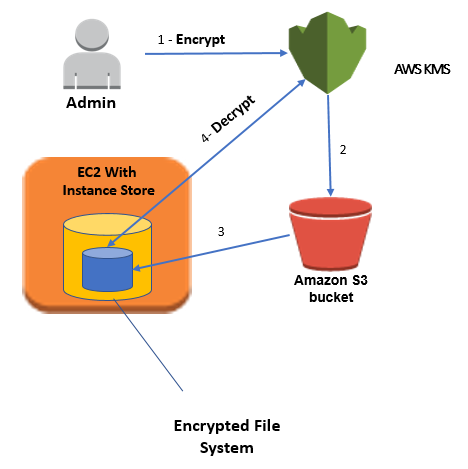
How to Protect Data at Rest with Amazon EC2 Instance Store Encryption
April 25, 2023: We’ve updated this blog post to include more security learning resources. Note: By default, an instance type that includes an NVMe instance store encrypts data at rest using an XTS-AES-256 block cipher. See this FAQ about NVMe-supported instance types. If you’re using an NVMw instance type, then data at rest is encrypted […]

How to Detect and Automatically Remediate Unintended Permissions in Amazon S3 Object ACLs with CloudWatch Events
Update on October 24, 2018: Note that if you do not author the Lambda function correctly, this setup can create an infinite loop (in this case, a rule that is fired repeatedly, which can impact your AWS resources and cause higher than expected charges to your account). The example Lambda function I provide in Step […]

New SOC 2 Report Available: Confidentiality
As with everything at Amazon, the success of our security and compliance program is primarily measured by one thing: our customers’ success. Our customers drive our portfolio of compliance reports, attestations, and certifications that support their efforts in running a secure and compliant cloud environment. As a result of our engagement with key customers across […]

How to Monitor AWS Account Configuration Changes and API Calls to Amazon EC2 Security Groups
You can use AWS security controls to detect and mitigate risks to your AWS resources. The purpose of each security control is defined by its control objective. For example, the control objective of an Amazon VPC security group is to permit only designated traffic to enter or leave a network interface. Let’s say you have […]

Announcing AWS Organizations: Centrally Manage Multiple AWS Accounts
Today, AWS launched AWS Organizations: a new way for you to centrally manage all the AWS accounts your organization owns. Now you can arrange your AWS accounts into groups called organizational units (OUs) and apply policies to OUs or directly to accounts. For example, you can organize your accounts by application, environment, team, or any […]

AWS CloudTrail Now Tracks Cross-Account Activity to Its Origin
You can use AWS Identity and Access Management (IAM) roles and AWS Security Token Service (STS) to set up cross-account access between AWS accounts. When you assume an IAM role in another AWS account to obtain cross-account access to services and resources in that account, AWS CloudTrail logs the cross-account activity. Starting today, CloudTrail logs […]

Now Create and Manage Users More Easily with the AWS IAM Console
Today, we updated the AWS Identity and Access Management (IAM) console to make it easier for you to create and manage your IAM users. These improvements include an updated user creation workflow and new ways to assign and manage permissions. The new user workflow guides you through the process of setting user details, including enabling […]

How to Move More Custom Applications to the AWS Cloud with AWS Directory Service
Some Active Directory (AD) integrated applications require custom changes to the directory schema. Today, we have added the ability for an administrator to extend the schema of AWS Directory Service for Microsoft Active Directory (Enterprise Edition), also known as Microsoft AD. Specifically, you can modify the AD schema and enable many more applications. This feature […]