AWS Partner Network (APN) Blog
Simplifying AWS Outposts Operations at Scale with CloudPrimus
By: Sumeeth Siriyur, Hybrid Edge SA – AWS
By: Jitender Singh, Solutions Architect – Comquest
By: Alfian Abdi, Solutions Architect – Xtremax
By: Raja Rajaram, Hybrid Edge BD – AWS
As AWS Outposts deployments scale across multiple teams and customers, organizations need consistent ways to manage shared compute and storage capacity across tenants. In this post, we explore how CloudPrimus builds on the Outpost capabilities to provide a centralized operational layer for tenant onboarding, self-service provisioning, shared-capacity allocation, and consolidated cost visibility.
AWS Outposts extends AWS infrastructure and services to your data center, colocation facility, or edge location. This supports workloads that require low-latency access to on-premises systems, local data processing, or data residency. AWS Organizations provides a foundation for managing multiple AWS accounts. You share an Outpost rack across accounts in the same organization using AWS Resource Access Manager (AWS RAM). AWS services and APIs provide the underlying infrastructure and account-level controls.
Comquest Brunei, a Brunei-based technology and cloud services partner, uses CloudPrimus to operate an Outpost environment on behalf of several business units and customers. With this model, Comquest has cut provisioning time by 50% and reduced manual capacity tickets by 45% compared with its previous ticket-based process, based on Comquest’s internal operational data. Throughout the post, tenant refers to a separate AWS account consuming capacity from a single, shared Outpost within an organization environment.
Augmenting native AWS Outposts capabilities at scale
With CloudPrimus, Cloud Management Platform (CMP) teams can operate cloud infrastructure without routing every request through a central IT ticket queue. They can also avoid exposing the AWS Management Console and APIs to every team. CloudPrimus provides two core capabilities for managing Outposts operations:
- Cloud identity and tenant management: Federate identities from your on-premises corporate identity provider. Define tenant boundaries and assign role-based access to control resources.
- Capacity and billing management: Provide a self-service catalog and orchestration engine for AWS APIs. Approval workflows and capacity controls govern provisioning, while consolidated billing covers Outpost and AWS Region consumption.
Together, these give you a single control point for the Outposts service lifecycle.
How CloudPrimus manages the Outposts lifecycle
CloudPrimus extends Outposts operations with automated workflows for capacity management, service provisioning, monitoring, and billing. CloudPrimus supports managed SaaS delivery. The following workflow shows how CloudPrimus supports the Outposts lifecycle, from initial discovery and account setup through capacity allocation, provisioning, monitoring, and billing.
- Connect and discover: Find Outposts resources and available capacity across AWS accounts and Outposts deployments to establish a centralized operational view.
- Manage accounts and access: Align tenants with your AWS Organizations, business units, and organizational structures, while applying role-based access controls and approval workflows.
- Allocate shared capacity: Track allocated, consumed, and available capacity across tenants to improve utilization and support informed allocation decisions.
- Simplify service provisioning: Authorized users can request approved services, including Amazon EC2, Amazon EBS, Application Load Balancer (ALB), customer-owned IP (COIP) addresses, and Amazon S3 on Outposts, through the self-service portal.
- Monitor usage and plan capacity: Tenants can see their resource consumption and request additional capacity. Administrators can reallocate available capacity or plan an Outpost expansion when physical capacity limits are reached.
- Attribute and consolidate billing: Attribute resources and usage to the correct account. You can view consolidated billing across Outpost and parent AWS Region consumption for unified showback or chargeback.
Tenant Dashboard – CloudPrimus tenant dashboard with tiles for Account Management, Service Catalog, Service Management, Quota Allocation, and Service Request.
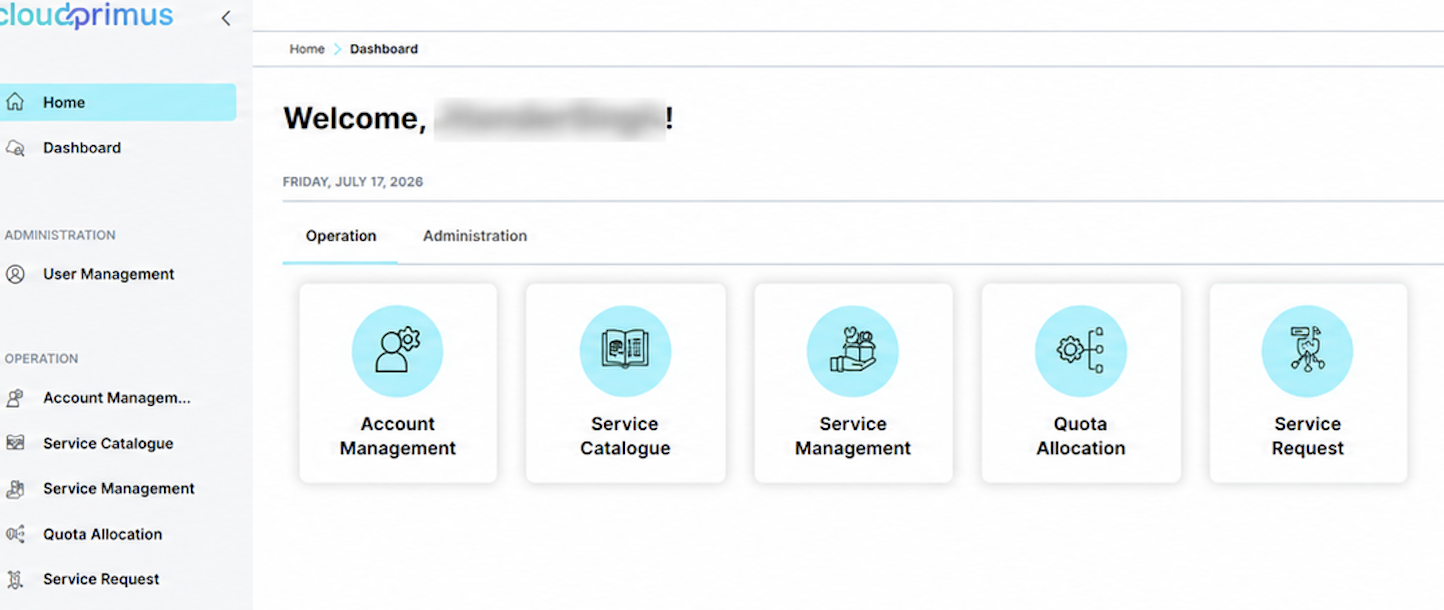 Figure 1. Tenant dashboard with direct access to CloudPrimus service modules.
Self-service provisioning and management through CloudPrimus
CloudPrimus provides a self-service catalog scoped to the capabilities of the target Outpost. Authorized users can request approved resources within defined tenant allocations. This reduces provisioning delays and administrative overhead while maintaining governance.
- Amazon EC2 instances: Provide a catalog of instance types and sizes available on the target Outpost for consistent, approval-based provisioning.
- Amazon S3 on Outposts: Automate bucket, endpoint, and access point configuration using standardized access policies and encryption baselines.
- Application Load Balancer: Simplify load balancer provisioning with reusable target group and listener configurations that keep networking and security practices consistent.
- Customer-owned IP (COIP) addresses: Authorized users can select addresses from approved COIP pools during deployment, which reduces manual IP allocation while enforcing tenant and network policies.
CloudPrimus tags every resource at creation with the requesting account, department, and cost center.
Service Catalog – CloudPrimus service catalog listing Outpost services such as EC2, S3, ALB. Each service shows whether quota is available.
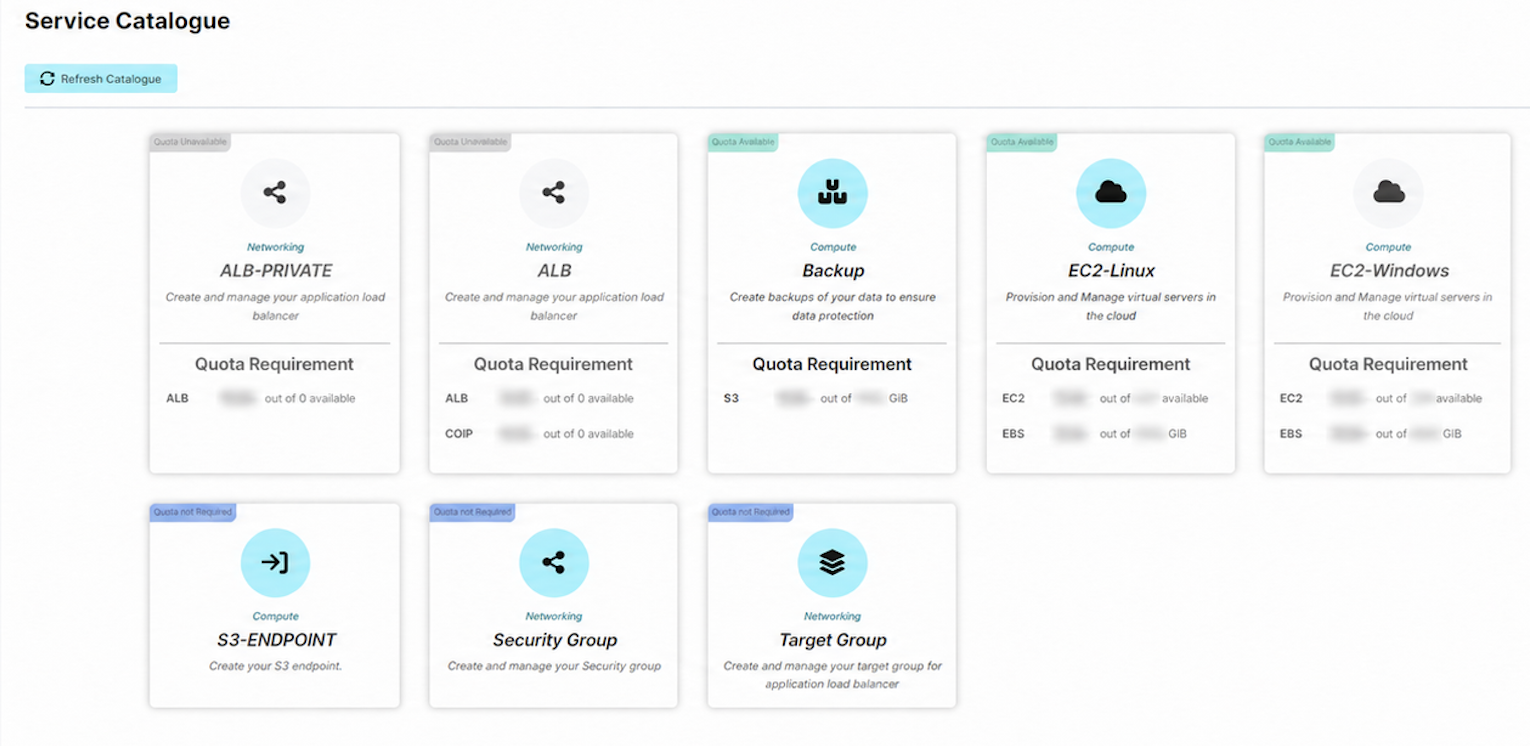
Figure 2. Tenant service catalog showing Outpost services and quota requirements.
Per-tenant capacity and quota management
CloudPrimus holds the capacity configuration of each Outpost and traces every provisioned resource back to the requesting account.
- Per-account allocations: CloudPrimus administrators assign soft or hard limits for Amazon EC2, Amazon EBS, Amazon S3 on Outposts, and other catalog resources, according to each tenant’s entitlement.
- Pre-provision validation: CloudPrimus checks each request against the tenant’s remaining allocation and the Outpost’s actual available capacity before it proceeds.
- Threshold visibility and alerts: Administrators and tenants can see consumption against allocation and get an early warning as usage nears a threshold.
- Additional-capacity requests: A tenant can request additional capacity directly from CloudPrimus, providing the required service, quantity, business justification, and target date for review and approval.
Service Quotas provides quota controls for supported AWS services in an AWS Region. CloudPrimus complements these controls with tenant-level allocation and pre-provisioning checks against the capacity available on a shared Outpost.
Quota allocation – CloudPrimus quota table showing allocated and used capacity for each Outpost service.
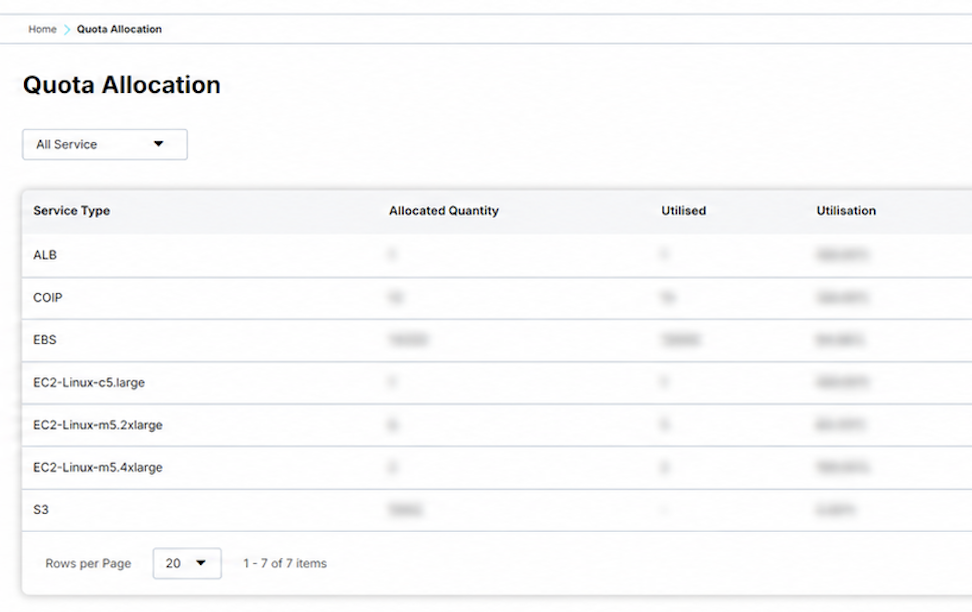
Figure 3. Tenant quota allocation and utilization by Outpost service.
Tenant, user, and role management
CloudPrimus provides a central platform for operating multiple customer tenants, while keeping each account, resources, approvals, and commercial information logically separated:
- Tenant management: Create and maintain tenant profiles and map them to cost centers or departments. Assign service entitlements and associate each tenant with an approved capacity allocation.
- User lifecycle management: Onboard, update, suspend, or remove users directly or through synchronization with the organization’s identity source.
- Role-based access control: Separate responsibilities among platform administrators, tenant administrators, requesters, approvers, operators, and billing viewers, so users receive only the access their role requires.
- Tenant-scoped visibility and audit: Users are scoped to authorized requests, resources, capacity, and billing, while administrators keep a complete audit trail across tenants.
Tenant management – CloudPrimus tenant management page listing active tenants.
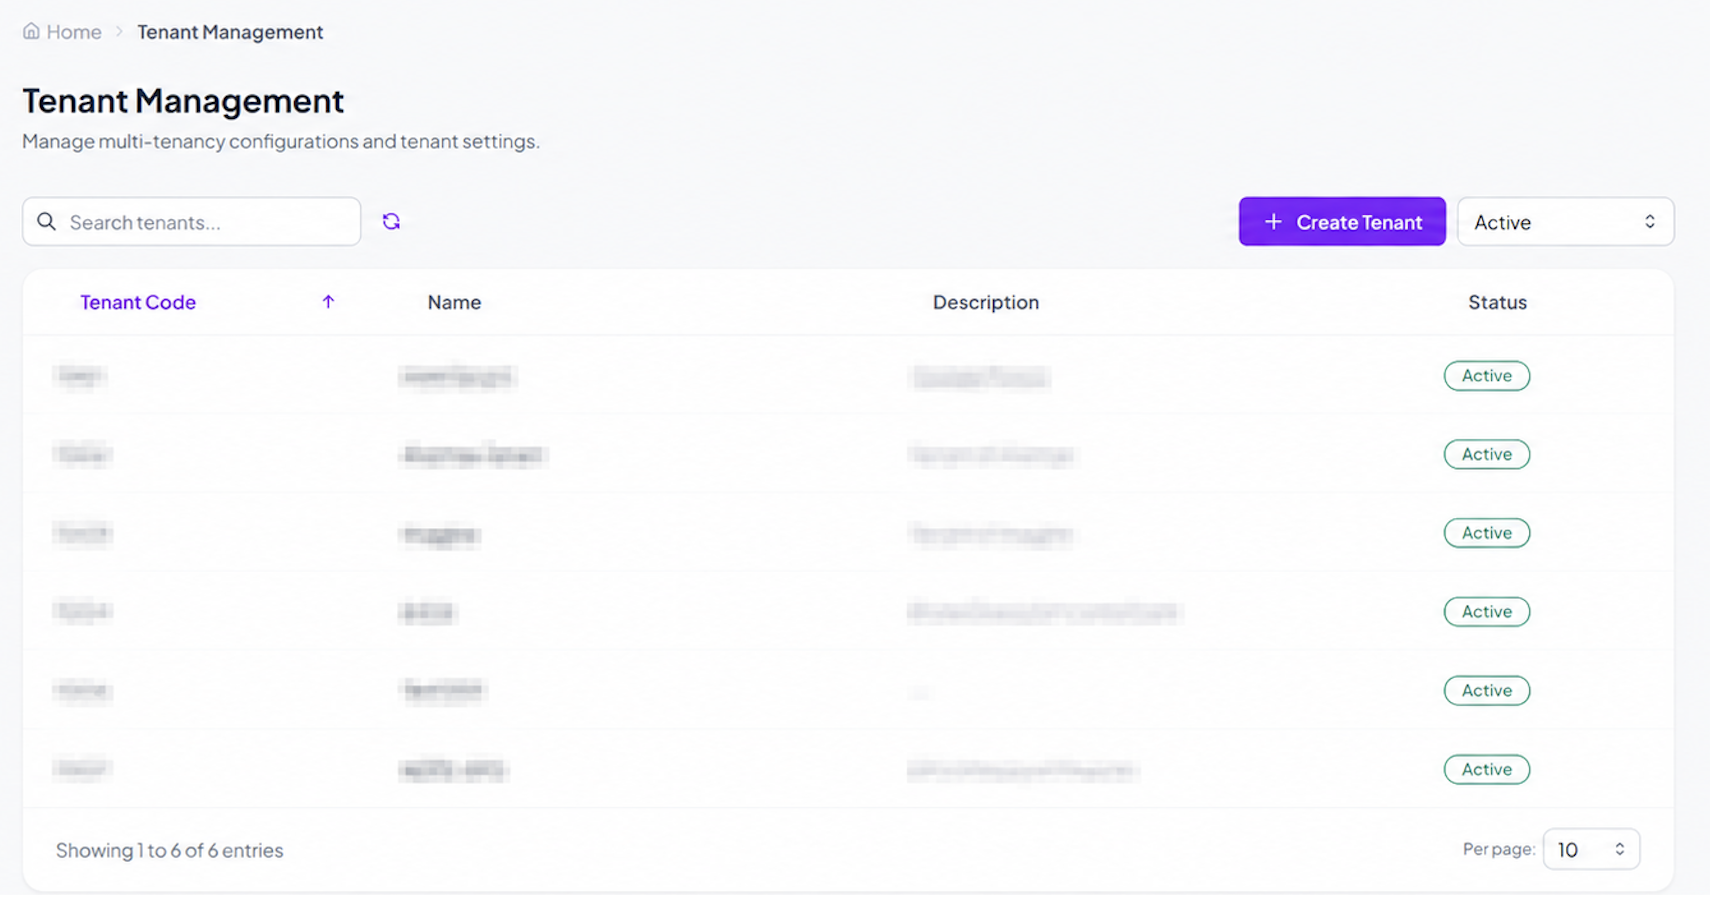
Figure 4. Tenant management for shared CloudPrimus environments.
Consolidated billing across your Outpost and the parent AWS Region
CloudPrimus attributes resources and usage to the correct account and consolidates consumption on your Outpost and in the parent AWS Region into one billing module. This can reduce the need for separate reports and manual reconciliation, giving you a consistent account-level view.
Billing report – CloudPrimus monthly billing report with charges for Outpost services, including EC2, EBS, S3, ALB, and COIP.
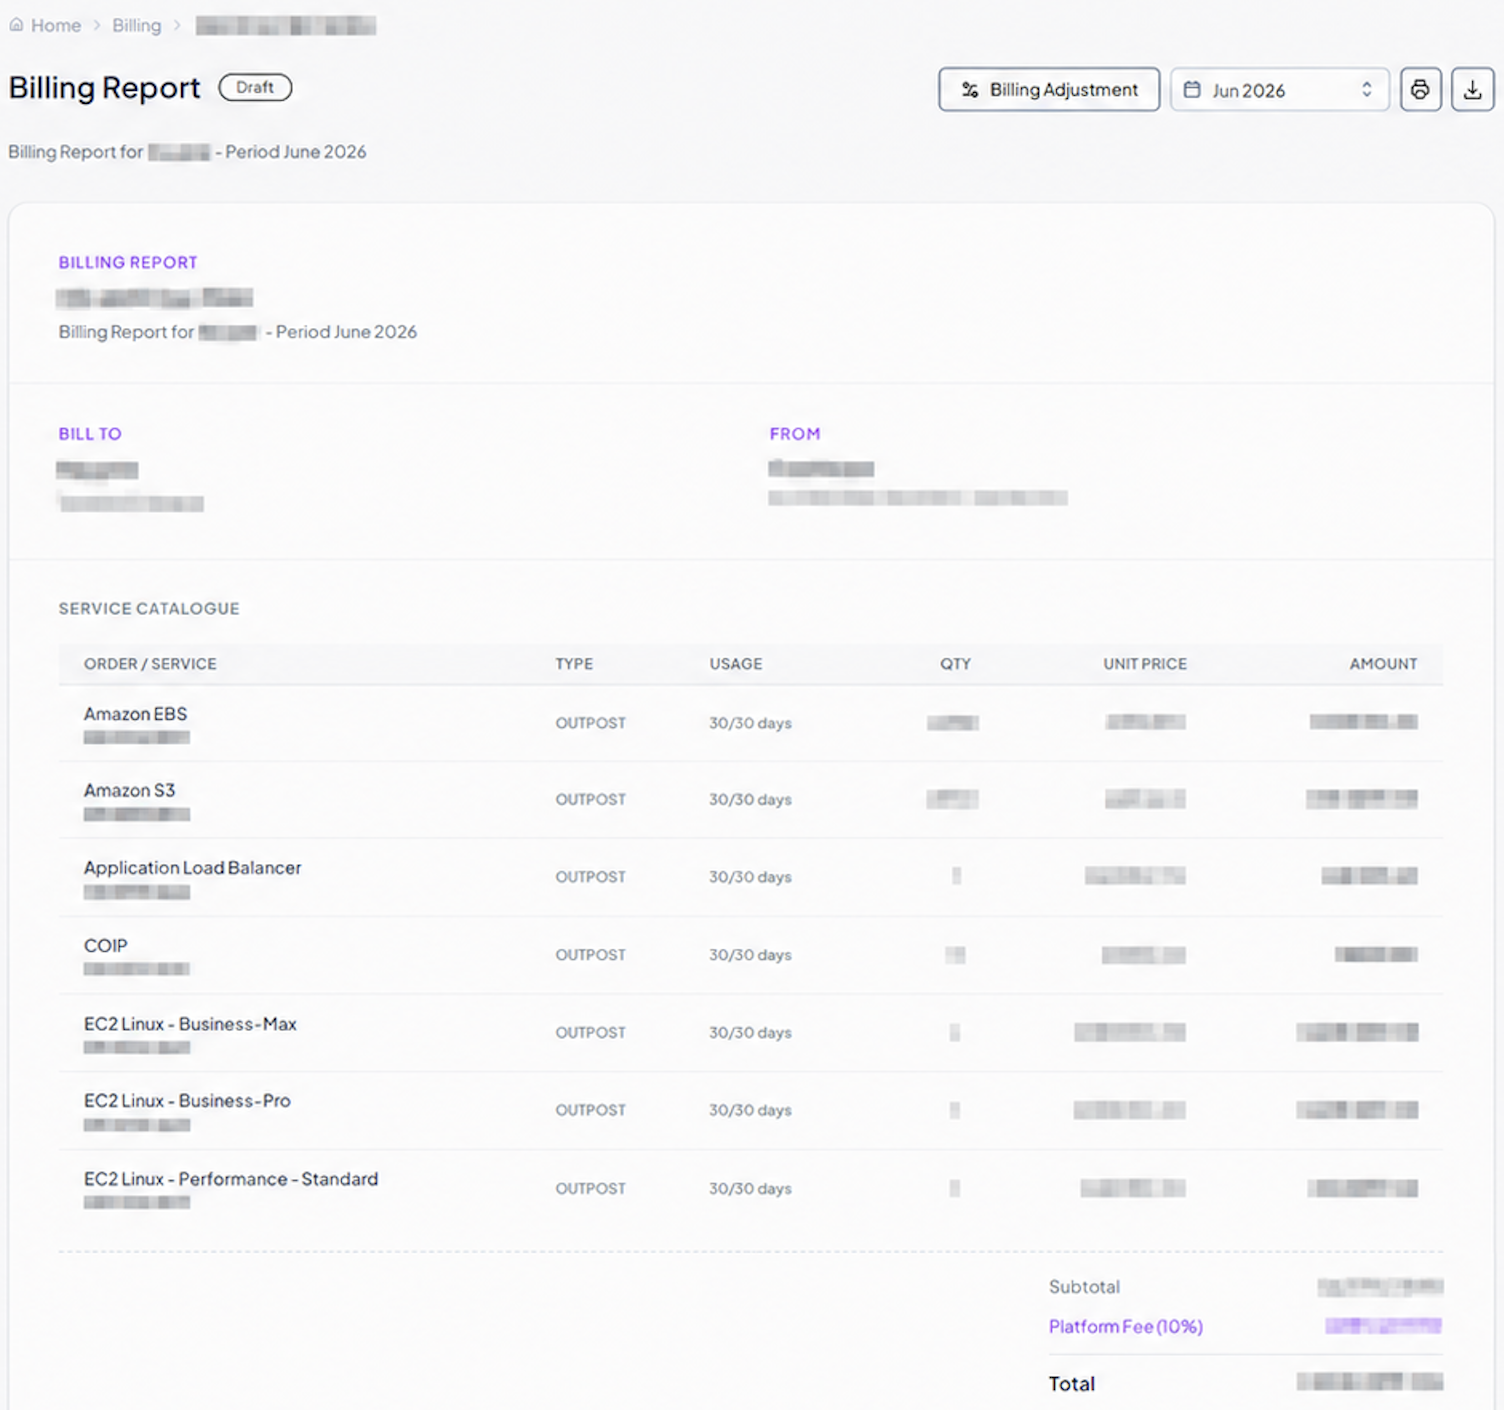
Figure 5. Tenant billing report for Outpost consumption and consolidated charges.
Organizations often run Outposts in regulated environments, including government agencies, financial services firms, and shared-services providers. Several business units might consume a single physical Outpost, which makes granular cost attribution important for governance and cost visibility.
Conclusion
In this post, we showed you how CloudPrimus builds on Outposts and AWS Organizations to help you manage tenant administration, self-service provisioning, shared-capacity governance, and consolidated billing. If you operate a shared Outpost across multiple AWS accounts, start by opening the AWS Outposts console and comparing installed capacity against the accounts consuming it. For more information, see the AWS Outposts User Guide and the Guidance for Multi-Account Outposts Operations on AWS. To discuss CloudPrimus for your environment, contact your AWS account team and Xtremax.
The content and opinions in this blog are those of the third-party author and AWS is not responsible for the content or accuracy of this blog.
Xtremax – AWS Partner Spotlight
Xtremax is an AWS Advanced Tier Partner and AWS Managed Service Provider (MSP) who delivers cloud engagements across public sector, financial services, and enterprise customers in Southeast Asia.