AWS Security Blog
Category: Security, Identity, & Compliance

How to Use SAML to Automatically Direct Federated Users to a Specific AWS Management Console Page
Identity federation enables your enterprise users (such as Active Directory users) to access the AWS Management Console via single sign-on (SSO) by using their existing credentials. In Security Assertion Markup Language (SAML) 2.0, RelayState is an optional parameter that identifies a specified destination URL your users will access after signing in with SSO. When using […]

How to Use the REST API to Encrypt S3 Objects by Using AWS KMS
August 4, 2023: This blog post is out of date, and is in the process of being updated. AWS Key Management Service (AWS KMS) allows you to use keys under your control to encrypt data at rest stored in Amazon S3. The two primary methods for implementing this encryption are server-side encryption (SSE) and client-side […]

Frequently Asked Questions About HIPAA Compliance in the AWS Cloud: Part Two
July 19, 2021: We’ve updated this post to clarify PHI encryption requirements for Amazon CloudWatch Logs. In a previous blog post, Frequently Asked Questions About HIPAA Compliance in the AWS Cloud, I looked at some of the broad questions you have asked us about running protected health information (PHI) in the AWS cloud. In this […]

How to Control Access to Your Amazon Elasticsearch Service Domain
September 9, 2021: Amazon Elasticsearch Service has been renamed to Amazon OpenSearch Service. See details. With the recent release of Amazon Elasticsearch Service (Amazon ES), you now can build applications without setting up and maintaining your own search cluster on Amazon EC2. One of the key benefits of using Amazon ES is that you can […]

How to Import IP Address Reputation Lists to Automatically Update AWS WAF IP Blacklists
Note from July 3, 2017: The solution in this post has been integrated into AWS WAF Security Automations, and AWS maintains up-to-date solution code in the companion GitHub repository. You can use AWS WAF (a web application firewall) to help protect your web applications from exploits that originate from groups of IP addresses that are known […]
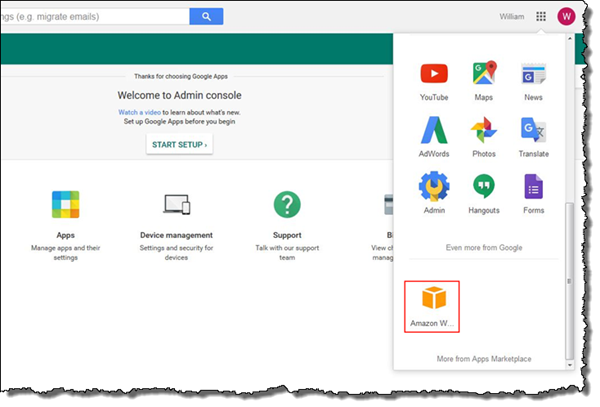
How to Set Up Federated Single Sign-On to AWS Using Google Apps
March 10, 2020: This blog post is out of date. Please refer to this post for updated info: How to set up federated single sign-on to AWS using Google Workspace The AWS Security Blog has covered a variety of solutions for federating single sign-on (SSO) to the AWS Management Console. For example, How to Connect […]
Frequently Asked Questions About HIPAA Compliance in the AWS Cloud
Today, we continue a series of AWS cloud compliance FAQs by focusing on the Health Insurance Portability and Accountability Act (HIPAA) and protected health information (PHI). AWS’s Healthcare and Life Science customers are doing important things for their customers in the AWS cloud, and we are excited to work with our partners to help tackle […]

How to Enable Windows Integrated Authentication for RDS for SQL Server Using On-Premises Active Directory
On March 23, 2016, AWS announced that Amazon Relational Database Service for SQL Server (RDS for SQL Server) now supports authentication to AWS Directory Service for Microsoft Active Directory (Enterprise Edition), also known as Microsoft AD. On April 7, 2016, AWS launched a new console feature for Microsoft AD that makes it easy for you […]

Now Available: Simplified Configuration of Trust Relationships in the AWS Directory Service Console
Today, we made it easier for you to configure trust relationships between AWS Directory Service for Microsoft Active Directory (Enterprise Edition), also referred to as Microsoft AD, and your on-premises Microsoft Active Directory. Establishing trust relationships requires conditional forwarders, which resolve Domain Name System (DNS) queries between the domain names of trusting directories. Now, by […]

Frequently Asked Questions About Compliance in the AWS Cloud
May 22, 2019 update: We’ve removed a reference to the IT-Grundschutz Certification Workbook. AWS now recommends that customers refer to the Cloud Computing Compliance Controls Catalog (C5) instead. Learn more about C5 here: https://aws.amazon.com/compliance/bsi-c5/ Every month, AWS Compliance fields thousands of questions about how to achieve and maintain compliance in the cloud. Among other things, […]