AWS Security Blog
Category: AWS WAF
Introducing the new AWS WAF security analytics dashboard
When blocked requests spike or a customer reports being locked out, a security team has to work out what is happening, where it is happening, and if AWS WAF is making the right call. Currently, that usually means opening each protection pack (web ACL) in turn, across domains, AWS Regions, and Amazon CloudFront distributions, or […]
Introducing simplified onboarding for AWS WAF Bot Control at the targeted inspection level
Today, we’re announcing simplified onboarding and bot confidence levels for AWS WAF Bot Control at the targeted inspection level, which we refer to as Targeted bot control in this post, matching the console. Bot confidence levels and the new LATEST rule group version are available for the resource types that AWS WAF protects: you act […]
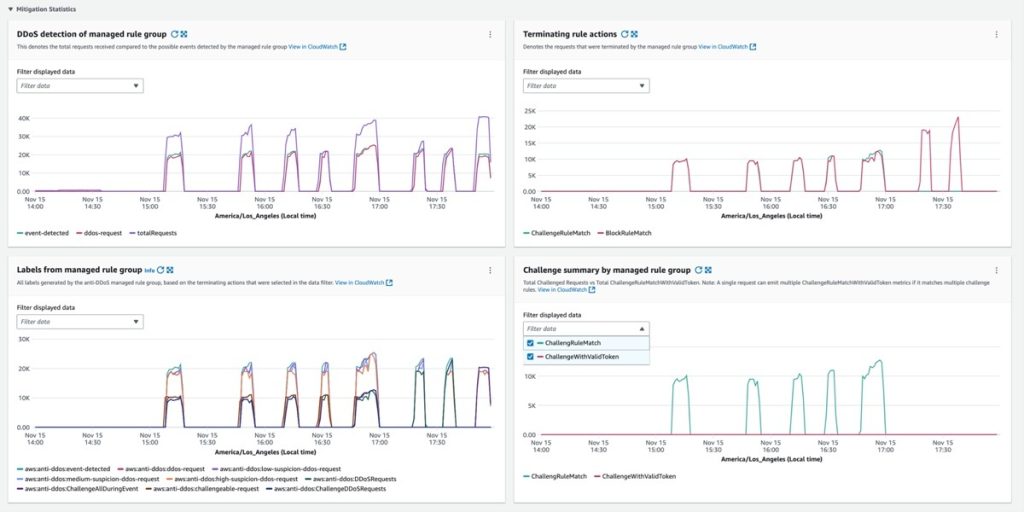
AWS Shield Advanced is embracing the AWS WAF Anti-DDoS managed rule group: What changes and how to prepare
October 5, 2026: We clarified Anti-DDoS AMR configuration details during auto-upgrade. September 14, 2026: AWS has updated the current auto-migration from October 1, 2026, to October 25, 2026, and postponed the Shield Advanced application-layer automatic mitigation sunset from December 31, 2026, to January 29, 2027. We’ve updated the post to reflect these changes. July 29, […]
Do more with AWS WAF labels using dynamic label interpolation
September 29, 2026: This post was updated to clarify the header names that AWS WAF inserts. AWS WAF classifies web traffic by attaching metadata to each request it evaluates. Managed rule groups such as AWS WAF Bot Control and AWS WAF Fraud Control account takeover prevention (ATP) attach labels that describe what they found. A […]
Authenticate legitimate AI agent traffic with AWS WAF Bot Control
As AI agents and automated tools increasingly access web applications, distinguishing legitimate bot traffic from malicious attempts has become a critical security challenge. Traditional approaches such as IP-based filtering and reverse DNS lookups fail in multi-tenant systems (such as Amazon Bedrock AgentCore) where thousands of distinct workloads share the same IP space. Attackers can easily […]
Complimentary virtual training: Get hands-on with AWS Security Services
If you’re looking to strengthen your organization’s security posture on Amazon Web Services (AWS) but aren’t sure where to start, then we’re here to help. Security Activation Days are complimentary, virtual, hands-on workshops designed to help you get practical experience with AWS security services in a single session. What to expect Each Security Activation Day […]
Introducing AI traffic analysis dashboards for AWS WAF
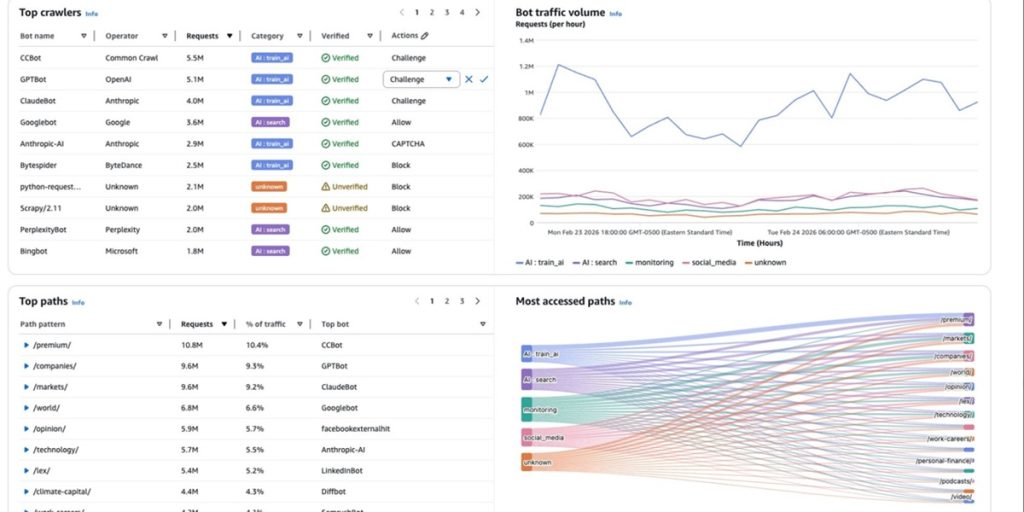
October 13, 2026: We updated this post to add a dashboard screenshot and to cover AWS WAF AI traffic monetization, which lets you charge AI bots for content access. As AI agents, bots, and programmatic access become an increasingly significant portion of web traffic, organizations need better tools to understand, analyze, and manage this activity. […]
Security posture improvement in the AI era
It’s only been a few weeks since Anthropic announced the Claude Mythos Preview model and launched Project Glasswing with AWS and other leading organizations. This has generated a lot of discussion about the future of cybersecurity and what the ever-increasing capabilities of foundation models mean to organizations. As AWS CISO Amy Herzog pointed out in […]
How to customize your response to layer 7 DDoS attacks using AWS WAF Anti-DDoS AMR
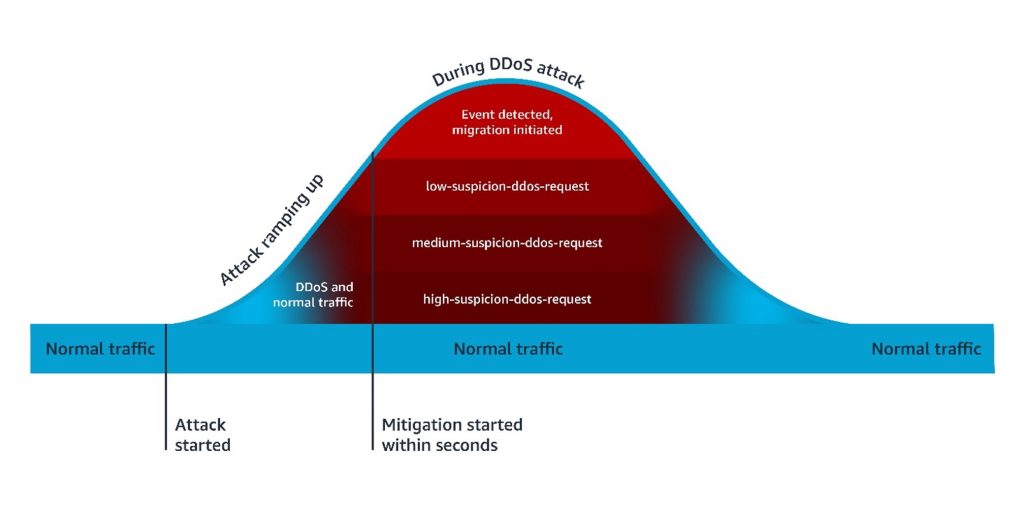
Over the first half of this year, AWS WAF introduced new application-layer protections to address the growing trend of short-lived, high-throughput Layer 7 (L7) distributed denial of service (DDoS) attacks. These protections are provided through the AWS WAF Anti-DDoS AWS Managed Rules (Anti-DDoS AMR) rule group. While the default configuration is effective for most workloads, […]

Introducing the new console experience for AWS WAF
Protecting publicly facing web applications can be challenging due to the constantly evolving threat landscape. You must defend against sophisticated threats, including zero-day vulnerabilities, automated events, and changing compliance requirements. Navigating through consoles and selecting the protections best suited to your use case can be complicated, requiring not only security expertise but also a deep […]