AWS Security Blog
Category: Amazon Simple Storage Service (S3)

IAM Policies and Bucket Policies and ACLs! Oh, My! (Controlling Access to S3 Resources)
September 11, 2023: This post has been updated. Updated on July 6, 2023: This post has been updated to reflect the current guidance around the usage of S3 ACL and to include S3 Access Points and the Block Public Access for accounts and S3 buckets. Updated on April 27, 2023: Amazon S3 now automatically enables […]

Top 10 security best practices for securing data in Amazon S3
With more than 100 trillion objects in Amazon Simple Storage Service (Amazon S3) and an almost unimaginably broad set of use cases, securing data stored in Amazon S3 is important for every organization. So, we’ve curated the top 10 controls for securing your data in S3. By default, all S3 buckets are private and can […]

How to securely create and store your CRL for AWS Private CA
June 25, 2025: As of Sept 28, 2022, AWS has changed the name of ACM Private CA to AWS Private CA. This post has been updated to reflect this change. December 4, 2023:We’ve updated the new Amazon CloudFront security feature Origin Access Control in place of the Origin Access Identity. December 14, 2021:The code in […]
Use IAM Access Analyzer to generate IAM policies based on access activity found in your organization trail
January 25, 2024: The path of the bucket was updated in this post. In April 2021, AWS Identity and Access Management (IAM) Access Analyzer added policy generation to help you create fine-grained policies based on AWS CloudTrail activity stored within your account. Now, we’re extending policy generation to enable you to generate policies based on […]

Strengthen the security of sensitive data stored in Amazon S3 by using additional AWS services
October 13, 2021: We’ve added a section on redacting and transforming personally identifiable information with Amazon S3 Object Lambda. In this post, we describe the AWS services that you can use to both detect and protect your data stored in Amazon Simple Storage Service (Amazon S3). When you analyze security in depth for your Amazon […]

How to scale your authorization needs by using attribute-based access control with S3
August 31, 2021: AWS KMS is replacing the term customer master key (CMK) with AWS KMS key and KMS key. The concept has not changed. To prevent breaking changes, AWS KMS is keeping some variations of this term. More info. May 26, 2021: In the section “Secure your tags using an AWS Organizations service control […]
Validate access to your S3 buckets before deploying permissions changes with IAM Access Analyzer
AWS Identity and Access Management (IAM) Access Analyzer helps you monitor and reduce access by using automated reasoning to generate comprehensive findings for resource access. Now, you can preview and validate public and cross-account access before deploying permission changes. For example, you can validate whether your S3 bucket would allow public access before deploying your […]

Learn and use 13 AWS security tools to implement SEC recommended protection of stored customer data in the cloud
Most businesses collect, process, and store sensitive customer data that needs to be secured to earn customer trust and protect customers against abuses. Regulated businesses must prove they meet guidelines established by regulatory bodies. As an example, in the capital markets, broker-dealers and investment advisors must demonstrate they address the guidelines proposed by the Office […]
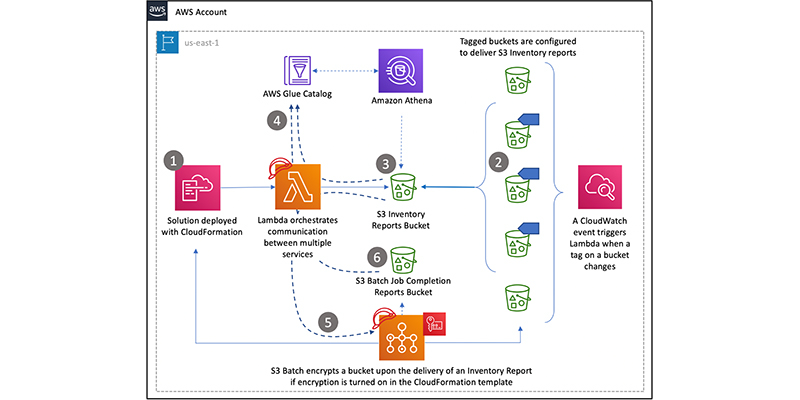
How to retroactively encrypt existing objects in Amazon S3 using S3 Inventory, Amazon Athena, and S3 Batch Operations
February 5, 2026: Amazon S3 now supports the UpdateObjectEncryption API so you can atomically update the server-side encryption type of existing encrypted objects from server-side encryption with S3 managed encryption (SSE-S3) to server-side encryption with AWS Key Management Service (AWS KMS) encryption keys (SSE-KMS). Read the documentation. November 1, 2021: AWS KMS is replacing the […]

Tighten S3 permissions for your IAM users and roles using access history of S3 actions
September 28, 2023: IAM is incrementally adding support for actions from more services. For a list of services that report action last accessed information, see IAM action last accessed information services and actions. Customers tell us that when their teams and projects are just getting started, administrators may grant broad access to inspire innovation and […]