AWS Architecture Blog
How Revinate accelerated API adoption with Amazon API Gateway
Accelerating API adoption while reducing operational overhead is a challenge that every growing organization faces. For Revinate, a hospitality provider serving over 12,500 hotels worldwide and powering more than 1.25 billion guest profiles, Amazon API Gateway became the foundation of their solution.
Revinate empowers hoteliers to connect directly with guests at every touchpoint, driving $24 billion in lifetime direct revenue through an AI-powered Customer Data Platform (CDP) that helps reduce reliance on online travel agencies (OTAs) and deliver data-driven insights.
With the expansion of CDP capabilities, Revinate needed to expose rich guest data through APIs, so that hotel properties and partners can programmatically access guest profiles, reservation data, and other critical hospitality information.
This post explores how Revinate used Amazon API Gateway and the newly released Amazon API Gateway Portal to create a scalable, secure, and developer-friendly API program.
Business need: Evolving API infrastructure to match growth
As Revinate expanded its CDP capabilities and began exposing guest profile and reservation data through APIs, the limitations of managing API infrastructure in-house became clear. Each new partner integration required manual provisioning, custom security configuration, and ongoing maintenance. The team needed an API gateway solution that could scale with growing partner demand without adding operational burden. Rather than building and maintaining a self-hosted solution, Revinate wanted an approach that would open up engineering time, streamline partner integrations, and align infrastructure costs with actual usage. The team identified four key business drivers:
- Operational efficiency and agility – Accelerate API deployment cycles and reduce time spent on infrastructure maintenance so the engineering team can focus on building features that directly serve customers.
- Faster partner and developer onboarding – Helping external developers and partners to discover and adopt Revinate’s APIs required a faster, more self-service experience.
- Growth aligned costs – Infrastructure costs needed to scale proportionately with revenue generation. An on-demand pricing model, where costs flex with actual API usage rather than fixed overhead, was essential to support sustainable growth. Equally important was the ability to attribute API costs per consumer, enabling transparent cost allocation across hotel properties and partners.
- Enhanced security and compliance – API security controls including authentication, authorization, rate limiting, and threat protection. Meeting compliance requirements and maintaining customer trust demanded strong security without adding complexity to the development workflow or requiring the team to build and maintain custom security infrastructure.
These requirements shaped the team’s evaluation of available solutions.
Evaluating alternatives
When evaluating API gateway solutions, the team translated the business drivers into four core technical requirements. On-demand pricing was essential to align infrastructure costs with actual API usage and enable per-consumer cost attribution. Authentication federation allows integration with Revinate’s existing identity provider, so partners can onboard faster without building custom auth infrastructure. Rate limiting was needed to protect backend services and enforce fair usage across hotel properties and partners as the API program scales. Finally, strong security, including threat protection, audit logging, and access controls, was required to meet compliance requirements for protecting sensitive guest data.
The engineering team evaluated three approaches. Each approach came with distinct tradeoffs across cost, flexibility, and operational burden.
Self-managed API management
Deploying a self-managed API gateway would provide flexibility and avoid licensing fees, but requires ongoing infrastructure management, security patching, scaling, and monitoring. The team would also need to build a custom developer portal from scratch.
Custom-built
Building a proprietary API gateway tailored to Revinate’s exact needs offers maximum control but demands significant upfront development investment and ongoing maintenance. Every capability, including routing, authentication, rate limiting, and documentation, would need to be built and maintained in-house, diverting engineering resources from core hospitality platform features.
Enterprise API management platforms
Enterprise platforms offer comprehensive out-of-the-box features, but introduce vendor dependencies, higher costs, and fixed-term licensing models where costs misalign with revenue growth.
All three approaches shared a common drawback: they would divert resources, whether engineering time, budget, or both, toward capabilities that don’t differentiate Revinate’s product, delaying time-to-market for features that directly serve hotel customers.
The solution: Amazon API Gateway with Developer Portal
Revinate needed the comprehensive capabilities of an enterprise API management platform without the fixed-term licensing, vendor dependencies, and operational overhead. Amazon API Gateway, combined with the newly released Amazon API Gateway Portal, delivered exactly that, aligning with both the technical requirements and business objectives that shaped the evaluation.
Fully managed infrastructure
Amazon API Gateway removes the need to manage underlying infrastructure, so the engineering team can focus on the core hospitality solution rather than API gateway operations.
Native AWS integration
Amazon API Gateway provides native integration with other AWS services, including Amazon Elastic Kubernetes Service (Amazon EKS) for backend services and AWS Lambda authorizers for federated authentication with an external identity provider. This allows Revinate to authenticate API consumers against the existing identity provider infrastructure with minimal development effort.
Infrastructure as code with Terraform
The team maintains strict infrastructure-as-code practices, using Terraform exclusively for all production deployments. The AWS provider for Terraform enables defining the Amazon API Gateway configuration, including REST APIs, stages, usage plans, and authorizers as version-controlled code. This approach verifies consistency across environments, enables peer review of infrastructure changes, and provides complete audit trails for compliance requirements. The declarative nature of Terraform enables rapidly iterating on the API Gateway configuration during development while maintaining confidence in production deployments.
Cost-effective pay-per-use model
Amazon API Gateway’s pay-per-use pricing model aligned perfectly with Revinate’s growth strategy. During the initial rollout phase, costs remained minimal and scaled naturally as new API consumers onboarded. Usage plans allow Revinate to track and attribute costs per consumer, providing clear visibility into which hotel properties and partners drive API usage. This per-consumer cost attribution, combined with tiered pricing that scales from tens to hundreds of customers, replaced fixed annual licensing fees that required upfront investment regardless of actual usage.
Managed Developer Portal
The November 2025 release of Amazon API Gateway Portal provided a fully managed, AWS-native Developer Portal that served as the central hub for API discovery, documentation, and governance. This removes months of custom development work that building a comparable solution would require.
Developers can use the managed portal to:
- Set up a branded Developer Portal in minutes rather than months.
- Provide hotel property developers with self-service API discovery and interactive documentation.
- Maintain centralized control over API documentation freshness and access governance.
- Deliver a professional developer experience that accelerates customer onboarding from weeks to days.
Strong security
API Gateway provides built-in security features that meet stringent requirements for protecting sensitive guest data:
- OAuth2 client credentials for machine-to-machine (M2M) authentication.
- Authorization logic using AWS Lambda authorizers integrating with an external identity provider of choice.
- Request throttling and quota management to prevent abuse.
- Integration with AWS WAF and Amazon CloudFront for layered protection against common web exploits and DDoS threats.
- Comprehensive audit logging through AWS CloudTrail for compliance and access tracking.
- Real-time observability through Amazon CloudWatch metrics and dashboards, with support for streaming to third-party observability platforms.
Architecture overview
The solution uses a modern, scalable AWS architecture designed to serve hotel properties globally. Hotel properties access the platform as API consumers through Amazon CloudFront for edge caching and low-latency responses, with AWS WAF providing comprehensive protection against common web threats and bots. Requests flow through Amazon API Gateway, which serves as the unified entry point for API operations. Lambda authorizers handle authentication and authorization by integrating with an identity provider (IdP) to provide secure, token-based access control for each request. After authentication, API Gateway routes traffic to backend services running on Amazon EKS, providing the flexibility and scalability needed for containerized microservices. The EKS application layer orchestrates requests to the Customer Data Platform.
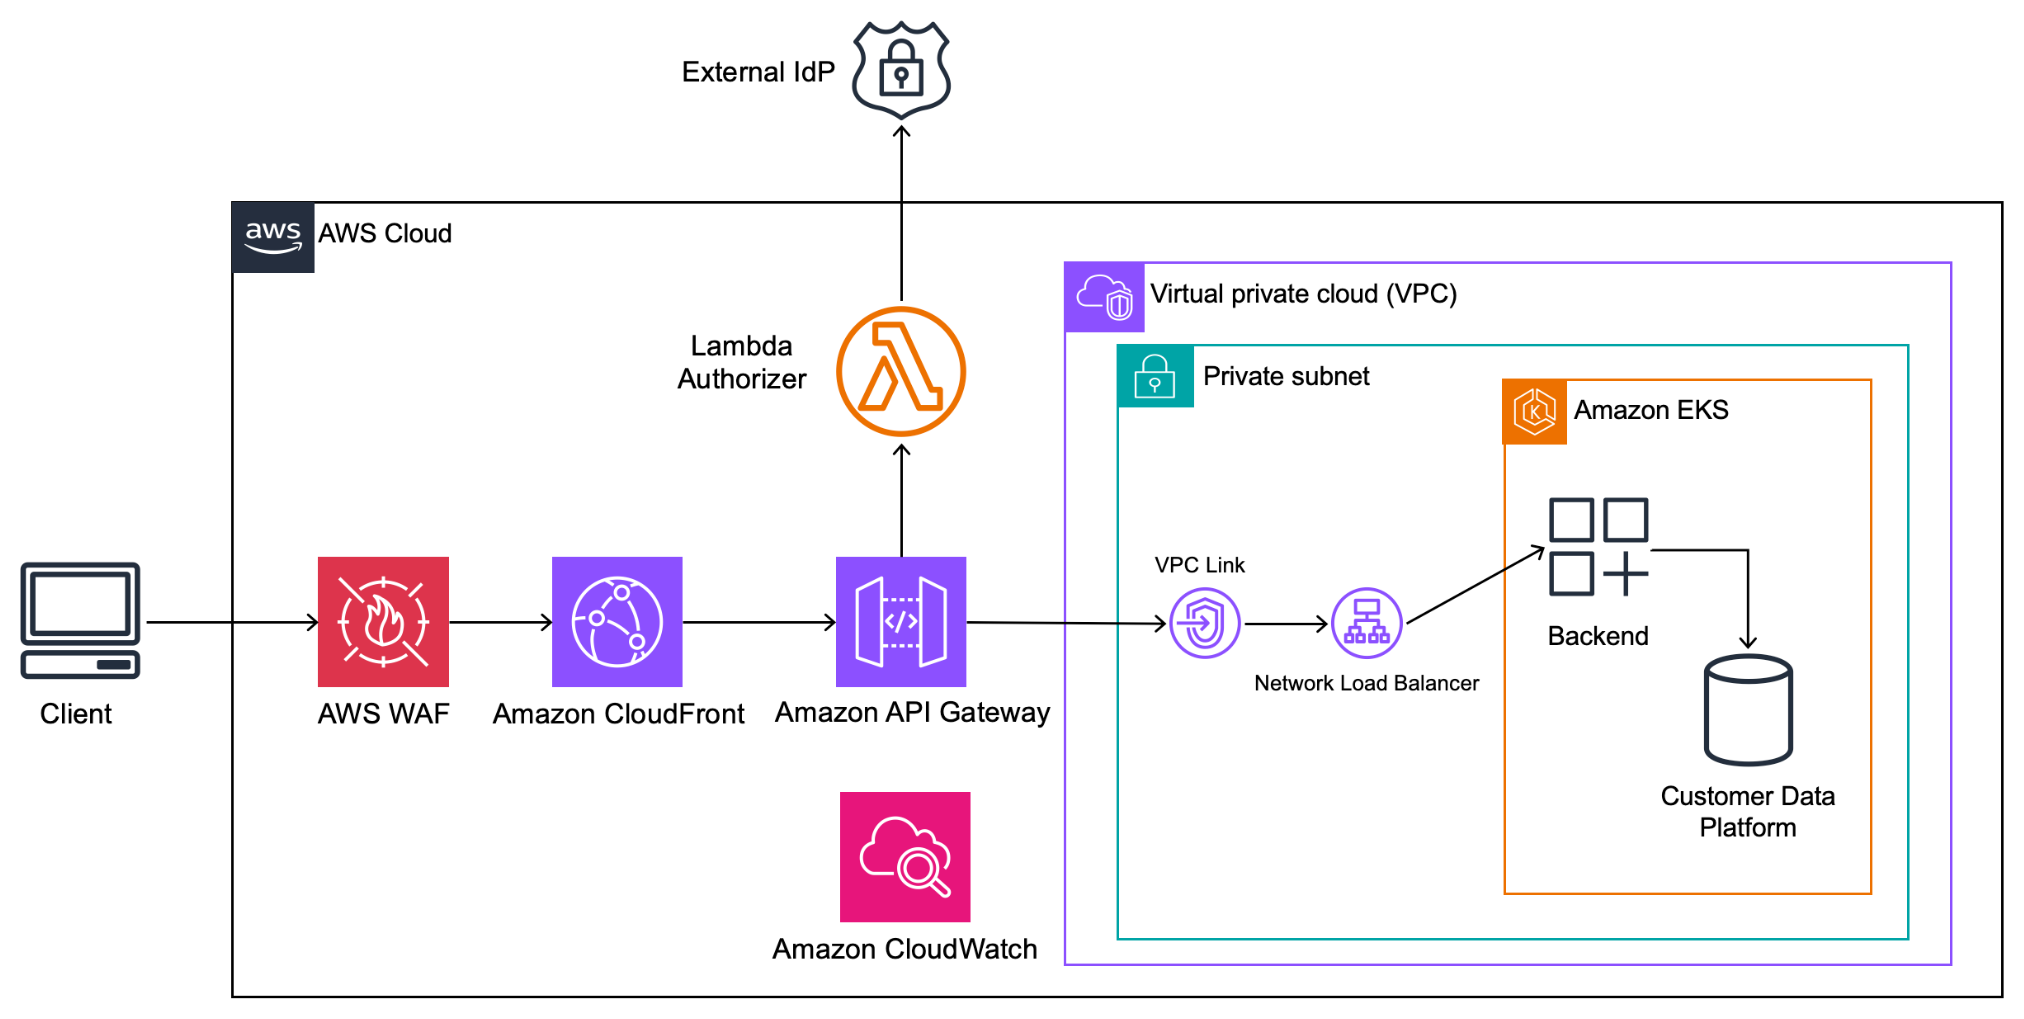
Figure 1: Architecture diagram showing the end-to-end flow from hotel property consumers accessing the Amazon API Gateway Portal, through Amazon API Gateway, to backend services running on Amazon EKS.
Connecting API Gateway to EKS
A critical design decision emerged: how to securely and efficiently connect API Gateway to backend services in Amazon EKS while keeping traffic within the AWS backbone network using VPC Link. The team evaluated four options:
Option 1: NGINX ingress controller: Route traffic through a Kubernetes-native NGINX Ingress Controller with a Load Balancer service.
Pros: Highly customizable routing, flexible header manipulation, consistent with common Kubernetes patterns.
Cons: Adds extra latency hop, requires manual lifecycle management (upgrades, configs, scaling), non-AWS-native monitoring.
Option 2: AWS load balancer controller: Use the AWS Load Balancer Controller to manage LB resources as Kubernetes Ingress objects.
Pros: Bridges AWS and Kubernetes natively, supports path-based routing, AWS-managed Load Balancer (LB) lifecycle.
Cons: Introduces an additional hop (Amazon API Gateway → LB → service).
Option 3: Target group binding: Directly bind Amazon EKS pods to Network Load Balancer (NLB) Target Groups using the AWS Load Balancer Controller’s TargetGroupBinding feature.
Pros: Removes ingress controller overhead, lowest latency, native AWS integration, cost-efficient (shared NLB across multiple Target Groups), fine-grained control over health checks and scaling.
Cons: More complex initial setup, less Kubernetes-native (more AWS-specific), different applications will need individual NLB.
Option 4: LoadBalancer service: Expose each service directly via a Kubernetes LoadBalancer service (NLB/ALB).
Pros: Most straightforward setup, minimal routing complexity, no ingress controller needed.
Cons: No path-based routing, costly at scale (each service requires its own load balancer), limited observability, requires TLS offloading configuration, different applications will need individual NLB.
The team selected Target group binding because it effectively balances performance, cost-efficiency, and AWS-native integration. By removing the extra hop introduced by traditional ingress controllers, this approach provides direct control over Target Groups and health checks while maintaining sub-second latency at scale.
Security implementation
The API Gateway implementation uses OAuth 2.0 client credentials flow with an external identity provider, delivering strong authentication for machine-to-machine (M2M) communication. This approach provides secure, scalable access control as Revinate onboards new hotel properties and partners.
API Gateway enforces usage plans with configurable throttling and quota limits, for fair usage and protection against abuse.
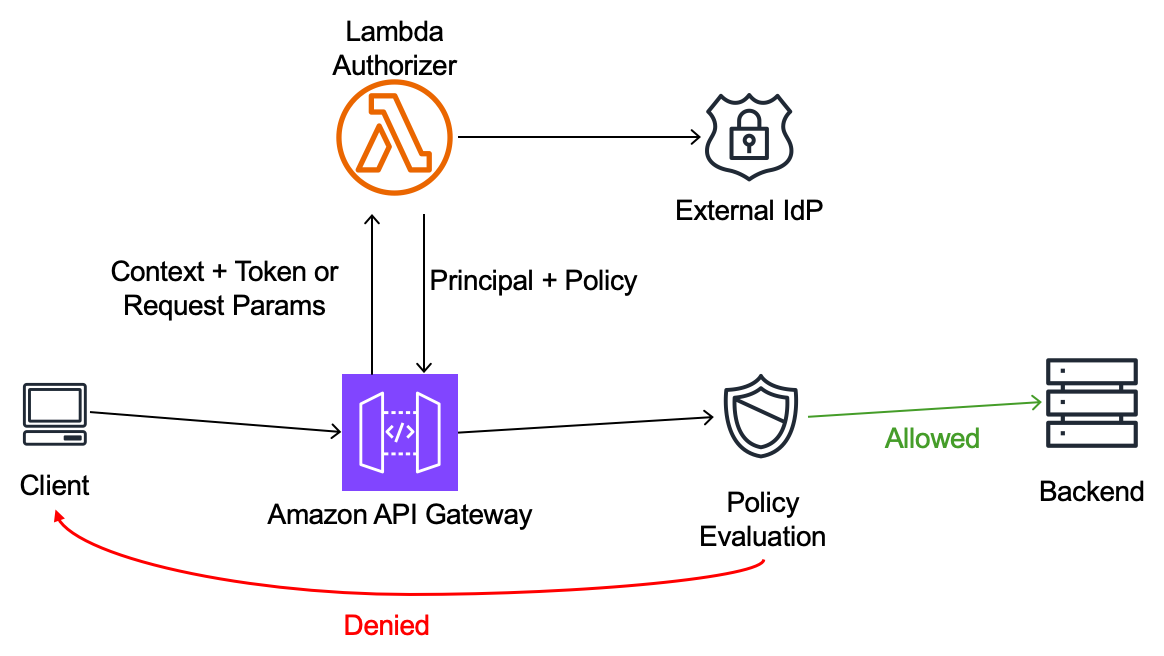
Figure 2: Sequence diagram illustrating the OAuth 2.0 authentication flow using AWS Lambda authorizers.
AWS Lambda authorizers take the caller’s identity as the input and return an IAM policy as the output. This architecture provides flexibility to implement sophisticated authorization logic while maintaining the simplicity of the API Gateway managed infrastructure. The team also deploys and manages the Lambda authorizer functions through Terraform, maintaining infrastructure as code (IaC) standards.
Developer Portal experience
The Amazon API Gateway Portal serves as the central hub for the API operations, providing developers using APIs with a streamlined experience.
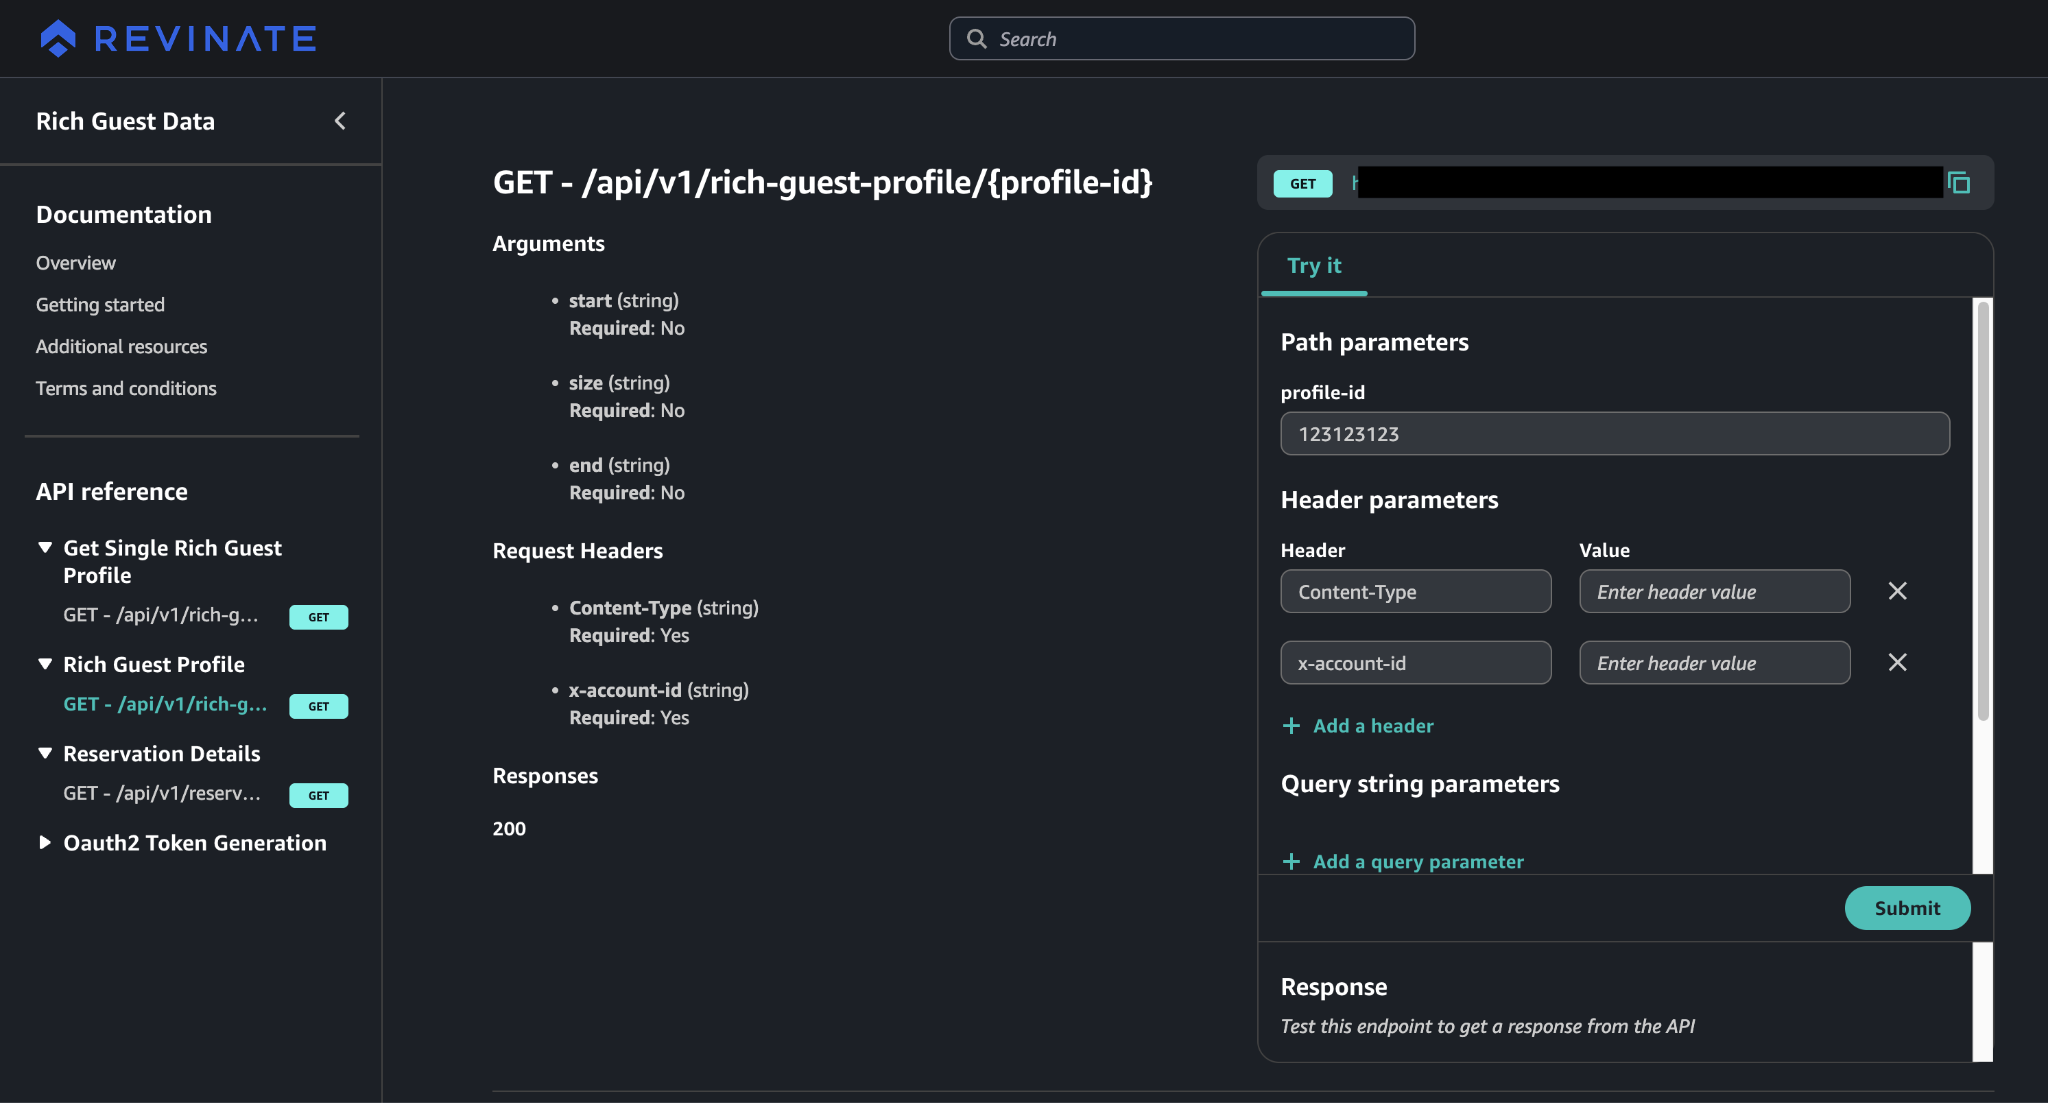
Figure 3: User interface flow showing the developer journey through the Amazon API Gateway Portal, including API discovery, interactive documentation with try-it-now functionality, and subscription management.
Developers can:
- Browse available REST APIs with comprehensive documentation.
- Test API endpoints directly in the portal with interactive examples.
- Access code samples and integration guides.
This self-service model reduced burden on support while accelerating customer time-to-value.
Results and benefits
The implementation of Amazon API Gateway and the Developer Portal delivered significant qualitative benefits across operational efficiency, developer experience, and business scalability.
Reduced operational overhead
By choosing a fully managed API gateway, the engineering team avoided the burden of maintaining, scaling, and troubleshooting self-hosted infrastructure. With the fully managed API gateway, the team can focus on core platform innovations that directly benefit hotel customers rather than undifferentiated gateway operations.
Improved developer experience
The centralized Developer Portal transformed the integration experience for hotel properties and partners. Self-service API discovery and interactive documentation reduced onboarding time from weeks to days. Developers consistently praised the professional portal experience and comprehensive documentation.
Accelerated customer onboarding
With the Developer Portal’s self-service capabilities, new customers can discover APIs and begin integration without waiting for manual provisioning or support intervention. This self-service approach positions Revinate to scale API access to hundreds of hotel properties and partners as demand grows.
Enhanced governance and control
The solution centralized control over API documentation, versioning, and access policies, verifying consistency across customer integrations. A single source of truth for API specifications removes documentation drift and reduces integration errors. Managing infrastructure through Terraform verifies changes follow proper review and approval processes.
Cost optimization
The pay-per-use pricing model aligns costs with actual usage and revenue generation. Usage plans and API keys provide per-consumer cost attribution, giving Revinate clear visibility into infrastructure spend by customer. As usage scales, tiered pricing verifies predictable cost growth that tracks with business value, replacing fixed licensing models that require upfront investment regardless of adoption.
Positioned for growth
The API layer, from Amazon API Gateway to the Developer Portal, scales automatically to meet demand without capacity planning or operational intervention. The team can confidently pursue growth targets knowing the API infrastructure will scale automatically.
Enhanced security posture
Amazon API Gateway provides strong security capabilities built into the platform, including centralized authentication and authorization mechanisms, request throttling and rate limiting to protect against abuse, and automatic threat protection through AWS Shield integration. Built-in security capabilities remove the need to build and maintain custom infrastructure while verifying consistent security policies across API endpoints. The centralized approach reduces the attack surface and provides comprehensive audit trails through CloudWatch integration, so the team can maintain robust security without additional operational overhead.
Key takeaways
The successful implementation of Amazon API Gateway and the Amazon API Gateway Portal offers valuable lessons for organizations exposing APIs to external customers and partners:
Managed services accelerate time-to-market – By using fully managed infrastructure and the new Amazon API Gateway Portal, the team avoided months of custom development work and launched the API program faster than would have been possible with self-managed alternatives.
Developer experience drives adoption – The professional, self-service Amazon API Gateway Portal significantly reduced friction in the customer onboarding process, so API access can rapidly scale as new hotel properties and partners onboard.
Infrastructure as code verifies consistency – Using Terraform for all production deployments provided the infrastructure team with version control, peer review, and audit trails while maintaining deployment consistency across environments.
Pay-per-use aligns costs with value – For organizations in growth mode, pay-per-use pricing removes the risk of overcommitting to fixed costs before achieving product-market fit with API offerings.
OAuth 2.0 delivers strong security at scale – Implementing OAuth 2.0 client credentials flow with an external identity provider enables a robust, scalable authentication foundation that grows securely alongside its expanding customer base.
Native AWS integration reduces complexity – For organizations already running on AWS, API Gateway’s native integration with services like EKS, Lambda, and CloudWatch minimizes architectural complexity and operational overhead.
Future enhancements
With the outbound API program successfully launched, the team is planning to extend API Gateway to inbound APIs, where partners push data into Revinate’s service. This will provide consistent security, monitoring, and governance across API traffic.
The team is also exploring advanced API Gateway features including request and response transformation, caching for improved performance, and deeper integration with AWS WAF for enhanced security against evolving threats.
Conclusion
Choosing Amazon API Gateway with the Developer Portal demonstrates how fully managed services can accelerate innovation while reducing operational complexity. By embracing AWS-native solutions and infrastructure-as-code practices, Revinate built a scalable, secure API program that supports growth as more customers get onboarded.
As the hospitality industry continues its digital transformation, this API-first approach positions them to empower hoteliers with the data and integrations needed to deliver exceptional guest experiences and drive direct revenue growth.
Next steps
Whether you’re in hospitality, software as a service (SaaS), healthcare, or any industry where partners and customers need programmatic access to your service, the pattern Revinate followed is broadly applicable. Start by mapping your business drivers to concrete technical requirements. This grounds your API gateway choices in outcomes, not only features. From there, explore Amazon API Gateway’s REST and HTTP API options to find the right fit for your traffic patterns and integration needs. Use the Amazon API Gateway Portal to give your developers a self-service onboarding experience from day one. If you’re already running workloads on AWS, the native integration with services like EKS, Lambda, and CloudWatch means you can build on your existing architecture rather than introducing new operational complexity. For teams that follow infrastructure as code practices, the Terraform AWS Provider for API Gateway helps you to define your entire API configuration as version-controlled code. To get started, visit the Amazon API Gateway documentation or reach out to your AWS account team for architecture guidance tailored to your use case and scale.
Resources
- Amazon API Gateway
- Improve API discoverability with the new Amazon API Gateway Portal
- AWS Lambda authorizers
- Deploying Amazon API Gateway and Lambda with Terraform