Every conversation safe. Proven at enterprise scale.
Secure your customer experience (CX) interactions with native AI governance, auditable reasoning, and cloud architecture built for enterprise control — not bolted on after.
Moving fast with AI takes trust you can measure
Amazon Connect Customer keeps conversational workflows contained inside the AWS trust boundary of your existing cloud infrastructure — giving you native, turn-level policy enforcement and verifiable audit trails without third-party network hops or vendor proxies.
Data protection standards
- Data protection standards
-
143
- Browse the AWS Compliance Directory
- Of qualifying contacts evaluated automatically
- 100%
- See how automated performance evaluations work
- Operational and compliance metrics monitored
- 150+
- Browse the AWS Compliance Directory
Worldwide pre-validated regulatory frameworks
Meeting strict compliance standards often means months of security reviews before a project can launch. Connect Customer comes with pre-audited regulatory frameworks already built into the AWS infrastructure. This gives risk and compliance teams instant clarity — clearing the runway for you to continuously launch innovative CX without regulatory delays.
Globally accredited, locally compliant
AWS continuously validates against 143 global security standards and compliance frameworks (including FedRAMP High, HIPAA, PCI DSS, and GDPR), verifying that your contact center meets strict regional requirements from day one.
Structural multi-region resilience
Amazon Connect Global Resiliency (ACGR) enables active-active multi-region deployment across paired AWS regions, with traffic distribution adjustable in 10% increments, so new contacts can be shifted between Regions in a controlled way. ACGR requires enablement for your account and is available only for supported Region pairs; phone numbers and agents must be configured in both Regions. For setup prerequisites, see the ACGR requirements guide.
PCI DSS Level 1
 Native compliance for secure payment card data handling across voice and digital interactions.
HIPAA Eligible
 Built-in data protection and PII redaction for healthcare customer experiences.
FedRAMP High
 Exceeds standard moderate baselines in AWS GovCloud (USWest), providing the highest level of security authorization for U.S. federal and public sector deployments.
SOC 1, 2, and 3
 Third-party audited operational, security, and confidentiality controls.
ISO 27001, 27017, and 27018
 Internationally recognized standards for information security and privacy management.
Global Privacy and Security
 Fully aligned with GDPR (Europe), C5 (Germany), ENS (Spain), IRAP (Australia), and MTCS (Singapore), and HITRUST CSF aligned (Healthcare).
Launch agentic AI agents you can trust with your customers
Standalone AI agents often lack real-time policy controls and visibility, while retrofitting legacy contact center tools creates security gaps.
Connect Customer gives you guardrails where you define exactly what the AI can and cannot do, human-in-the-loop escalation when judgment matters more than speed, and a full audit trail on every action so your compliance team, your board, and your regulators can see exactly what happened and why. Your most sensitive customer moments don't require a tradeoff between innovation and trust.
See how to build dynamic customer experiences while keeping strict safety standards in place.
Governed, transparent, and natively secure AI
Third-party security add-ons force your data to hop across external vendor networks, creating new attack surfaces and compliance risks. Connect Customer embeds governance natively within a single AWS trust boundary — giving you live, turn-by-turn control over every conversation. Your customer interaction data stays strictly inside your environment, encrypted at rest and in transit.
Closing the cybersecurity speed gap
Machine-speed AI interactions demand machine-speed governance.
Turn-level policy enforcement
Machine-speed AI interactions demand machine-speed governance. Connect Customer replaces slow, manual committee reviews with real-time SecOps and automated runtime evaluations — verifying policy compliance before responses reach customers.
Each AI reasoning step is visible, controlled, and enforced per turn. Real-time evaluation scoring catches anomalies, while automated alerts notify security teams as potential issues occur.
Citation-backed answers
Give your risk and compliance teams clarity. Every response links directly back to your approved content, so you always have simple, auditable proof behind what your AI says.
Blended deterministic and agentic control
You define the rules. Compliance-critical steps follow structured, deterministic business logic, while conversational steps leverage governed AI reasoning. Built-in escalation paths allow AI agents to transfer interactions to human agents when additional support is needed.
Keep it simple. Keep it safe.
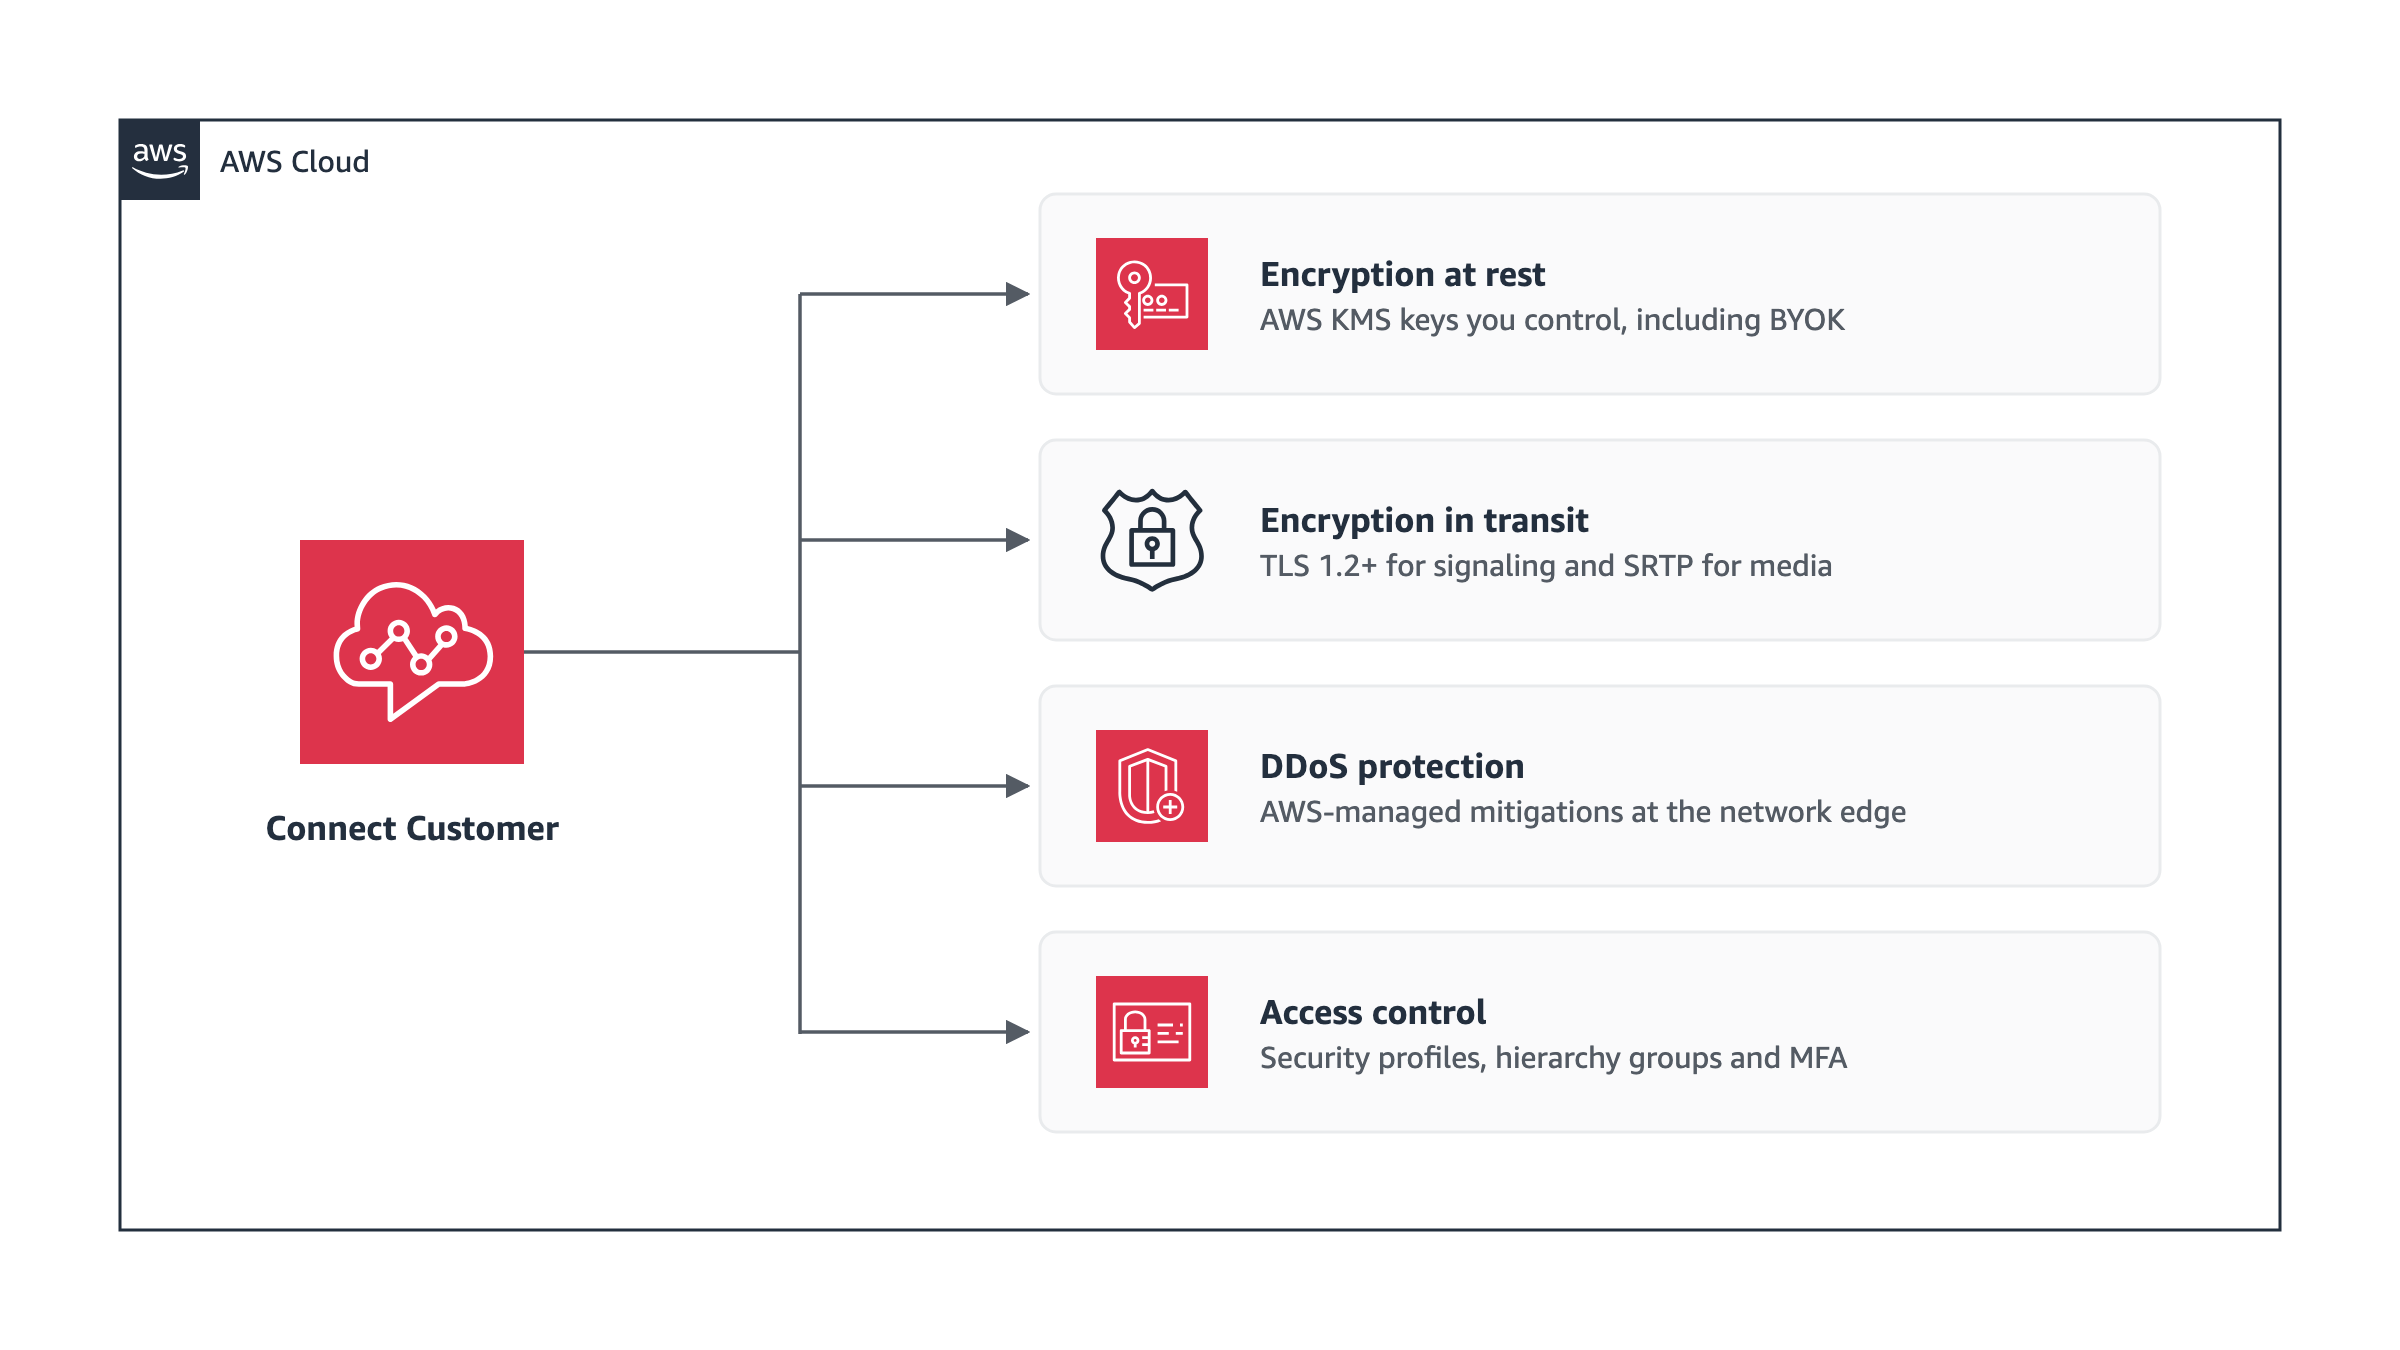
Your contact center infrastructure should always be secure. Connect Customer handles your data, models, agents, and conversational logic within a single AWS trust boundary, simplifying threat modeling and accelerating security reviews.
- Customer-managed encryption
- Encrypted transport and isolation
- Automated DDoS protection
- Strict access control and federation
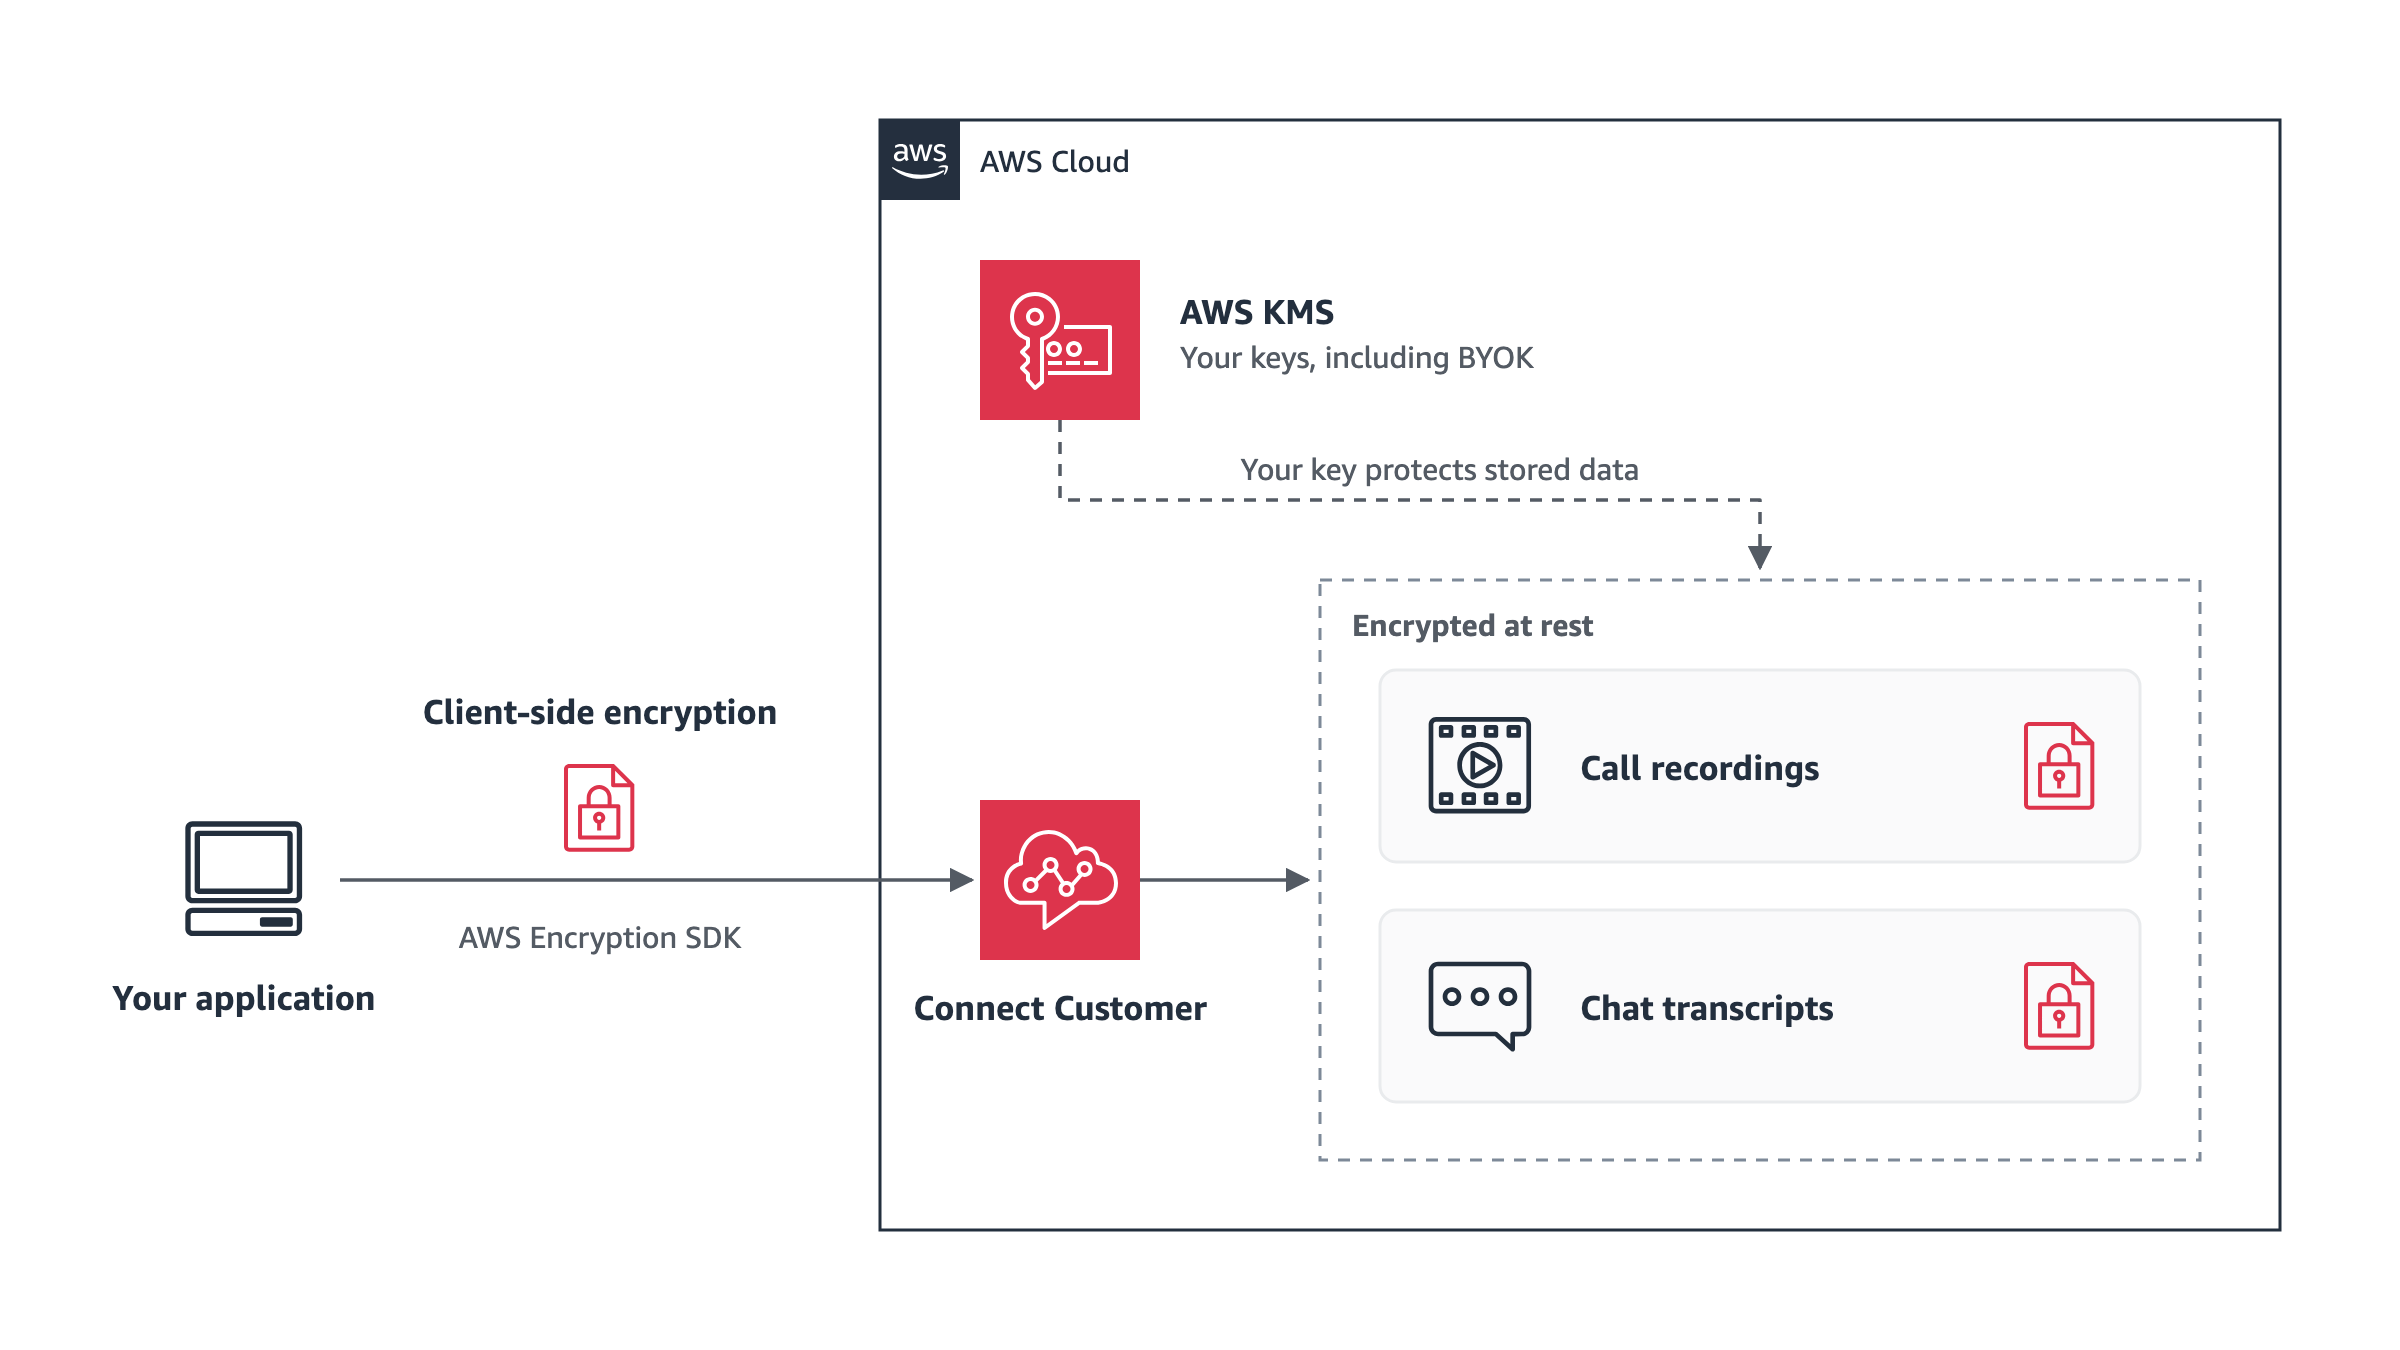
Customer-managed encryption and client-side privacy
Safeguard your data at rest using AWS Key Management Service (AWS KMS). Maintain full control over encryption keys for all call recordings and chat transcripts, including bring your own keys (BYOK), to use for envelope encryption with Amazon S3 input/output buckets.
Connect Customer supports client-side encryption using the AWS Encryption SDK, maintaining end-to-end data protection before transmission.
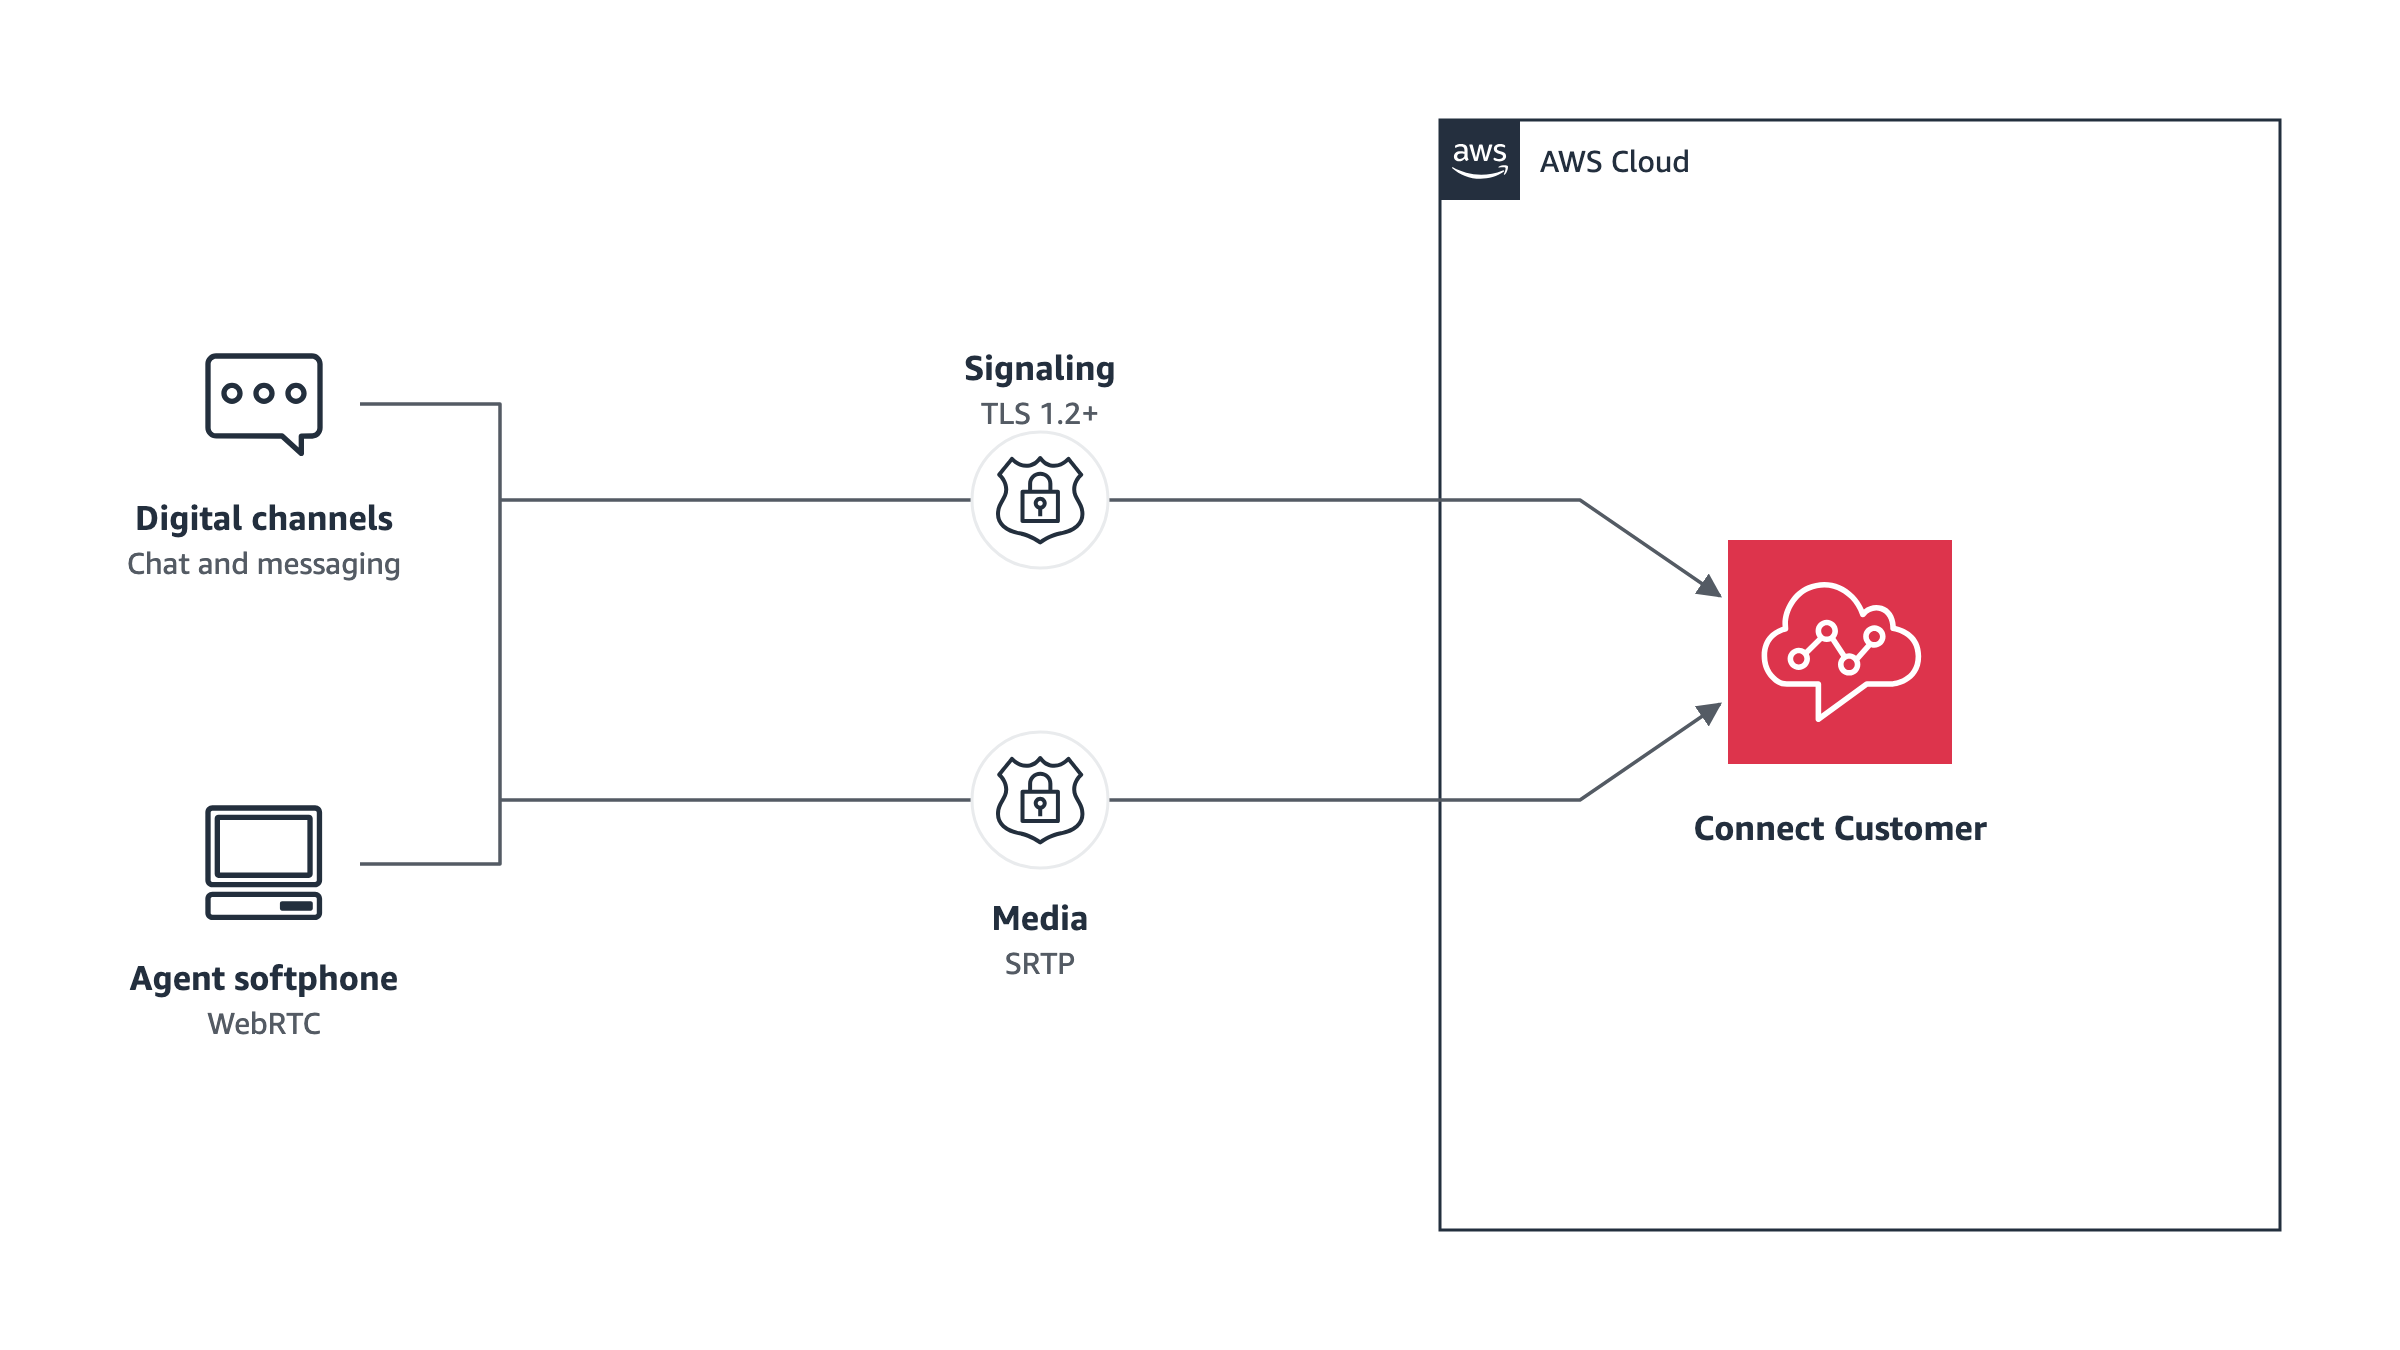
In-transit security and network isolation
Connect Customer protects signaling and media across digital channels and softphone WebRTC sessions using Transport Layer Security (TLS 1.2+) and Secure Real-Time Transport Protocol (SRTP).
While traditional public switched telephone network (PSTN) calls rely on external carrier networks that fall outside AWS’s encryption boundary, your cloud and back-end environments remain tightly isolated.
Deploy AWS Lambda integrations within your Amazon VPC and enforce granular domain allowlists and IP restrictions to limit administrative access.
Learn more about infrastructure security and network controls
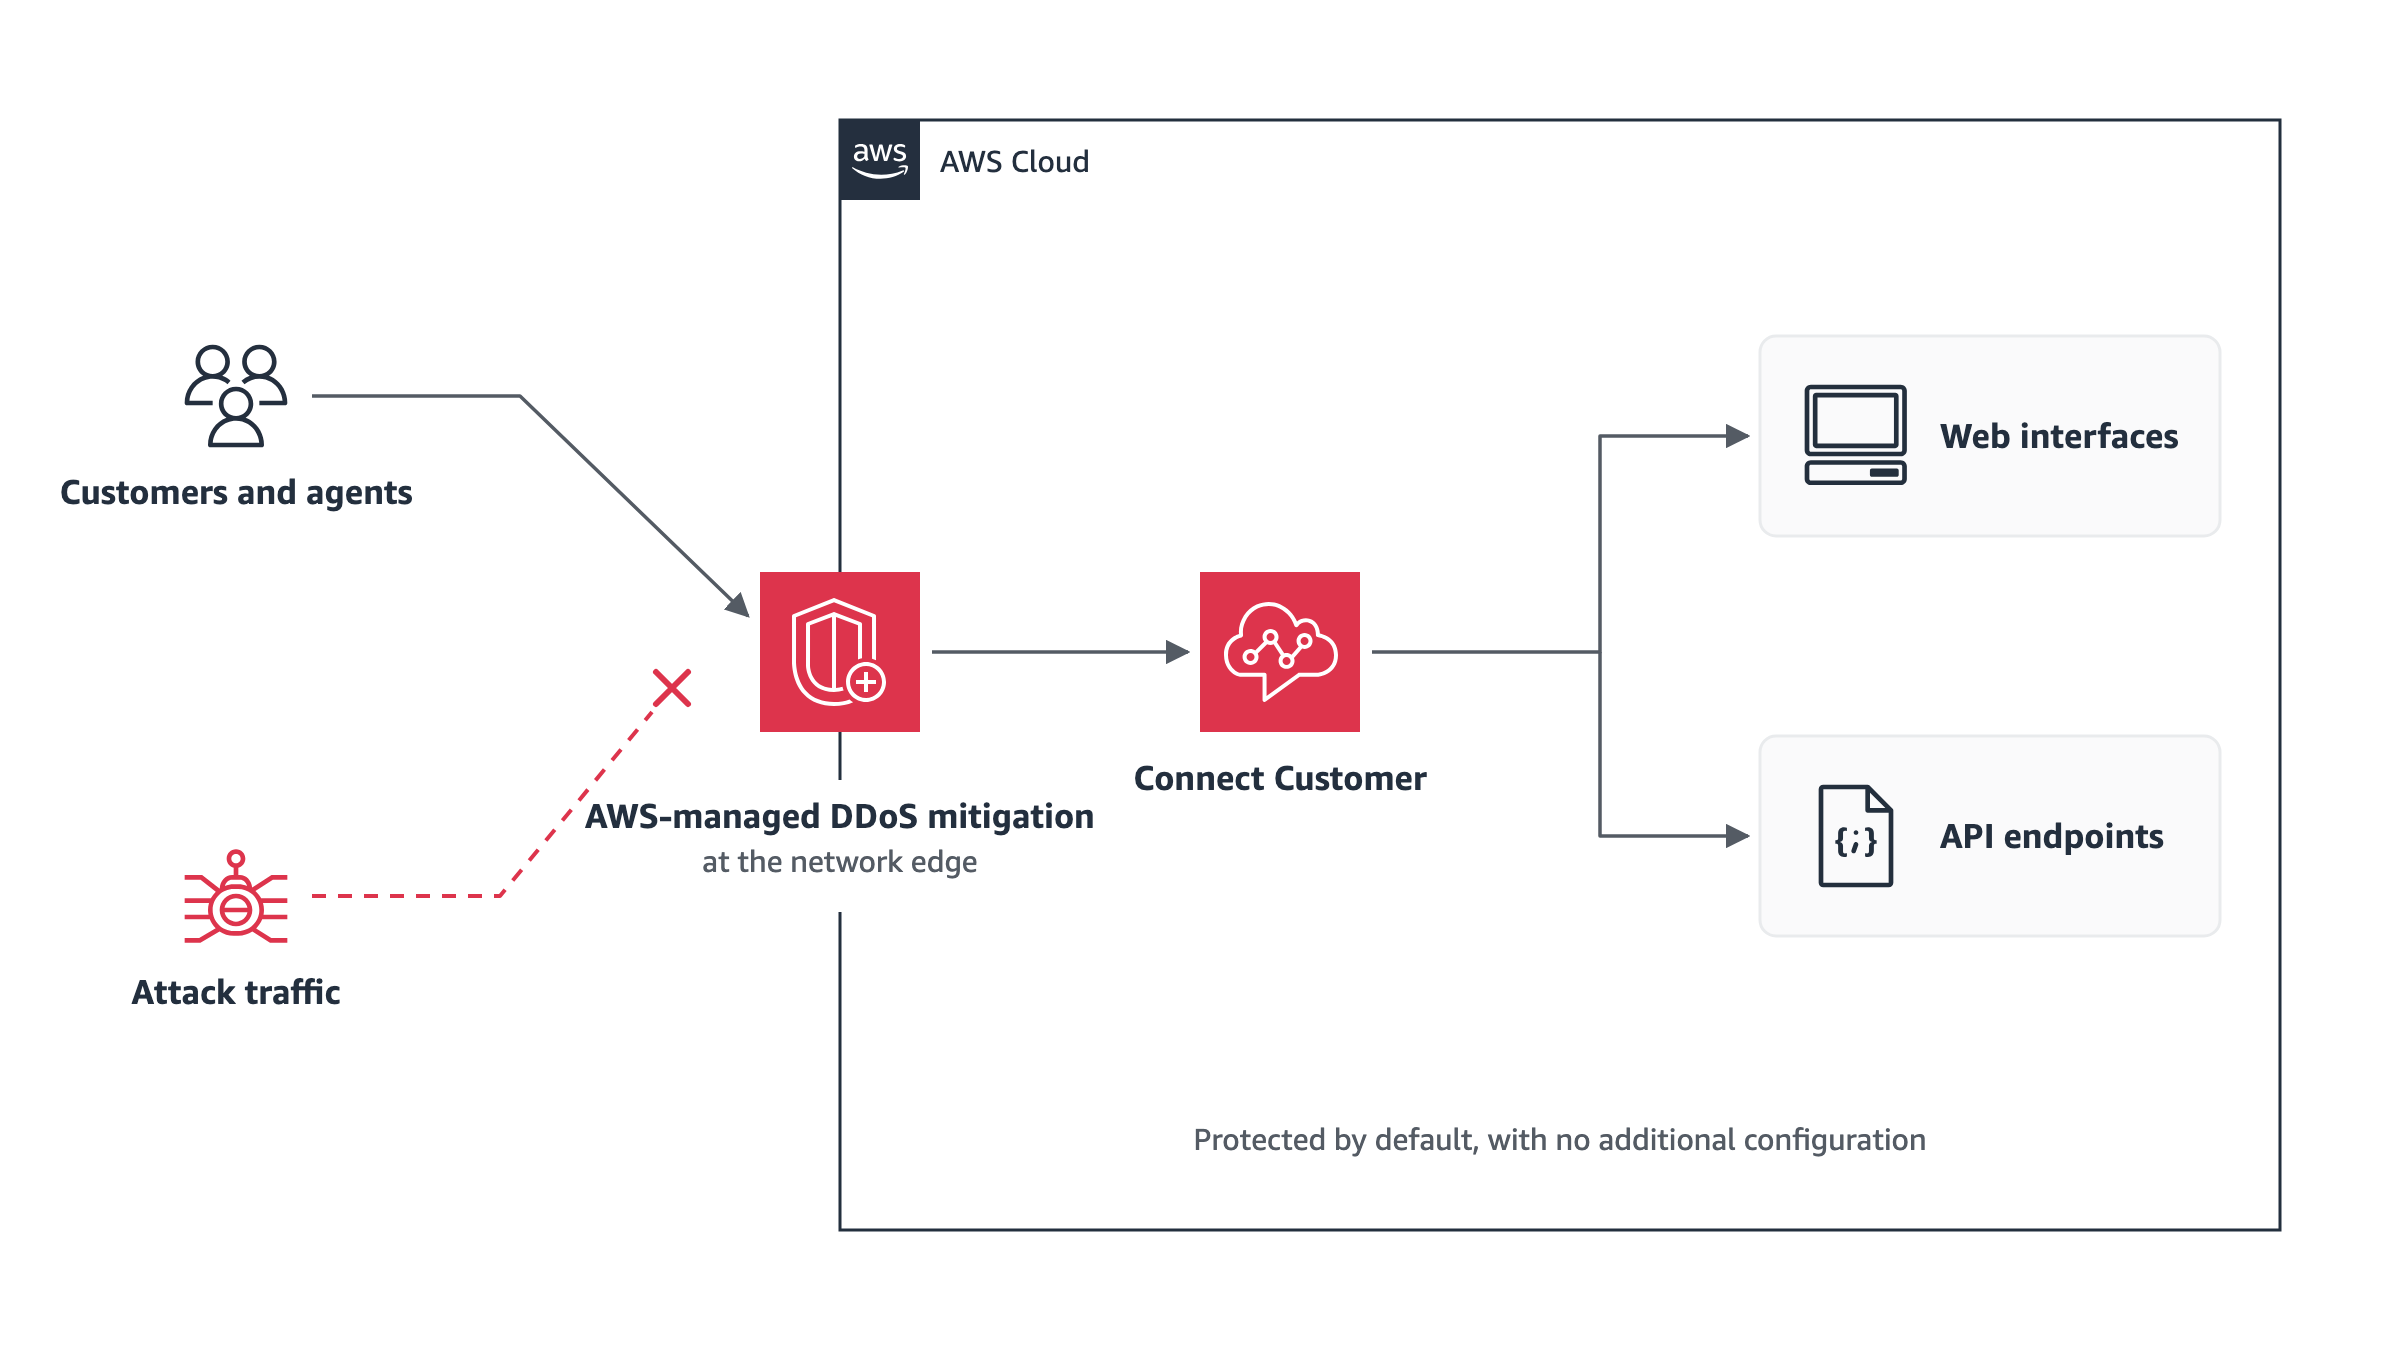
Automated DDoS protection
Keep your customer experience solution online and secure. Defend against distributed denial-of-service (DDoS) attacks with AWS-managed mitigations at the network edge. These protections safeguard Connect Customer web interfaces and API endpoints without requiring additional configuration.
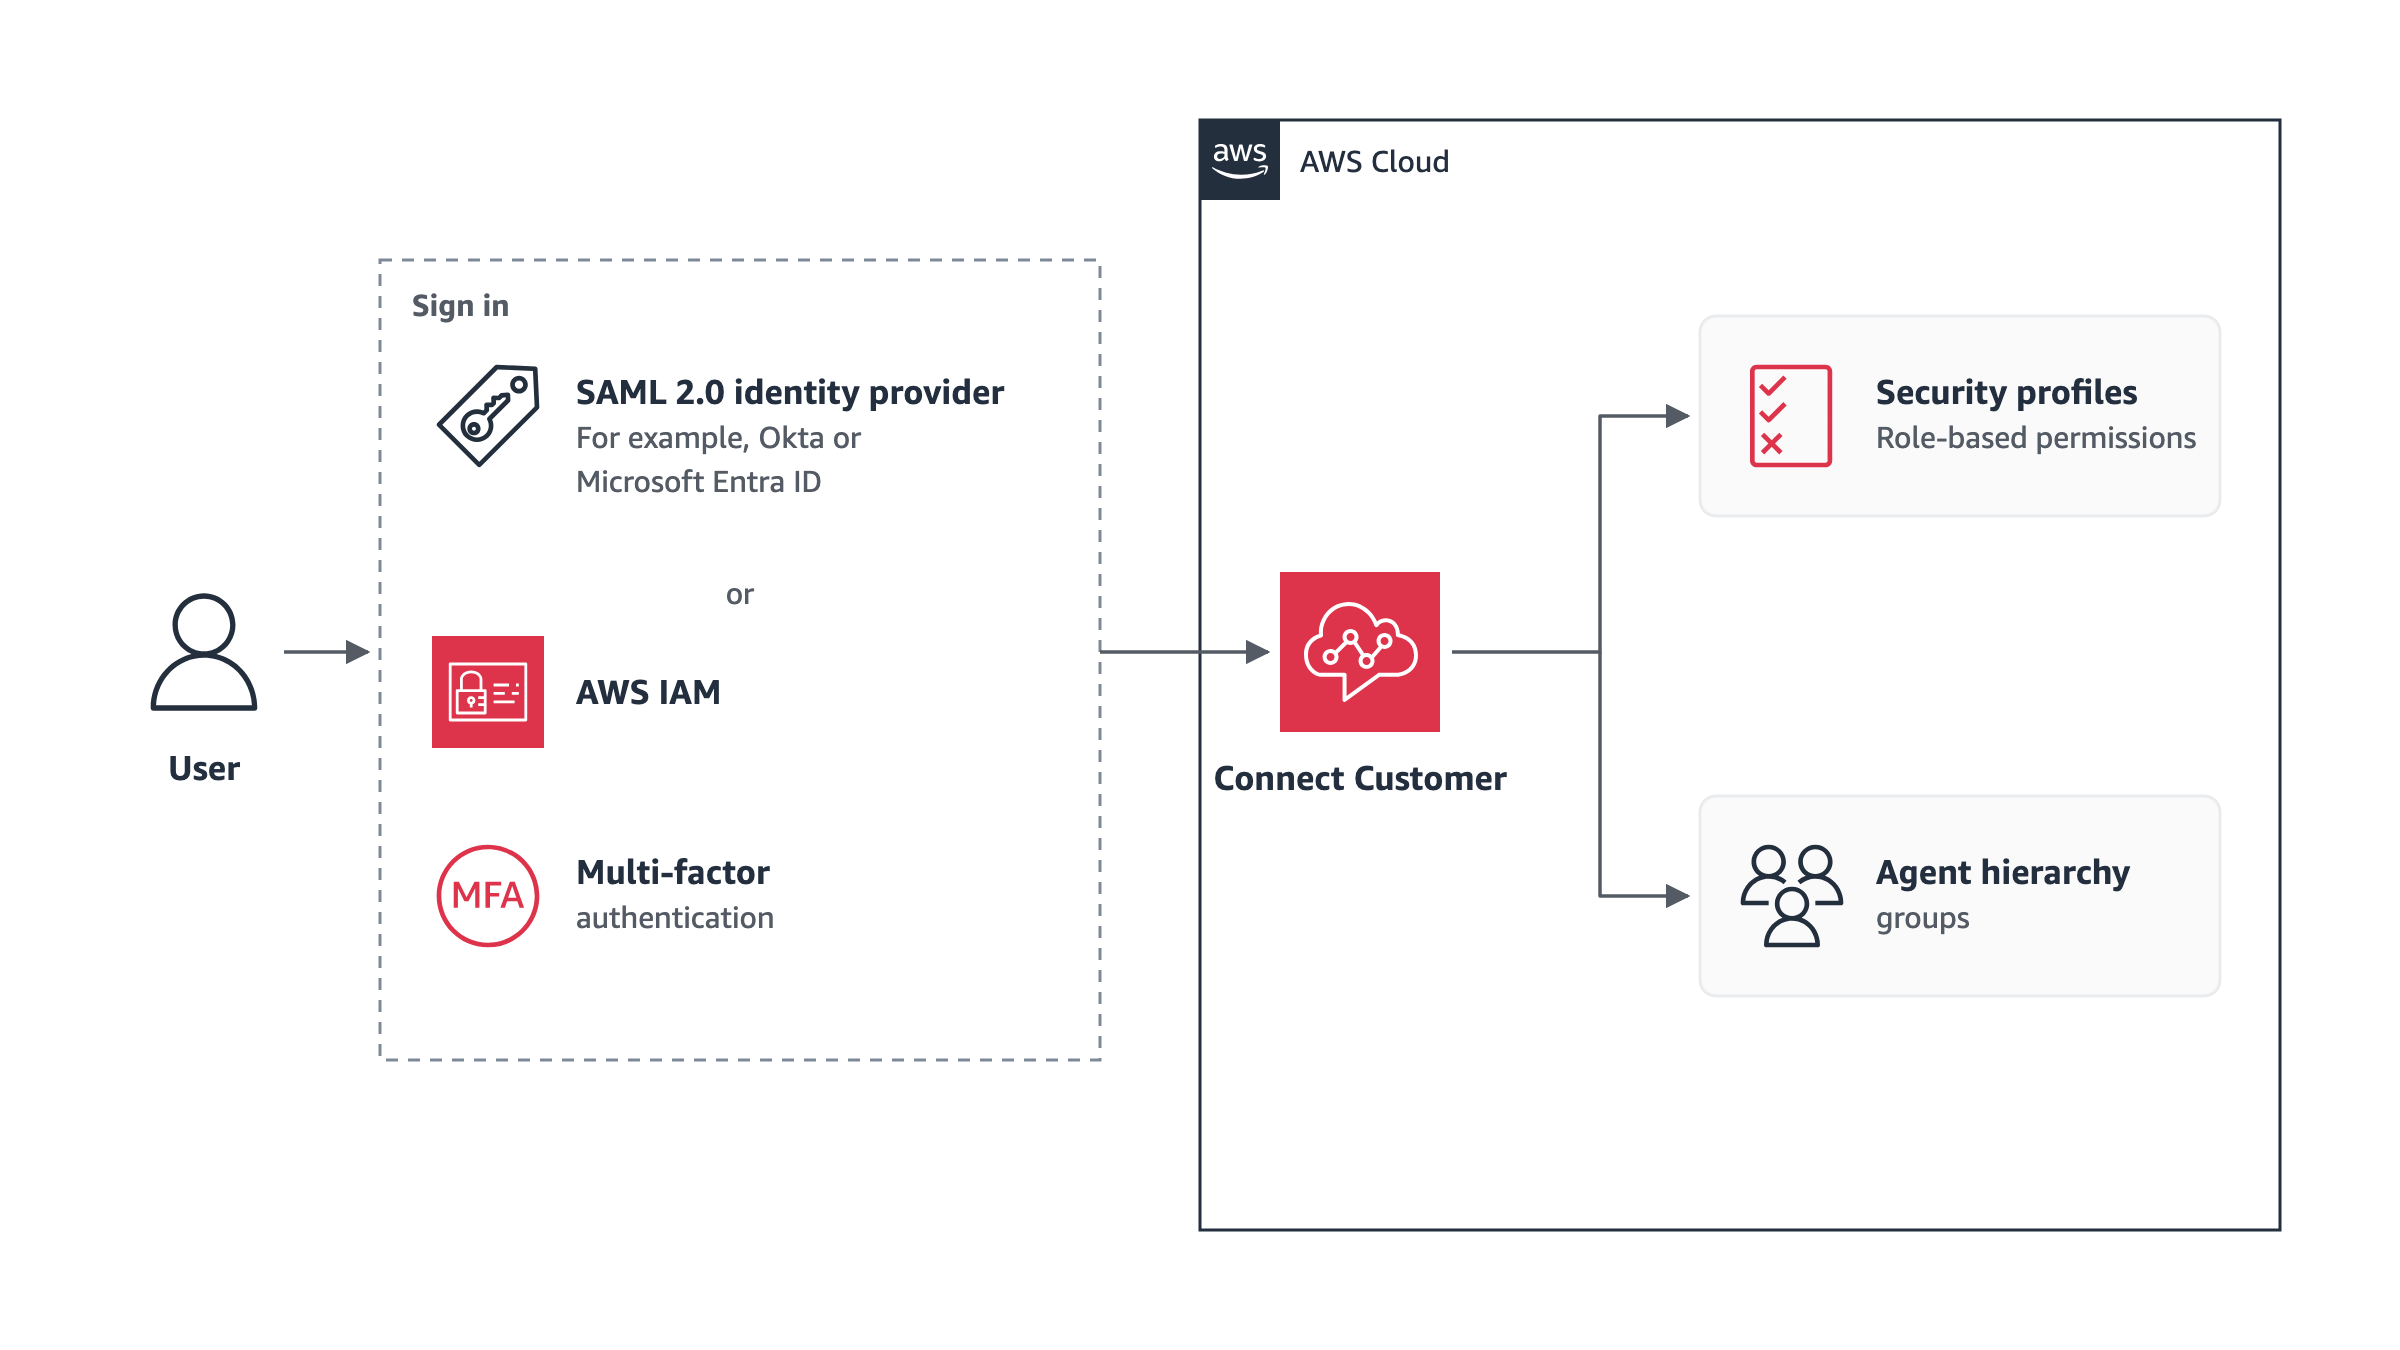
Strict access control and federation
Enforce granular role-based access control (RBAC) via security profiles and agent hierarchy groups. Multi-Factor Authentication (MFA), enforced through your SAML 2.0 identity provider (such as Okta, Microsoft Entra ID) or AWS IAM, offers an additional layer of authentication before you connect to Connect Customer. For enhanced administrative governance, customizable session timeouts automatically terminate inactive console and agent sessions to prevent unauthorized access.
Common questions (FAQs)
Answers on Connect Customer security, compliance, and data isolation
Is our customer data safe on AWS, and what are we responsible for?
Yes. Connect Customer operates under the AWS Shared Responsibility Model. AWS secures the physical data centers, underlying hardware, and network infrastructure, providing built-in compliance for FedRAMP High, PCI DSS, and HIPAA. You control your data and who can access it. You manage your user permissions, encryption settings (via AWS Key Management Service), and routing logic. An AWS Partner can review your setup to confirm it meets specific compliance requirements.
How does AWS handle security across 42+ countries and 65+ languages?
Every region runs inside the same AWS trust boundary, so the security model doesn’t change as you expand. Your contact center data, call recordings, and conversational models stay in the AWS Region you select, and they don’t cross regional or account boundaries unless you explicitly configure it. Compliance is validated against frameworks including HIPAA, PCI DSS, FedRAMP High, SOC 1/2/3, ISO 27001, GDPR, IRAP Protected, C5, OSPAR, and MTCS. AI reasoning is auditable turn by turn, so you get the same visibility in every market and every language.
How does runtime AI governance helps detect and block ungrounded responses?
Guardrails are built into every stage of the runtime pipeline — speech recognition, reasoning, and text-to-speech — to catch and block ungrounded responses before they reach the customer. Plus, every answer is citation-backed, meaning it links directly to your approved source content. Deterministic rules enforce compliance at each step: every guardrail action, mask, modification, reroute, and flag is recorded and traceable, giving your compliance team the evidence they need for regulatory audits without chasing logs across systems. When a conversation crosses a threshold you define the system escalates to a human with full context. The AI improves with every engagement but never drifts; guardrails ensure it evolves within the boundaries you set, so improvement never comes at the cost of compliance.
How do we continuously monitor our contact center against AWS security standards?
AWS CloudTrail provides a complete, auditable record of every administrative action, API call, and configuration change, while Amazon CloudWatch captures full operational logs across automated self-service and agent activities. Amazon Macie adds sensitive-data discovery for your data stored in Amazon S3.
Can we run penetration tests on our Connect Customer environment?
Amazon Connect does not permit customer-driven penetration testing of the platform itself. Customers may test their own components (Lambda, DynamoDB, custom CCP, agent workstations) under the standard AWS Penetration Testing Policy. Pen-testing requests should be routed through your AWS account team.
Will adding agentic AI capabilities disrupt our existing contact center routing?
No. Connect Customer is designed to integrate agentic AI directly into your current contact flows. Capabilities like AI agents, Live Sync, and the agentic CX designer plug directly into your existing infrastructure. This modular approach allows you to deploy AI at your own pace — without tearing down established routing or overhauling your environment.
What new security risks emerge during migration?
- Business-as-usual (BAU) integration failure: Integration gaps are a common cause of migration challenges. Consider making integration validation a go-live checkpoint.
- Identity strategy locked at instance creation: Your identity approach is set when you create your Amazon Connect instance, so it helps to plan it carefully up front.
- Number porting delays: In North America, porting can take several weeks, depending on carrier. Build that into your cutover window.
- Data split during dual platform period: Running two platforms can divide your data across systems. Plan for analytics continuity so you keep full visibility.
- Agent training gap: Agent Workspace is a new interface, so training time helps your teams get comfortable before go-live.
Customer stories
Capita
 For public sector work, data residency and security are non-negotiable. Capita chose Connect Customer to serve over 1.6 million UK residents because data stays within AWS services, and built-in simulation and observability tooling lets it validate agent behavior before going live.
Intuit
 With more than 275 million minutes of customer interactions each year, Intuit uses Connect Customer to support thousands of agents across 11 countries with automated redaction of sensitive data in call transcripts. As the company expands its voice security, Intuit plans to add new security functionality to ensure that customer data is highly secure.
Siemens
 Siemens is testing Connect Customer AI agents that connect callers with employees without ever revealing employees' phone numbers or personal details, and outbound AI agents that respect opt-outs, calling time windows and GDPR consent.
Build on AWS with enterprise-level trust built in
Because Connect Customer runs on AWS, you get visibility into each answer, strict safety guardrails on every conversation, and control over what your AI can say and do.