Sold by: Adana Technologies
Stay authorized every day, not every three years. Adana Technologies deploys ATOReady, an AI authorization engineer, in your AWS account to place each system at its NIST RMF step, keep control evidence current from your scans and pipelines, run every POA&M to verified closure, and assemble the package your Authorizing Official needs when a trigger fires. Built for cloud providers and contractors whose systems must earn and keep federal authorization.
Overview
Image
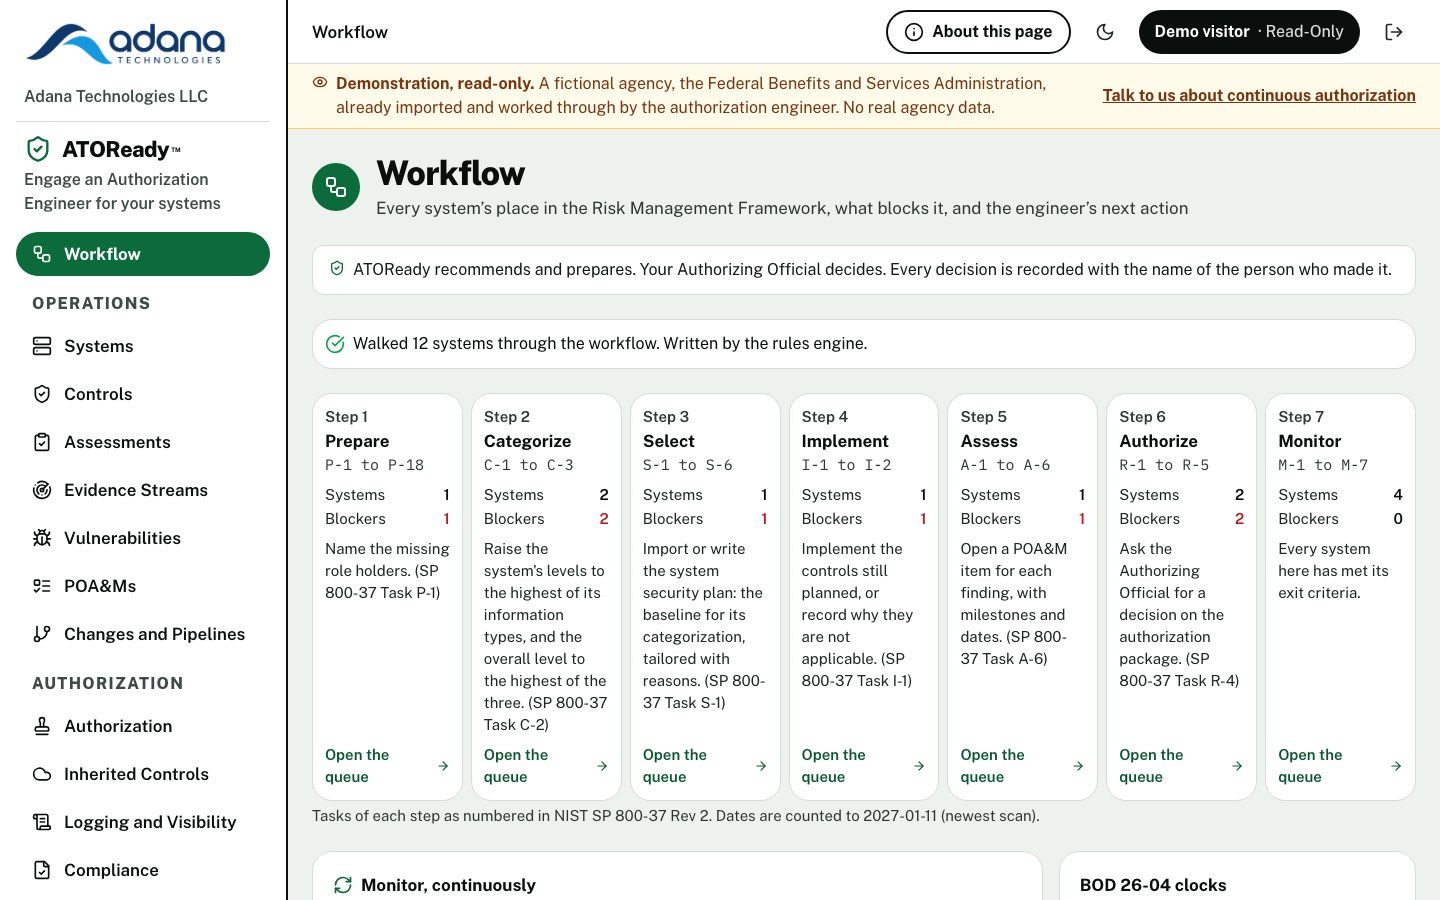
Every system at its RMF step
Image
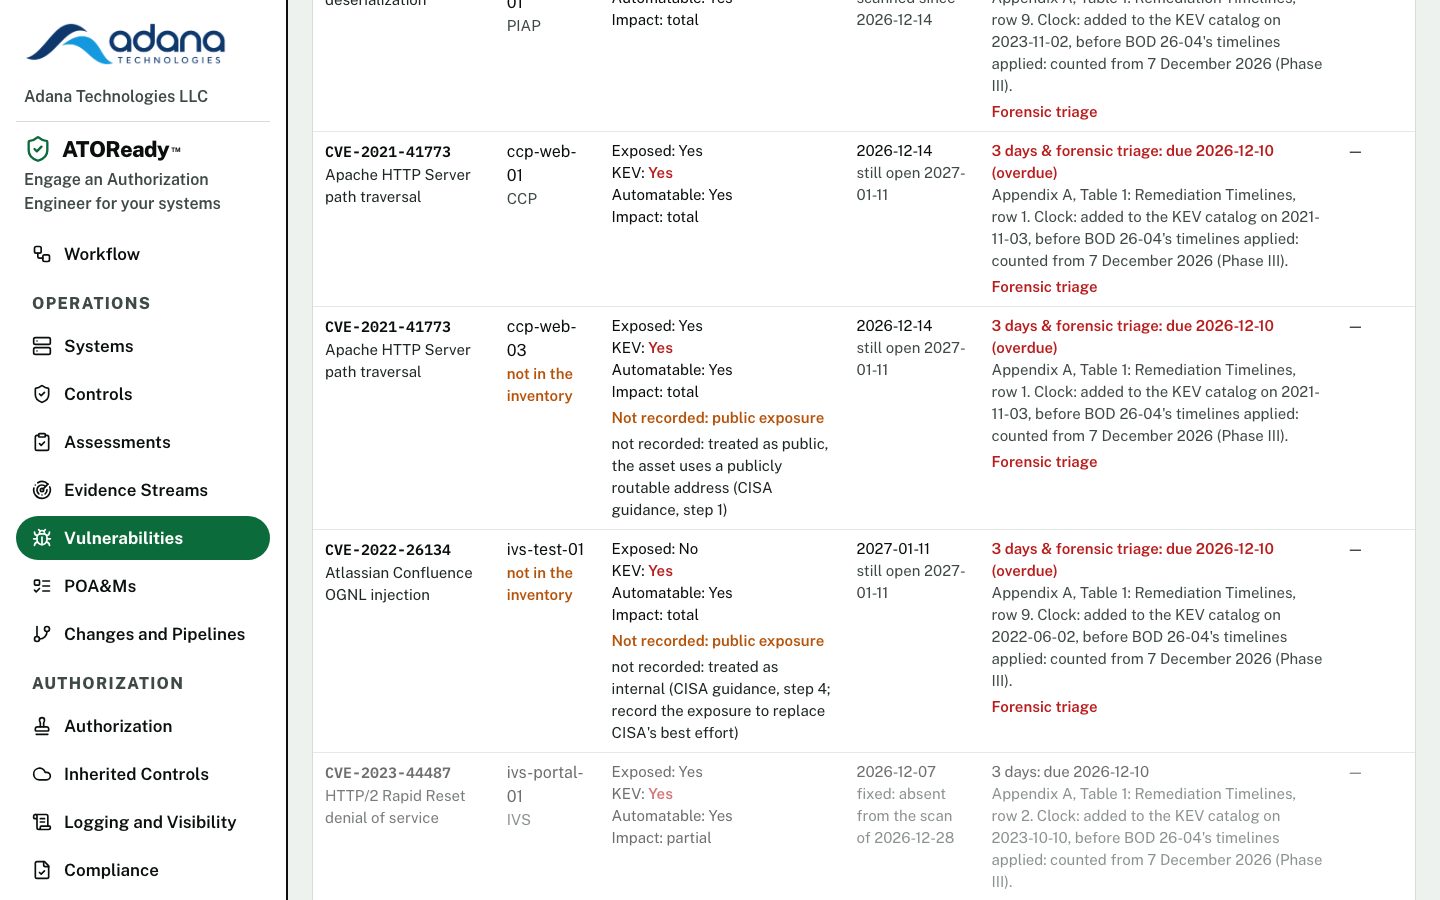
Every vulnerability with its deadline
Image
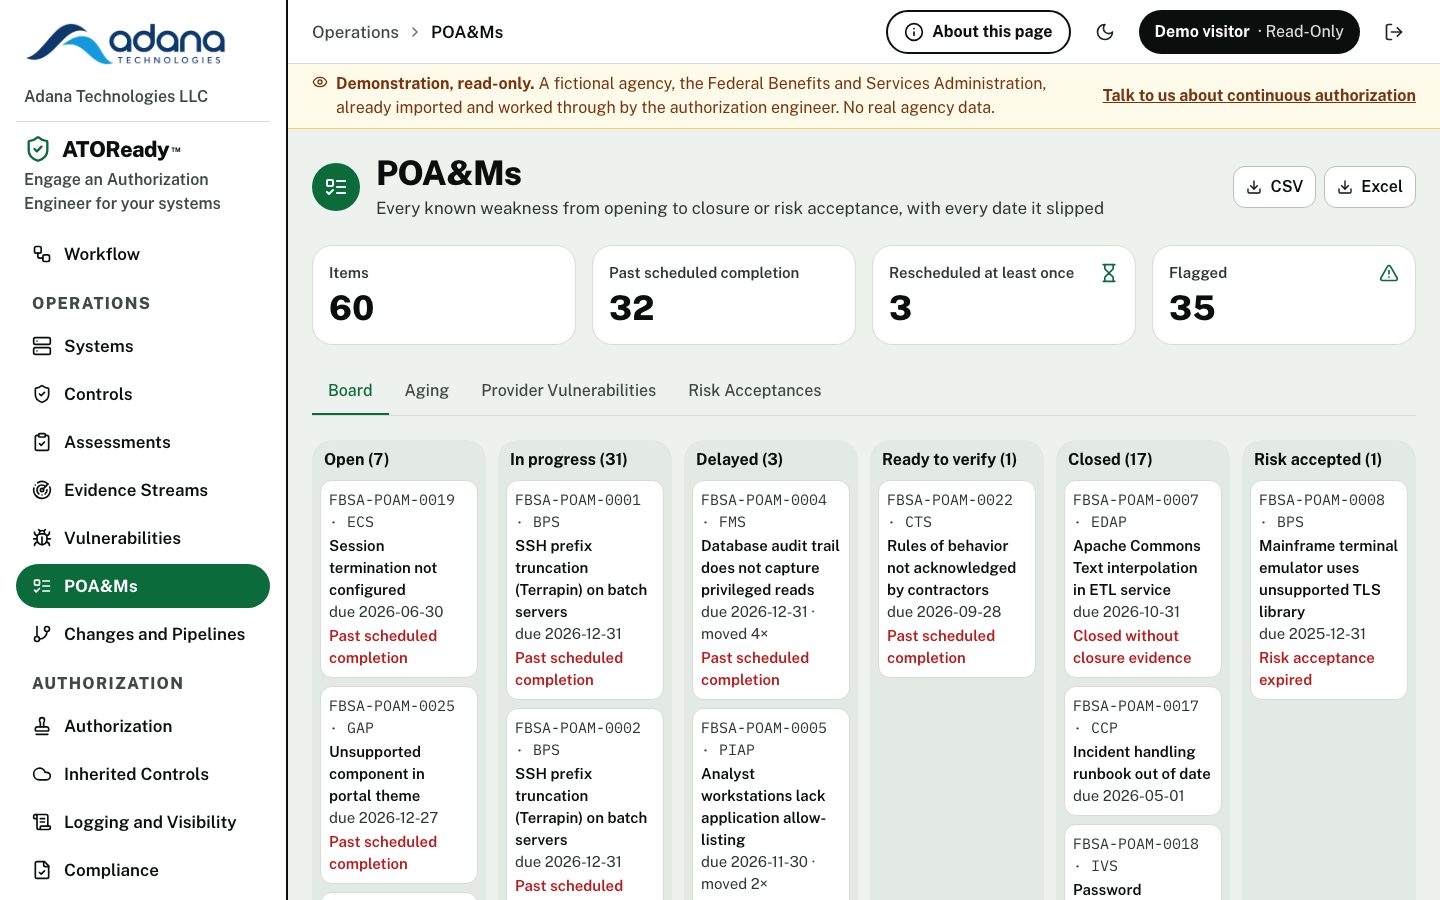
POA&Ms run to verified closure
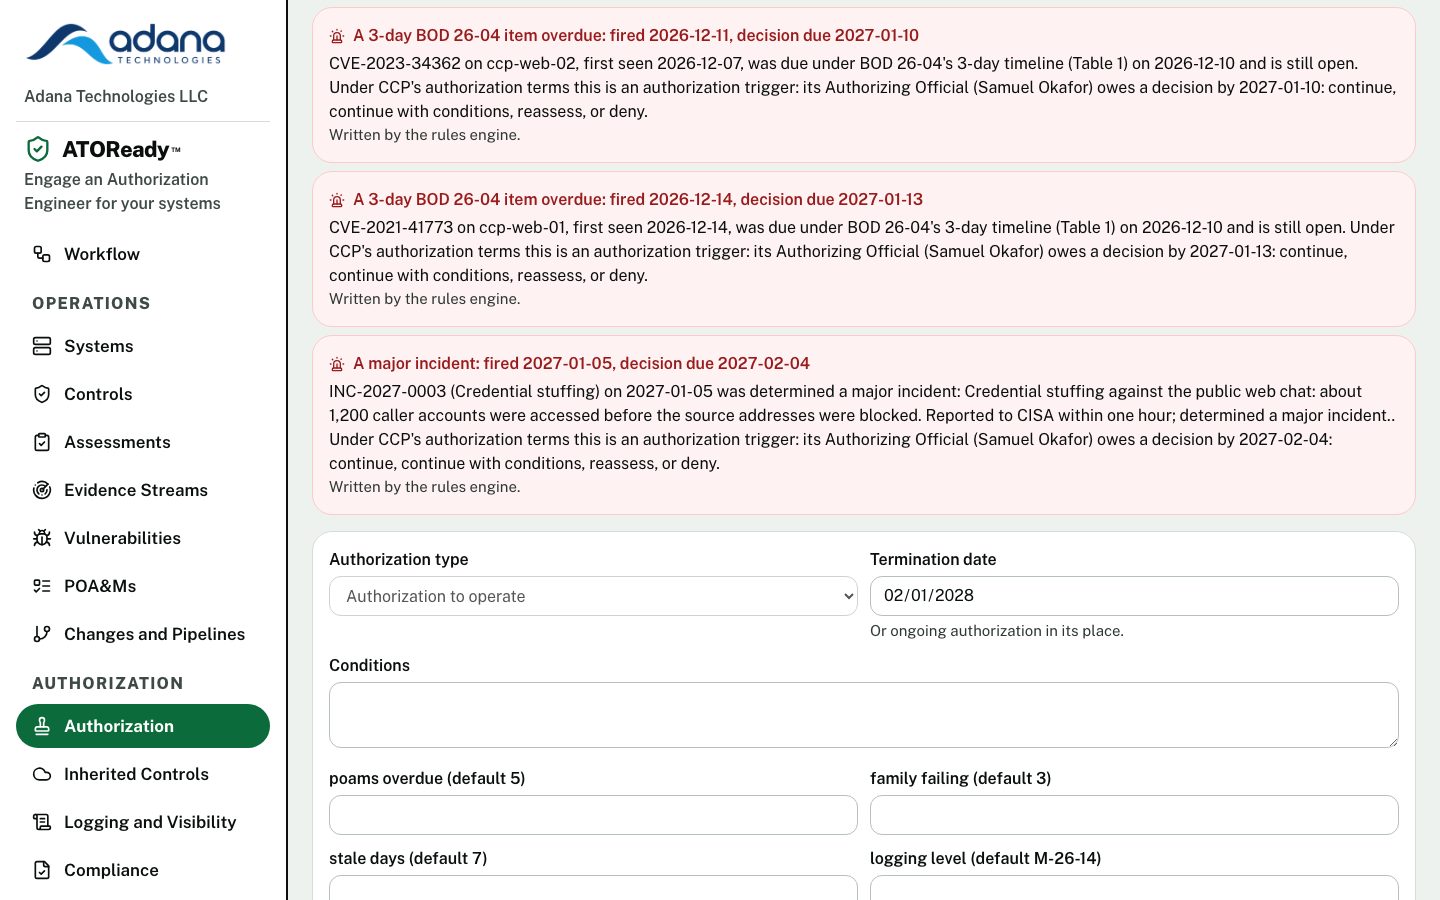
Image
Triggers briefed when they fire
Image
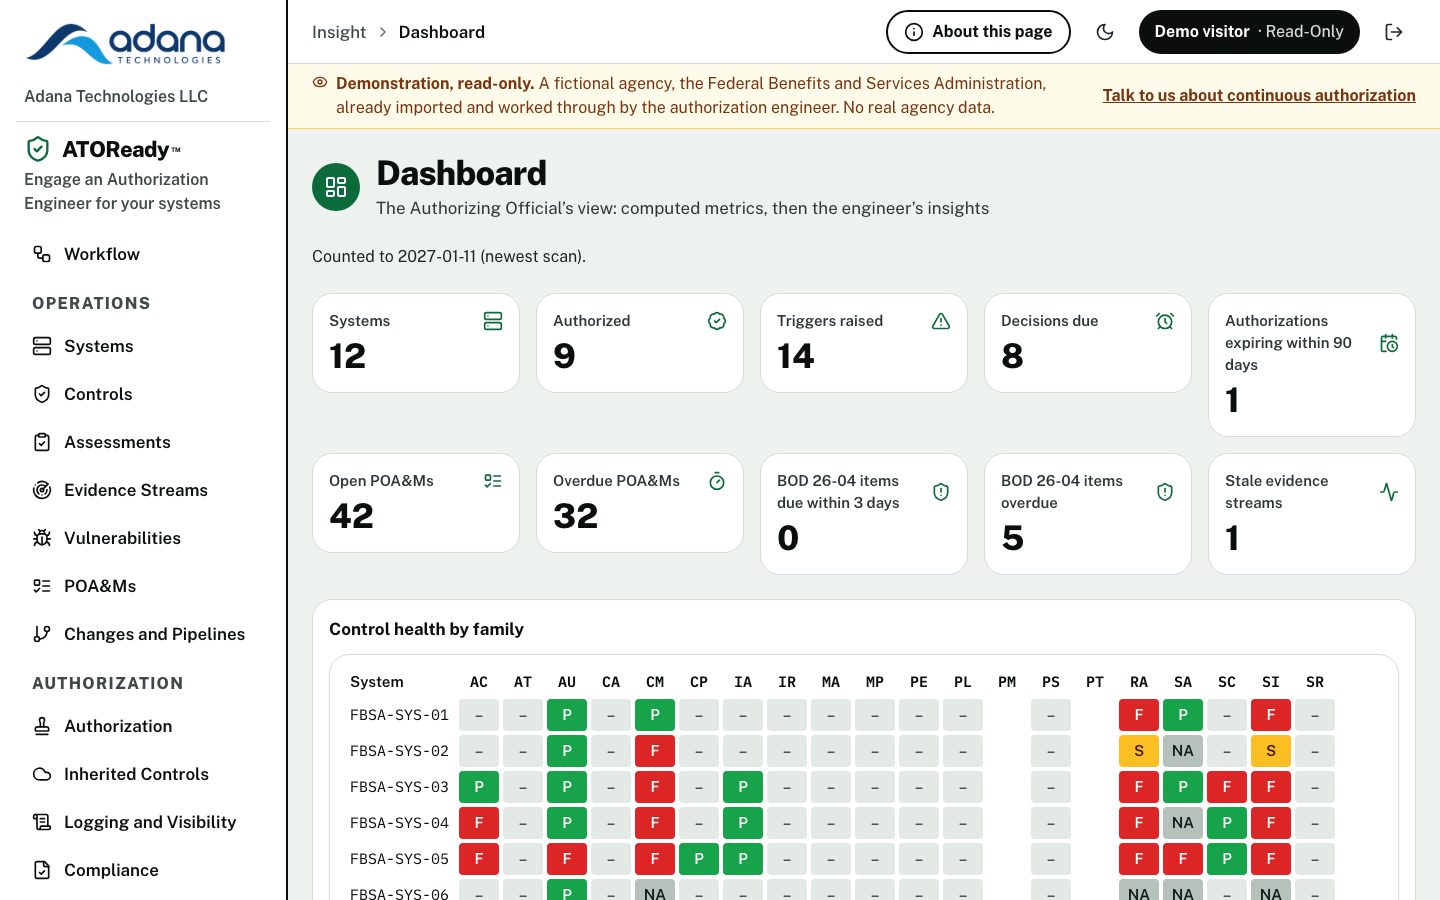
The decision-maker's view, from the records
Image
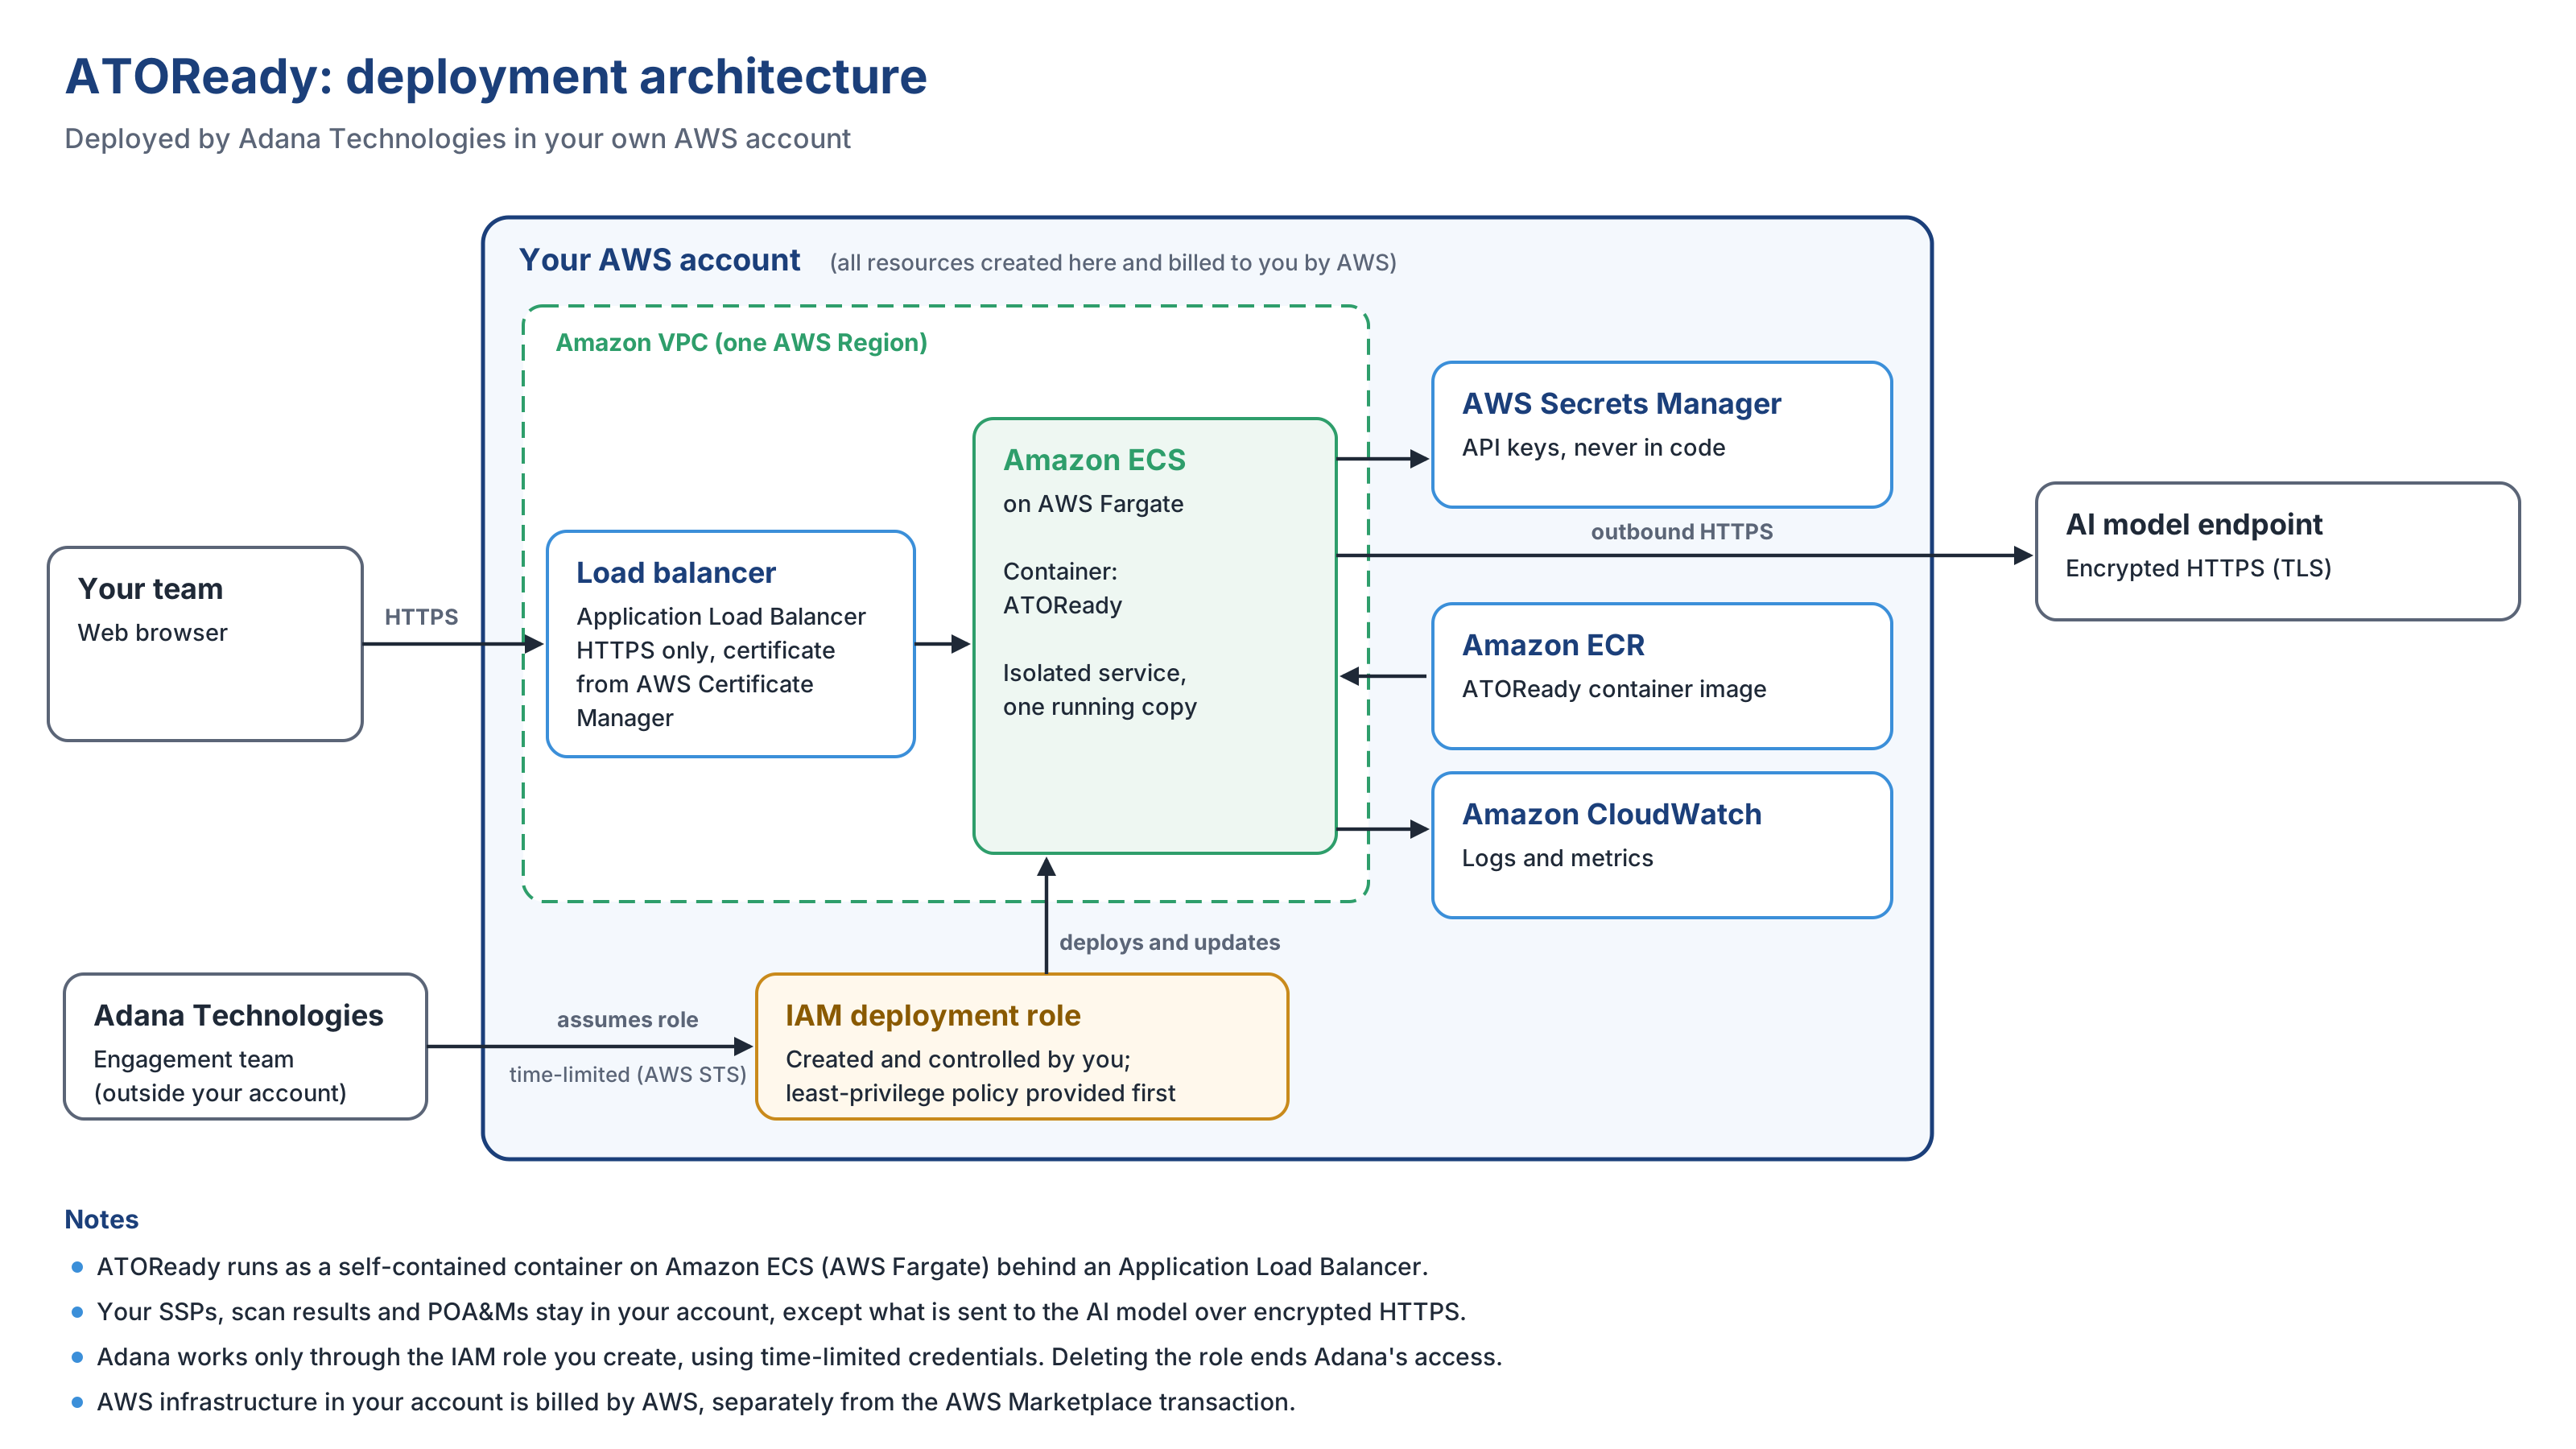
Runs in your own AWS account
An authorization should stay current between decisions. NIST SP 800-37 calls this ongoing authorization, and it depends on continuous monitoring and a plan of action and milestones (POA&M) that tracks each weakness to closure. For a cloud provider holding FedRAMP authorization, or a contractor whose system runs under an agency ATO, the records that prove it (system security plans, scan exports, POA&M spreadsheets, pipeline results, decision letters) often disagree, and someone has to reconcile them and spot what needs a decision before the agency does. From December 7, 2026, CISA BOD 26-04 gives every vulnerability a 3-, 14- or 60-day deadline, and systems operated on an agency's behalf are measured against those clocks.
This engagement puts an AI authorization engineer on that work. Adana Technologies deploys ATOReady in your AWS account, loads the records you already have, and works with your security and compliance team to keep each system authorization-ready every day, with every insight traced to the record behind it.
WHAT HAPPENS DURING THE ENGAGEMENT • Import and place. ATOReady imports your records in nineteen common layouts, flags problems, and places each system at its RMF step with its blockers and the SP 800-37 task that applies. • Monitor and remediate. Scans, configuration results, SBOMs, pipeline gates and logging self-assessments keep control health current. Each vulnerability is placed on BOD 26-04's table with its deadline, and missing factors are resolved by CISA's rule and flagged. • Run POA&Ms to closure. Items close only with closure evidence and verification. Risk acceptance requires the named Authorizing Official and an expiry date, and items moved again and again are flagged as risk acceptance by delay. • Brief the Authorizing Official. When an agreed trigger fires, such as a major incident, a significant change or overdue items, the engineer assembles the package. The Authorizing Official decides, and each decision is recorded with the decision-maker's name.
WHAT YOU RECEIVE • Each system placed at its RMF step, with its blockers and next tasks • A control evidence health view built from your own scans and pipelines • A vulnerability deadline register and a fix-first remediation list • A POA&M register with closure evidence and every slipped date • An Authorizing Official briefing package and an executive readout
WHO IT IS FOR Cloud service providers pursuing or maintaining FedRAMP authorization; contractors that build or operate systems that must hold an agency ATO; and state and local governments that follow the NIST Risk Management Framework. Within each: CISOs, ISSMs and ISSOs, system owners and DevSecOps teams.
POLICY BASIS ATOReady follows NIST SP 800-37 Rev. 2, SP 800-53 Release 5.2.0 and SP 800-53B, CISA BOD 26-04, OMB M-26-14 and FedRAMP's 2026 rules for cloud services. It does not grant an ATO or a FedRAMP authorization: it recommends, prepares packages and monitors, and the Authorizing Official decides. It is not legal advice.
ENGAGEMENT OPTIONS Authorization Readiness Workshop, Continuous Monitoring Readiness Assessment, Ongoing Authorization Program Build and Advisory Hours. Each is priced in a private offer once scope is agreed.
HOW IT RUNS ON AWS ATOReady runs as a self-contained container on Amazon ECS in your AWS account, behind HTTPS, with secrets held in AWS Secrets Manager, so your security records stay in your environment. We deploy through an IAM role that you create and control, and we give you the architecture, the IAM policy and the deployment steps before anything is provisioned. Use beyond a pilot follows your organization's own security authorization process. The AI model is reached over an encrypted connection. If the model is unavailable, built-in rules do the same work and the screen shows which method was used. Everything the AI writes is labeled as AI-generated.
AWS infrastructure provisioned in your account for this engagement (for example Amazon ECS, Elastic Load Balancing and AWS Secrets Manager) is billed to you by AWS, separately from this AWS Marketplace transaction.
SEE IT FIRST The read-only live demo at ato-ready.labs.adanatech.com shows ATOReady at work on a fictional agency with invented systems, people, hosts and findings. The overview is at labs.adanatech.com/ato-ready. To scope an engagement, choose Request private offer and we will reply within two business days.
Highlights
- Every system placed at its NIST RMF step, with control evidence kept current from your scans and pipelines.
- Every vulnerability on BOD 26-04's deadline table and every POA&M run to verified closure, with each slip recorded.
- Authorizing Official packages assembled when an agreed trigger fires; the named official decides.
Details
Sold by
Categories
Delivery method
Deployed on AWS
New
Introducing multi-product solutions
You can now purchase comprehensive solutions tailored to use cases and industries.
Pricing
Custom pricing options
Pricing is based on your specific requirements and eligibility. To get a custom quote for your needs, request a private offer.

Legal
Content disclaimer
Vendors are responsible for their product descriptions and other product content. AWS does not warrant that vendors' product descriptions or other product content are accurate, complete, reliable, current, or error-free.
Resources
Vendor resources
Support
Vendor support
Adana Technologies replies to every inquiry within two business days. During an engagement you have a named engagement lead, a weekly status meeting and email support at admin@adanatech.com on US business days (Eastern Time). Support covers deployment, use of ATOReady and questions about deliverables. ATOReady does not grant authorizations and is not a 24x7 monitoring service, and we do not provide legal advice. Refunds, where applicable, follow the terms of your private offer. Website: