Sold by: Kraitos
Deployed on AWS
Govern and secure agentic AI across your endpoints. Monitor every prompt, tool call, MCP connection, and token spent, with policy enforcement, DLP, and compliance evidence built in.
Overview
Image
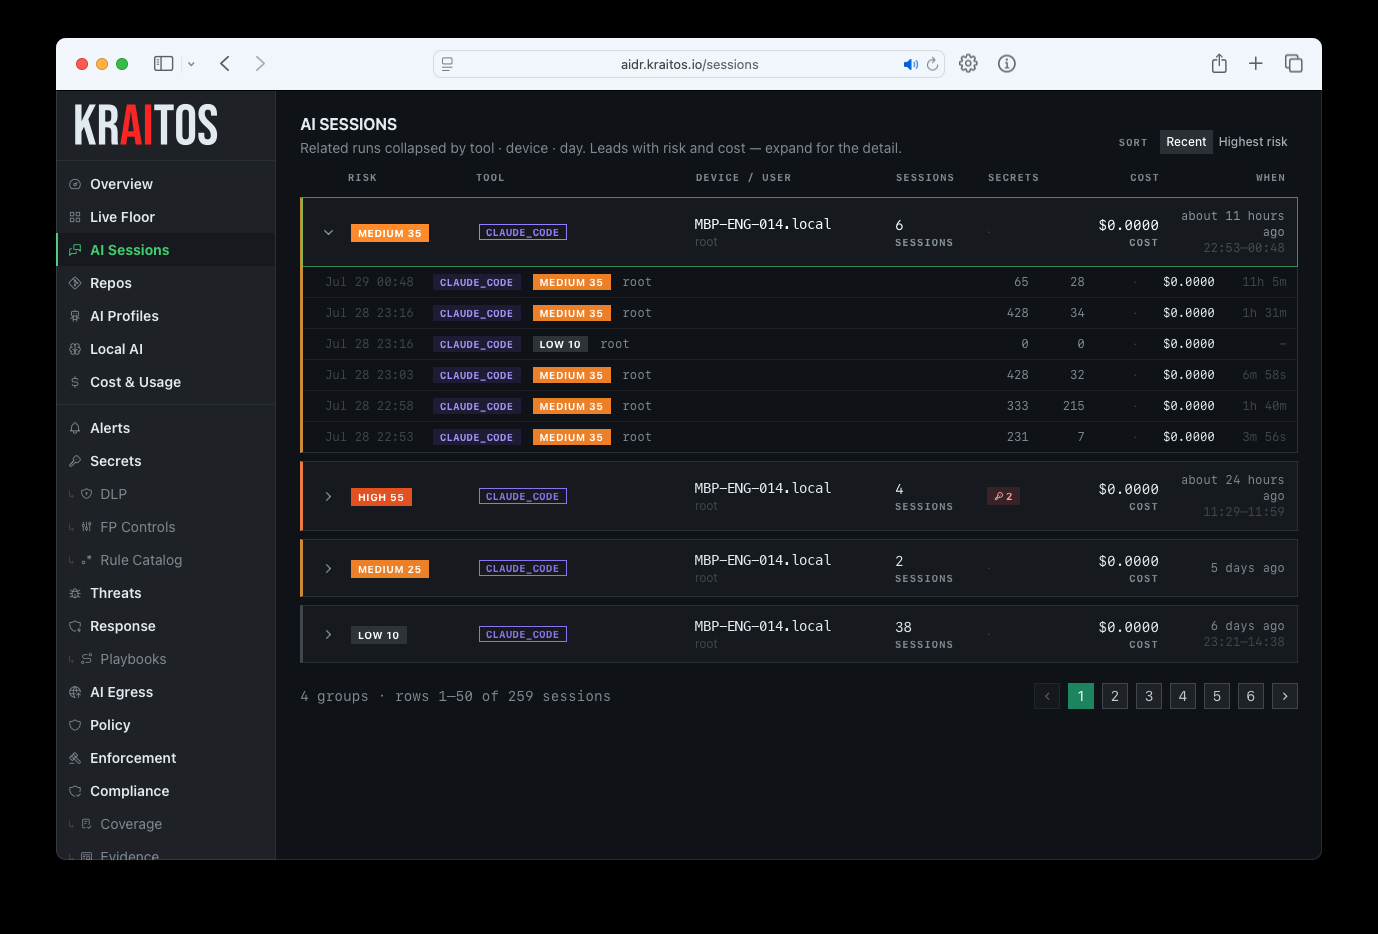
AI session timeline
Image
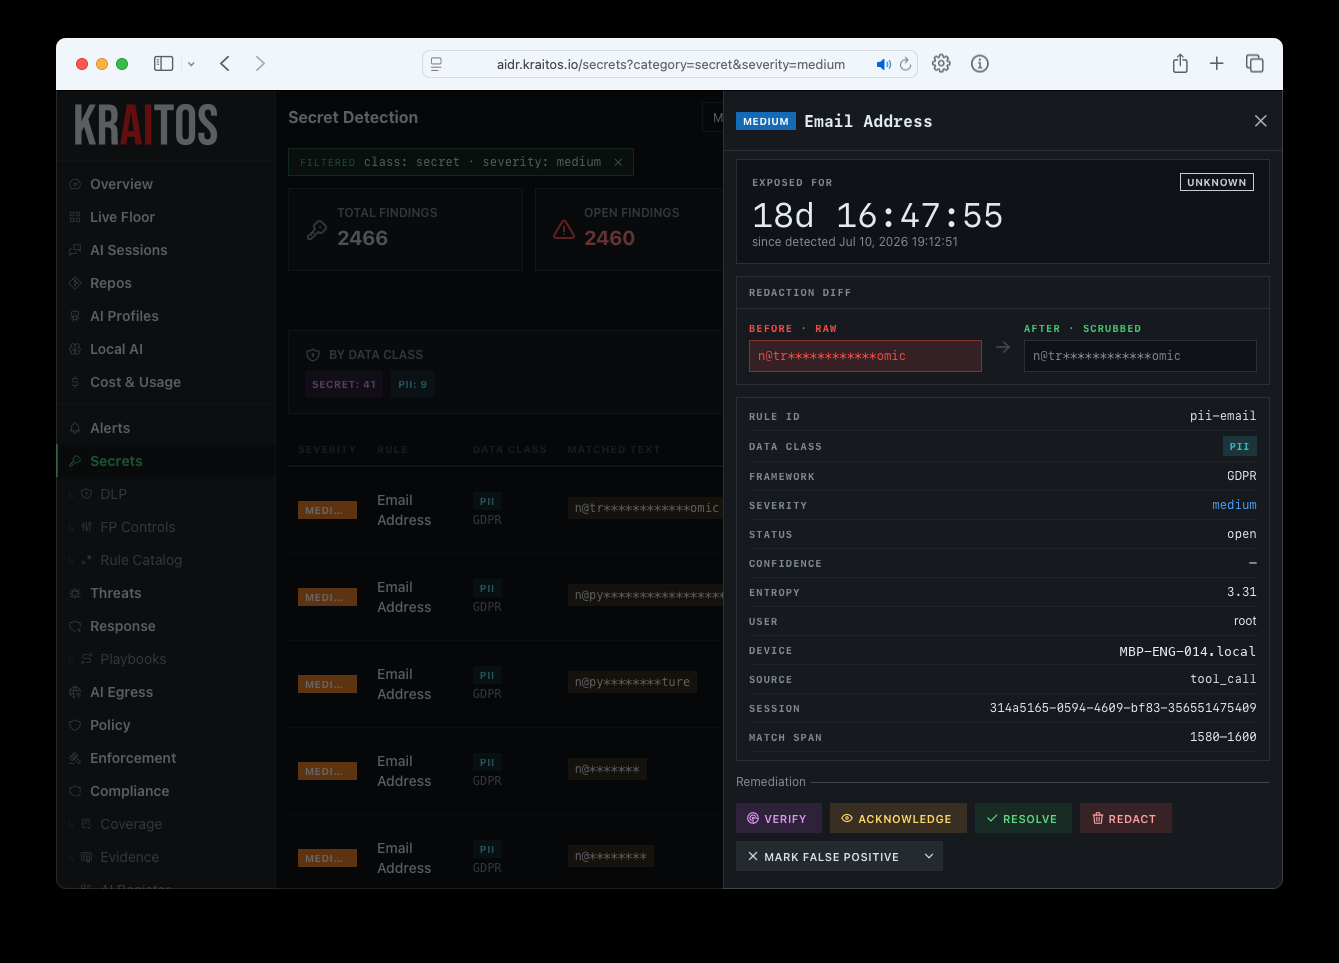
DLP redaction detail
Image
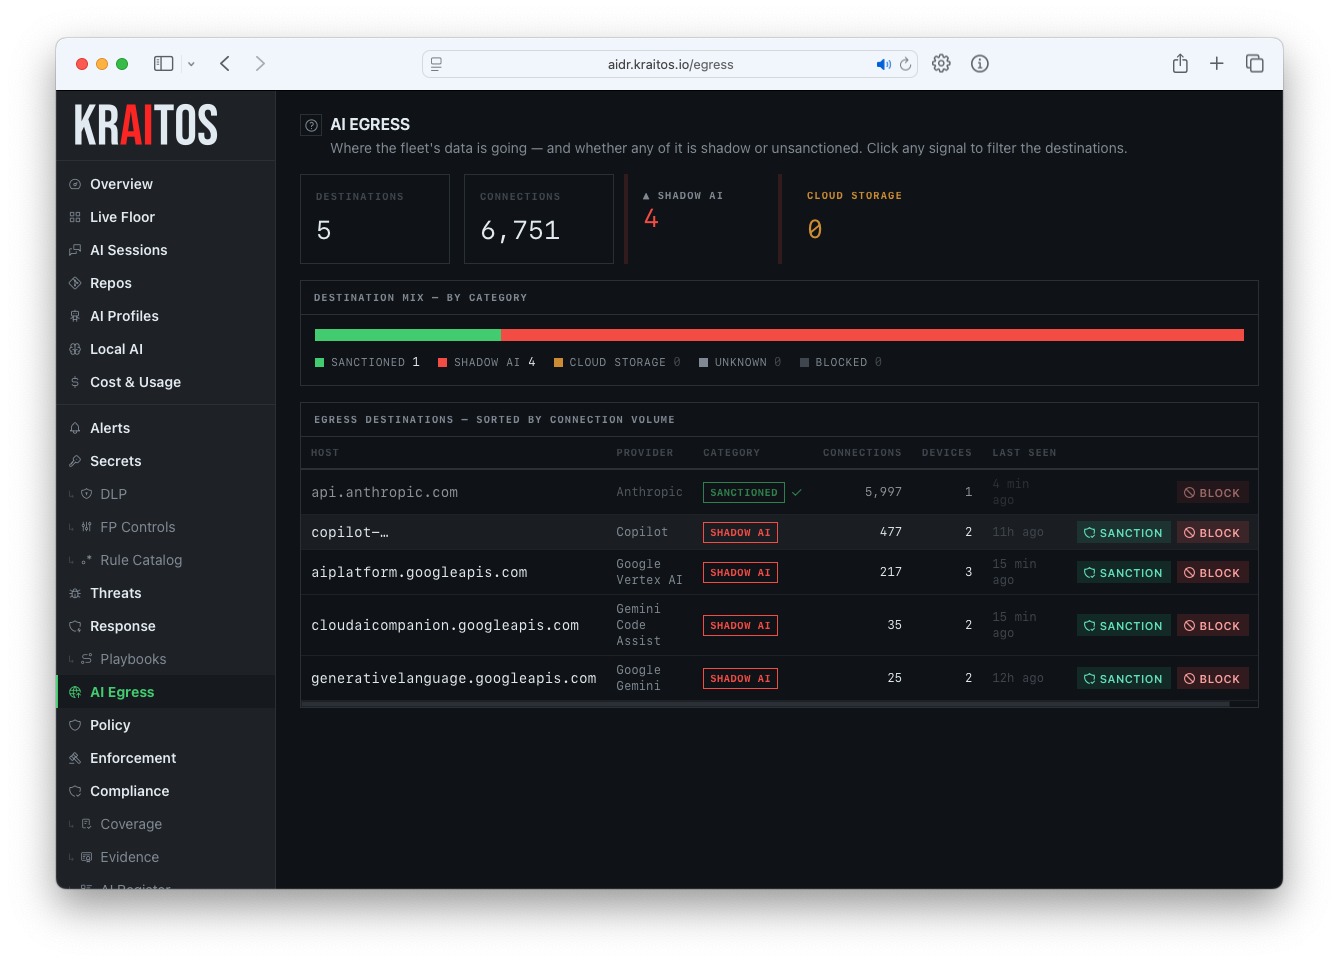
Data egress monitoring
Image
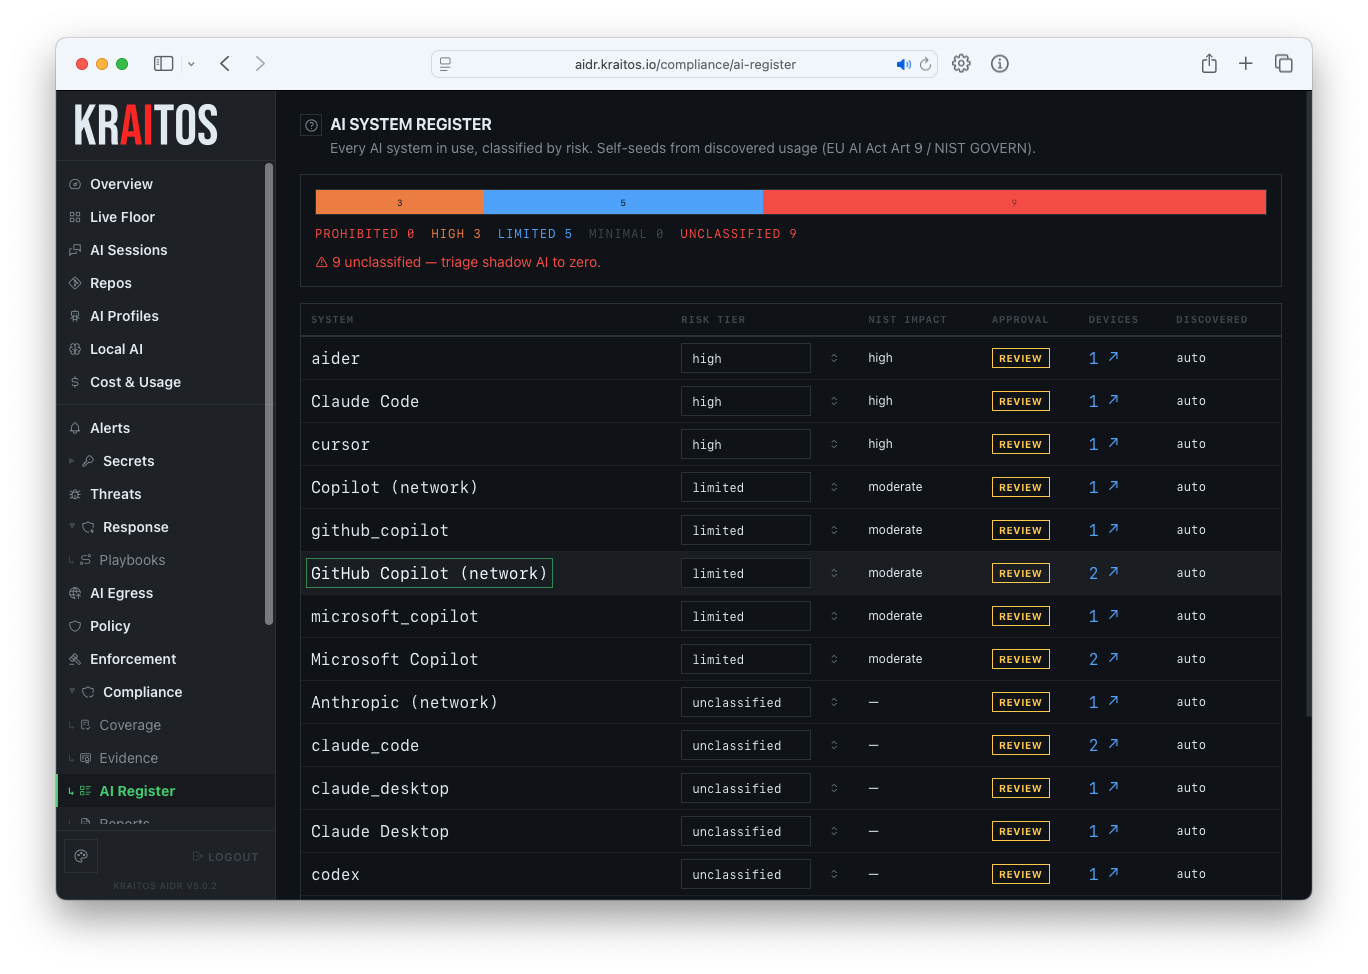
AI register and evidence
Image
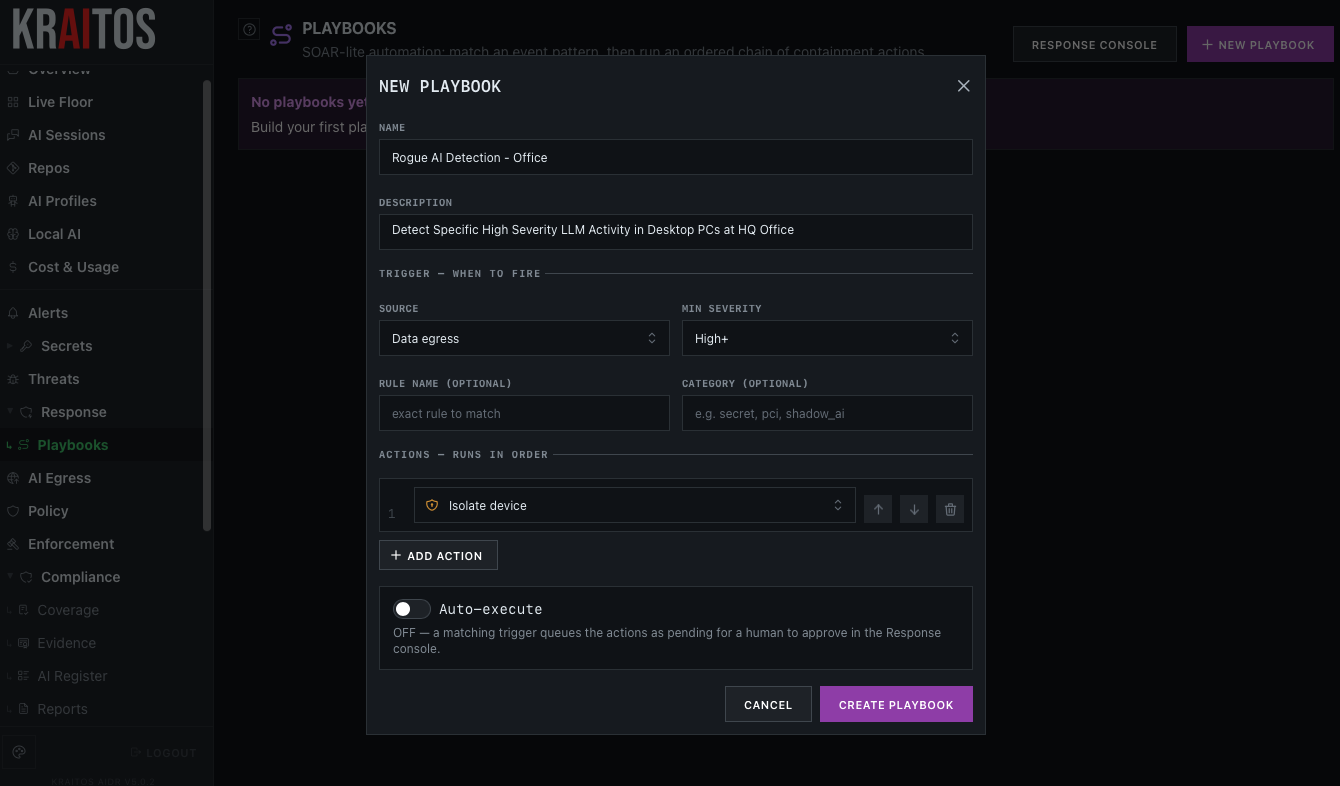
Response playbook builder
Your workforce already uses AI agents (Claude Code, Copilot, Cursor, local models) with or without an approved rollout. Kraitos AIDR gives security teams the same depth of visibility into AI agent activity that they have into network traffic, and the controls to act on it.
A lightweight endpoint agent (macOS, Windows, Linux) detects AI tools five ways: filesystem, network, behavioral heuristics, dependency audit, and session capture. It streams every prompt, response, tool call, MCP connection, and token spend to your dashboard. Policy enforcement blocks disallowed tools and destructive commands; DLP redaction stops secrets and PII at the prompt boundary; data-egress monitoring surfaces shadow AI; and the compliance engine turns all of it into signed evidence bundles, AI registers, and attestation-ready reports for ISO 27001, SOC 2, and HITRUST programs.
Billing runs through your AWS account: a simple per-device daily rate, a 14-day free trial, and no card to enter. Subscribe, create your org, install the agent, and see your AI estate on the live floor in minutes.
Highlights
- Full-fidelity AI session capture: every prompt, response, tool call, MCP connection, and token spent across Claude Code, Copilot, Cursor, and local models on macOS, Windows, and Linux.
- Act, don't just observe: policy enforcement blocks disallowed tools and destructive commands, DLP redaction stops secrets at the prompt boundary, and SOAR-lite playbooks automate response.
- Compliance-ready by default: signed evidence bundles, an always-current AI register, and attestation-ready reports for ISO 27001, SOC 2, and HITRUST programs.
Details
New
Introducing multi-product solutions
You can now purchase comprehensive solutions tailored to use cases and industries.

Features and programs
Financing for AWS Marketplace purchases
AWS Marketplace now accepts line of credit payments through the PNC Vendor Finance program. This program is available to select AWS customers in the US, excluding NV, NC, ND, TN, & VT.

Pricing
Pricing is based on actual usage, with charges varying according to how much you consume. Subscriptions have no end date and may be canceled any time.
Additional AWS infrastructure costs may apply. Use the AWS Pricing Calculator to estimate your infrastructure costs.
Dimension | Description | Cost/unit |
|---|---|---|
Team: device-day | One protected device for one day on the Team tier | $0.30 |
Business: device-day | One protected device for one day on the Business tier | $0.634 |
Dimensions summary
You pay by the device-day, meaning one protected device for one day. Billing counts only devices that are online and reporting, so idle machines add nothing. Two tiers set the rate. The Team tier fits smaller deployments, while the Business tier adds response actions, compliance dashboards, evidence export, and longer session retention. Both meter usage the same way; the tier you pick determines the per-device-day rate and the features included. Costs scale directly with how many devices report each day, so your bill tracks active fleet size rather than a fixed seat count.
Top-of-mind questions for buyers
A protected device is any machine running the agent, including laptops and servers on macOS, Linux, or Windows. Each virtual machine or physical device counts separately. Billing counts only devices that are online and actively reporting. A machine offline for the billing period is not charged.
Device counts are snapped hourly and metered before each invoice. Only online, actively-reporting devices accrue charges. A machine that goes offline stops adding to the count for the hours it is not reporting, so your bill tracks actual active usage.
You can switch tiers at any time. Because billing is metered per device, a tier change takes effect on the next invoice with no migration step. The Business tier rate then applies, and you gain response actions, compliance dashboards, evidence export, and longer session retention.
www.kraitos.io+1
Helpful?
Vendor refund policy
Refunds for unused service are considered on request within 30 days of first subscription, pro-rated to metered usage. Contact support@kraitos.io ; refunds are processed through AWS Marketplace support.

Legal
Vendor terms and conditions
Upon subscribing to this product, you must acknowledge and agree to the terms and conditions outlined in the vendor's End User License Agreement (EULA) .
Content disclaimer
Vendors are responsible for their product descriptions and other product content. AWS does not warrant that vendors' product descriptions or other product content are accurate, complete, reliable, current, or error-free.
Delivery details
Software as a Service (SaaS)
SaaS delivers cloud-based software applications directly to customers over the internet. You can access these applications through a subscription model. You will pay recurring monthly usage fees through your AWS bill, while AWS handles deployment and infrastructure management, ensuring scalability, reliability, and seamless integration with other AWS services.
Support
Vendor support
Email support at support@kraitos.io , weekdays 9 to 18:00 US Eastern, first response within 1 business day. Product documentation at docs.kraitos.io. Security contact: security@kraitos.io .
AWS infrastructure support
AWS Support is a one-on-one, fast-response support channel that is staffed 24x7x365 with experienced and technical support engineers. The service helps customers of all sizes and technical abilities to successfully utilize the products and features provided by Amazon Web Services.
Similar products
The AI-native CrowdStrike Falcon Platform provides comprehensive protection across all areas of enterprise risk - devices, identities, data, endpoints and cloud. Powered by a single agent, crowdsourced data, expert threat intelligence, and advanced AI, the Falcon Platform simplifies security operations and stops breaches.

IBM Guardium Data Detection and Response (DDR) is a capability of the IBM Guardium data security platform, delivering real-time threat detection and response. By leveraging an AI-powered engine and advanced analytics. IBM Guardium DDR alerts on risks to your data before they lead to costly breaches.

Mitiga delivers Zero-Impact Breach Prevention, a modern approach that reduces the business impact of cloud and SaaS attacks. Its AI-native Cloud Detection and Response (CDR) Platform provides proactive, real-time monitoring and broad visibility across cloud, SaaS, identity, and AI. It continuously monitors activity across your entire cloud environment, identifies anomalous behaviors, and reconstructs attacks into clear, contextualized timelines to help security teams contain active threats and minimize breach impact when traditional protection falls short.

Netzilo is AIDR (AI Detection & Response) for AI agents, governing what your agents do (tool calls, data access, network activity), not just what a model says. It detects and stops prompt injection, tool poisoning, and multi-step data exfiltration in real time across Amazon Bedrock AgentCore, MCP, and A2A, and streams enriched events to your SIEM. Deploy cloud or self-hosted, agentless or with the Netzilo Client, for AI agent security, runtime governance, and agentic AI observability.
Customer reviews
No customer reviews yet
Be the first to review this product . We've partnered with PeerSpot to gather customer feedback. You can share your experience by writing or recording a review, or scheduling a call with a PeerSpot analyst.