Sold by: Pwned Labs
Manual AWS penetration testing of IAM, S3, Lambda, EC2, ECS, EKS and cross-account trust, with findings mapped to MITRE ATT&CK and the detection that should have fired.
Overview
Image
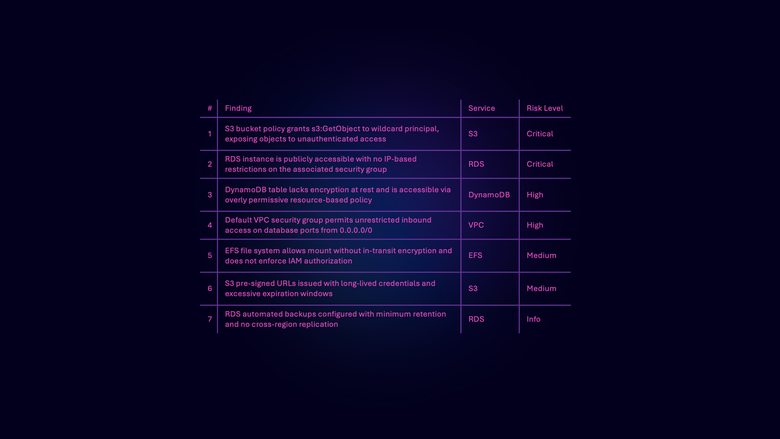
Example AWS penetration test findings
Image
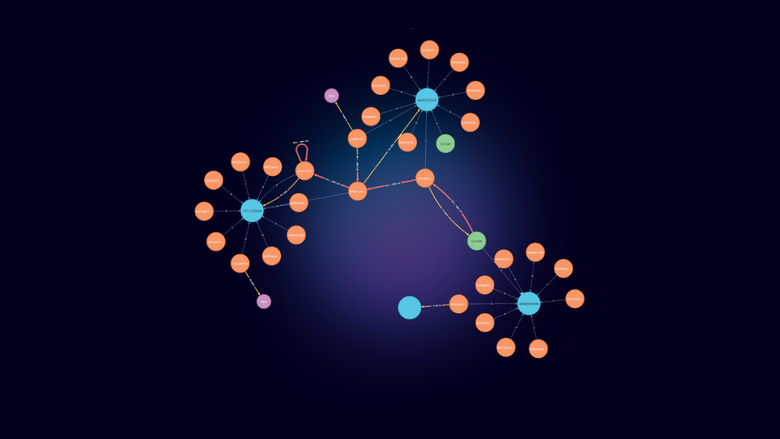
AWS attack path graph
Image
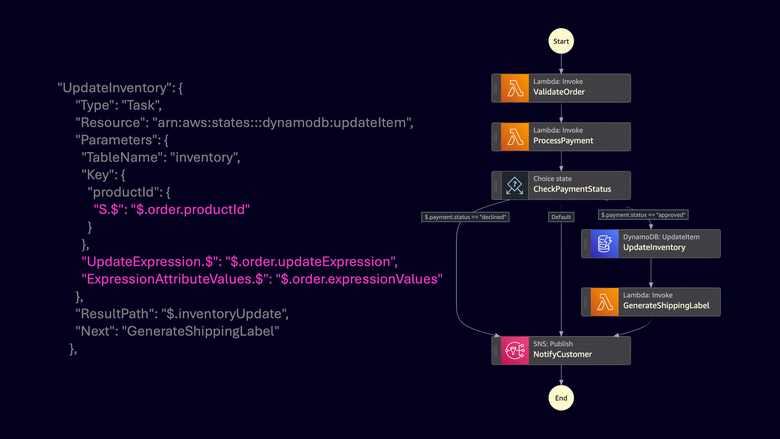
Serverless workflow testing
Pwned Labs tests your AWS environment the way an attacker would. We go beyond automated scanning to manually test IAM and IAM Identity Center, S3 and other data stores, EC2 and the instance metadata service, Lambda and API Gateway, ECS and EKS, and the cross-account trust relationships that connect them.
What we test
- IAM and identity: privilege escalation paths, overly permissive policies, role chaining, cross-account trust abuse and federation misconfigurations.
- Data storage: S3 bucket policies and ACLs, pre-signed URL abuse, snapshots and AMIs shared more widely than intended, and the paths data could take out of the account.
- Serverless and containers: injection into Lambda and API Gateway event payloads, secrets left in environment variables, overly permissive execution roles, ECS task roles, EKS pod identity, and access to the instance metadata service from inside a running container.
How we work
We agree the accounts, regions and services in scope before testing starts, and align the work with AWS's customer support policy for penetration testing. Testing follows PTES, OWASP and the MITRE ATT&CK Cloud matrix, from reconnaissance through exploitation and post-exploitation.
What you receive
An executive summary for stakeholders and a technical report for engineers. Each finding includes the evidence behind it, the specific AWS API calls involved, prioritized remediation guidance and the detection that should have caught the activity.
The techniques our testers use are the same ones we teach in our AWS labs and the Amazon Cloud Red Team Professional (ACRTP) certification, so the methodology is exercised against current AWS behavior.
Each engagement is scoped with you and priced through a private offer.
Highlights
- Manual testing of IAM, S3, Lambda, EC2, ECS, EKS and cross-account trust
- Findings mapped to MITRE ATT&CK Cloud, with the API calls involved and the detection that should have fired
- The same methodology we teach in our ACRTP AWS red team certification
Details
New
Introducing multi-product solutions
You can now purchase comprehensive solutions tailored to use cases and industries.

Pricing
Custom pricing options
Pricing is based on your specific requirements and eligibility. To get a custom quote for your needs, request a private offer.

Legal
Content disclaimer
Vendors are responsible for their product descriptions and other product content. AWS does not warrant that vendors' product descriptions or other product content are accurate, complete, reliable, current, or error-free.
Resources
Vendor resources
Support
Vendor support
Email hi@pwnedlabs.io or book a call at https://pwnedlabs.io/business/demo .
We reply to AWS Marketplace enquiries within two business days, agree scope and timing with you before a private offer is issued, and contact you with next steps within two business days of an accepted offer.