Sold by: Reco
Deployed on AWS
Reco secures the ecosystem so enterprises can enable agents with confidence. The Reco Platform discovers every agent, app, and identity across your environment, prioritizes real risk over raw alert volume, and remediates before exposure becomes a breach.
4.6
Overview
Image
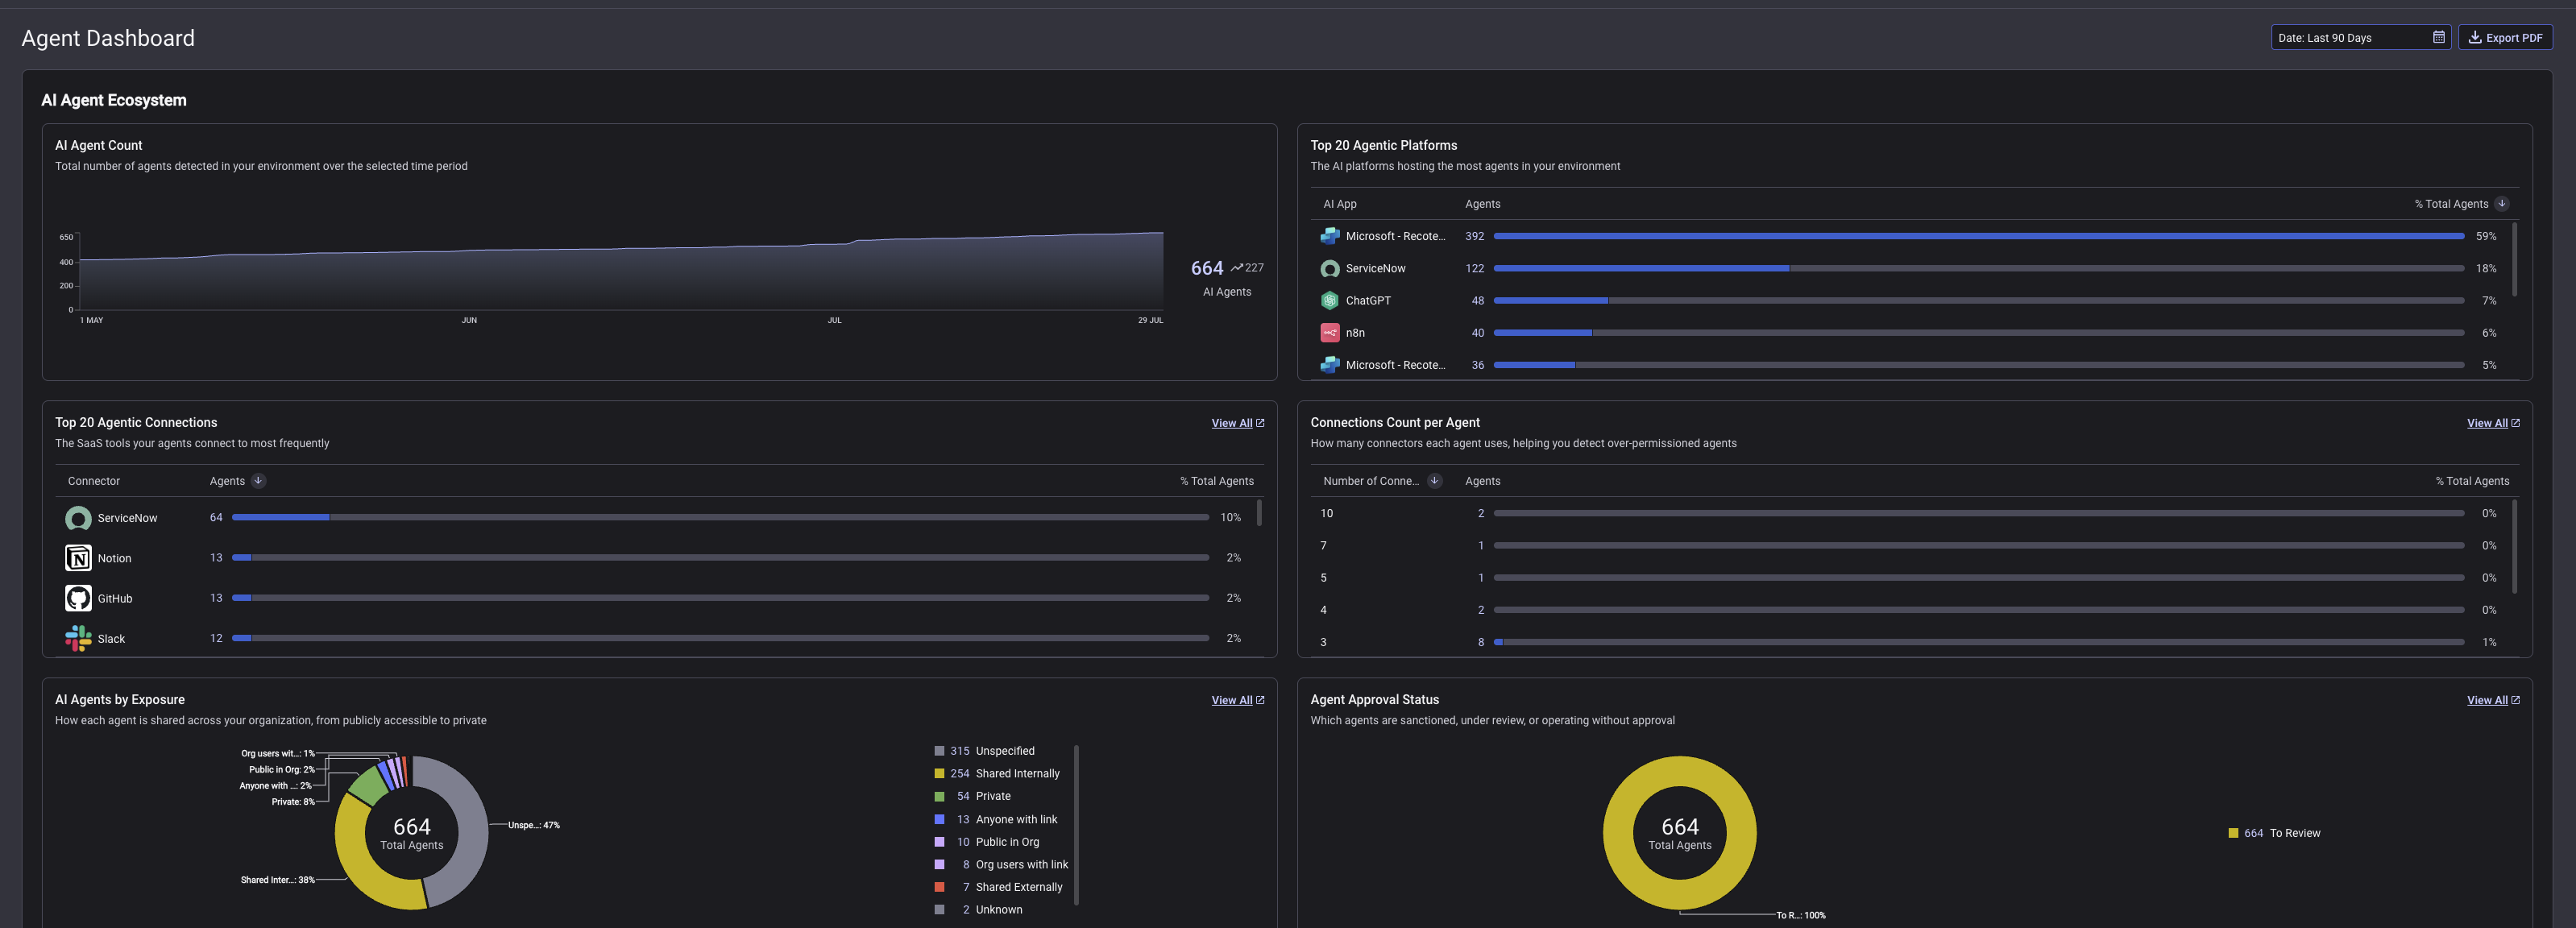
Executive Dashboard: AI Agent & App Discovery
Image
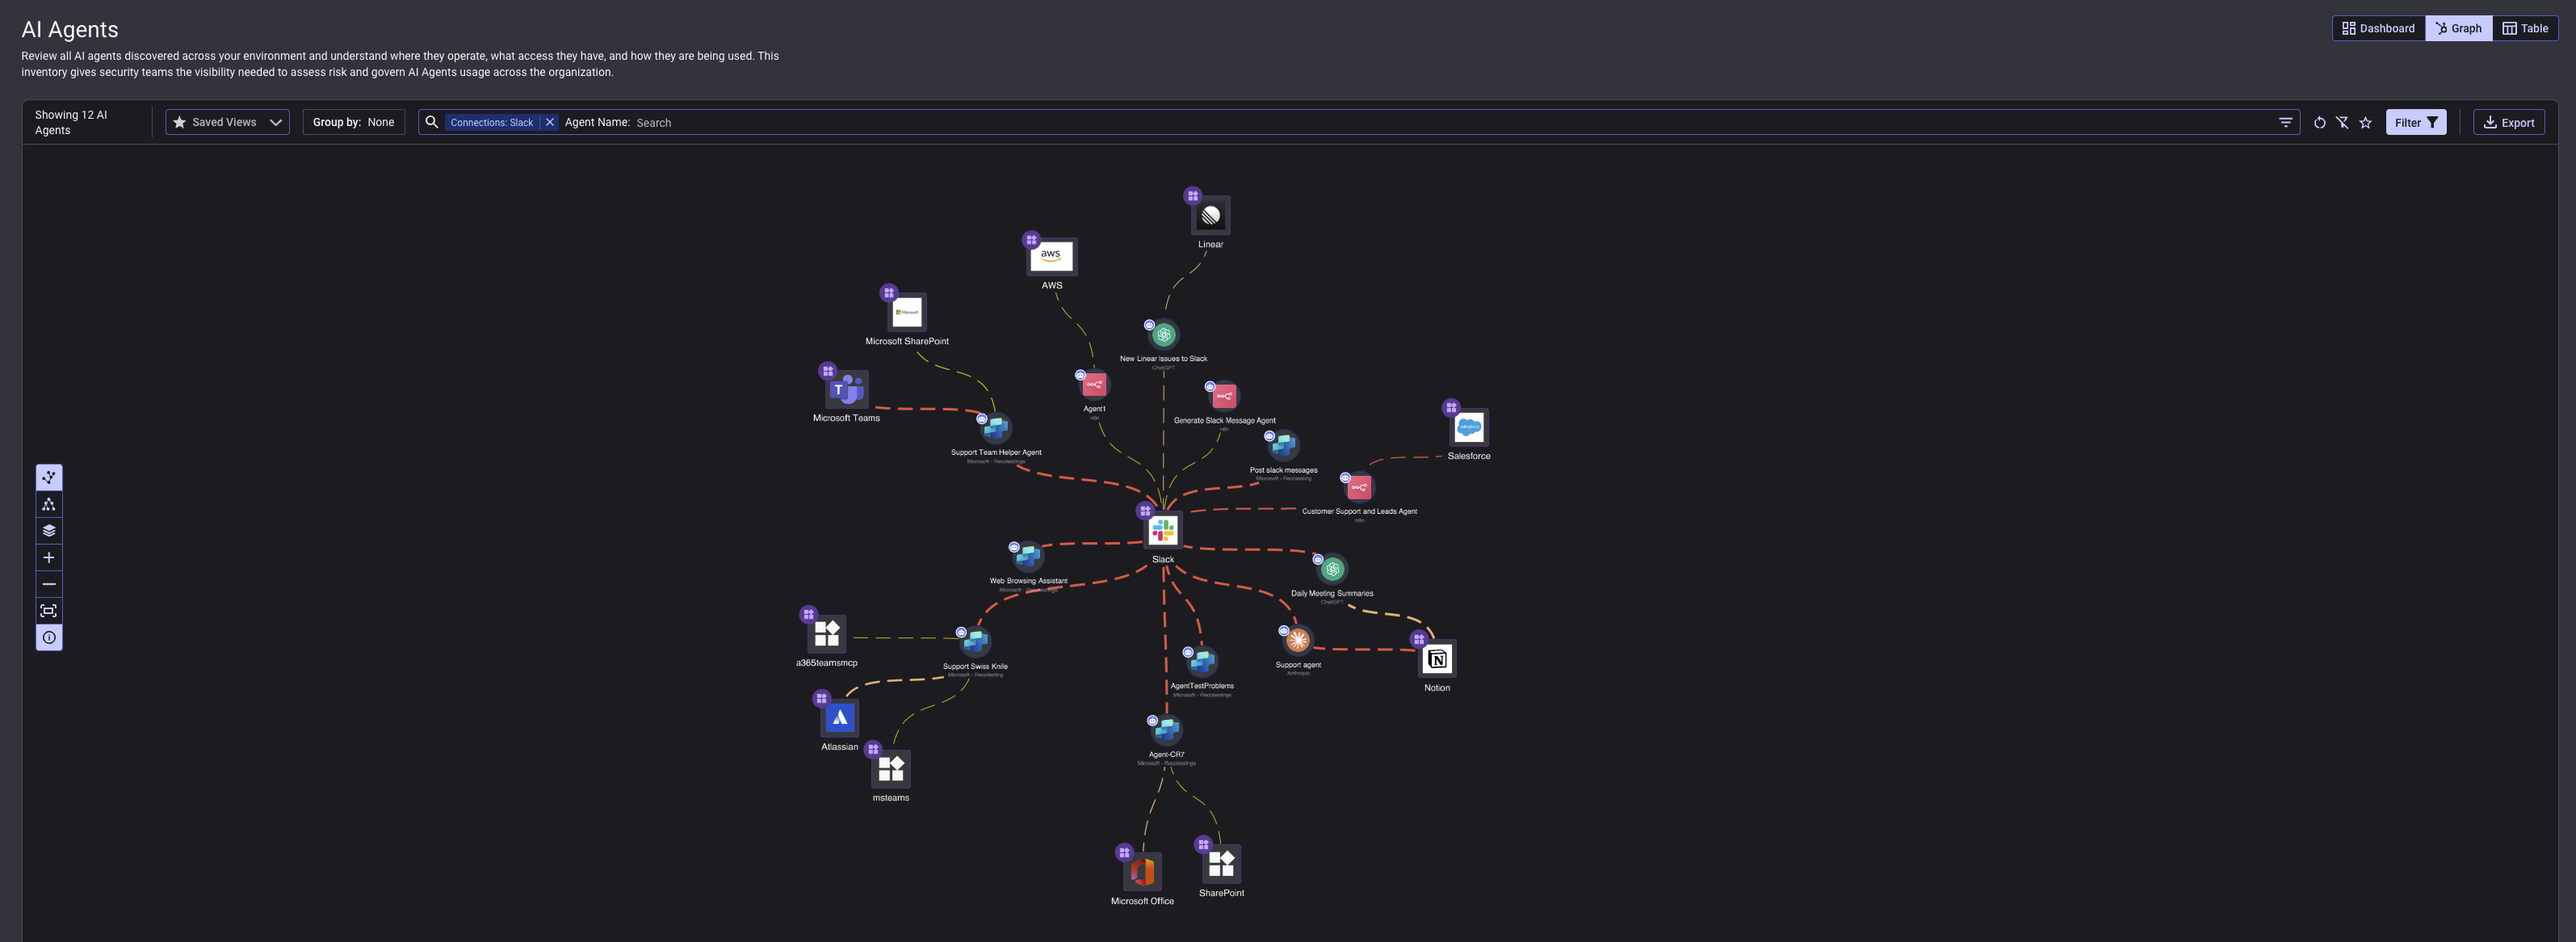
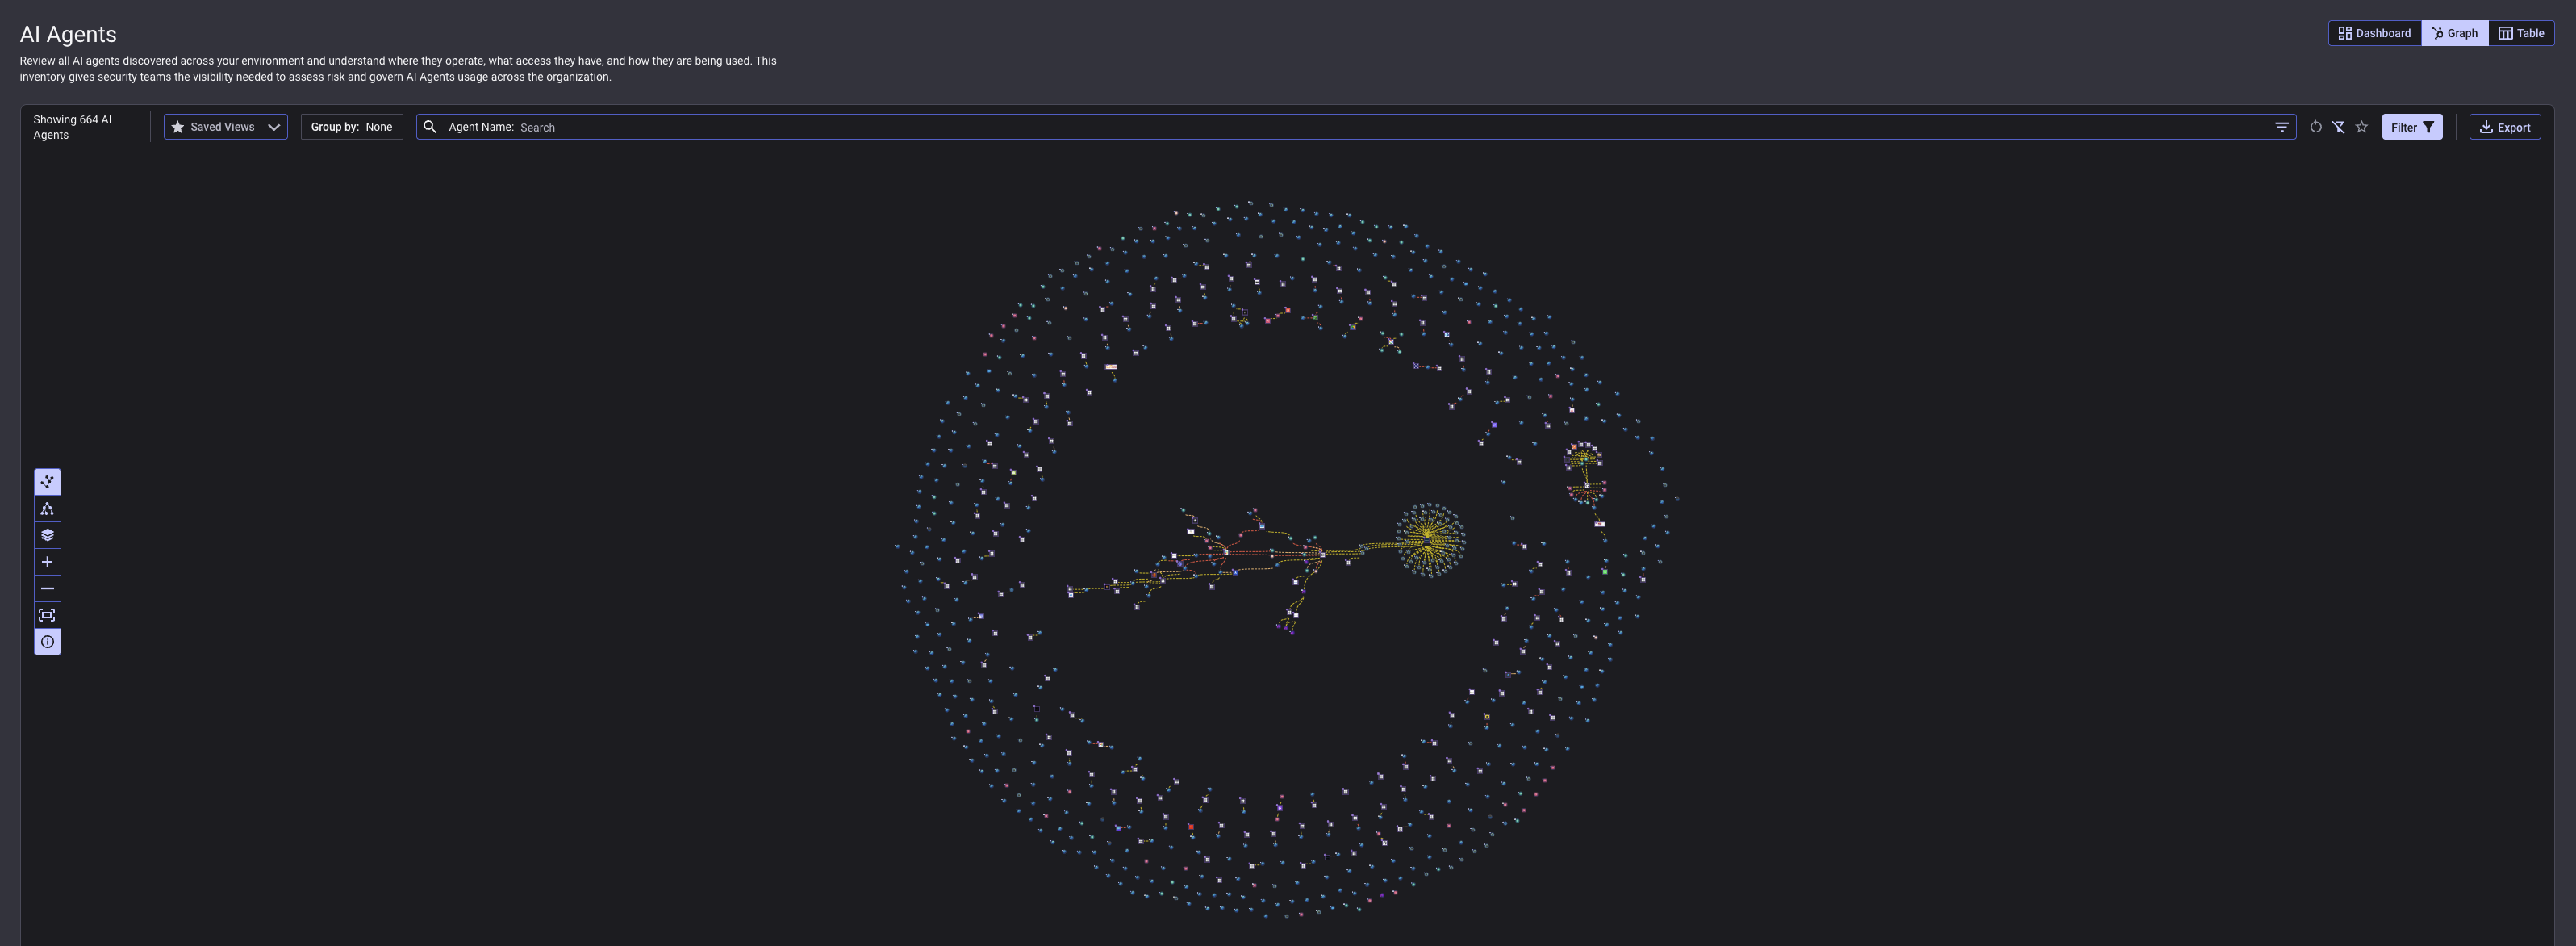
Agent Knowledge Graph: Map Agent and App Ecosystem
Image
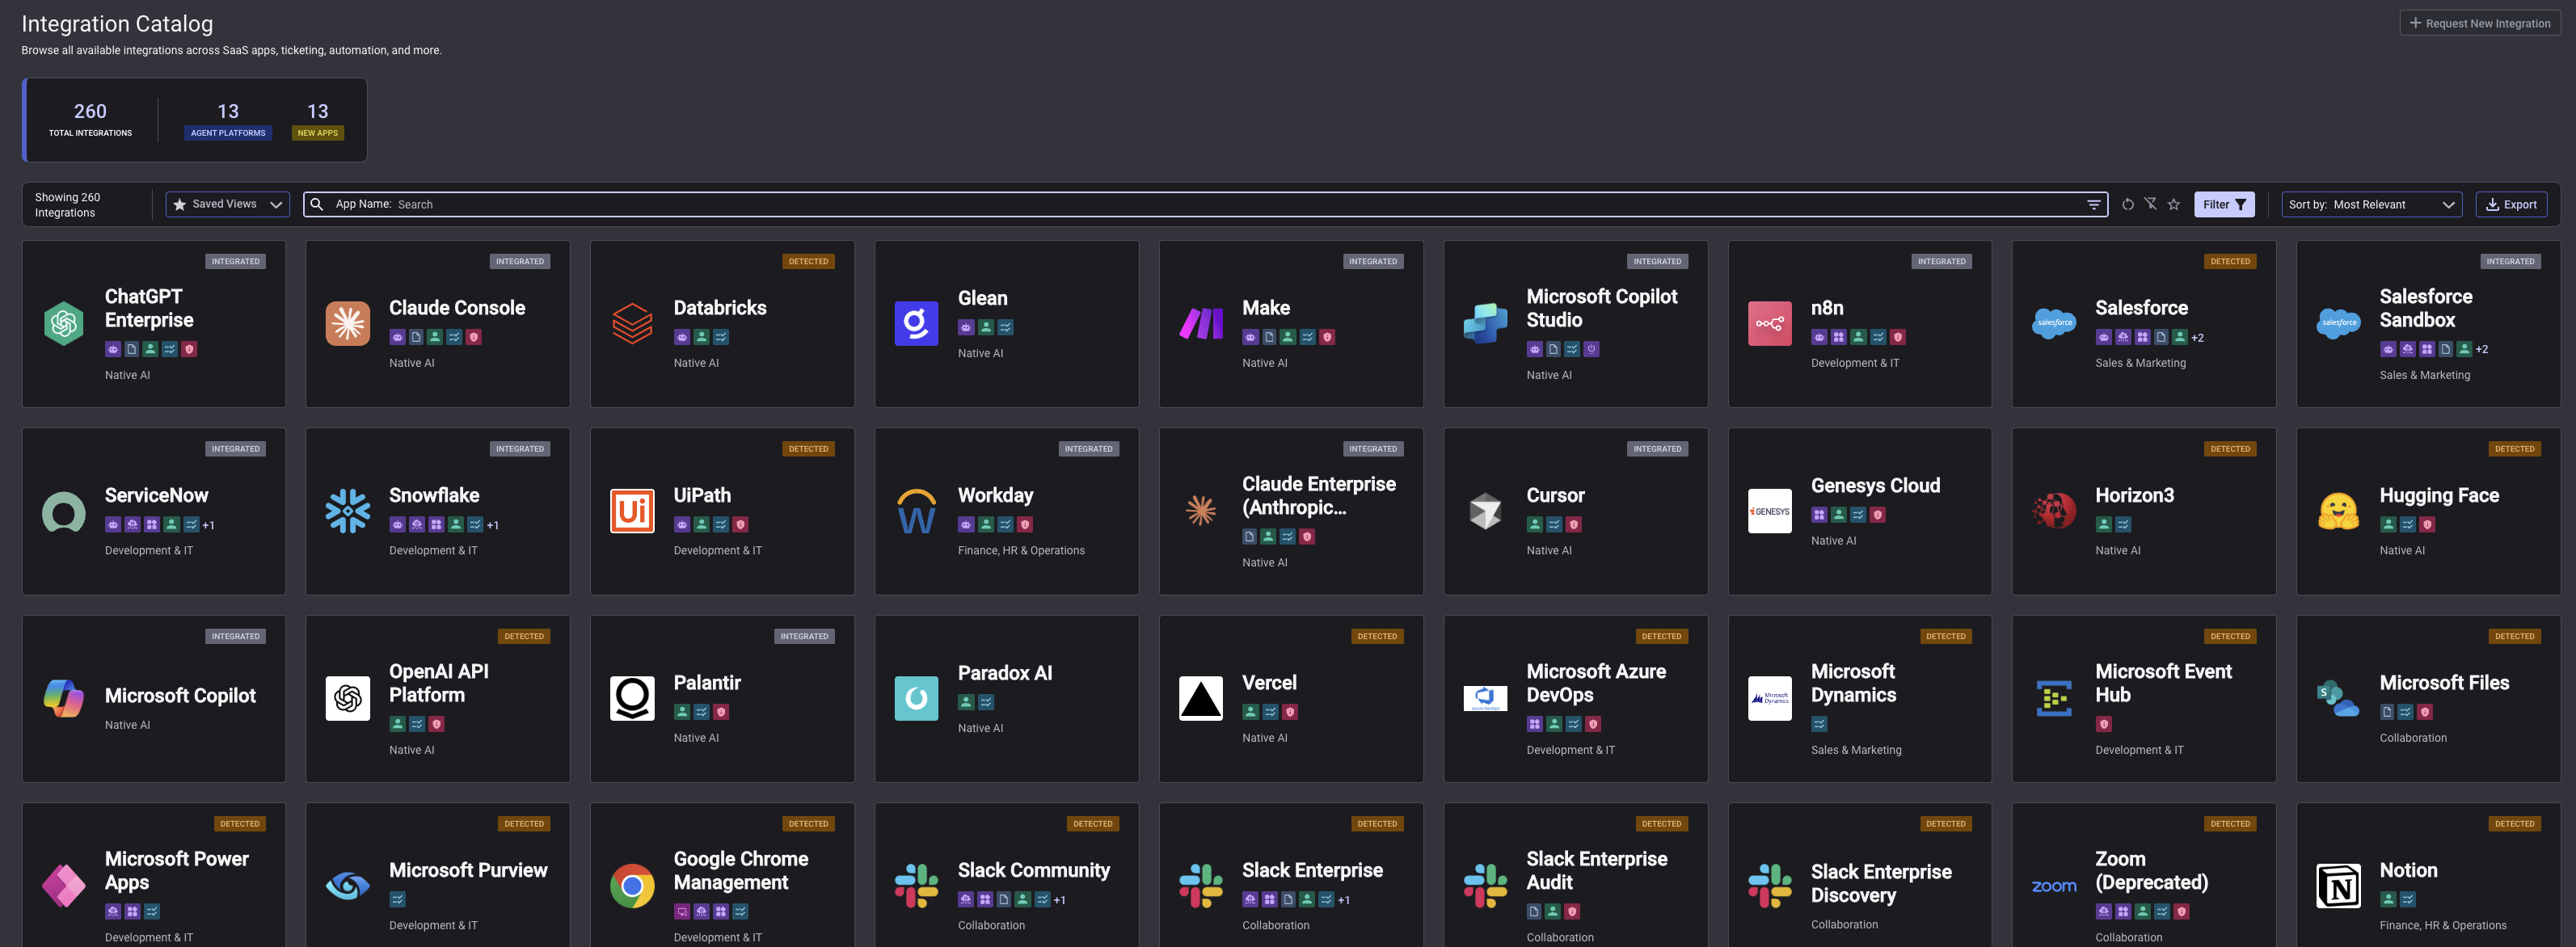
Reco App Factory: 260+ Integrations
Image
Agent Knowledge Graph: Agent Ecosystem Map
AI is the most important initiative in the business, and security has to keep up. Most AI security conversations focus on the AI enterprises build in-house. The bigger, faster-growing risk is the AI they buy: thousands of third-party apps shipping new AI features, millions of agents built on new frameworks every week, and billions of interactions among agents, apps, and the AI inside them.
Reco secures that ecosystem. The Reco Platform runs on three components: Reco Factory builds deep third-party agent and app integrations in hours, not weeks. Reco Library is the largest agent and app catalog in the market, giving security teams pre-classified risk profiles from day one instead of a blank slate, with over 260 agent and app integrations available to-date. Reco Graph maps every agent, app, and connection in your ecosystem across four dimensions (identity, permissions, connectivity, and activity), so nothing runs unmonitored.
The workflow is simple: discover every agent, app, and connection; prioritize risk by real-world impact, not alert volume; and remediate with precision, routing findings and revoking access without disrupting the business. By securing the ecosystem, Reco gives enterprises the confidence to scale agents without fear.
Highlights
- Discover every agent, app, and identity. Reco maps your entire AI ecosystem using the largest agent and app catalog on the market - 260+ integrations. Security teams start with real risk profiles, not a blank slate.
- Prioritize real risk, not alert volume. Reco correlates agent identity, permissions, connectivity, and activity to surface the exposures that actually matter. Cutting noise so teams can focus on what's genuinely exploitable.
- Remediate before exposure becomes a breach. Automatically revoke risky agent and AI app access and route every finding to the right owner - without disrupting the business. That's how you scale AI agent adoption with confidence.
Details
New
Introducing multi-product solutions
You can now purchase comprehensive solutions tailored to use cases and industries.
Features and programs
Trust Center

Access real-time vendor security and compliance information through their Trust Center powered by Drata or Vanta. Review certifications and security standards before purchase.
Buyer guide
Gain valuable insights from real users who purchased this product, powered by PeerSpot.
Financing for AWS Marketplace purchases
AWS Marketplace now accepts line of credit payments through the PNC Vendor Finance program. This program is available to select AWS customers in the US, excluding NV, NC, ND, TN, & VT.

Pricing
Pricing is based on the duration and terms of your contract with the vendor. This entitles you to a specified quantity of use for the contract duration. If you choose not to renew or replace your contract before it ends, access to these entitlements will expire.
Additional AWS infrastructure costs may apply. Use the AWS Pricing Calculator to estimate your infrastructure costs.
Dimension | Description | Cost/12 months |
|---|---|---|
Reco Essential | SSPM - Posture Management & Compliance up to 3 integrations | $18,000.00 |
Reco Advanced | SaaS Security - SaaS detection and response, Identity & Access Governance with unlimited integrations | $90,000.00 |
Dimensions summary
You choose between two contract tiers billed by units. Reco Essential covers SaaS Security Posture Management, giving you posture monitoring and compliance for up to 3 integrations. Reco Advanced expands the scope to SaaS Security with detection and response plus Identity and Access Governance, and it supports unlimited integrations. The tiers scale by both capability and integration count: Essential caps how many applications you connect, while Advanced removes that limit and adds identity governance and threat response functions. Pick the tier that matches how many apps you need to secure and which security functions you require.
Top-of-mind questions for buyers
An integration is a connection between Reco and one SaaS application in your stack, such as a productivity suite or CRM. Reco pulls identity, permission, and configuration data from each connected app. Essential lets you connect up to three of these applications for posture monitoring and compliance.
Essential caps you at three connected applications. To connect more apps, you move to Reco Advanced, which removes the integration limit entirely. This is a tier change, not an automatic overage. Advanced also adds detection and response plus identity and access governance functions.
Essential provides SaaS Security Posture Management: configuration monitoring and compliance mapping. Advanced adds SaaS detection and response, which alerts you to account compromise and configuration drift, plus Identity and Access Governance, which maps identities and enforces least-privilege access across connected apps.
www.reco.ai+3
Helpful?
Vendor refund policy
Please contact us at support@reco.ai
Custom pricing options
Request a private offer to receive a custom quote.
Legal
Vendor terms and conditions
Upon subscribing to this product, you must acknowledge and agree to the terms and conditions outlined in the vendor's End User License Agreement (EULA) .
Content disclaimer
Vendors are responsible for their product descriptions and other product content. AWS does not warrant that vendors' product descriptions or other product content are accurate, complete, reliable, current, or error-free.
Delivery details
Software as a Service (SaaS)
SaaS delivers cloud-based software applications directly to customers over the internet. You can access these applications through a subscription model. You will pay recurring monthly usage fees through your AWS bill, while AWS handles deployment and infrastructure management, ensuring scalability, reliability, and seamless integration with other AWS services.
Support
Vendor support
Reco provides enterprise-grade support to all customers. Buyers get a dedicated customer success manager, onboarding and deployment assistance, and access to Reco's support team via email and slack.
AWS infrastructure support
AWS Support is a one-on-one, fast-response support channel that is staffed 24x7x365 with experienced and technical support engineers. The service helps customers of all sizes and technical abilities to successfully utilize the products and features provided by Amazon Web Services.
Updated weekly
By Reco
By Check Point Software Technologies

By AppOmni, Inc
Sentiment is AI generated from actual customer reviews on AWS and G2
Functionality
Ease of use
Customer service
Cost effectiveness
Positive reviews
Mixed reviews
Negative reviews
AI generated from product descriptions
Agent and Application Discovery
Maps every agent, app, and identity across the environment using a catalog of over 260 agent and app integrations with pre-classified risk profiles.
Multi-Dimensional Ecosystem Mapping
Tracks agent, app, and connection relationships across four dimensions: identity, permissions, connectivity, and activity.
Risk Prioritization and Correlation
Correlates agent identity, permissions, connectivity, and activity data to identify exploitable exposures and reduce alert noise.
Automated Access Remediation
Automatically revokes risky agent and AI app access while routing findings to appropriate owners without business disruption.
Third-Party Integration Framework
Builds deep third-party agent and app integrations through Reco Factory component to enable rapid ecosystem security coverage.
API-Based Threat Detection and Prevention
Scans uploads, downloads, stored files, and shared content using API-based scanning to detect and block known and unknown threats including malware, phishing, data theft, and compromised identities across SaaS applications.
AI-Powered Data Loss Prevention
Utilizes multilayer AI/ML engine with private LLMs, NLP, NER, and neural classifiers to identify sensitive data across 800+ types with high precision, enabling accurate DLP across API-based scanning activities.
SaaS Discovery and Visibility
Automatically discovers all SaaS applications including OAuth connected apps, shadow SaaS, third-party integrations, and unmanaged plugins across the environment to provide complete visibility into sanctioned and unsanctioned services.
Continuous Security Posture Management
Continuously monitors configurations, identity exposures, SaaS-to-SaaS connections, and compliance violations against standards including GDPR, SOC 2, ISO 27001, and NIST, with prioritized alerts and automated remediation capabilities.
Identity Risk Detection and Behavioral Analytics
Uses ThreatCloud AI and behavioral analytics to identify anomalous identity activity, account takeover attempts, risky SaaS integrations, and unauthorized data access without disrupting users.
Continuous Security Posture Management
Continuous monitoring and assessment of SaaS security posture across applications including M365, Salesforce, ServiceNow, and Workday
Threat Detection and Analysis
Real-time threat detection capabilities within SaaS environments with security insights and threat identification
Misconfiguration and Data Exposure Detection
Identification of misconfigurations, data exposures, and configuration drift across the entire SaaS estate
Unsanctioned Connection Discovery
Discovery and mapping of unsanctioned third-party and fourth-party SaaS connections within the organization
Identity and Privilege Management
Management of identities and privileges with compliance requirement mapping across SaaS applications
Standard contract
No
Customer reviews
Ayush Pandey
Centralized visibility has cut manual SaaS security investigations and now streamlines reviews
Reviewed on Oct 06, 2026
Review provided by PeerSpot
What is our primary use case?
My main use case for Reco is that it has been a valuable part of our security and SaaS visibility stack. Over time, I have found its main value to be giving us better visibility into our SaaS environment and helping identify areas that require attention. Reco is relatively straightforward to work with, and its centralized view makes it easier to investigate issues compared with checking individual applications manually.
A specific example of how I used Reco to solve a problem and improve my workflow is when we were trying to understand an unfamiliar SaaS application in our environment. Instead of manually going through different systems to figure out who is using it and whether it needs attention, Reco gives a centralized place to start that investigation, which saves quite a bit of time, especially when dealing with a growing number of applications. For me, it is primarily the visibility that matters.
I think another benefit is the context around the visibility because it helps us decide which findings actually need attention, rather than treating everything the same.
How has it helped my organization?
The biggest positive impact Reco has had on our organization is improving our SaaS visibility and reducing the amount of manual work involved in security investigation. Previously, we had a lot of manual work going on in security audits. Before having this centralized visibility, understanding an application often means checking multiple systems, looking at access and permissions, and sometimes reaching out to different teams to understand who is using it and why. With Reco, we have a much more centralized view, allowing us to quickly investigate usage and identify the users or teams associated with an unfamiliar application instead of spending a lot of time gathering that information manually. This helps us reduce investigation time and prioritize our security efforts.
I can estimate that previously it was taking thirty minutes to forty-five minutes for messaging someone to check things, and now it reduces to five to six minutes, which is a reduction of around sixty to sixty-five percent. If we calculate it on a larger scale concerning fifteen to twenty hours, then it is a great estimation because fifty to sixty percent time saved is a lot.
What is most valuable?
The best features that Reco offers, in my opinion, are the centralized view of the SaaS applications being used across our organization. For example, if a new SaaS application starts being used by an employee, Reco helps us identify it and investigate things such as who is using it, how widely it is being used, and whether it needs to be reviewed from a security perspective. This is particularly useful because manually tracking every application across a growing organization would be time-consuming. We also use the visibility to prioritize applications or users that require attention rather than manually reviewing everything. For us, the biggest value is having centralized SaaS visibility combined with security context, which helps us reduce manual investigations and gives our security team a better understanding of our SaaS environment.
I had one incident approximately six months ago when our security team noticed that a new SaaS application, such as a project management or AI productivity tool, was being used by an employee. Previously, to investigate it, we might have had to check our identity providers to see which employees have access, look at application logs to understand usage, check with the application owner, and then manually determine whether the application should be approved. With Reco, we can start from a centralized view and quickly understand the application, who is using it, how broadly it is being used, and what security information is available around it. Instead of spending thirty or forty-five minutes collecting information from several places, we get the initial context much faster and focus on deciding whether there is an actual risk. I think this is the biggest time saving for us. It is not just that Reco puts information on one screen; it reduces the back and forth between different tools and teams during an investigation.
Whenever I use Reco, I feel safe. Governance and security are definitely important considerations, especially because SaaS environments can contain sensitive organizational user data. Understanding what data is being processed is crucial.
The breadth of coverage Reco offers for SaaS operations is strong, particularly around SaaS visibility, application discovery, and user and access context. Reco is not just showing us a list of applications; it gives us additional context that helps us understand how those applications are being used and where we may need to investigate further. For example, identifying applications across the organization to understand associated users and access helps prioritize potential security or governance issues, which becomes particularly valuable as our SaaS environment grows.
The use of eight different sensors for SaaS application discovery has made a noticeable difference for us. The main benefit is that we are not relying on a single source of information to discover SaaS applications, as different applications can show up through different signals, giving us broader coverage and making the discovery process more reliable. Having multiple sensors feed into Reco and provides a more complete picture of what is actually being used in the organization, reducing blind spots and the amount of manual discovery work for our team.
The LLM integration is interesting because the knowledge graph gives context about the relationships between users, application access, and security signals. Instead of an analyst manually connecting those dots, the AI can help explain what is happening and why something might deserve attention, significantly speeding up investigation. This is probably the biggest differentiator compared with more traditional SaaS visibility tools.
The AI agent security capability is particularly useful because AI agents are becoming another category of SaaS technology users that security teams need to understand. The biggest challenge is that agents can be connected to applications, APIs, and data sources, and sometimes have permissions to take actions on behalf of users. Discovering those connected AI agents and bringing them into the same governance process as the rest of our SaaS is quite valuable because we need to understand what is connected to what permission it has, what data it can access, and who owns it.
My impression of Reco's Device Management feature when it comes to discovering every device in our organization is quite positive, particularly from a visibility perspective. One of the challenges with device management is getting a complete and up-to-date picture of what devices are present. Reco provides centralized device visibility without maintaining separate inventories and correlating devices with users and SaaS applications manually.
What needs improvement?
I think overall Reco works well for our use case, but there are a few areas where it could become even more valuable. The biggest one would be more customizations and automations, such as having more flexibility in creating organization-specific dashboards and reports, because different security teams have different priorities. Being able to customize which metrics, applications, risks, and users we want to track would be helpful. I would also like to see more automations around remediation, such as triggering actions automatically based on predefined policies without human dependency to avoid delays.
Another improvement I wish to see is deeper integration with other security and identity tools, because the more information Reco can correlate automatically, the less time the security team has to spend moving between different systems. Overall, I would not say there is a major gap; it is more about enhancing the strong visibility Reco already provides by adding more customization, automation, and integrations.
My impression of the accuracy and reliability of Reco's AI output is that there is a lot of manual analysis the security team has to do.
For how long have I used the solution?
I have been using Reco for the last one year, and I value this service highly.
Which solution did I use previously and why did I switch?
Before using Reco, we were actually using a combination of existing identity and security tools. The main limitation was that the information was fragmented, so we could not get a complete picture from different tools, which forced us to rely on a mix of Wiz, Okta, Zscaler, and Microsoft Defender.
How was the initial setup?
Setting up Reco agents for automating tasks in our business processes is relatively straightforward, especially once the integrations and permissions are already in place. An agent could detect a SaaS application that meets certain risk criteria and then automatically notify the user owner or initiate a security review. The main thing we focus on is permission and guardrails for higher impact actions, wanting approval and auditability rather than giving the agent complete autonomy.
What was our ROI?
We have seen a positive return on investment, estimating that the initial investigation effort has dropped by roughly fifty percent. Something that previously took thirty to forty minutes might now take fifteen to twenty minutes, providing the biggest measurable efficiency gain by saving twenty to forty hours of team time to focus on something more complex or prioritized.
What's my experience with pricing, setup cost, and licensing?
We have purchased Reco through the Google Cloud Marketplace. Overall, the setup cost was straightforward because it is a SaaS, and we did not have major infrastructure costs. Most of our effort was configuring integrations, permissions, and workflows. From a licensing perspective, the main thing I look for is predictable pricing as the number of users and applications grows.
Which other solutions did I evaluate?
We evaluated several options before choosing Reco, which included comparing solutions such as Wiz, Netscope, Microsoft Defender, and assessing what we could have accomplished with our existing tools. Ultimately, we compared how well each solution could provide complete SaaS visibility.
What other advice do I have?
Reco is not deployed in a completely private cloud environment for my organization. The cloud provider we use with Reco is Google Cloud Platform, or GCP. I did not find any much deviations since our organization is a long-term user of this Google Cloud provider, and most of the services are from Google Cloud, which we trust.
My advice for others looking into using Reco is to consider that we evaluated a few alternatives before selecting it, focusing on SaaS discovery, visibility into users and access, security context, and the potential to eliminate manual investigations, which is why Reco stood out with its centralized view across different signals.
I would rate Reco around eight out of ten. I choose this rating because of the improvements I am expecting, particularly more automations and customizations. The majority of things are correct, but I think in this AI era, everything is automated, and those two things would significantly reduce time. Regarding how Reco is deployed in my organization, I took the plan.
Krishan Y.
Streamlined Security Monitoring with Reco
Reviewed on Aug 20, 2026
Review provided by G2
What do you like best about the product?
I use Reco to monitor and manage security with better visibility into user activity, potential risks, and security events, which helps our team identify suspicious behavior and investigate issues faster. I like most about Reco is its visibility and ease of use, which brings useful security insights together in one place. The straightforward interface and actionable alerts help us reduce the time we spend investigating security issues. The visibility Reco provides into user activity helps us spot unusual behavior or potential risks earlier, and the alerts help prioritize what needs our attention. These features make Reco valuable, allowing us to get a clear picture of what's happening across our environment without digging through multiple sources.
What do you dislike about the product?
One area that could be improved is the level of customization. We would benefit from more flexibility around alerts, dashboards, and reporting to better tailor Reco to our specific team requirements. It would also be helpful to have more detailed documentation and guidance for advanced configurations and integrations. These are relatively minor areas, but improving them would make the overall experience even better.
What problems is the product solving and how is that benefiting you?
Reco improves security management by providing better visibility into user activity and potential risks. It reduces manual investigation and streamlines identifying and prioritizing security risks, saving time. The straightforward interface and actionable alerts help us understand and respond to suspicious behavior quickly.
Nirmal K.
Reco Excels at Discovering Hidden SaaS Integrations and AI Agents
Reviewed on Aug 18, 2026
Review provided by G2
What do you like best about the product?
Shadow SaaS & AI Agent Discovery: Reco excels at uncovering hidden integrations. It continuously discovers unsanctioned SaaS apps, embedded GenAI tools, third-party OAuth connections, and autonomous AI agents that often bypass traditional security perimeters.
What do you dislike about the product?
Varying Connector Depth: While Reco connects to an impressive number of applications, the depth of visibility and remediation capabilities can vary significantly depending on the target app. SaaS tools with limited or poorly documented APIs will naturally offer less granular security coverage.
What problems is the product solving and how is that benefiting you?
Identity-First Threat Detection (ITDR): Instead of just looking at static configurations, it monitors behavioral signals. It links posture data with user roles to detect privilege abuse, compromised accounts, or excessive access across both human users and "non-human identities" (like service accounts or API keys).
Shivansh V.
Excellent Visibility Into Identities, Permissions, and Integrations
Reviewed on Aug 03, 2026
Review provided by G2
What do you like best about the product?
Reco maps all user identities, permissions, and integrations, helping teams detect security risks and reduce attack surfaces efficiently.
What do you dislike about the product?
Reco is highly effective for visibility and automation, but it can struggle with highly customized or niche SaaS applications that use non-standard APIs. It also requires careful fine-tuning to prevent excessive alerts or inaccurate notifications. In addition, it mainly operates as a detection-only tool and lacks built-in remediation features, which can create extra work for users who need automated fixes.
What problems is the product solving and how is that benefiting you?
Organizations gain a unified, real-time view across all applications, identities, and AI agents, which makes it easier to spot, assess, and prioritize risks.
Sharon Lawrence
Improved security monitoring has prioritized critical alerts but still generates many false positives
Reviewed on Jul 23, 2026
Review provided by PeerSpot
What is our primary use case?
I used Reco when I worked at the company as a software security tool that monitored all the software the company was using. Reco functioned as a detection tool that identified any type of malicious event occurring within the software environment for users.
What is most valuable?
What I appreciated most about Reco was its strong detection capability. It detected when we received a large volume of critical alerts and displayed those at the top, alerting us that it was urgent to investigate them.
What needs improvement?
What I disliked about Reco was, I remember the system didn't have tickets #'s and it was hard to keep up with sometimes. I would have to save the incident as web link to keep up. Its sometimes produced a lot of false positives. There were things that were not really alerts but triggered anyway, and we had to go through many of them even though nothing was actually wrong. But, then they found a way fine-tune it more later.
For how long have I used the solution?
I have been using Reco for about a year overall in my career.
What do I think about the stability of the solution?
I have seen some lagging and downtime with Reco. There were times when there were glitches, when dealing with logs pages, but they fixed them, even though it took a while to address them. They would either fix them or tell you how to work around them.
What do I think about the scalability of the solution?
Regarding Reco's scalability, I think they can add more to it, but I'm not entirely sure how to phrase this.
How are customer service and support?
I did not have to contact Reco's customer support because the client took care of that issue, but we did have team meetings with Reco sometimes. Sometimes we discussed any problems and concerns we had during live Reco tech support calls.
Which solution did I use previously and why did I switch?
We used alternatives such as Gurucul, which allows you to see malicious things triggering on a network basis instead of just the software, and we also had CrowdStrike. Those are a few alternatives we used.
How was the initial setup?
The initial deployment of Reco was not difficult.
What about the implementation team?
Maintenance for Reco was being taken care of by them.
Which other solutions did I evaluate?
Of all the alternatives, I preferred Reco more because it was easier.
What other advice do I have?
Reco is spelled R E C O. If Reco had a system for setting up agents to automate tasks in our business processes, that would be beneficial and would make things go much faster. Regarding Reco's use of eight different sensors for SaaS application discovery in our environment, I do not understand what they mean by that. I would rate this review a 7.