Sold by: SentinelOne
Deployed on AWS
SentinelOne Singularity AI SIEM revolutionizes your security operations on AWS. Eliminate the skyrocketing ingestion costs and data overloads of legacy SIEMs by utilizing Observo AI to filter data volumes. This provides a deeper, richer dataset, enabling smarter and more accurate detections, accelerated generative AI investigations, and precise responses with Singularity Hyperautomation. AI SIEM is fundamentally shifting the role of security analyst from manual, repetitive tasks to strategic defense. Empower your team to accelerate investigations and mitigate critical risks with a fast, scalable, and intelligent SIEM built for the Autonomous SOC.
4.1
Overview
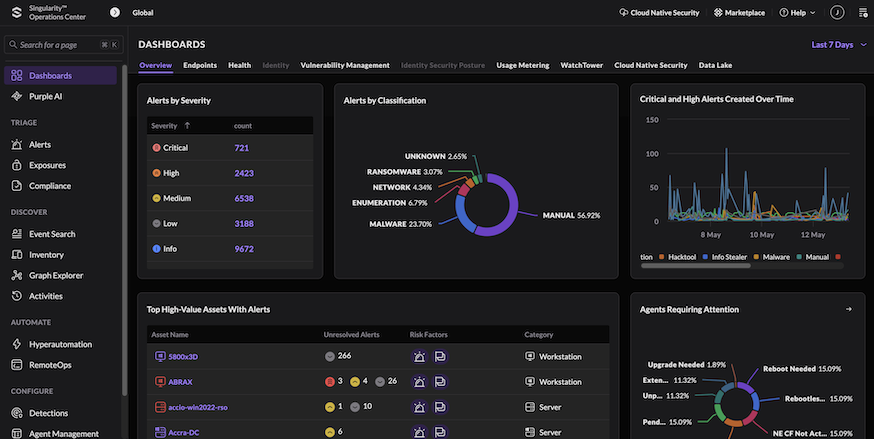
SentinelOne Singularity AI SIEM is a cloud-native SaaS solution that revolutionizes security operations by unifying cutting-edge generative and agentic AI with advanced hyperautomation. This fundamentally shifts the security analyst's role from repetitive, manual tasks to strategic threat analysis and proactive defense, enabling teams to operate with unprecedented speed and efficiency.
Unlike legacy SIEMs, our platform is built on an open, unified data lake designed for the scale and speed of modern cloud environments. It processes rich, unfiltered data to deliver autonomous threat mitigation, drastically reducing alert fatigue and mean time to resolution (MTTR) for AWS customers.
Key Features & Benefits
Autonomous & Agentic AI: Critical threats are autonomously mitigated by our AI, seamlessly augmenting human analysts for effective threat hunting and investigations.
Hyperautomation Workflows: Streamline security operations with no-code automation to design and deploy workflows that automate triage, investigation, and response processes.
Observo AI for Data Optimization: Our integration gives you an AI-native pipeline that ingests, enriches, and optimizes data before it reaches the SIEM. This reduces ingestion costs by ensuring you only pay for critical security posture data.
Purple AI for Accelerated SecOps: Our generative AI analyst is built into the platform to reduce manual effort. It provides instant summaries and automates threat hunting with natural language to accelerate investigations.
Seamless AWS Integrations
SentinelOne Singularity AI SIEM is designed to integrate seamlessly into your AWS security ecosystem, providing enhanced visibility and simplified operations.
Amazon Security Lake: Ingest high-fidelity security data from SentinelOne and other sources into Amazon Security Lake for a unified view, simplifying compliance and enabling in-depth threat hunting.
AWS Security Hub: Automatically send and receive security findings, allowing for centralized management and a comprehensive security posture assessment across your entire AWS environment.
Amazon GuardDuty: Enhance your threat detection by correlating SentinelOne data with findings from GuardDuty, gaining a deeper understanding of malicious activity in your AWS accounts.
AWS AppFabric: Get a unified, contextualized view of user activity across your SaaS applications and your AWS environment, improving your ability to detect and respond to insider threats and compromised accounts.
NEW - AWS Security Incident Response: Manage security incident response across AWS environments within Hyperautomation's no-code canvas, adding context from both external and internal sources and reducing MTTR.
Experience the Autonomous SOC
Break free from the limitations of legacy SIEMs and empower your security team to focus on what matters most. With SentinelOne Singularity AI SIEM on AWS, you can achieve faster threat detection, more efficient investigations, and a stronger security posture.
Highlights
- 100x faster than legacy SIEM
- 50% lower operational costs and 246% ROI compared to legacy SIEM
- 99% reduction in risk exposure, and 80% faster threat detection compared to AI SIEM
Details
New
Introducing multi-product solutions
You can now purchase comprehensive solutions tailored to use cases and industries.

Features and programs
Trust center

Access real-time vendor security and compliance information through their Trust Center powered by Drata or Vanta. Review certifications and security standards before purchase.
Buyer guide
Gain valuable insights from real users who purchased this product, powered by PeerSpot.

Financing for AWS Marketplace purchases
AWS Marketplace now accepts line of credit payments through the PNC Vendor Finance program. This program is available to select AWS customers in the US, excluding NV, NC, ND, TN, & VT.

Pricing
Pricing is based on the duration and terms of your contract with the vendor. This entitles you to a specified quantity of use for the contract duration. If you choose not to renew or replace your contract before it ends, access to these entitlements will expire.
Additional AWS infrastructure costs may apply. Use the AWS Pricing Calculator to estimate your infrastructure costs.
Dimension | Description | Cost/12 months |
|---|---|---|
Contact us for pricing | Daily ingestion starting from $721 | $125,000.00 |
Dimensions summary
This listing uses a single contract-based pricing dimension. Your cost is driven by daily data ingestion volume, with pricing starting from the amount shown in the table. You pay based on how much security data you feed into the platform each day, so the price scales with your ingestion needs. Because pricing is quote-based, you contact the vendor to set final terms for your environment. There are no separate tiers or add-on line items in the Marketplace table — the daily ingestion rate is the one metric that determines your commitment.
Top-of-mind questions for buyers
Daily ingestion measures the volume of security data you feed into the platform each day. This includes telemetry from cloud, identity, endpoints, and third-party tools routed through one data pipeline. Your daily total across all these sources sets the metric your contract is priced against.
Your price scales with daily ingestion, so feeding more data each day raises your cost. The platform is built to ingest large volumes without forcing early filtering or moving older data to slow archives. Because pricing is quote-based, you contact the vendor to set terms for higher ingestion levels.
The Marketplace table shows one metric: daily ingestion. Data pipelines, Purple AI investigation, and Hyperautomation response run on the same platform foundation and share the same data. There are no separate line items in the table for these capabilities. Contact the vendor to confirm what your contract covers.
sentinelone.com+1
Helpful?
Vendor refund policy
Contact us for refund questions or concerns.
Custom pricing options
Request a private offer to receive a custom quote.

Legal
Vendor terms and conditions
Upon subscribing to this product, you must acknowledge and agree to the terms and conditions outlined in the vendor's End User License Agreement (EULA) .
Content disclaimer
Vendors are responsible for their product descriptions and other product content. AWS does not warrant that vendors' product descriptions or other product content are accurate, complete, reliable, current, or error-free.
Delivery details
Software as a Service (SaaS)
SaaS delivers cloud-based software applications directly to customers over the internet. You can access these applications through a subscription model. You will pay recurring monthly usage fees through your AWS bill, while AWS handles deployment and infrastructure management, ensuring scalability, reliability, and seamless integration with other AWS services.
Support
Vendor support
Support is available for these solutions via telephone or our customer support portal. Contact: 1-855-868-3733 General Inquiries: sales@sentinelone.com
AWS infrastructure support
AWS Support is a one-on-one, fast-response support channel that is staffed 24x7x365 with experienced and technical support engineers. The service helps customers of all sizes and technical abilities to successfully utilize the products and features provided by Amazon Web Services.
Similar products
Unlock enterprise-wide security for your AWS environment with SentinelOne Singularity Platform. This AI-powered solution provides real-time threat detection and automated response across your infrastructure, ensuring continuous protection at infinite scale. By autonomously securing endpoints, cloud workloads, and identity, SentinelOne delivers total visibility while eliminating security silos. Integrate seamlessly with AWS and leverage our unified data lake and Purple AI to accelerate investigations and gain deeper insights. Secure your AWS cloud and focus on innovation with the speed and efficiency of AI.
Block attacks and secure your entire cloud with SentinelOne Singularity Cloud Security, an AI-powered CNAPP providing deep visibility and robust, real-time protection to defend your AWS environment from initial access to mission target. It unifies proactive exposure management, and real-time protection to safeguard your AWS infrastructure, workloads (VMs, containers), and data with AI-powered detection and automated response. Try Cloud Security for free!
Observo AI, a SentinelOne Company, helps you reduce security and observability costs by 50% or more while resolving incidents 40% faster.
Purple AI Model Context Protocol (MCP) Server provides secure, seamless integration between the Singularity Platform and any AI framework or large language model. Acting as a universal translator and intelligence hub, it empowers developers and partners to build custom agentic AI experiences powered by the full context and analytics of the SentinelOne platform. The open-source Purple AI MCP Server is available today on GitHub and will also be deployable as an EKS and through Amazon Bedrock, using Agent Core. Users will need to have an active deployment of SentinelOne console and be able to obtain the SentinelOne Singularity Console token and url to be able to deploy and use the Purple AI MCP server.
Customer reviews
reviewer2915043
Centralized monitoring has improved threat detection speed and simplified alert investigations
Reviewed on Nov 05, 2026
Review provided by PeerSpot
What is our primary use case?
My main use case for SentinelOne Singularity AI SIEM is centralized log management, fast threat detection, and creating a clear dashboard that helps us spot issues quickly.
For example, we spotted repeated failed logins from one source IP to a specific destination late at night, and the alert showed up clearly on the dashboard, enabling us to respond fast and block the noise.
It helps us save time, keep everything organized, and make decisions quickly without chasing logs across different tools.
How has it helped my organization?
SentinelOne Singularity AI SIEM has positively impacted my organization by making threat detection faster and easier to understand, enabling us to respond quicker and spend less time searching for information.
In our case, the dashboard reduces the time to understand an alert. Previously, we had to read raw logs across tools, which could take 15 to 20 minutes per alert, but now with the dashboard and filter views, we are closer to five minutes to understand what is happening.
SentinelOne Singularity AI SIEM has improved our SOC's efficiency significantly by helping prioritize important alerts, so we spend less time investigating the ones that do not matter.
It improved response time by helping us spot suspicious activity quickly and focus on critical alerts, preventing us from being stuck in manual investigation.
In our experience, using SentinelOne Singularity AI SIEM has helped reduce the risk of downtime by catching suspicious activity earlier, leading to smoother operations and quicker incident handling.
Since implementing SentinelOne Singularity AI SIEM, our organization's security posture feels stronger and more proactive.
Our security posture has improved with better visibility across security events, faster threat detection, and improved incident response.
Consolidating tools into SentinelOne Singularity AI SIEM has reduced operational overhead since our team is not bouncing between separate dashboards.
What is most valuable?
The best part of SentinelOne Singularity AI SIEM is the clear dashboard that makes threat detection easy to understand, plus a simple alert mechanism that saves time, and centralizing logs so we do not jump between tools is also a significant win.
The dashboard has made the biggest difference for me because it gives a quick, clear picture, enabling us to understand what is happening without guessing.
The combination of a clean dashboard and centralized logs is what makes everything faster and less stressful because it gives us confidence that we are not missing something important.
The governance and security aspects of SentinelOne Singularity AI SIEM feel solid for day-to-day use. Role-based access made access control straightforward, and the platform seems secure and stable with nothing that raised a red flag on compliance or data handling.
The accuracy and reliability of SentinelOne Singularity AI SIEM feel solid. Alerts are consistent and not fluctuating erratically, so we do not waste time chasing false positives.
My impression of the AI-driven threat detection capabilities of SentinelOne Singularity AI SIEM is strong and steady. The alerts are consistent, and the details align with the logs, making its detection feel trustworthy.
The real-time monitoring feature of SentinelOne Singularity AI SIEM is quite useful. It lets us spot suspicious activity as it happens, allowing us to respond without much delay.
We have used the automated workflow features of SentinelOne Singularity AI SIEM to reduce repetitive tasks, especially around alert handling and basic investigation steps.
SentinelOne Singularity AI SIEM's AI-driven analytics has helped reduce false positives to some extent. The AI analytics pick up suspicious patterns more accurately, allowing our SOC to focus more on the real threats.
What needs improvement?
It would be helpful if some alerts had cleaner, clearer explanations right away, such as suggesting next steps inside the alert, and fewer clicks to get from alert to raw event details would make the triage even faster.
Integration could be more plug-and-play, and improving built-in guidance for new analysts would help cut the learning curve. Performance-wise, it is adequate for us, but easier bulk searches would make investigations smoother.
It would be helpful for each alert to come with clear suggested next steps right inside the alert, so analysts do not have to guess or click around too much. Making integration more plug-and-play would smooth out setup for new data sources.
For how long have I used the solution?
I have been using SentinelOne Singularity AI SIEM for around a year.
What do I think about the stability of the solution?
SentinelOne Singularity AI SIEM has been stable in our environment, handling our data volumes without causing disruption.
What do I think about the scalability of the solution?
SentinelOne Singularity AI SIEM has been stable and adaptable as our data volume and IT setup became more complex.
SentinelOne Singularity AI SIEM is scalable and handles growing log volume while supporting monitoring across multiple services.
How are customer service and support?
The customer support was helpful, responsive, and easy to work with.
I would rate the customer support an eight out of ten. The support team was responsive, helpful, and professional.
Which solution did I use previously and why did I switch?
Before, I used traditional SIEM tools for log monitoring and analysis, but I switched to SentinelOne Singularity AI SIEM because I wanted better centralized visibility and faster threat detection.
What was our ROI?
I have seen a positive return on investment through time saving and improved team efficiency since I can now understand an alert in about five minutes.
What's my experience with pricing, setup cost, and licensing?
Pricing and licensing for SentinelOne Singularity AI SIEM feel reasonable for what I get. The initial setup took some planning, but once up and running, day-to-day management becomes easier.
Which other solutions did I evaluate?
I evaluated a few other SIEM solutions, including Splunk and IBM QRadar, comparing their log management, threat detection, alerting, and integration capabilities.
What other advice do I have?
I give SentinelOne Singularity AI SIEM an eight out of ten.
I chose eight out of ten because it has been reliable, clear, and helpful, but clearer next steps inside alerts and easier integration would push it to ten for me.
My advice would be to understand your security needs and log volume, take time to configure integration, and customize alerts to your environment.
Chirag Thavidaboiyna
Ai-driven investigations have reduced manual log analysis and improve security rule creation
Reviewed on Oct 31, 2026
Review provided by PeerSpot
What is our primary use case?
I use SentinelOne Singularity AI SIEM for security operations. An AI-powered SIEM uses machine learning, and for us, the primary value is reducing manual investigation effort while improving the detection of threats that traditional rule-based SIEMs may miss. SentinelOne Singularity AI SIEM has Purple AI for that purpose. Analysts can use natural language to investigate security data and generate queries. It also has unified security data analytics, which allows us to analyze endpoints, firewalls, identity, cloud, and third-party security logs from a common platform without switching between tools. If a potentially compromised employee account exists, a traditional SIEM may generate separate alerts for each event. However, SentinelOne Singularity AI SIEM can help correlate the events, summarize the investigation, and identify the relationship between them.
A particular example of my use is creating a detection rule. I used SentinelOne Singularity AI SIEM AI and machine capabilities to develop detection logic, generate a query, and ingest logs. Purple AI helped me build the detection logic, but I still validated and deployed the rule. I wanted to create a custom detection rule for external port scanning activity. I analyzed the available FortiGate firewall logs and identified the source IPs originating from external networks. I grouped events by source IP and destination IP, counted the unique destination ports scanned, and used Purple AI by entering a prompt regarding all of this. I reviewed the generated query and confirmed the fields that match with my FortiGate logs. I executed the query and adjusted the threshold, then created the scheduled detection rule using the validated query. I tested it and performed tuning as required.
I also use SentinelOne Singularity AI SIEM for rule and detection development. I developed detections for repetitive failed VPN login attempts. I analyzed gaps with Purple AI and detected data exfiltration using Purple AI.
How has it helped my organization?
SentinelOne Singularity AI SIEM has the potential to improve my organization's security operations by reducing manual investigation efforts, accelerating threat detection, and improving the efficiency of the SOC. Its AI-powered threat hunting and detection engineering capabilities help us develop better detection rules, identify security threats more effectively, and streamline incident response. This has led to improved operational efficiency and better utilization of our security analysts' time.
I have observed time savings in security investigations and detection rule development. AI-assisted techniques reduce the time spent manually writing queries and analyzing security logs. It helps correlate related events and identify relevant evidence faster, allowing our SOC to investigate incidents more efficiently and focus on critical security activities. An example of time savings I have observed is with AI SIEM threat hunting. AI performed investigation using natural language and quickly identified relevant activity, which reduces the time spent on manual log analysis and allows our SOC to focus on validating findings and responding to threats. It also simplifies detection rule development by generating and refining queries.
I have used automated workflows to streamline repetitive security operations tasks. Automating routine activities such as alert enrichment or event handling and response helps reduce manual intervention and improves operational efficiency. This also reduces alert fatigue, allowing our SOC team to focus more on threat investigation and incident response rather than repetitive administrative tasks.
The automated workflows have the potential to reduce false positives by enriching the alerts with contextual information and filtering. This has reduced unnecessary alert handling and improved SOC efficiency. However, the effectiveness depends on the quality of detection rules and workflow configurations. Continuous tuning and validation will remain necessary to ensure genuine intrusions are not overlooked.
I find SentinelOne Singularity AI SIEM efficient in supporting our SOC operations. Its AI-powered threat hunting and investigation capabilities help reduce the effort of manually analyzing security logs and correlating events. The platform also assists in developing and refining detection queries, improving the efficiency of threat investigations. However, the accuracy of the generated queries and the need for manual validation can affect the overall efficiency, particularly when working with complex or third-party log sources.
I assess SentinelOne Singularity AI SIEM efficiency by measuring how much time it saves in daily SOC operations, how accurately it identifies threats, and how much manual work remains. I also assess the efficiency of SentinelOne Singularity AI SIEM based on security activities done manually for threat hunting, detection, and incidents. For example, investigating external port scanning activity traditionally requires manually filtering firewall logs, correlating events, and calculating investigation reports. Assisted investigation helps simplify this process by identifying relevant events and assisting with query development. This improves detection efficiency, although the generated queries still require analysts' modification.
If a Windows endpoint starts communicating with a suspicious external IP, SentinelOne Singularity AI SIEM can correlate firewall logs with endpoint telemetry to help identify the affected system. If the activity is confirmed as malicious, the SOC can isolate the endpoint. SentinelOne Singularity AI SIEM does not directly prevent system downtime. It is entirely dependent on detection quality, response speed, and whether required mitigation and response actions were taken. SentinelOne Singularity AI SIEM can help reduce the potential impact of security events on system availability by improving threat detection and investigation speed.
I believe my organization's security posture has improved with the implementation of SentinelOne Singularity AI SIEM. The platform provides better visibility into security events across multiple data sources and helps identify suspicious activities more efficiently. Its AI-powered threat hunting, event correlation, and investigation capabilities support faster threat identification and improve our ability to detect potential attacks. It also assists in developing and refining detection rules, helping us address detection gaps and strengthen our monitoring capabilities. Overall, the platform has improved our security visibility and investigation efficiency, while continuous detection tuning and analysis remain essential to maintaining an effective security posture.
Consolidating security data from multiple sources into SentinelOne Singularity AI SIEM has helped streamline our SOC operation by providing a centralized view of security events. Instead of switching between different tools to investigate suspicious activities, analysts can correlate and analyze data from multiple sources within a single platform. This improves investigation efficiency, reduces manual effort, and simplifies threat hunting. It helps our team identify relationships between events that might otherwise remain unnoticed.
What is most valuable?
The best features of SentinelOne Singularity AI SIEM are the AI-powered threat hunting and investigation, natural language search, and the ability to query data so I can search with my own language with Purple AI. Custom detection rules and correlation of security events across multiple data sources, real-time threat detection and alerting, integration with SentinelOne EDR and XDR and third-party security products, data normalization and log parsing, historical log analysis for identifying attack patterns, and automated response and orchestration workflows are all valuable.
AI-powered threat hunting using natural language stands out the most to me. It allows me to investigate security data using plain language questions instead of manually writing complex queries. This reduces the time required for threat hunting and makes investigations more accessible for analysts who are less familiar with query languages. I was not that much familiar with the SentinelOne query language before. During the first six months, I was not familiar with the query language, but now I am an expert. However, analysts who are less familiar with query languages can use Purple AI to query SentinelOne data using plain English.
Another standout feature worth mentioning is AI-assisted detection engineering. Unlike simply using AI to summarize events, this focuses on helping me develop, investigate, and refine detection logic. It can make detection engineering more accessible and reduce the manual effort involved in writing and troubleshooting queries. Other features that may stand out are assisted investigation, explainable AI verdicts, and OCSF normalized data. Assisted investigation is a strong feature to mention alongside the features I have mentioned.
What needs improvement?
SentinelOne Singularity AI SIEM can improve in several areas. AI accuracy is one area where the platform can improve the accuracy of AI-generated queries and investigation findings, especially for complex log formats. Detection rule creation should be easier, making it simpler to convert AI-generated queries into production-ready detection rules. False positive reduction is another important area where improved detection tuning is needed to reduce unnecessary alerts and manual triage. For example, SentinelOne Singularity AI SIEM can catch SentinelAgent.exe as a potential threat, but it should not because it is the agent of SentinelOne itself. Third-party integrations should be improved because the platform does not integrate with some Microsoft-related products currently. Expanding out-of-the-box integrations and simplifying the onboarding of non-SentinelOne data sources would be beneficial.
Log parsing should be improved by enhancing automatic extraction and normalization for custom and third-party logs. Investigation transparency should provide clearer explanations of why an event was classified as suspicious or malicious because the AI is constantly classifying SentinelOne agent as suspicious. The platform should support more formats and optimize costs by improving query execution and optimizing data and storage costs.
The accuracy of SentinelOne Singularity AI SIEM is generally useful for threat hunting and security investigations. However, AI-generated queries may require manual validation, particularly when dealing with complex log formats or custom data sources. Sometimes, query results may need refinement to avoid false positives or may miss some relevant events. Improving query accuracy, field mapping, and consistency across third-party observability would make the platform more reliable and reduce the need for manual troubleshooting.
For how long have I used the solution?
I have been using SentinelOne Singularity AI SIEM for approximately two and a half years.
What do I think about the stability of the solution?
I find SentinelOne Singularity AI SIEM is generally stable for security monitoring and investigation. It is cloud-based and provides consistent access to security data across multiple sources. It can be affected by log ingestion delays, query performance issues, and issues with third-party data. For example, daily investigations involving large volumes of firewall logs depend on query performance and availability factors. Overall, the platform provides a reliable foundation for SOC operations. Continuous monitoring of data ingestion and integrations is essential to maintain consistent performance.
What do I think about the scalability of the solution?
I find SentinelOne Singularity AI SIEM scalable in terms of adapting to my organization's evolving security events. Its cloud-based architecture allows us to expand security monitoring as the volume of endpoints, logs, and data sources increases without requiring significant changes to our underlying infrastructure. The platform's ability to integrate data from different security products also supports the onboarding of new log sources as the environment grows. For example, we can extend monitoring to additional firewalls, cloud, and on-premises environments while maintaining centralized visibility. Its AI-powered threat hunting and investigation capabilities further support scalability by helping analysts manage increasing volumes of security data more efficiently.
I find SentinelOne Singularity AI SIEM scalable and capable of supporting growing security monitoring requirements. The cloud-based architecture allows us to expand and integrate additional security data sources without changing underlying infrastructure. From stability to security data, it supports assisted threat hunting with increasing volumes more efficiently. For example, integrating firewall logs can be extended while maintaining centralized visibility. The platform has met our needs, but data migration capacity, integration complexity, and licensing costs must be considered.
How are customer service and support?
My experience with SentinelOne customer support has been positive. The support team provides assistance with technical issues and product queries. Response times and resolution timelines can vary depending on the complexity. For example, issues involving log ingestion or third-party integrations may require additional investigation and coordination. Overall, customer support is helpful, but faster resolution of complex technical issues and more communication would be better.
Which solution did I use previously and why did I switch?
I used Wazuh, which provided flexibility for log collections and a custom rule-based detection model. However, managing integrations, writing detection rules, and management required considerable manual effort. SentinelOne Singularity AI SIEM offers a more streamlined approach to AI-assisted threat hunting, natural language query assistance, and centralized data analysis. These capabilities can reduce the effort required for detection engineering and investigations. The main advantage is improved operational efficiency and simplified security analysis rather than the complete elimination of some technical tools or manual investigation.
What was our ROI?
I have experienced operational benefits from SentinelOne Singularity AI SIEM, which has reduced the time required for security investigations and detection rule creation. For example, investigating suspicious firewall activity traditionally involves manually filtering logs, but assisted investigations help simplify this to identify relevant events more quickly and spend less time on such tasks. Consolidating security data also reduces the need to switch between multiple tools during investigations. These improvements contribute to better utilization of SOC resources and potential cost savings through reduced manual effort. These are the direct forms and data of interest for return on investment, and the actual savings depend on investigation volume, analyst efficiency, and efficiency costs. I get every endpoint at a reduced cost, below the market value. The ROI may be better than I expected.
What's my experience with pricing, setup cost, and licensing?
My experience in pricing and licensing has been primarily from an operational perspective. The platform's cloud-based data model simplifies infrastructure management and reduces the need for maintaining security system hardware. Pricing transparency and license flexibility are important considerations as the volume of security data and number of environments increase. Having clear visibility into data ingestion costs, licensing, and the impact of expanding integrations would help my organization plan its operations more efficiently.
Which other solutions did I evaluate?
I did not evaluate any other option because my company was already a partner of SentinelOne, and then we approached SentinelOne for AI SIEM, specifically SentinelOne Singularity AI SIEM. There were not any other options for me. Additionally, we trusted SentinelOne so much that we switched to AI SIEM without any hesitation.
What other advice do I have?
I would rate SentinelOne Singularity AI SIEM an eight out of ten because it stands out in AI-powered threat hunting. The natural language query assistance is valuable for newer SOC analysts. Automated investigation, event correlation, and detection rule development are excellent. I have deducted two points because it could improve more on accurate AI-generated queries and easier conversion of queries into production rules, better third-party log parsing, and reduced false positives.
I find SentinelOne's governance and security approach valuable, particularly in its centralized security data management and AI system investigation capabilities. The platform provides visibility across multiple security data sources while allowing analysts to remain involved in investigation and response decisions. I would also like to see more granular controls over AI's interactions, clearer audit trails, and improved visibility into how AI reaches its conclusions. These enhancements would further strengthen trust, accountability, and governance with SentinelOne Singularity AI SIEM.
SentinelOne Singularity AI SIEM is deployed as a cloud-based SaaS solution in a public cloud. It allows us access to security monitoring, threat hunting, and investigation without maintaining the underlying SIEM infrastructure on premises. This simplifies deployment, infrastructure management, and provides scalability as security monitoring requirements grow.
I would recommend SentinelOne Singularity AI SIEM to those looking to improve their security monitoring. Its AI features can simplify complex queries, reduce manual investigation efforts, and provide better visibility across multiple security data sources. Organizations should evaluate their requirements, integration capabilities, and licensing costs before adoption. I would also recommend rule tuning and automation tuning. Overall, it is a valuable solution for SOC teams to improve their operational efficiency and strengthen their security posture.
Likhith Varma
AI-driven investigations have improved real-time monitoring and simplified alert analysis
Reviewed on Sep 07, 2026
Review provided by PeerSpot
What is our primary use case?
SentinelOne Singularity AI SIEM is a tool that we use to support our clients. Our organization is a service-based organization, so we use SIEM to provide services to software-based clients. We are a partner with SentinelOne.
What is most valuable?
The best features of SentinelOne Singularity AI SIEM include its ability to give you a brief description of what the alert is about. When an alert is triggered with AI SIEM, we have a basic analysis of what the alert is about, and it will give you the understanding of what the alert is.
I especially value that analysis feature. If you get an alert in SentinelOne Singularity AI SIEM, we have an auto-investigate tab as well. If you click on that auto-investigate tab, it will correlate with all the products and data sources it has, and it will give you a deep analysis of what the alert is and what is happening, so everything is covered.
The real-time monitoring is pretty good. It correlates between all the different data sources that have been integrated with SentinelOne Singularity AI SIEM. It will correlate everything and give you a pretty good storyline of what the alert is about.
Overall, this affects my security posture positively because it improves it since it helps us in real-time monitoring, and it gives us automated investigation and also the auto-investigate tab, so it is pretty good.
What needs improvement?
My impression of the AI-driven threat detection capabilities is that it helps a little bit, but they need to tune it a bit because we are seeing too many false positives recently. Since we are a partner with SentinelOne, we are working along with them to tune those out.
I assess the efficiency of SentinelOne Singularity AI SIEM in improving our responses to sophisticated threats as not having improved a lot because, as I mentioned earlier, there are a few things that need improvement, including the false positive rate. Since we are seeing too many false positives, even if a true positive comes, it is harder for us to determine the difference between the false positive and true positive.
The effect on our SOC ability in reducing false positives has not been significant. We have opted for the possibility of doing some automation. Because of that automation, if SentinelOne Singularity AI SIEM already does the basic analysis, it will close out a few of the false positives, but not that much. I would say around ten to twenty percent of the alert volume is reduced.
The areas that need improvement with SentinelOne Singularity AI SIEM include faster responses. The tool is a bit slow since it is under development, so it is not that fast. They also need to improve on developing more use cases that will help determine the true positives.
I have not worked with any SIEM that is integrated with AI, but if I compare SentinelOne Singularity AI SIEM with Microsoft Sentinel, Sentinel has some use cases that are kind of true positives and all. Here, they need to improve on the tool functionality and faster responses.
For how long have I used the solution?
I have been using SentinelOne Singularity AI SIEM for the past one and a half years.
What do I think about the stability of the solution?
I rate the stability of SentinelOne Singularity AI SIEM as pretty stable unless there is an upgrade. But if you run too many queries, it will be down.
What do I think about the scalability of the solution?
The scalability of SentinelOne Singularity AI SIEM is pretty good; I would rate it around a nine.
How are customer service and support?
I would rate the technical support around five.
I rate it five because even if you raise a case with SentinelOne support, you will not get that fast of a response. Even if you raise a P1 or P2, you have to engage back-end support in order to get a response from them. That has been a major drawback in the tool. Also, even if you get a response, it will be a generic response.
What was our ROI?
The alert volume has been reduced by around ten to twenty percent.
What's my experience with pricing, setup cost, and licensing?
The pricing for SentinelOne Singularity AI SIEM is cheap when compared with other tools. I do not know the exact prices, but I heard it is cheap when compared with the other tools in the market.
What other advice do I have?
In my organization, approximately eighty people work with SentinelOne Singularity AI SIEM.
Our clients vary in size; we have small businesses, medium enterprises, and large enterprises as well.
SentinelOne Singularity AI SIEM does require maintenance in that we manage the integration and everything, but the tool UI and everything is updated by the SentinelOne team itself. We do not upgrade anything.
Doing updates for SentinelOne Singularity AI SIEM is easy.
I evaluate the efficiency in investigating alerts and responding to various incidents as pretty good; they have a pretty good collection of events. You will have all the events that you need to do an investigation, and I would say it is pretty good. Once you start working with the tool, you will have pretty good responses in the event search to investigate.
We are using the automated workflow feature in order to reduce the number of false positives. With that, benign threats and all will be there, so we are just closing them out. It is reducing the volume of alerts for now.
The advice I would give others looking to implement SentinelOne Singularity AI SIEM is that it has its pros and cons. If you are looking for a decent tool for investigation, it is good. But if you are a large enterprise and if you have loads of logs that are being ingested, I would say just think about it because we are having issues while handling large clients and pulling a larger number of logs. I would rate this product an eight out of ten.
reviewer2835498
AI-driven security workflows have transformed investigations and now reduce incident response times
Reviewed on Jul 23, 2026
Review from a verified AWS customer
What is our primary use case?
SentinelOne Singularity AI SIEM's main use case is to enhance cybersecurity by using AI to detect, investigate, and automatically respond across endpoints, cloud, and identities. It helps security teams reduce manual efforts, accelerate incident response, and improve overall security operations.
In my previous role, I used SentinelOne Singularity AI SIEM to investigate endpoint security alerts. Instead of manually using logs from multiple systems, I used the AI-powered investigation features to quickly identify the root cause of suspicious activities. SentinelOne Singularity AI SIEM automatically correlated related events and highlighted the affected endpoints while recommending response actions. We isolated the endpoints with a single click after verifying it was a malicious script, and we remediated the issue much faster than the previous manual process.
What is most valuable?
The best features of SentinelOne Singularity AI SIEM are AI-powered threat detections, unified security data, Purple AI assistant, automated investigations, hyper-automations, and fast threat hunting. These features include centralized log management, Purple AI for natural log investigations, automated alert correlations, and hyper-automations for incident response. These features help security teams detect threats faster, reduce manual effort, minimize false positives, and significantly improve mean time to detect and mean time to respond.
These features significantly improved our SOC workflow. Previously, analysts had to manually collect logs from multiple tools and correlate alerts, which was time-consuming. With SentinelOne Singularity AI SIEM, alerts were automatically correlated into a single incident with an attack timeline, making investigations much faster. Purple AI helped summarize the incident and answer natural language queries, reducing the time spent searching through logs.
SentinelOne Singularity AI SIEM has improved our overall security posture and is reducing the workload on the SOC team. Its AI-driven detection and automated response capabilities help us identify threats faster, reduce false positives, and shorten incident response times. The centralized visibility across endpoints and cloud environments also made investigations more efficient, while automation reduced repetitive manual tasks.
It has improved SOC efficiency by reducing time analysts spend on manual alert investigations and response. Previously, analysts had to collect information from multiple sources and manually correlate events. With SentinelOne Singularity AI SIEM's AI-driven alert prioritization, automated incident correlations, and investigation timelines provide better context quickly. The team can identify the root cause faster, reduce alert fatigue, and take response actions such as isolating affected endpoints more efficiently.
What needs improvement?
SentinelOne Singularity AI SIEM is a strong platform, but there are a few areas where it could be improved. First, the initial setup and integration with some third-party tools could be simpler. Second, more customizable dashboards and reporting would help the management team confirm their needs.
For how long have I used the solution?
I have been using SentinelOne Singularity AI SIEM for the last three years.
What other advice do I have?
My impression of SentinelOne Singularity AI SIEM's AI-driven threat detection capability is very positive. It uses behavioral analysis and machine learning to identify suspicious activity that may not be detected by traditional signature-based methods.
I used SentinelOne Singularity AI SIEM's automated workflow capability to reduce repetitive security tasks. For example, when a high-risk alert was detected, automated workflows helped with actions such as endpoint isolation, alert enrichment, and triggering response processes without requiring manual intervention at every step. This reduced the time analysts spent on routine tasks and has improved consistency in incident handling.
My advice would be to clearly define your security goals and use cases before deploying SentinelOne Singularity AI SIEM. Start with proper endpoint coverage, integrate with your existing security tools, and spend time tuning policies to reduce unnecessary alerts. I would also recommend training the SOC team on the AI investigations and automation features so they can fully benefit from the platform. Finally, continuously review detection results and response processes to ensure the platform is meeting the organization's security needs. I would rate this solution an eight out of ten.
Which deployment model are you using for this solution?
Public Cloud
If public cloud, private cloud, or hybrid cloud, which cloud provider do you use?
Amazon Web Services (AWS)
Dev Reshwal
Automation has reduced workload and real-time monitoring provides faster incident response
Reviewed on Jul 20, 2026
Review from a verified AWS customer
What is our primary use case?
In my daily work, the main use case for SentinelOne Singularity AI SIEM is creating rules, fine-tuning, source recording, rule creations, and when any alerts are triggered. We can raise them to the client side, continuously monitoring any alerts. We can raise them to the client side for early resolution, also creating the dashboards, checking the logs, and agents installation. Those are the day-to-day tasks in our SIEM tool.
Alert fighting is a specific example of a recent situation where I used SentinelOne Singularity AI SIEM for one of these tasks. Sometimes multiple alerts are triggered in the SIEM. At that time, we analyze what type of alert it is, whether it is a true positive or false positive. That is challenging for me.
Our day-to-day tasks include alert raising, continuous monitoring, raising the alerts, dashboard managing, creating the dashboard, rule creating, and decoder creating. If there is any requirement from the client side, we will also do these types of activities, creating any new rule.
When I have those multiple alerts and I need to figure out if they are true positives or false positives, I usually check in Deep Visibility if it belongs to any suspicious fields or anything malicious, or if it is a true positive belonging to our organization. I also check if it belongs to any suspicious sites, IPs, or IOCs such as malicious IPs or malicious hashes, or if it belongs to any malicious paths. I will check the source, the destination, and what it is doing. We can check if the path belongs to a genuine path or a suspicious path. We will do that type of analysis and then I will specify if it belongs to a true positive or a false positive. We can follow those types of steps.
What is most valuable?
SentinelOne Singularity AI SIEM offers the best features that belong to the AI. This includes automated alerts. We can also do the automated alerts on these fields. I can create multiple types of use cases. It means we will create multiple types of use cases for our requirements. For example, if we have blocked any suspicious or malicious app in the environment, we can block these. That is a best feature, and Purple AI is also a best feature in SentinelOne Singularity AI SIEM tools. Deep Visibility is also a best feature because we can check multiple types of activity, such as what it is doing, what activities it is currently performing, and what the steps are. There are multiple types of best features in there.
I will give an example of how Deep Visibility has helped me in my investigations or daily work. If any suspicious or malicious malware types of alerts are triggered in SentinelOne Singularity AI SIEM, then I will check the source of this with the help of Deep Visibility. Deep Visibility is basically for when any alerts are triggered on any endpoint. You can see what types of activity are being done, what is being downloaded, and what types of history there are. You can check the source, the destination, and what systems are doing this activity. I will check that type of feature in Deep Visibility.
SentinelOne Singularity AI SIEM has impacted my organization positively because I am observing some improvement. There are multiple tool alerts in our organization, but SentinelOne Singularity AI SIEM feature is real-time monitoring and real-time threat detection. With the help of our and the client's organization, it is secure. There are improvements. Those types of improvements are better for securing our organization from anything suspicious or any malicious types of alerts.
There are faster response times available with SentinelOne Singularity AI SIEM. Also, there is the automation alert. We can set any parameter on SentinelOne Singularity AI SIEM source, and it will automatically raise an alert to the client side. We can also integrate that type of feature with SentinelOne Singularity AI SIEM. With the help of alert raising, there is the fastest way to raise an alert. That is the best feature and there is a very big improvement.
What needs improvement?
SentinelOne Singularity AI SIEM is the best, but sometimes the dashboards are a little simple compared to other tools. The custom dashboard is not available in their features. Therefore, I would suggest adding the custom dashboard for any of our requirements.
The AI-driven analytics from SentinelOne Singularity AI SIEM has not affected our ability to reduce false positives.
SentinelOne Singularity AI SIEM has affected my SOC's efficiency in investigating alerts and responding to incidents. If we receive any alerts, we can observe what activity is being done. We can see if it is malicious or something suspicious, or a true positive. We can analyze the path, the hash, and whether the signature is verified or not. We can see if it is an alert triggered by any engine. We can see the source of this. We will do that type of analysis and raise it to the client side. Also, if I identify anything suspicious or malicious in the alert, I will forcefully kill and quarantine it immediately.
For how long have I used the solution?
I have been working in my current field for the last two years and five months.
What do I think about the stability of the solution?
SentinelOne Singularity AI SIEM is stable.
What do I think about the scalability of the solution?
The pricing for SentinelOne Singularity AI SIEM is best, and it has very easy features for understanding. There are multiple tools with various types of features, but SentinelOne Singularity AI SIEM provides some features, maybe fewer features, but they are very useful features. We can say that to the client. Also, the integration parts are easy. It is cloud-based, and there are multiple automation activities also being done. It is an easy way to work, and minimum workers are needed. SentinelOne Singularity AI SIEM is doing multiple types of activities because there are automated tools with AI features. There are also Deep Visibility and multiple Purple AI types. It has multiple best features. We can suggest those types of things to the client for purchasing SentinelOne Singularity AI SIEM.
I will give SentinelOne Singularity AI SIEM a ten out of ten on scalability.
I rate SentinelOne Singularity AI SIEM a ten out of ten because there are the best features in there. There are multiple types of features such as auto-raising, automation, AI features, and the Deep Visibility feature. There is an improvement in our organization to be faster to secure our organization's safety. That is why I will give it a ten out of ten. The integration part is also best. It is a ten out of ten from my side. That is why I give it a ten out of ten.
How are customer service and support?
The customer support for SentinelOne Singularity AI SIEM is also the best because we have raised tickets to the support center multiple times. The support team gives an immediate answer, within ten to fifteen minutes. They also schedule calls and troubleshoot the alerts and solve the issue. The support team is very best.
I rate the customer support for SentinelOne Singularity AI SIEM a ten out of ten.
Which solution did I use previously and why did I switch?
In our organization, we previously used the CrowdStrike solution.
We switched from CrowdStrike to SentinelOne Singularity AI SIEM because our organization is an MSSP organization. That means I provide services to the client. We had twenty to thirty clients in our organization that we managed. Twenty-seven or twenty-eight clients were using SentinelOne Singularity AI SIEM, but only one or two clients were on CrowdStrike. Their client also switched to SentinelOne Singularity AI SIEM. That is why, at this time, we are only managing SentinelOne Singularity AI SIEM.
How was the initial setup?
The integration part for SentinelOne Singularity AI SIEM is very easy. Any fresher can easily do this. The agent installation is also so easy. Within one to two minutes, we can install SentinelOne Singularity AI SIEM agents in the environment or client environment network. It is the best, fastest installation.
What was our ROI?
I have seen a return on investment with SentinelOne Singularity AI SIEM. The tool also saves our money and time. The pricing is very medium, and time is also saved because there are automation features available. That is why multiple alerts are raised by the automated process. In those times, manual alerts are less frequent compared to other tools. It is helpful. Sometimes, in our organization, two people are working on these AI-driven features in SentinelOne Singularity AI SIEM. But when the automation features are started, one person can also manage the console. It is money saved, and the automation and those types of activities are doing the automated alerts. One person is only managing and checking if the alerts are going properly. That is why it is also money-saving. It is a money-saving tool, and the pricing is also low. Any small or startup organization can also buy it easily.
What's my experience with pricing, setup cost, and licensing?
My experience with pricing, setup cost, and licensing for SentinelOne Singularity AI SIEM is that the setups are very easy for any fresher. Any basic knowledge can also do the setups. Regarding the pricing, it is not heavy. It is in the middle, not high, not low. Any small organization can also purchase this. Compared to another SIEM tool's pricing, the pricing is the best, from my side.
Which other solutions did I evaluate?
Before choosing SentinelOne Singularity AI SIEM, I did not evaluate other options because SentinelOne Singularity AI SIEM is the best according to me. We have used other tools, but SentinelOne Singularity AI SIEM has multiple types of features and it is an easy-to-understand tool. That is why I am choosing SentinelOne Singularity AI SIEM.
What other advice do I have?
The accuracy and reliability of output from SentinelOne Singularity AI SIEM are very high. SentinelOne Singularity AI SIEM is very accurate. It is also very reliable. We have not found any glitching. It is faster, and it also has real-time threat hunting and real-time detection. That is the capability in there.
The real-time monitoring feature of SentinelOne Singularity AI SIEM helps with Deep Visibility. If any malicious or suspicious alerts are triggered, I will check the alert. We can analyze this alert with the help of Deep Visibility. We can see its source, its destination, what it is trying to do, and if the path is genuine or not. We receive the alerts and we can do this type of investigation. Then, if anything malicious happens, we can raise it to the client side for notification purposes. We can say we observed this type of alert at this time, and it is this type of malicious activity.
My impression of the AI-driven threat detection capabilities of SentinelOne Singularity AI SIEM is that it is the best feature because multiple alerts can be happening, but the AI-driven features immediately block them. Any alerts are blocked before they happen. And it gives the action, such as killing and quarantining the threat.
I give SentinelOne Singularity AI SIEM an overall rating of ten out of ten.
Which deployment model are you using for this solution?
Public Cloud
If public cloud, private cloud, or hybrid cloud, which cloud provider do you use?
Amazon Web Services (AWS)