
Sold by: H2H Technology
Deployed on AWS
Tutela Agentic Security gives security teams runtime visibility and policy control over AI prompts, files, outputs, and tool calls to prevent sensitive data leakage and destructive actions across browsers, embedded AI, SDKs/APIs and MCP Gateways.
Overview
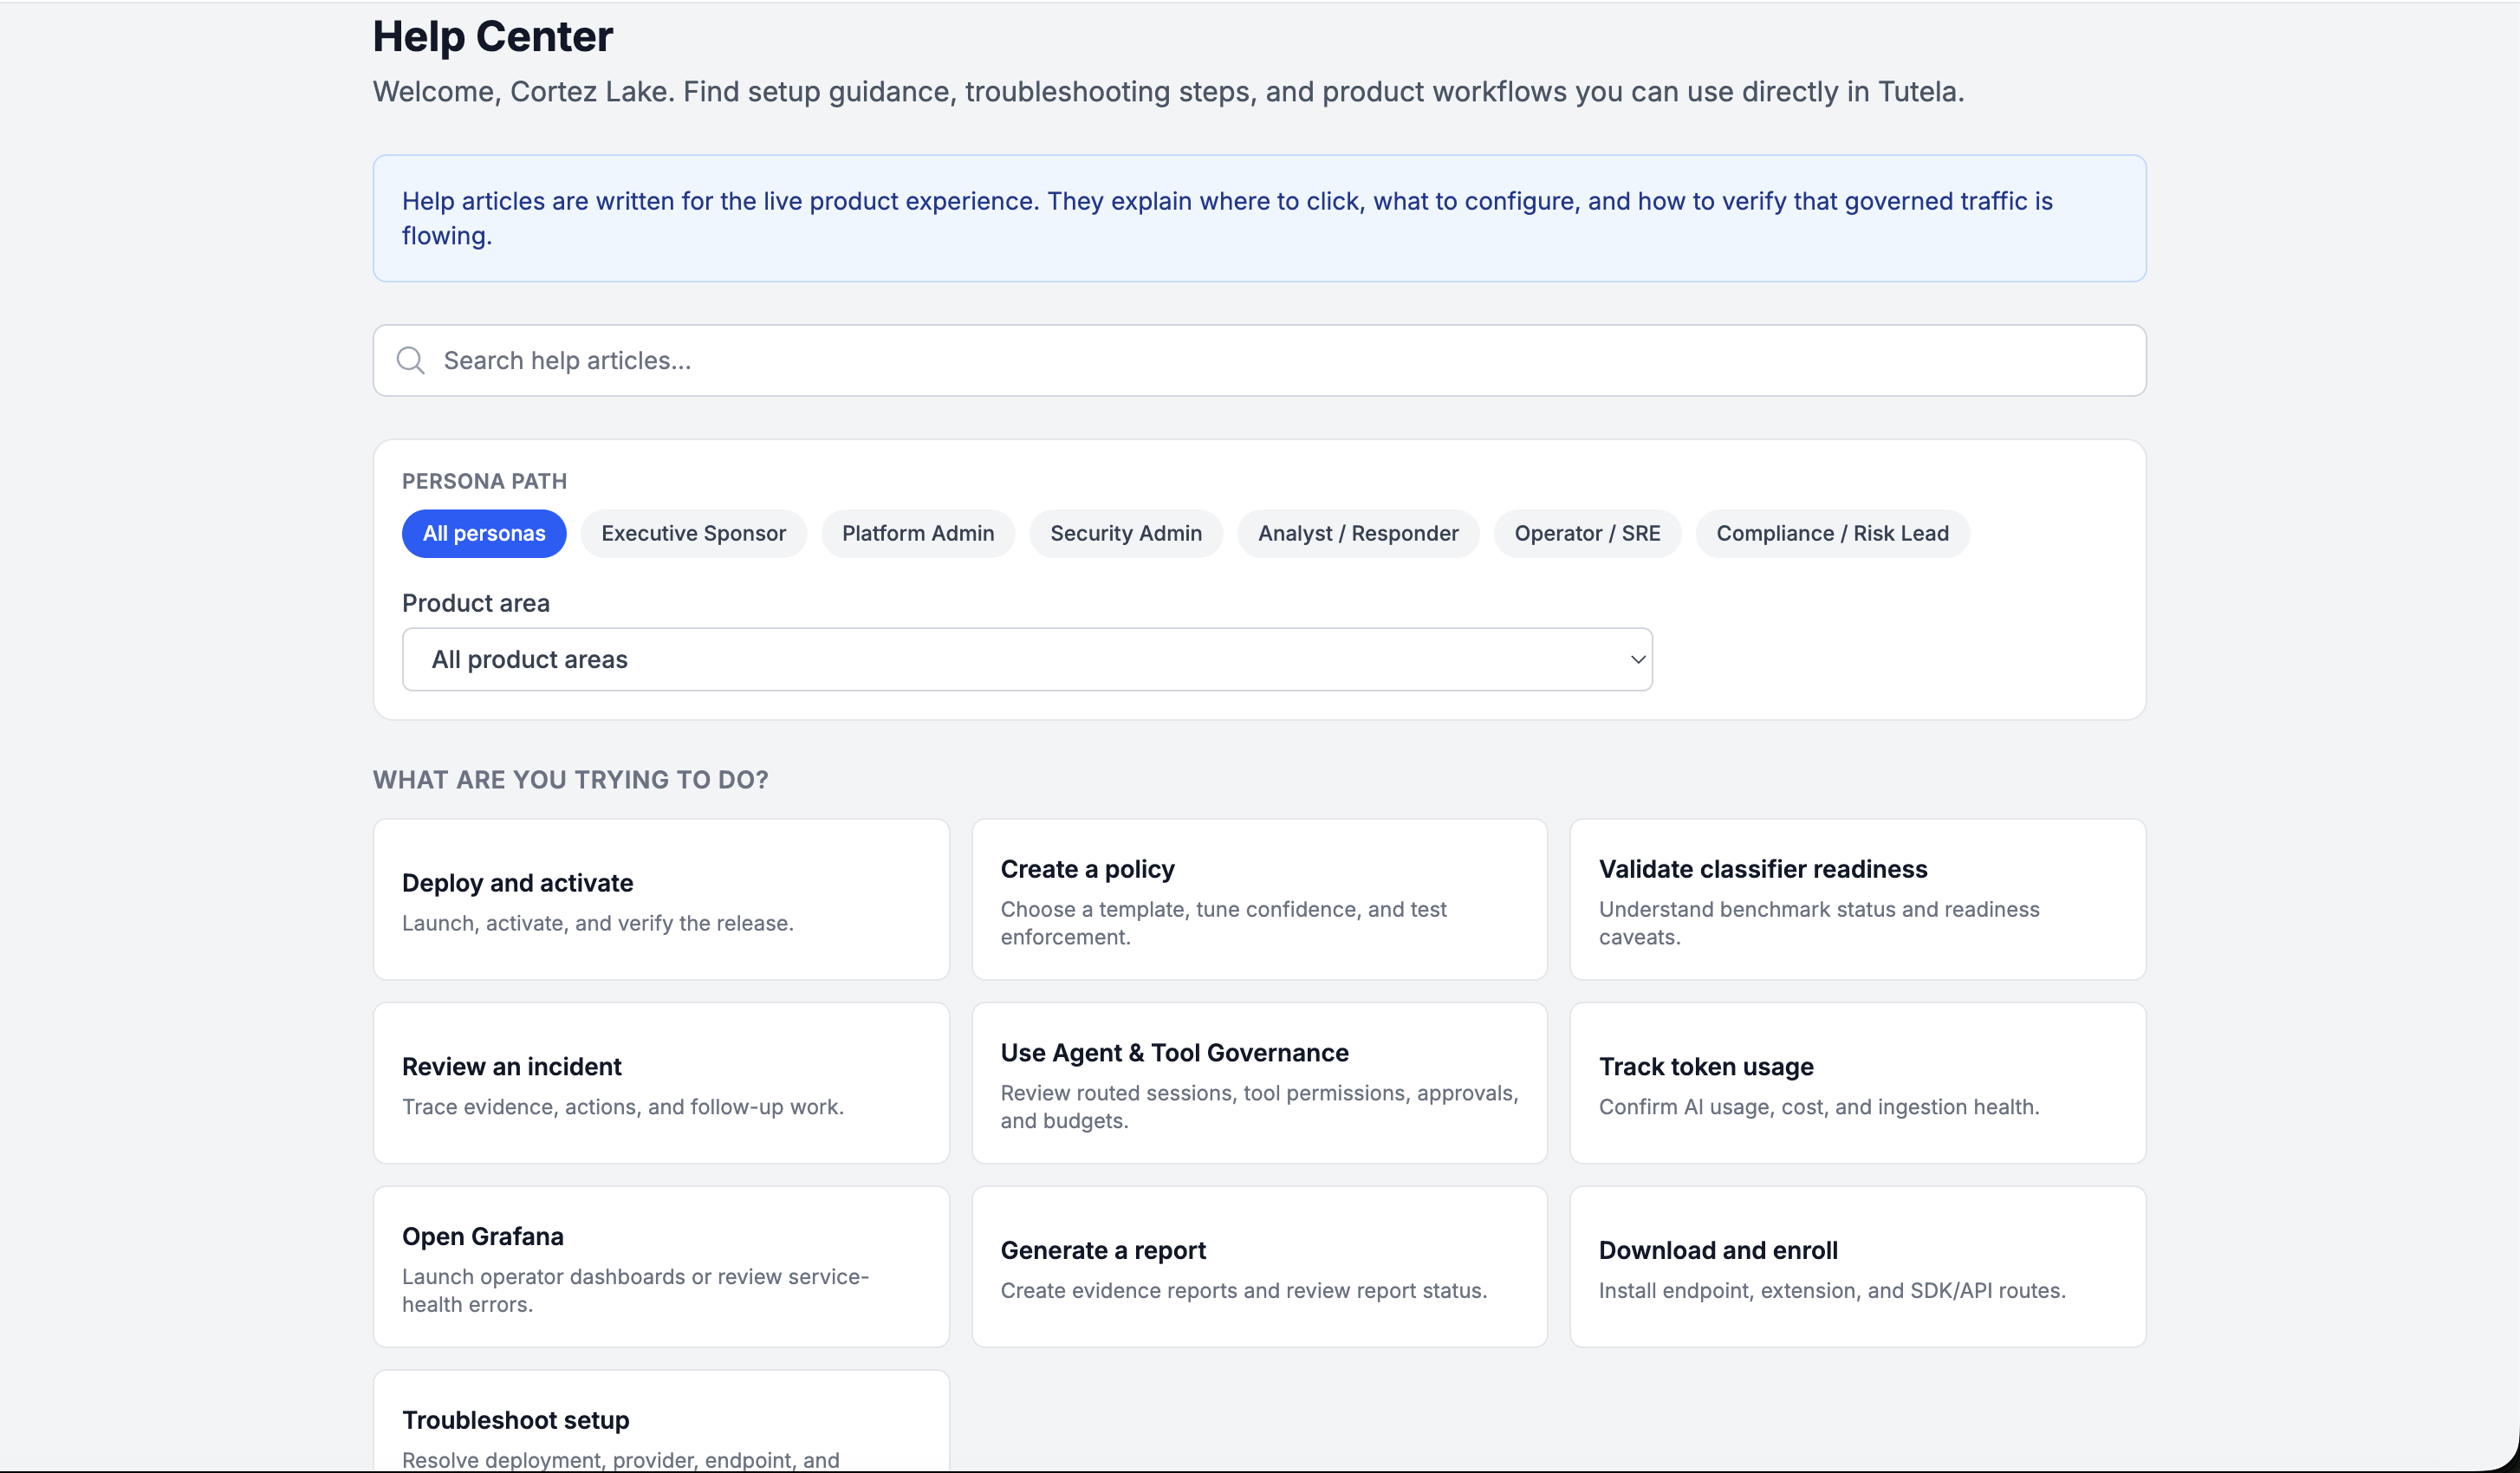
Image
Tutela Agentic Security - Help Center
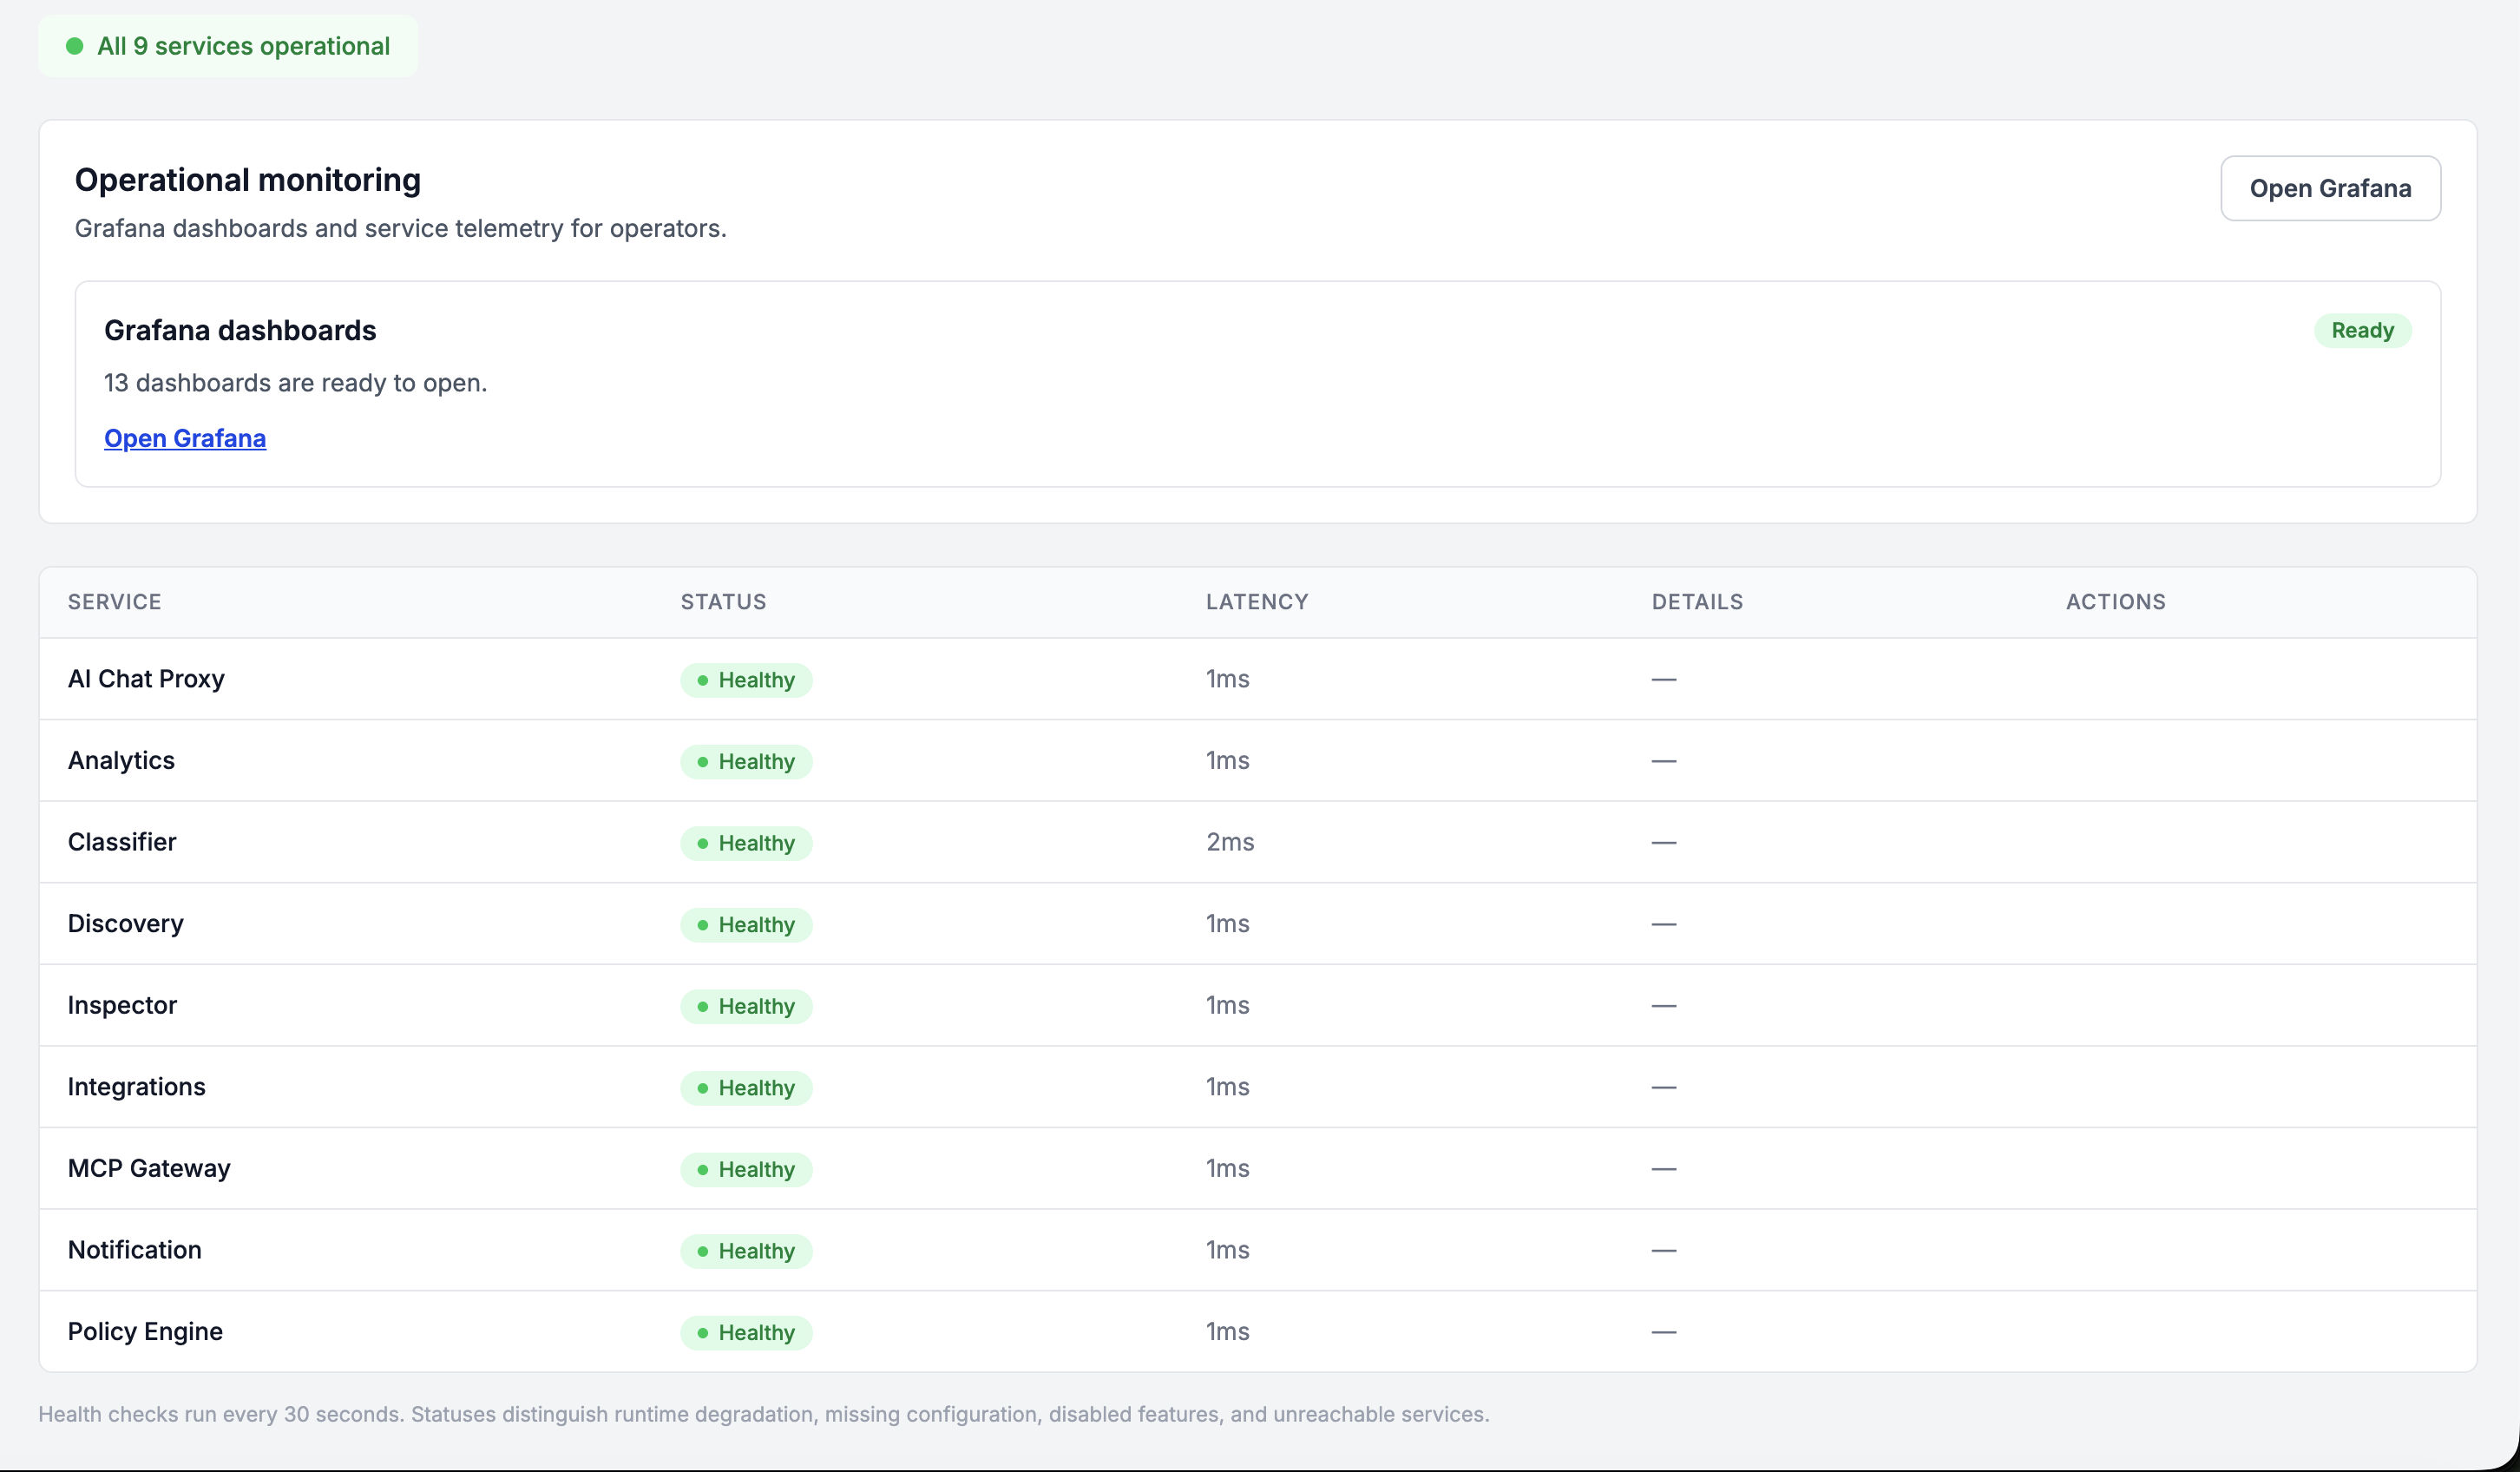
Image
Tutela Agentic Security - Service Health
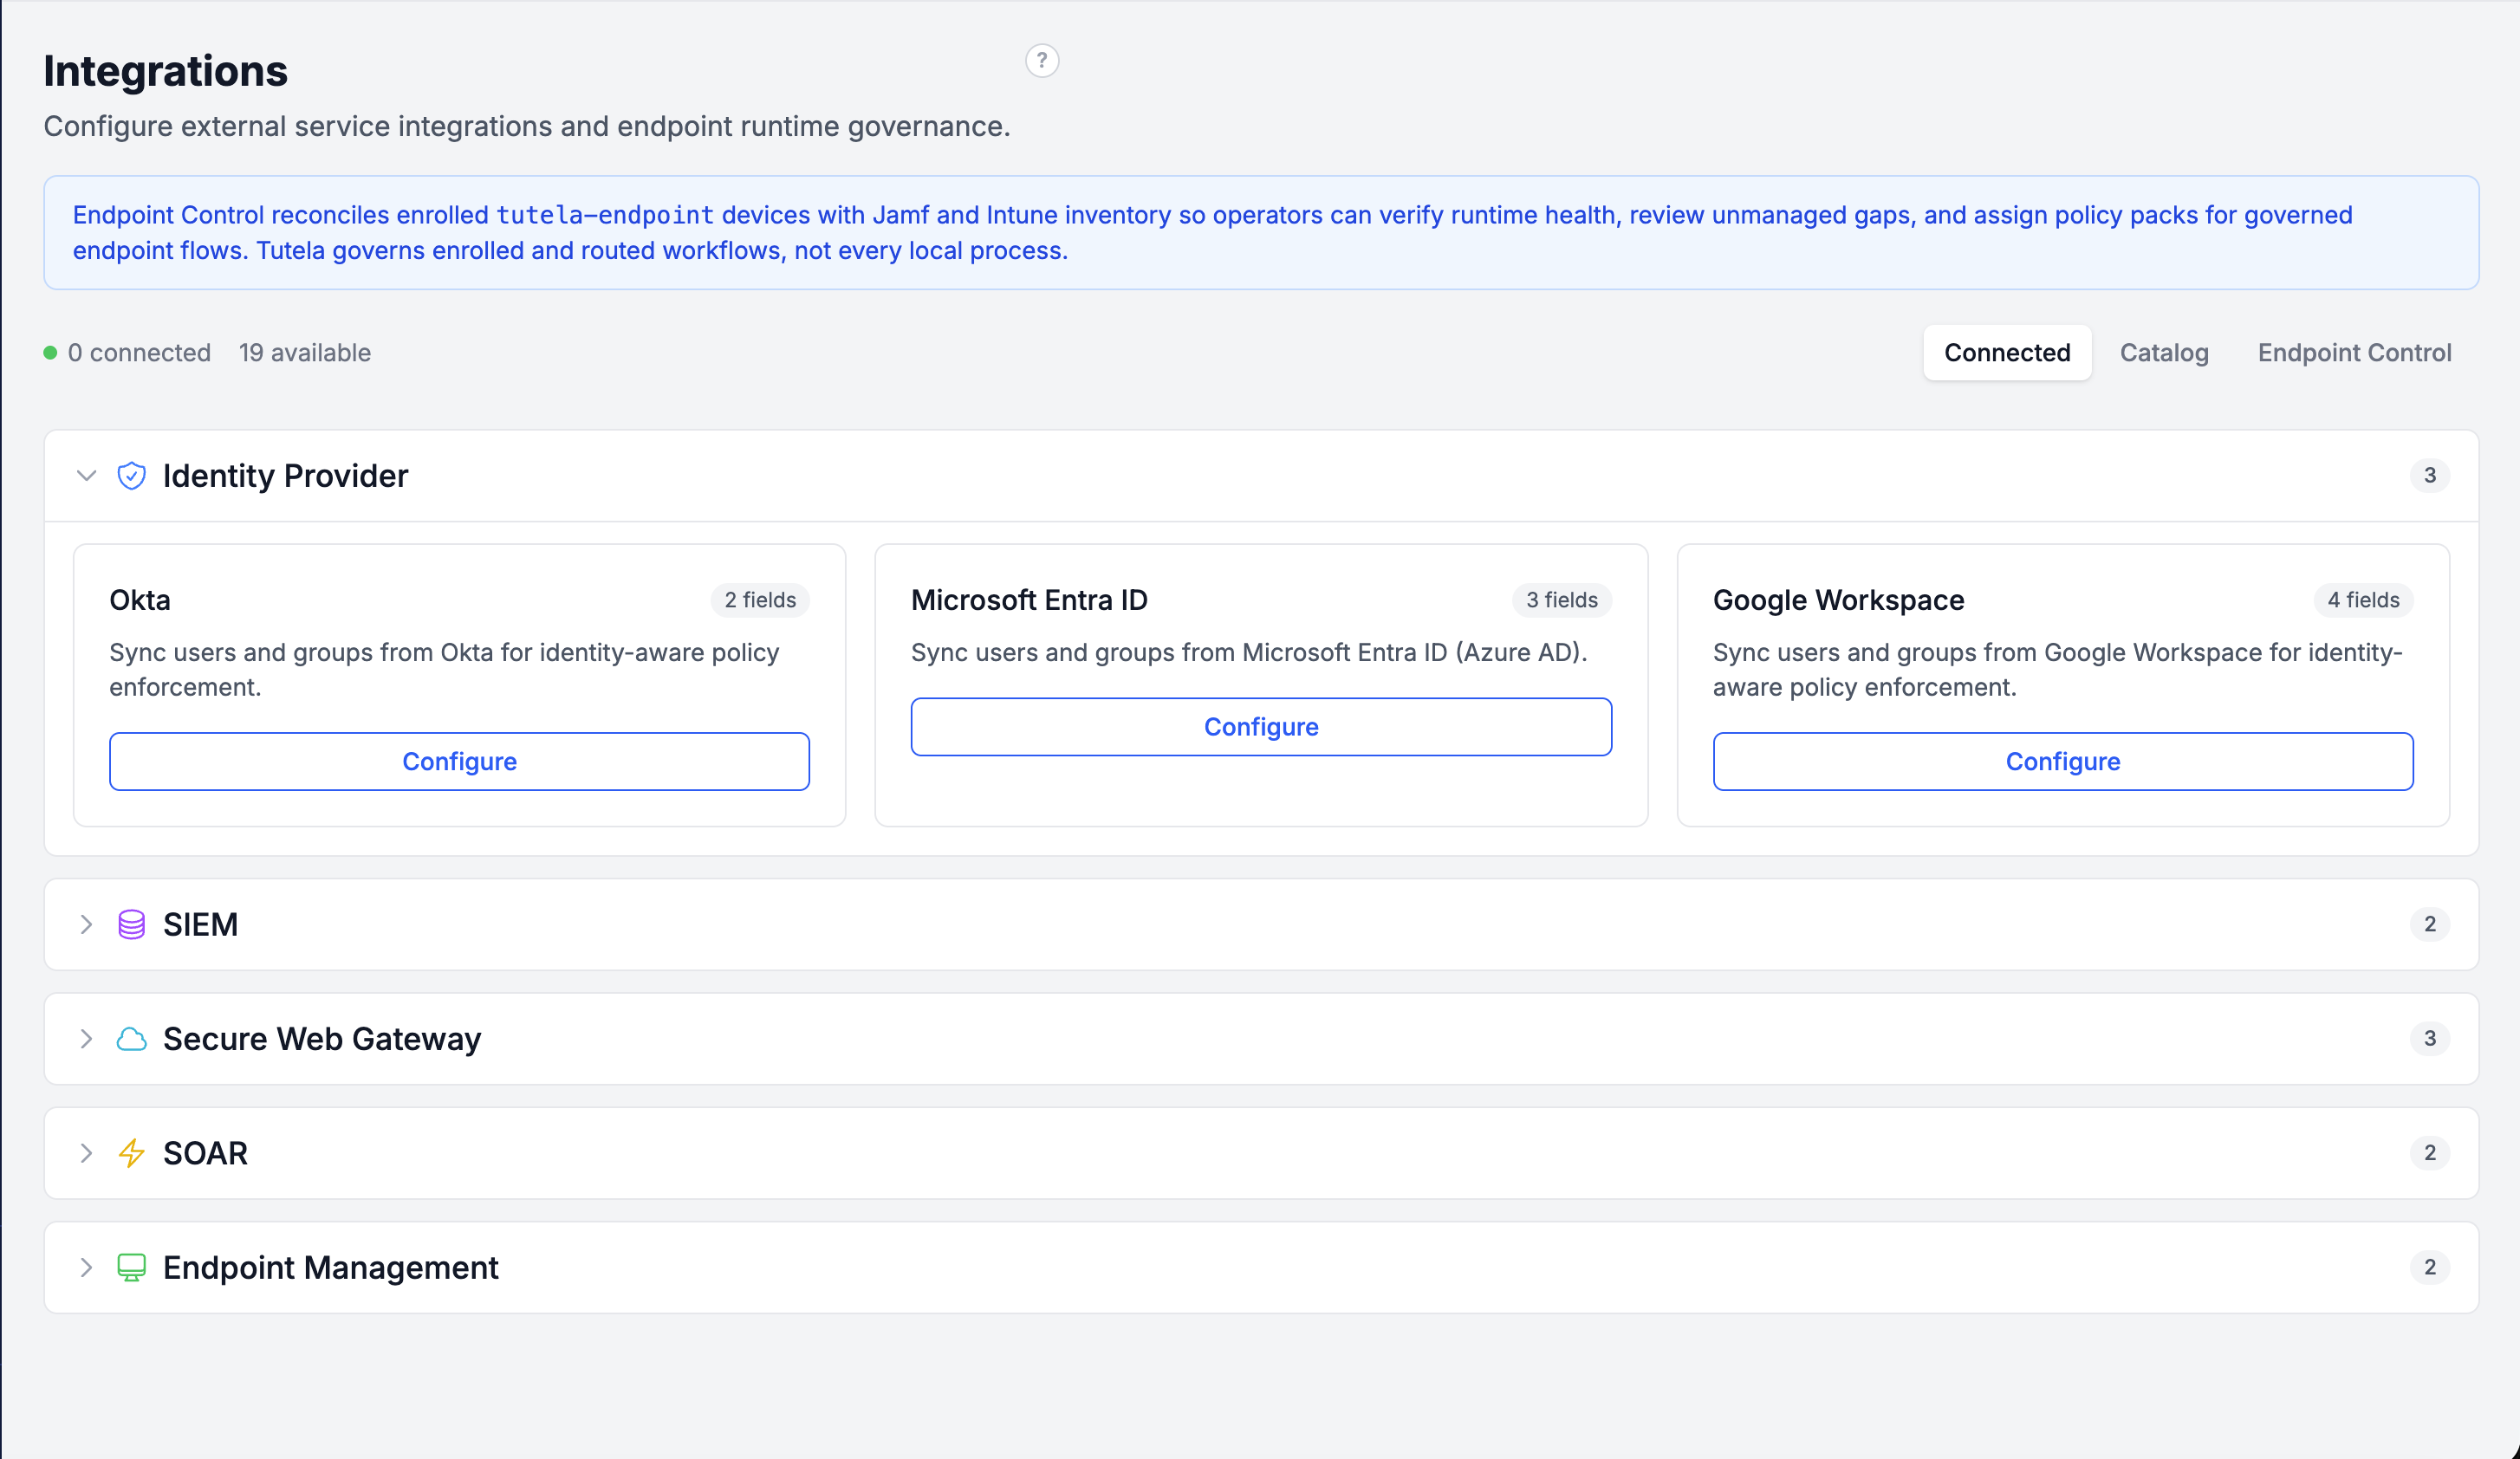
Image
Tutela Agentic Security - Integration Dashboard

Video
Product video
Tutela Agentic Security by H2H gives security teams visibility and policy control over prompts, files, outputs, tool calls, usage signals, and autonomous actions before sensitive data moves. Approve AI adoption with runtime controls that prevent leakage, govern risky actions, and preserve evidence your security team can inspect.
Key Capabilities
-
Runtime AI Governance across four deployment patterns: Browser AI, Embedded AI, Enterprise AI Gateways, and Agentic/MCP Ecosystems
-
Sensitive data leak prevention for AI workflows including prompts, files, outputs, API payloads, and tool calls
-
Prompt, file, output, and tool-call inspection with granular policy enforcement
-
AI usage and token-cost visibility connecting cost, model, app, user, and activity signals to governance records
-
MCP trust validation and agent action governance for autonomous tool use
-
Searchable audit trail preserving evidence for policy decisions, usage signals, exceptions, and agent actions
How It Works
Tutela sits at the runtime control points where prompts, files, outputs, APIs, tools, models, users, and sensitive data meet. Each pattern gets the same governance record: context, decision, action, and proof.
Browser AI - Govern employee use of ChatGPT, Claude, Gemini, Copilot, and other browser-based AI before prompts or files expose sensitive data.
Embedded AI - Inspect internal copilots, customer assistants, and SaaS applications that send business context to LLM APIs.
Enterprise AI Gateways - Standardize policy, visibility, and audit evidence across centralized model routing and internal AI platforms.
Agentic and MCP Ecosystems - Validate trust, govern tool use, and audit requested actions across agents, MCP servers, and connected assistants.
Customer-Owned Deployment
Tutela is designed for customer-owned deployment. Workflow inspection, usage records, policy decisions, and audit evidence stay under customer control. Sensitive context remains in the environment your team controls, ensuring governance data never leaves your operating model.
H2H offers a 60-day software evaluation window. Request a private offer today for your free evaluation. Early adopters can lock in significant multi-year discounts.
Who This Helps
Security, AI governance, IT, legal, finance, HR, sales, support, application security, and platform teams use Tutela to approve AI workflows, investigate incidents, and prove controls without blanket bans. Teams can adopt useful AI workflows without unmanaged workarounds.
Outcomes
- Let teams adopt useful AI workflows without blanket bans or unmanaged workarounds
- Stop sensitive prompts, files, outputs, API payloads, and tool calls before data leaves trusted paths
- Give security teams searchable evidence for policy decisions, usage signals, exceptions, and agent actions
- Connect AI usage, cost, model, app, user, and unusual activity signals to the same governance record
Policy Controls
Protection policies define active controls including coach, warn, redact, block, allow, or review actions for regulated data, prompt injection, payment data, and source-code protection. Each policy decision is preserved as reviewable audit context.
Getting Started
Review your active AI deployment patterns across Browser AI, Embedded AI, Enterprise AI Gateways, or Agentic and MCP ecosystems. Use technical guides and architecture material to align ownership boundaries, operating responsibilities, and commercial review before production use.
Highlights
- Runtime AI Governance across Browser AI, Embedded AI, Enterprise AI Gateways, and Agentic/MCP Ecosystems with granular policy enforcement for prompts, files, outputs, API payloads, and tool calls.
- Customer-owned deployment keeps workflow inspection, usage records, policy decisions, and audit evidence under your team control while sensitive context remains in the environment you operate.
- AI usage and token-cost visibility connects cost, model, app, user, and activity signals to governance records. MCP trust validation helps teams govern tool use and audit agent actions.
Details
Sold by
Categories
Delivery method
Supported services
Delivery option
Tutela Marketplace Installer
Latest version
Operating system
Linux
Deployed on AWS
Features and programs
Financing for AWS Marketplace purchases
AWS Marketplace now accepts line of credit payments through the PNC Vendor Finance program. This program is available to select AWS customers in the US, excluding NV, NC, ND, TN, & VT.

Pricing
Pricing is based on the duration and terms of your contract with the vendor. This entitles you to a specified quantity of use for the contract duration. If you choose not to renew or replace your contract before it ends, access to these entitlements will expire.
Additional AWS infrastructure costs may apply. Use the AWS Pricing Calculator to estimate your infrastructure costs.
Dimension | Description | Cost/12 months |
|---|---|---|
Full Platform | Full Tutela platform entitlement | $125,000.00 |
Dimensions summary
This listing offers one pricing dimension: the Full Platform entitlement, billed by Units under a contract term. You buy access to the entire Tutela platform rather than choosing separate tiers or modules. Pricing scales with the number of Units you commit to. There are no add-ons or usage-based components to combine. The platform covers agentic security and AI workflow governance, along with runtime evidence and controls. To adjust scale, you change the Unit quantity within your contract.
Top-of-mind questions for buyers
The pricing table lists Units as the metric for full platform access, but it does not define what one Unit maps to. The exact mapping — such as protected agents, workflows, or endpoints — is not specified in either source. Contact the vendor to confirm how Units are counted for your deployment.
The entitlement covers agentic security and AI workflow governance. It includes runtime controls and evidence collection for autonomous AI agents. It supports governance across enterprise AI deployment patterns like browser AI, embedded AI, gateways, and agent workflows. You get the entire platform in one entitlement rather than separate modules.
You adjust the number of Units you commit to under the contract. There is one dimension, so no separate add-ons or usage-based charges combine into your bill. Cost changes with the Unit quantity you hold. Contact the vendor for details on changing quantity mid-term.
tutelacloud.com
Helpful?
Vendor refund policy
The public offer is a paid annual subscription at the USD 125,000 list price and does not include a complimentary trial. Complimentary 60-day evaluations are available only through an H2H-issued AWS Marketplace private offer requested at https://tutelacloud.com/trial . AWS infrastructure, GPU, model download, storage, network, and data-transfer costs are paid by the buyer. Public-offer software charges are non-refundable except as required by law or approved in writing by H2H and AWS Marketplace.

Legal
Vendor terms and conditions
Upon subscribing to this product, you must acknowledge and agree to the terms and conditions outlined in the vendor's End User License Agreement (EULA) .
Content disclaimer
Vendors are responsible for their product descriptions and other product content. AWS does not warrant that vendors' product descriptions or other product content are accurate, complete, reliable, current, or error-free.
Delivery details
Tutela Marketplace Installer
Supported services: Learn more
- Amazon ECS
- Amazon EKS
Container image
Containers are lightweight, portable execution environments that wrap server application software in a filesystem that includes everything it needs to run. Container applications run on supported container runtimes and orchestration services, such as Amazon Elastic Container Service (Amazon ECS) or Amazon Elastic Kubernetes Service (Amazon EKS). Both eliminate the need for you to install and operate your own container orchestration software by managing and scheduling containers on a scalable cluster of virtual machines.
Version release notes
Tutela v2.47.26 Marketplace release with one Tutela Marketplace Installer delivery option, parameter-selected Public Internet and Private Network launch modes, Standard, Slim Training, and AI Runtime Essentials deployment profiles, optional Private Inference with vLLM, Docker schema v2 Marketplace images, bundled Monitoring/Grafana services for production profiles, and explicit GPU/model-download acknowledgement for vLLM. This release supersedes earlier Tutela Marketplace versions. Historical delivery options should be Restricted while immutable release artifacts and Marketplace images remain retained for the current public release and designated rollback releases.
Additional details
Usage instructions
Accept the AWS Marketplace offer, choose Tutela Marketplace Installer, and launch the unified CloudFormation template. In the Resources section, open the resource labeled Usage instructions for the full Parameter Reference table, including when each parameter is required, defaults, customer-change guidance, and warnings. Enter customer-owned values including environment name, application domain, hosted zone or private DNS inputs, two availability zones, database password, and certificate inputs. Choose launch parameters as follows. Standard Public: AccessMode=public, EnableLocalModelRuntime=false, DeploymentProfile=production, CertificateMode=auto-public or existing-acm. AI Runtime Essentials Public: AccessMode=public, EnableLocalModelRuntime=false, DeploymentProfile=essentials_runtime, CertificateMode=auto-public or existing-acm. AI Runtime Essentials Private: AccessMode=private, EnableLocalModelRuntime=false, DeploymentProfile=essentials_runtime, CertificateMode=private-ca, existing-acm, or create-private-ca. Slim Public: AccessMode=public, EnableLocalModelRuntime=false, DeploymentProfile=slim_training, CertificateMode=auto-public or existing-acm. Standard Private: AccessMode=private, EnableLocalModelRuntime=false, DeploymentProfile=production, CertificateMode=private-ca, existing-acm, or create-private-ca. CertificateMode=create-private-ca requires PrivateCertificateAuthorityCostAcknowledgement=I_ACKNOWLEDGE_PRIVATE_CA_COSTS_AND_TRUST_BOOTSTRAP. Private Inference with vLLM Public: AccessMode=public, EnableLocalModelRuntime=true, DeploymentProfile=production, CertificateMode=auto-public or existing-acm, and enter I_ACKNOWLEDGE_GPU_AND_MODEL_DOWNLOAD_COSTS. Private Inference with vLLM Private: AccessMode=private, EnableLocalModelRuntime=true, DeploymentProfile=production, CertificateMode=private-ca, existing-acm, or create-private-ca, and enter I_ACKNOWLEDGE_GPU_AND_MODEL_DOWNLOAD_COSTS. vLLM creates billable GPU resources and downloads model weights at runtime using Marketplace ECR tutela-aig-vllm:v2.47.26-marketplace.1.
Resources
Vendor resources
Support
Vendor support
For technical assistance, product questions, or to request a refund, contact the H2H support team at support@h2htech.com .
Evaluation and Onboarding H2H offers a 60-day software evaluation window. Submit a private offer request today. To begin your evaluation or request deployment guides and architecture documentation, email support@h2htech.com with your organization name and intended deployment pattern (Browser AI, Embedded AI, Enterprise AI Gateway, or Agentic/MCP).
Getting Help
The support team can assist with product configuration, policy setup, troubleshooting governance workflows, deployment guidance, and general account inquiries. When contacting support, include your organization name, a description of the issue, and any relevant log output to help expedite resolution.
AWS infrastructure support
AWS Support is a one-on-one, fast-response support channel that is staffed 24x7x365 with experienced and technical support engineers. The service helps customers of all sizes and technical abilities to successfully utilize the products and features provided by Amazon Web Services.
Similar products
Agentic AI-powered, continuous web application penetration testing.
A scalable, continuous, deep, and robust pentest solution, fully aligned with your unique business context.

Pluto Security aims to enable business users to innovate securely.
Your AI agents are already in production. Every security tool you have was designed before they existed.
Salt Security is the full-stack Agentic Security Platform, purpose-built to discover, govern, and protect AI agents, MCP servers, and APIs across code, configuration, and runtime. Unlike model guardrails that stop at the conversation, Salt protects the action layer: where agents execute business logic, invoke APIs, and touch your most sensitive systems. Deploys agentlessly across your AWS environment in under 10 minutes.
RuntimeAI Core is the self-hosted AMI deployment of RuntimeAI's AI agent governance platform -- discovery, policy enforcement, and kill-switch control for AI agents and MCP tool calls, deployable entirely within your own AWS account.
Customer reviews
No customer reviews yet
Be the first to review this product . We've partnered with PeerSpot to gather customer feedback. You can share your experience by writing or recording a review, or scheduling a call with a PeerSpot analyst.