Sold by: Akadenia
Continuous external scanning of the hosts you own: ports, web, TLS, SSH and email security, lookalike domains and subdomains, with findings mapped to OWASP and NIST, change alerts, and client-ready pentest reports. Enterprise: custom limits and terms, by private offer.
Overview
Image
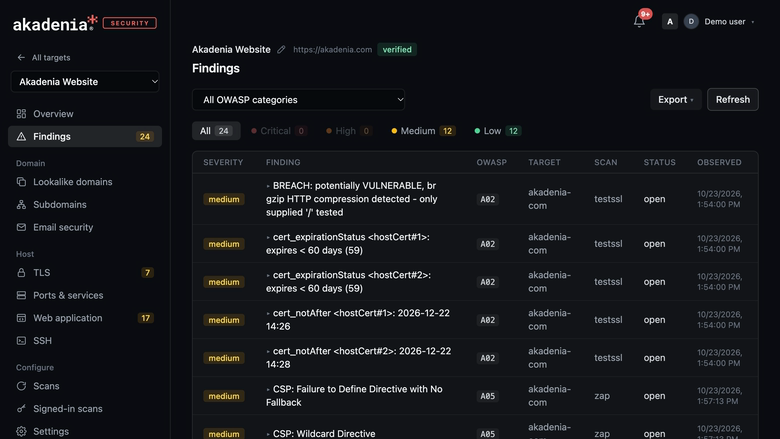
Findings by severity, tracked from scan to scan
Image
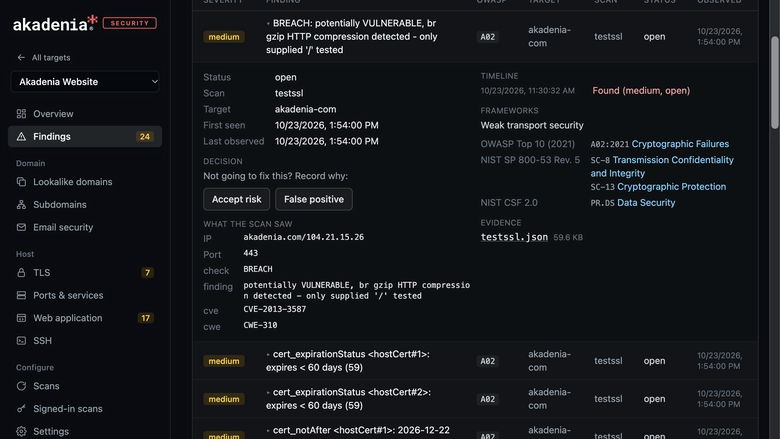
Finding detail mapped to OWASP and NIST
Image
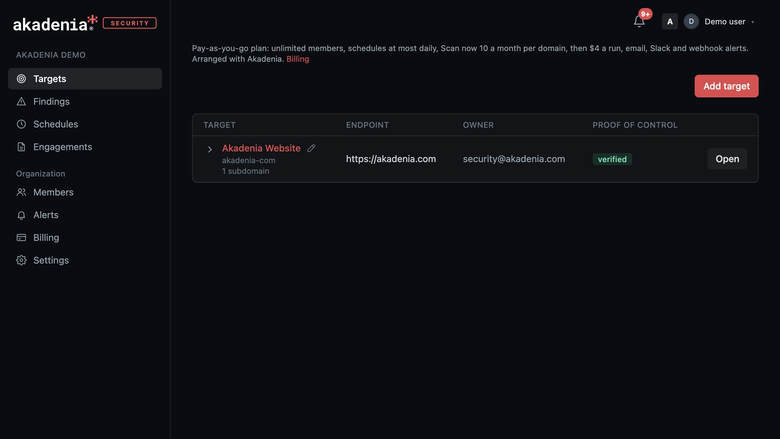
Targets, verified before any scan runs
Image
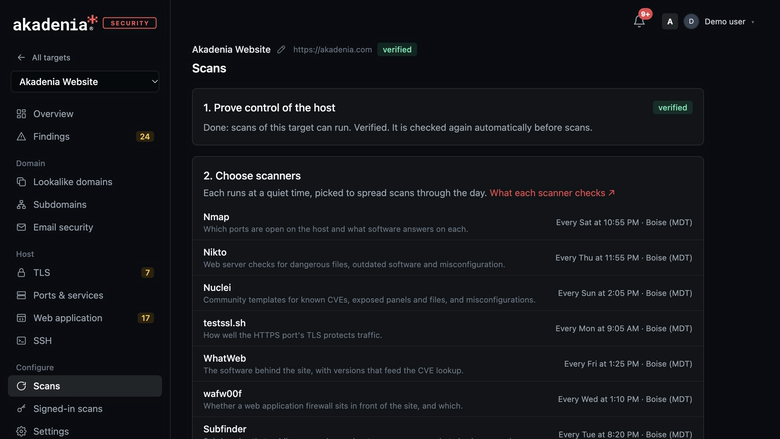
Every scanner on its own schedule
Image
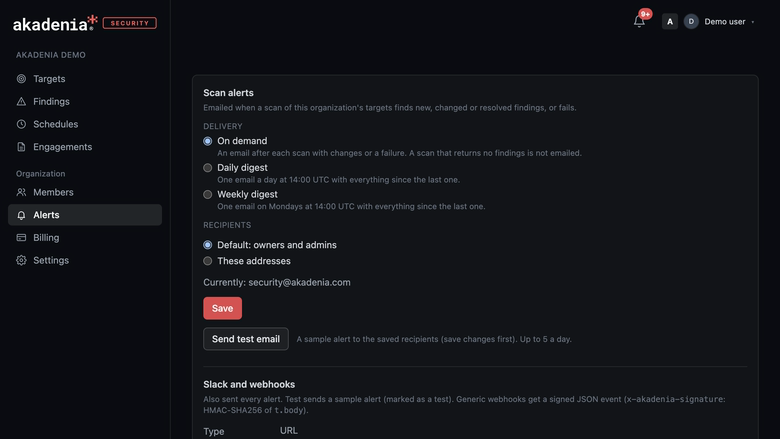
Alerts by email, Slack and webhooks
Akadenia Security shows you what attackers can see of your systems from the internet, and tells you when it changes.
Add the hosts and URLs you are responsible for, prove you control them with a DNS TXT record, and schedule the checks you need, or run them on demand:
- Network and services: open ports and service versions (nmap), and the cryptography of SSH servers (ssh-audit).
- Web and TLS: web server checks (Nikto), known CVEs, exposed panels and misconfigurations (Nuclei), a passive web application scan of the pages a crawler finds (ZAP), TLS protocols, ciphers and certificate (testssl.sh), the software behind the site (WhatWeb) and the firewall in front of it (wafw00f), plus uptime and certificate expiry.
- DNS and email: SPF, DMARC, MTA-STS and DNSSEC for your domain (checkdmarc), and registered lookalike domains that could be used for phishing (dnstwist).
- Discovery: subdomains that public sources know about (subfinder), each one click away from becoming a target.
Every run is compared with the previous one, so you see new, changed and resolved findings, the history of each target, and known CVEs for detected software versions. Mark the ports you expect to be open, and anything new stands out. What each scanner checks and sends is listed at security.akadenia.com/scanners.
Each finding is tagged with its OWASP Top 10 category, NIST SP 800-53 controls and NIST CSF 2.0 categories, linked to the official guidance, so results fit the frameworks you already report on. Alerts go to email, Slack or signed webhooks when findings change.
For penetration tests, engagements collect the scope, curated findings, retests and the tests run, and produce a branded report reviewed and approved by Akadenia's security team.
Scans only run against targets your organization has recorded authorization for and verified through DNS. Data is stored in AWS (us-west-2) and isolated per organization, with owner, admin, analyst and viewer roles.
Enterprise is for organizations that need more than self-serve: custom limits on targets, members, schedules (as often as every 5 minutes) and Scan now, signed-in scanning, and terms agreed with Akadenia. Pricing is by private offer, on 1, 12 or 24-month contracts billed through your AWS account; the public price is a starting point. To pay only for what you use instead, see Akadenia Security (pay-as-you-go) on AWS Marketplace, or sign up for free at security.akadenia.com.
Highlights
- Scheduled external scanning with 12 scanners: ports and services, SSH, web server and web app (Nikto, Nuclei, ZAP), TLS, email security, lookalike domains and subdomains, every run compared with the last.
- Mapped to OWASP and NIST: findings tagged with OWASP Top 10, NIST SP 800-53 and NIST CSF 2.0, with known CVEs for detected versions and alerts by email, Slack or signed webhook.
- Authorized by design: DNS ownership proof and recorded authorization before any scan, per-organization isolation, role-based access, and pentest reports reviewed by Akadenia.
Details
New
Introducing multi-product solutions
You can now purchase comprehensive solutions tailored to use cases and industries.

Features and programs
Financing for AWS Marketplace purchases
AWS Marketplace now accepts line of credit payments through the PNC Vendor Finance program. This program is available to select AWS customers in the US, excluding NV, NC, ND, TN, & VT.

Pricing
Pricing is based on the duration and terms of your contract with the vendor. This entitles you to a specified quantity of use for the contract duration. If you choose not to renew or replace your contract before it ends, access to these entitlements will expire.
Additional AWS infrastructure costs may apply. Use the AWS Pricing Calculator to estimate your infrastructure costs.
Dimension | Description | Cost/month |
|---|---|---|
Team | Up to 10 targets and 20 members; schedules as often as hourly; all scan types, including Nikto and ZAP; Scan now 5 times a day; email, Slack and webhook alerts. | $149.00 |
Business | Up to 50 targets and unlimited members; schedules as often as every 15 minutes; all scan types; unlimited Scan now; email, Slack and webhook alerts. | $499.00 |
Enterprise | Custom limits and terms for your organization: targets, members, schedules as often as every 5 minutes, Scan now, signed-in scanning, all scanners and alerts. Priced by private offer; this is the list price. | $999.00 |
Dimensions summary
This listing offers three tiers that scale by capacity and scan frequency. Team covers up to 10 targets and 20 members, with scheduled scans as often as hourly and a daily limit on manual scans. Business raises limits to 50 targets and unlimited members, with scheduling as often as every 15 minutes and unlimited manual scans. Enterprise sets custom limits for targets, members, and scheduling as often as every 5 minutes, and adds signed-in scanning. Enterprise is priced through a private offer, and the table shows the list price. All tiers include every scan type and all alert channels.
Top-of-mind questions for buyers
A target is an external asset you add and prove you control, such as a website or domain. You scan each target for findings, framework mappings, and email security checks. Team allows up to 10 targets, Business up to 50, and Enterprise uses custom limits.
Each tier caps capacity. Team supports up to 10 targets and 20 members. Business supports up to 50 targets and unlimited members. To add capacity beyond these caps, you move to the next tier. Enterprise sets custom limits for targets and members through a private offer.
Team schedules scans as often as hourly and allows manual "Scan now" five times daily. Business schedules as often as every 15 minutes with unlimited manual scans. Enterprise schedules as often as every 5 minutes and adds signed-in scanning. All tiers include every scan type and all alert channels.
security.akadenia.com
Helpful?
Vendor refund policy
New contracts cancelled within 14 days of purchase receive a full refund. After 14 days, fees are non-refundable, except where required by law. To request a refund, email support@akadenia.com or call +1 (208) 450-3637.

Legal
Vendor terms and conditions
Upon subscribing to this product, you must acknowledge and agree to the terms and conditions outlined in the vendor's End User License Agreement (EULA) .
Content disclaimer
Vendors are responsible for their product descriptions and other product content. AWS does not warrant that vendors' product descriptions or other product content are accurate, complete, reliable, current, or error-free.
Delivery details
Software as a Service (SaaS)
SaaS delivers cloud-based software applications directly to customers over the internet. You can access these applications through a subscription model. You will pay recurring monthly usage fees through your AWS bill, while AWS handles deployment and infrastructure management, ensuring scalability, reliability, and seamless integration with other AWS services.
Resources
Vendor resources
Support
Vendor support
Contact Akadenia support by email support@akadenia.com or by phone at +1 (208) 450-3637
AWS infrastructure support
AWS Support is a one-on-one, fast-response support channel that is staffed 24x7x365 with experienced and technical support engineers. The service helps customers of all sizes and technical abilities to successfully utilize the products and features provided by Amazon Web Services.
Similar products

Akadenia builds great software products — custom web and mobile apps, cloud-native APIs, and GenAI solutions powered by Amazon Bedrock. As an AWS Select Tier Partner, we embed as a full engineering team for seed-to-Series B startups in HealthTech, FinTech, and GovTech. Our team has protected 4.5M+ lives via real-time public safety infrastructure and built AI-driven products alongside teams like LandingAI.

Production-ready GenAI integrations using Amazon Bedrock. We embed large language models, intelligent automation, and AI workflows into your product — shipped, secured, and scaled on AWS. AWS Select Tier Partner.
Below∅Day has a talented and diverse team of security professionals based across the United States. Our team comprises experienced Penetration Testers, Malware Analysts, Security Architects, Audit and Policy experts, and Trainers. Our primary objective is to provide you with a clear understanding of any vulnerabilities present in your systems, and to facilitate the remediation process as seamlessly as possible.
Dune replaces legacy solutions with real time, User Adaptive Risk Management, quantifying behavioral risk, simulating specific attacks, and adapting controls automatically to prevent human layer breaches.
Customer reviews
No customer reviews yet
Be the first to review this product . We've partnered with PeerSpot to gather customer feedback. You can share your experience by writing or recording a review, or scheduling a call with a PeerSpot analyst.