Sold by: Spark Business Group
Spark EPC delivers a structured AWS Landing Zone review that produces a prioritised remediation roadmap, helping organisations reduce security risk and accelerate cloud growth.
Overview
Spark EPC AWS Landing Zone Review
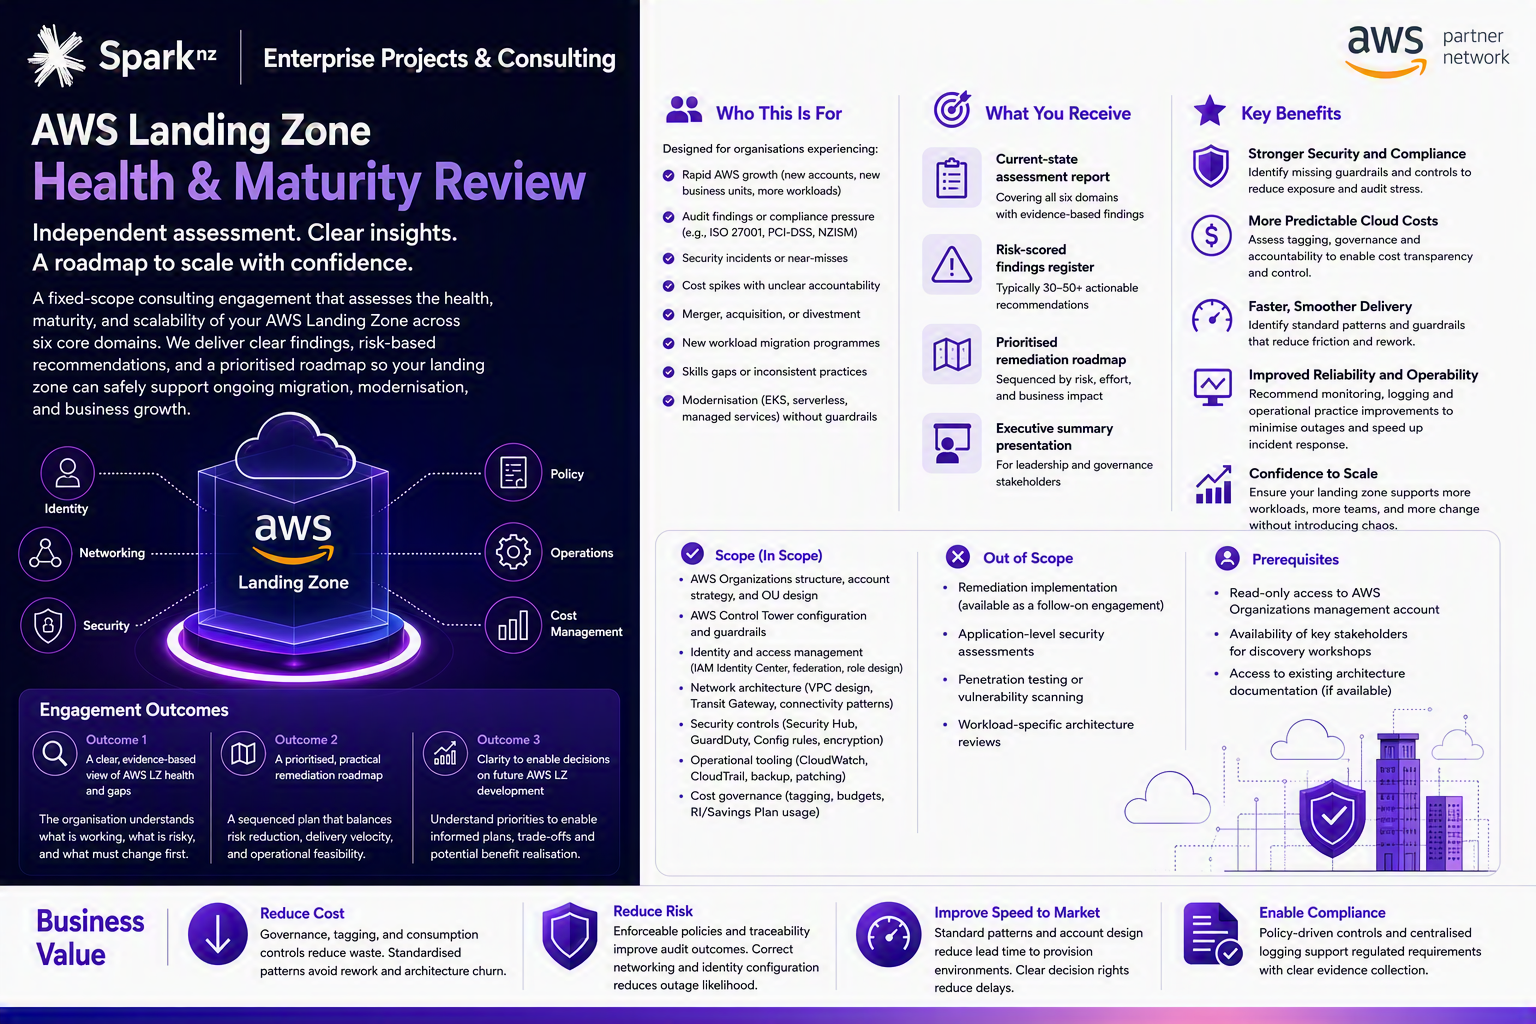
The AWS Landing Zone Review is a fixed-scope consulting engagement that assesses the health, maturity, and scalability of your AWS Landing Zone. We evaluate how your AWS environment is structured and governed - including AWS Organizations, AWS Control Tower, AWS IAM Identity Center, AWS CloudTrail, AWS Config, AWS Security Hub, and networking constructs - across six core domains: identity, networking, security, policy, operations, and cost management.
We deliver clear findings, risk-based recommendations, and a prioritised remediation roadmap so your landing zone can safely support ongoing migration, modernisation, and business growth.
Who This Is For
This engagement is designed for organisations experiencing:
- Rapid AWS growth (new accounts, new business units, more workloads)
- Audit findings or compliance pressure (e.g., ISO 27001, PCI-DSS, NZISM, or industry-specific obligations)
- Security incidents or near-misses with a growing security backlog
- Cost spikes with unclear accountability (chargeback/showback absent)
- Merger, acquisition, or divestment requiring AWS account restructuring
- New workload migration programmes where foundations must come first
- Skills gaps or inconsistent engineering practices across teams
- Modernisation (EKS, serverless, managed services adoption) without platform guardrails
Example Scenario
A financial services organisation consolidating 80+ AWS accounts post-acquisition engaged Spark EPC to assess their landing zone. The review identified critical IAM misconfigurations, inconsistent tagging across business units, and missing centralised logging. Within the engagement, we delivered a sequenced roadmap covering 45+ findings across all six domains, enabling the client to prioritise remediation aligned to their regulatory timeline.
What You Receive
- Current-state assessment report covering all six domains with evidence-based findings
- Risk-scored findings register typically producing 30-50+ actionable recommendations
- Prioritised remediation roadmap sequenced by risk, effort, and business impact
- Executive summary presentation for leadership and governance stakeholders
Key Benefits
Stronger Security and Compliance Identify missing guardrails and controls across AWS Security Hub, AWS Config rules, and IAM policies to reduce exposure and audit stress.
More Predictable Cloud Costs Assess tagging strategies, governance structures, and accountability models to enable cost transparency and control.
Faster, Smoother Delivery Identify standard patterns and guardrails that reduce friction and rework - helping teams stop reinventing the wheel for each new workload.
Improved Reliability and Operability Recommend monitoring, logging, and operational practice improvements using AWS CloudWatch and CloudTrail to minimise outages and speed up incident response.
Confidence to Scale Ensure your landing zone supports more workloads, more teams, and more change without introducing chaos.
Scope and Limitations
In Scope:
- Assessment of AWS Organizations structure, account strategy, and OU design
- Review of AWS Control Tower configuration and guardrails
- Identity and access management (IAM Identity Center, federation, role design)
- Network architecture (VPC design, Transit Gateway, connectivity patterns)
- Security controls (Security Hub, GuardDuty, Config rules, encryption)
- Operational tooling (CloudWatch, CloudTrail, backup, patching)
- Cost governance (tagging, budgets, Reserved Instance/Savings Plan usage)
Out of Scope:
- Remediation implementation (available as a follow-on engagement)
- Application-level security assessments
- Penetration testing or vulnerability scanning
- Workload-specific architecture reviews
Prerequisites:
- Read-only access to AWS Organizations management account
- Availability of key stakeholders for discovery workshops
- Access to existing architecture documentation (if available)
Business Value
Reduce Cost: Governance, tagging, and consumption controls reduce waste. Standardised patterns avoid rework and architecture churn.
Reduce Risk: Enforceable policies and traceability improve audit outcomes. Correct networking and identity configuration reduces outage likelihood.
Improve Speed to Market: Standard patterns and account design reduce lead time to provision environments. Clear decision rights reduce delays.
Enable Compliance: Policy-driven controls and centralised logging support regulated requirements with clear evidence collection.
Next Steps
Book a 30-minute Landing Zone Discovery Call with our team to scope your environment and receive an indicative timeline for your review.
Highlights
- Outcome 1: A clear, evidence-based view of AWS LZ health and gaps The organisation understands what is working, what is risky, and what must change first.
- Outcome 2: A prioritised, practical remediation roadmap A sequenced plan that balances risk reduction, delivery velocity, and operational feasibility.
- Outcome 3: Clarity to enable decisions on future AWS LZ development Understand AWS LZ development priorities to enable informed plans, trade-offs and potential benefit realisation.
Details
New
Introducing multi-product solutions
You can now purchase comprehensive solutions tailored to use cases and industries.

Pricing
Custom pricing options
Pricing is based on your specific requirements and eligibility. To get a custom quote for your needs, request a private offer.

Legal
Content disclaimer
Vendors are responsible for their product descriptions and other product content. AWS does not warrant that vendors' product descriptions or other product content are accurate, complete, reliable, current, or error-free.
Support
Vendor support
Engagement Support
During the Engagement
Your Spark EPC engagement team provides direct support throughout the review period. You will have a named engagement lead as your primary point of contact, with regular check-ins scheduled throughout the assessment.
Buyer Responsibilities and Access Requirements
- Provide read-only IAM access to your AWS Organizations management account
- Make key stakeholders available for discovery workshops (typically 2-3 sessions)
- Share existing architecture documentation, network diagrams, and governance policies where available
- Designate an internal sponsor to coordinate access and scheduling
Deliverable Format
You will receive a written assessment report, risk-scored findings register, prioritised remediation roadmap, and an executive summary presentation. A live walkthrough session is included to discuss findings and answer questions.
Post-Engagement Support
Following delivery of the final report, Spark EPC provides a 30-day clarification window during which your team can ask questions about findings and recommendations at no additional cost.
Contact
For engagement enquiries and scoping discussions, contact:
- Brett Snyman, Chapter Lead Public Cloud - Brett.Snyman@spark.co.nz
- Chris Nicholson, Domain Chapter Lead Enterprise Projects and Consulting - Chris.Nicholson@spark.co.nz
We aim to respond to all enquiries within one business day.