Sold by: PuzariCloud
Free Trial
AWS Free Tier
Daily read-only checks of your AWS account against Indian rules: CERT-In Directions 2022, DPDP Rules 2025, RBI Directions and SEBI CSCRF. Each check names the clause it supports and how to fix it, with a printable evidence pack per framework for your auditor.
Overview
Image
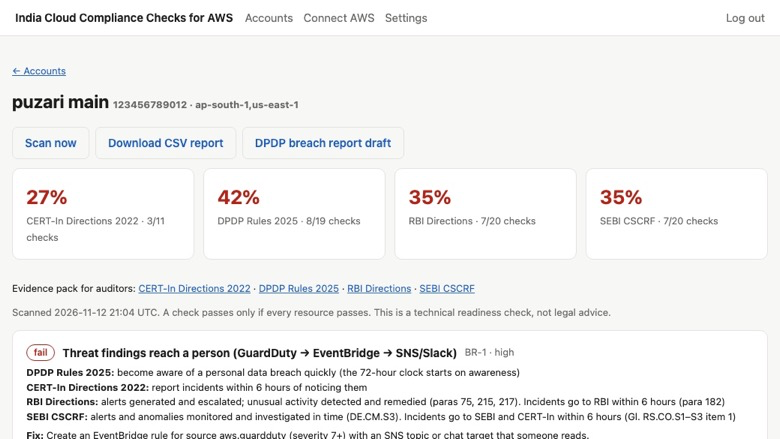
Scores for CERT-In, DPDP, RBI and SEBI
Image
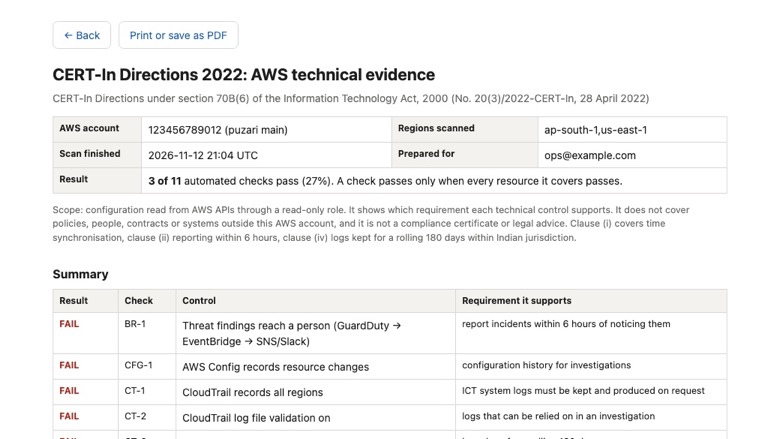
Printable CERT-In evidence pack
Show your auditor where your AWS account stands on Indian rules
Indian companies on AWS are asked the same questions by auditors, regulators and enterprise customers: are logs kept 180 days in India, is data encrypted, is MFA on, would a breach be noticed and reported in time? Answering means reading CERT-In, DPDP, RBI and SEBI documents and then checking dozens of AWS settings by hand.
India Cloud Compliance Checks for AWS does the AWS side for you every day.
What it checks
- Logging: CloudTrail in all Regions, log-file validation, retention of 180 days (CERT-In) or a year (DPDP), logs stored in India, CloudWatch retention, VPC flow logs, S3 data events
- Detection: GuardDuty, AWS Config, threat findings routed to a person, open high-severity findings
- Access: root MFA and no root keys, MFA for console users, key age, password policy
- Data: S3 public access, encryption of EBS and RDS, RDS backups, buckets and workloads outside India, Macie
- Network: SSH and RDP open to the internet
Mapped clause by clause
Each check shows the requirement it supports in the CERT-In Directions 2022, the DPDP Rules 2025, the RBI Directions for banks and payment operators, and SEBI CSCRF. Checks with no fitting clause are left unmapped rather than stretched.
What you get
- A score per framework and a plain-English fix for every failing check
- A printable evidence pack per framework, with scan history
- CSV export of every result
- Slack and email alerts when a check starts failing
- A DPDP breach-report draft built from your latest scan
Security and access
The CloudFormation stack creates one role that uses AWS's own SecurityAudit and ViewOnlyAccess managed policies, with an External ID so only your workspace can use it. It reads configuration only: no object contents, no database rows, no log text. Nothing in your account is changed. You can review the template before you deploy it, and deleting the stack removes our access.
Typical uses
- Preparing for a CERT-In, RBI or SEBI audit and showing the AWS side with dated evidence
- Answering security questionnaires from enterprise customers and banks
- Getting ready for the DPDP Rules before May 2027
- Catching a setting that drifted, such as a public bucket or an open SSH port, the day it happens
Who it is for
CTOs, CISOs and compliance leads at Indian SaaS, fintech, NBFCs, brokers, AMCs and healthtech companies running on AWS.
Getting started
- Subscribe, or start the 14-day free trial.
- Launch the read-only CloudFormation stack.
- Paste the role ARN. The first scan finishes in about a minute.
This is a technical readiness check, not legal advice or a certificate of compliance.
Start the 14-day free trial to see your scores for all four frameworks about a minute after connecting.
Highlights
- 28 AWS checks mapped clause by clause to four Indian frameworks. CERT-In Directions 2022 (logs kept 180 days in India, incident detection, clock sync, point of contact), DPDP Rules 2025 security safeguards, RBI Directions for banks and payment operators, and SEBI CSCRF standards. Where a framework has no fitting clause, the check is not mapped to it.
- An evidence pack your auditor can read. For each framework you get a printable page: every requirement the checks support, the result, the resources that fail, the fix and the scan history that shows continuous monitoring. Save it as PDF or export everything as CSV.
- Read-only and running in minutes. One CloudFormation stack creates a role with AWS's own SecurityAudit and ViewOnlyAccess policies: configuration only, never your data. Scans run daily, alerts go to Slack and email when a check starts failing, and a DPDP breach-report draft is ready if you need one. Priced per AWS account, unlimited users.
Details
Sold by
Categories
Delivery method
Deployed on AWS
New
Introducing multi-product solutions
You can now purchase comprehensive solutions tailored to use cases and industries.

Features and programs
Financing for AWS Marketplace purchases
AWS Marketplace now accepts line of credit payments through the PNC Vendor Finance program. This program is available to select AWS customers in the US, excluding NV, NC, ND, TN, & VT.

Pricing
Free trial
Try this product free according to the free trial terms set by the vendor.
Pricing is based on the duration and terms of your contract with the vendor. This entitles you to a specified quantity of use for the contract duration. If you choose not to renew or replace your contract before it ends, access to these entitlements will expire.
Additional AWS infrastructure costs may apply. Use the AWS Pricing Calculator to estimate your infrastructure costs.
Dimension | Description | Cost/month |
|---|---|---|
Starter | Daily CERT-In, DPDP and RBI checks for 1 AWS account, CSV reports, Slack and email alerts, unlimited users. | $49.00 |
Pro | Daily CERT-In, DPDP and RBI checks for up to 5 AWS accounts, CSV reports, Slack and email alerts, unlimited users. | $149.00 |
Business | Daily CERT-In, DPDP and RBI checks for up to 25 AWS accounts, CSV reports, Slack and email alerts, priority support, unlimited users. | $399.00 |
Dimensions summary
You choose one of three tiers priced as a contract. The tiers scale by how many AWS accounts you can check daily for CERT-In, DPDP and RBI compliance. Starter covers 1 account, Pro covers up to 5 accounts, and Business covers up to 25 accounts. All three include CSV reports, Slack and email alerts, and unlimited users. Business adds priority support. So the main difference across tiers is account coverage, with support level distinguishing the Business tier. You pick the size based on how many accounts you need to monitor.
Top-of-mind questions for buyers
Each AWS account you connect with a read-only role counts toward your tier limit. Starter allows 1, Pro up to 5, and Business up to 25. The service checks 28 controls daily across each connected account. You pick a tier based on how many accounts you need checked.
Each tier has a fixed account ceiling: Starter 1, Pro 5, Business 25. To check more accounts than your tier covers, you move to a tier with a higher account count. The limits are set per tier, so added coverage comes from choosing the tier that fits your account total.
Daily checks cover CERT-In, DPDP and RBI across all three tiers. The service reviews configuration metadata only through a read-only role, never your data. It reports readiness against framework requirements with plain-language fixes. This is a technical readiness check, not legal advice.
compliance.puzaricloud.in
Helpful?
Vendor refund policy
Full refund within 14 days of a new subscription if the product doesn't work for you. After that, cancel any time and you won't be renewed; we don't refund partial periods. To request a refund, email ritom@puzaricloud.in with your AWS account ID.

Legal
Vendor terms and conditions
Upon subscribing to this product, you must acknowledge and agree to the terms and conditions outlined in the vendor's End User License Agreement (EULA) .
Content disclaimer
Vendors are responsible for their product descriptions and other product content. AWS does not warrant that vendors' product descriptions or other product content are accurate, complete, reliable, current, or error-free.
Delivery details
Software as a Service (SaaS)
SaaS delivers cloud-based software applications directly to customers over the internet. You can access these applications through a subscription model. You will pay recurring monthly usage fees through your AWS bill, while AWS handles deployment and infrastructure management, ensuring scalability, reliability, and seamless integration with other AWS services.
Resources
Support
Vendor support
Getting help
Email ritom@puzaricloud.in . We reply within one business day, Monday to Friday, India time, and usually much sooner.
What support covers
- Launching the CloudFormation stack and connecting accounts
- What a check means and how to fix it
- Which clause a check supports and how to present the evidence pack to an auditor
- Billing and plan changes through AWS Marketplace
When you write to us
Include your AWS account ID and the check ID (for example CT-3). Support is included on every plan, including the free trial. We explain the technical controls; we do not give legal advice.
Plans
Starter covers 1 AWS account, Pro 5 and Business 25, with daily scans, evidence packs and unlimited users on every plan.
Refunds
Full refund within 14 days of purchase if the product does not work for you. Email ritom@puzaricloud.in with your AWS account ID and we will arrange it through AWS Marketplace.
AWS infrastructure support
AWS Support is a one-on-one, fast-response support channel that is staffed 24x7x365 with experienced and technical support engineers. The service helps customers of all sizes and technical abilities to successfully utilize the products and features provided by Amazon Web Services.
Similar products
This is a repackaged open source software product wherein additional charges apply for a pre-hardened AMI with automated startup. Self-hosted cloud security scanner for AWS, Azure, and GCP, powered by open source tooling.

Helps businesses achieve and maintain regulatory compliance in AWS environments by aligning security controls with local and global regulations while simplifying audits and governance.

Don’t let your security and compliance be an afterthought in your cloud journey. Understand your current state, address any issues proactively and prepare for future audits and potential security threats.
Multi-account AWS security visibility is hard: infrastructure and application vulnerabilities stay hidden across disconnected scans. CirrusHQ AWS Security Health Check combines infrastructure posture scanning (Acuity) with AI-driven penetration testing (AWS Security Agent) in a single 3-5 day engagement, covering AWS Security Hub, GuardDuty and Inspector findings plus OWASP Top 10 application testing. You get an executive summary, IAM risk register, findings report and prioritised remediation roadmap, ready to action immediately. Built for multi-account AWS environments, regulated industries (financial services, healthcare, public sector) and SaaS platforms. No surprise invoices, just an expert assessment and an actionable roadmap. Contact us for a 30-minute scoping call, no obligation.
Customer reviews
No customer reviews yet
Be the first to review this product . We've partnered with PeerSpot to gather customer feedback. You can share your experience by writing or recording a review, or scheduling a call with a PeerSpot analyst.