Sold by: Six Feet Up, Inc.
GRC advisory services that transform governance into a traceable, automatable engineering system using Cloud Custodian (c7n) across AWS cloud and AI environments.
Overview
Security Becomes an Enabler, Not a Blocker
Many organizations treat GRC (Governance, Risk, and Compliance) like a compliance checklist. That may satisfy an auditor, but it leaves most of the value on the table. Six Feet Up helps you design governance as a high-speed interchange - where security controls compound in value, compliance maps naturally to operations, and risk-informed decisions replace defensive paperwork.
The Growing Governance Gap in Cloud and AI
AI agents act continuously at machine speed across legal, HR, engineering, and customer-facing systems. Without structured governance in place before AI scales, organizations accumulate risk debt that compounds quietly until it surfaces as a breach or a failed audit. Six Feet Up's advisory services address this gap with instrumentation-first governance across AWS services and environments.
Compliance Frameworks We Map To
Six Feet Up's advisory engagements help clients achieve and maintain compliance across all applicable frameworks they face - simultaneously. The team has direct experience mapping policies and controls to SOC 2, HIPAA, PCI DSS, and NIST 800-53. A single traceable policy can satisfy all of these frameworks at once, eliminating overlapping compliance friction and reducing the effort required to maintain multiple certifications or attestations.
AWS Services Coverage
Six Feet Up has deep experience governing nearly every AWS service, including AI and machine learning offerings such as Amazon SageMaker, and Amazon Bedrock. The team actively extends Cloud Custodian (c7n) - the open-source cloud governance engine - to enforce policy as code across AWS AI services and the broader AWS ecosystem. This means your governance controls can cover compute (EC2, Lambda, ECS), storage (S3, EBS), databases (RDS, DynamoDB), networking (VPC, CloudFront), identity (IAM, Organizations), and AI/ML services from a single, traceable policy framework. Cloud Custodian integration enables real-time detection of configuration drift, automated remediation of policy violations, and continuous compliance monitoring across your entire AWS footprint.
How the Engagement Works
SFU delivers GRC advisory services through a structured, phased approach:
Phase 1 - GRC Architecture and Lexicon
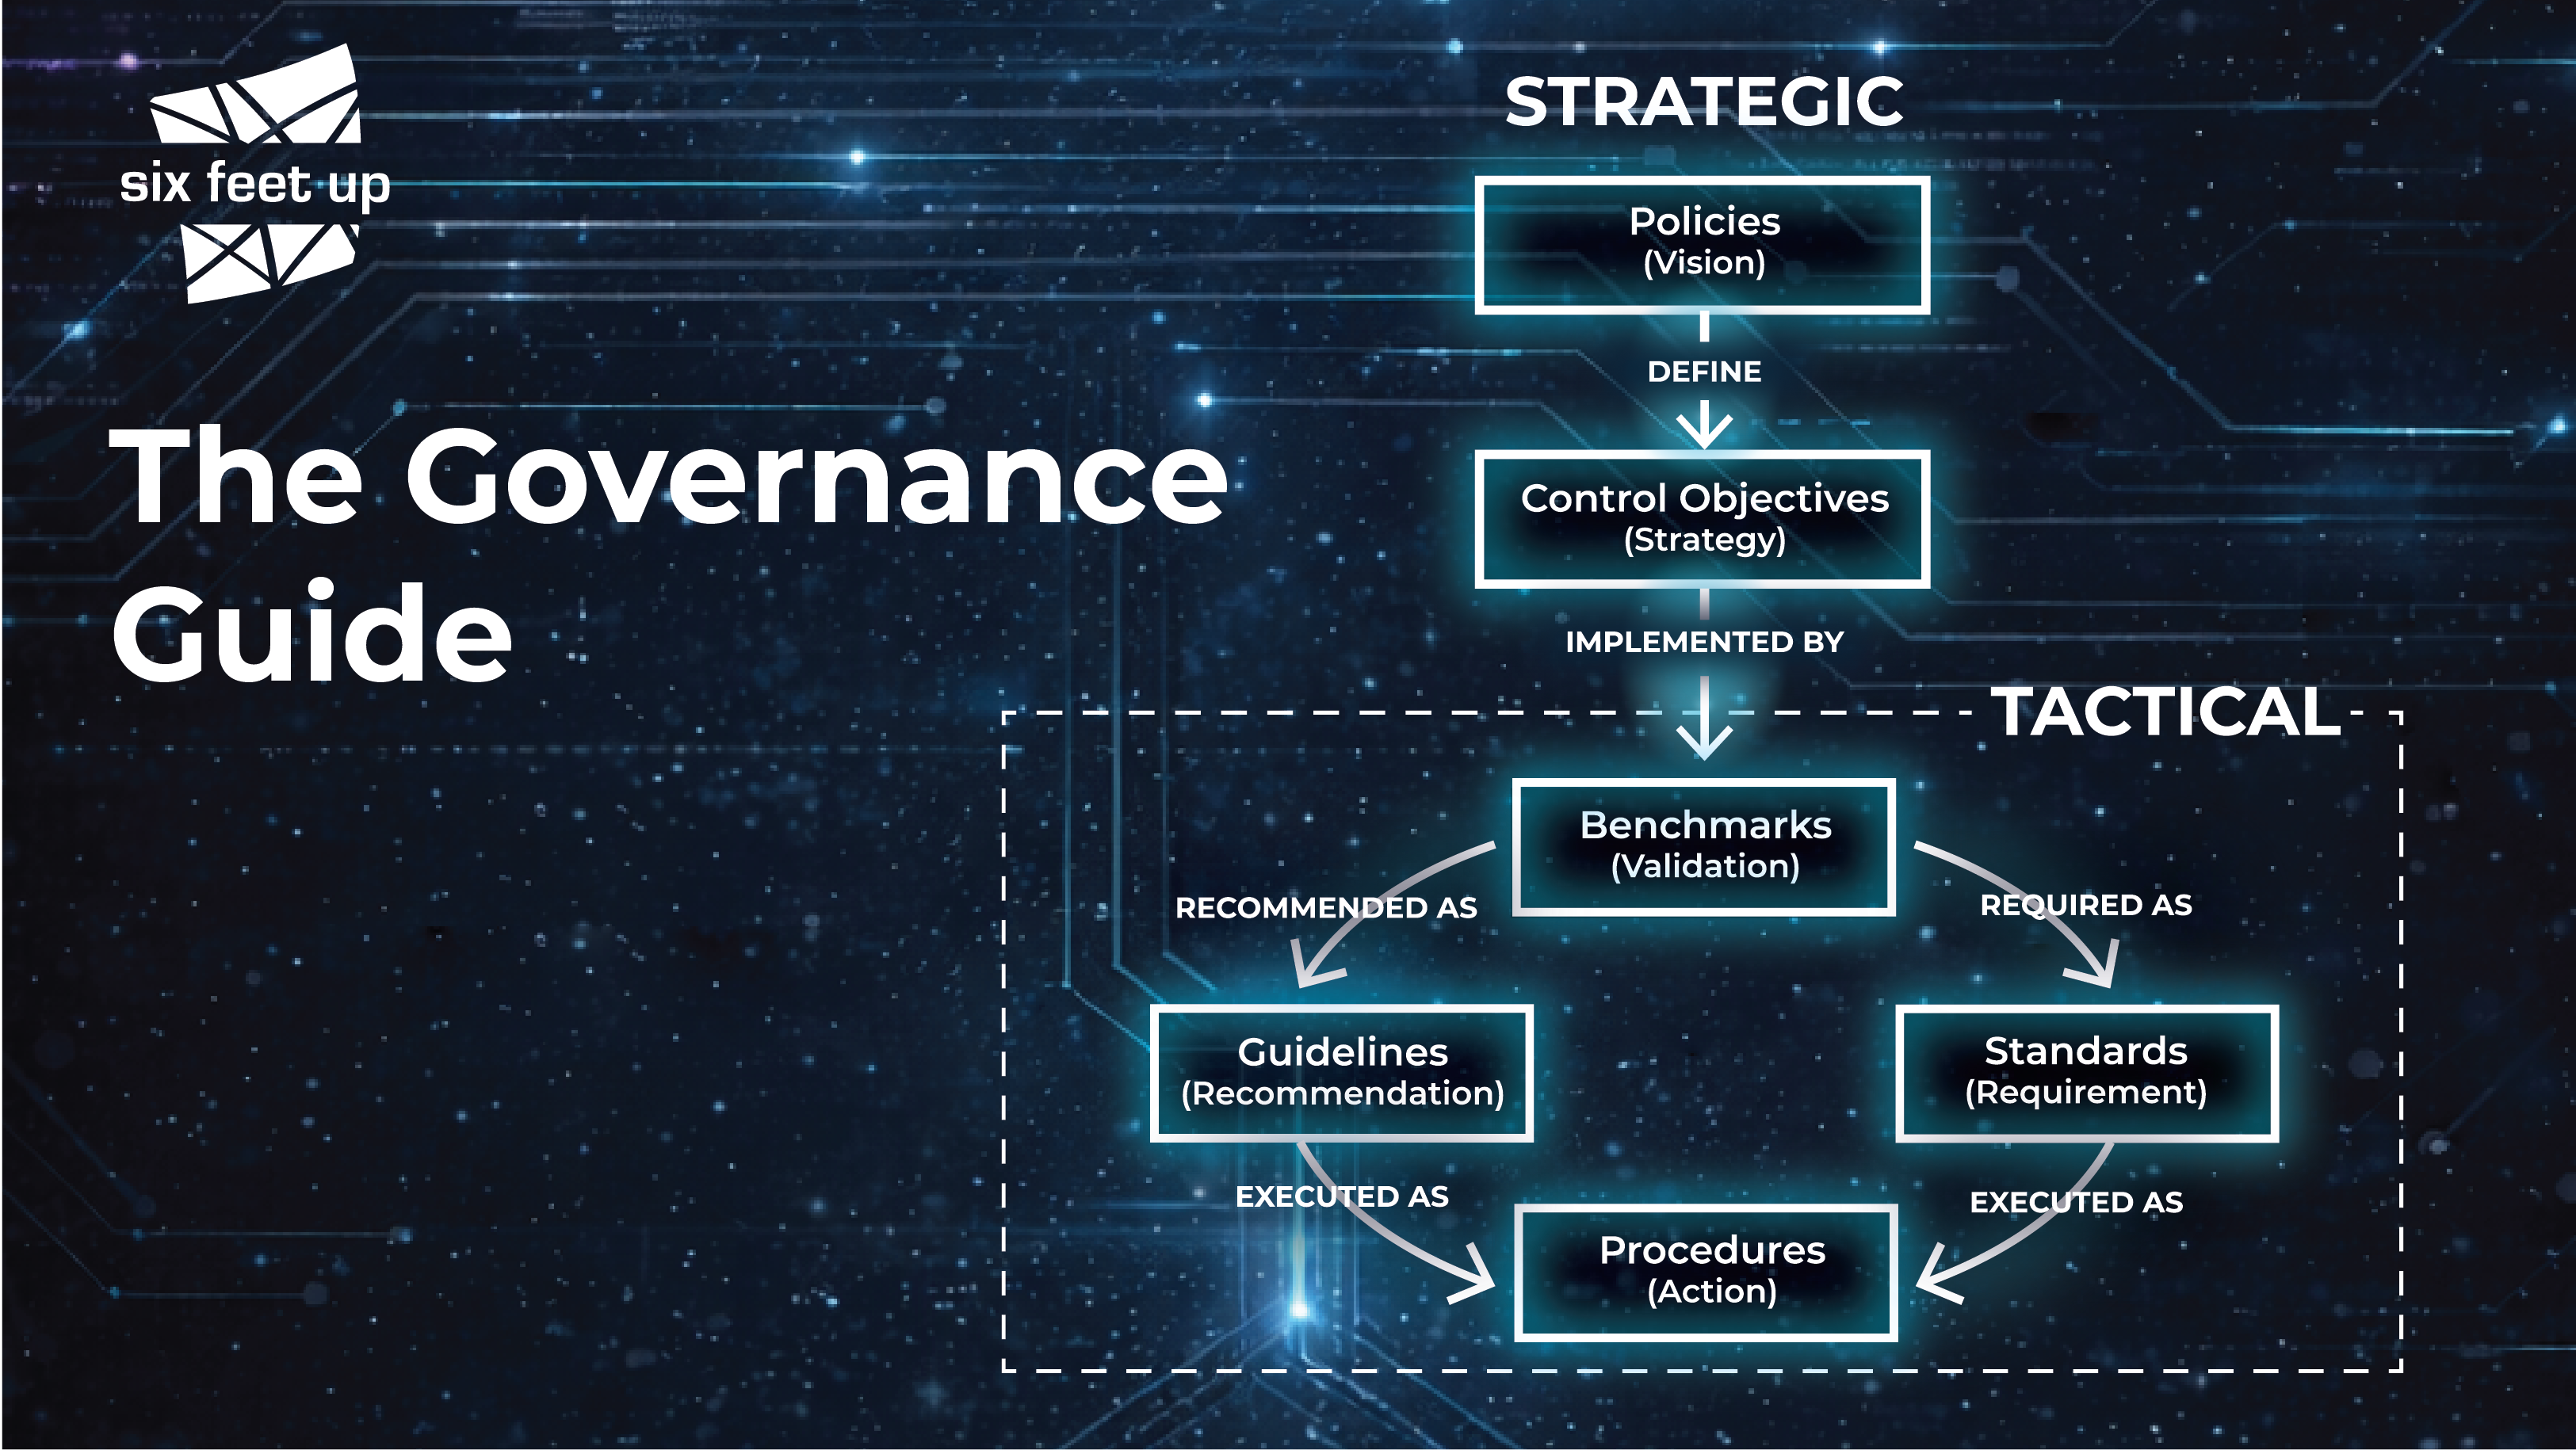
- Establish a shared GRC lexicon that flows from strategic intent to engineering execution
- Map policies to control objectives, benchmarks, standards, guidelines, and procedures aligned to SOC 2, HIPAA, PCI DSS, NIST 800-53, or other applicable frameworks
- Deliverable: Traceable Policy-to-Procedure Framework Document
Phase 2 - Discovery and Instrumentation
- Environment assessment and stakeholder interviews across your AWS footprint
- Instrumentation of systems using Cloud Custodian (c7n) and related tooling to observe what they touch, who uses them, and how behavior changes over time
- Deliverable: GRC Gap Assessment Report with prioritized risk findings
Phase 3 - Policy as Code Implementation
- Translate governance policies into automated, testable controls using Cloud Custodian (c7n) and complementary tooling
- Eliminate overlapping compliance friction across all applicable frameworks
- Deliverable: Policy as Code repository and compliance mapping matrix
Client Data Handling and Trust
Six Feet Up maintains a formal privacy policy and data classification standard that clients review prior to engagement. All client data is labeled and isolated on a per-client basis throughout discovery, instrumentation, and artifact delivery. Third-party vendors used during engagements are reviewed as part of Six Feet Up's procurement process to ensure they meet security and privacy requirements.
Use Case: AI-Driven Organizations Scaling Across Regulated Environments
Organizations deploying autonomous AI agents using services like Amazon Bedrock, or Amazon SageMaker across customer onboarding, internal operations, or decision-support systems need governance that keeps pace with machine-speed actions. Six Feet Up instruments these environments with Cloud Custodian (c7n) so governance decisions are driven by observed data rather than assumptions - critical for teams managing risk through a FinOps & cybersecurity lens.
What Buyers Need to Know
Prerequisites: Availability of a security, compliance, and/or FinOps stakeholder to participate in discovery sessions.
AWS Marketplace Relationship: This professional services offering relates directly to AWS services including but not limited to Amazon EC2, Amazon S3, AWS IAM, AWS Organizations, Amazon SageMaker, Amazon Bedrock, Amazon Q, AWS Lambda, Amazon RDS, Amazon VPC, and every other AWS service supported by Cloud Custodian (c7n).
Independent Reviews: Six Feet Up's advisory work has been reviewed on Clutch.
Next Step
Schedule a GRC Gap Assessment call to discuss your governance, risk, and compliance needs and determine engagement fit.
Highlights
- GRC as an Engineering System Built on Cloud Custodian (c7n): Transform governance from a compliance checklist into a traceable, automatable system spanning nearly every AWS service - including AI offerings such as Amazon Bedrock and Amazon SageMaker. A single policy maps to all applicable compliance frameworks a client faces - such as SOC 2, HIPAA, PCI DSS, and NIST 800-53 simultaneously.
- AI and Cloud Governance for Regulated AWS Environments: Instrument risk before AI scales across your environment. Six Feet Up actively extends Cloud Custodian (c7n) to support AWS AI services, observing what systems touch, who uses them, and how behavior changes over time - ensuring governance decisions are driven by observed data rather than assumptions.
- Policy as Code with Structured Delivery Across AWS Services: Eliminate overlapping compliance friction across SOC 2, HIPAA, PCI DSS, and NIST 800-53 through automated, testable policy controls powered by Cloud Custodian (c7n). Typical advisory engagements run 8-12 weeks, delivering a GRC Gap Assessment, Policy-to-Procedure Framework, and Policy as Code repository with compliance mapping matrix. Advisory scope covers architecture and codification - not remediation engineering.
Details
Sold by
Categories
Delivery method
Deployed on AWS
New
Introducing multi-product solutions
You can now purchase comprehensive solutions tailored to use cases and industries.
Pricing
Custom pricing options
Pricing is based on your specific requirements and eligibility. To get a custom quote for your needs, request a private offer.
Legal
Content disclaimer
Vendors are responsible for their product descriptions and other product content. AWS does not warrant that vendors' product descriptions or other product content are accurate, complete, reliable, current, or error-free.
Support
Vendor support
Support for GRC Advisory Engagements
Six Feet Up provides advisory support throughout the lifecycle of GRC engagements.
Contact Channels:
- Email: info@sixfeetup.com
- Phone: +1 (317) 861-5948
During Active Engagements: Clients receive dedicated advisory support with regular check-ins aligned to engagement milestones. Your Six Feet Up advisory team is available via email and scheduled calls throughout the engagement duration.
Post-Engagement Support: After deliverables are handed off, Six Feet Up remains available to answer questions about the governance frameworks, policy artifacts, and Policy as Code implementations delivered during the engagement.
Requesting Assistance: For questions about scoping a new engagement, troubleshooting delivered artifacts, or requesting changes to an active engagement, contact the team via email or phone.