Sold by: Threat Protect
Know where you stand against DORA or NIS2 and what to fix before regulators ask. Threat Protect confirms which regime applies, assesses gaps against each requirement, reviews ICT third-party and supplier risk, incident reporting and resilience testing, and gives your board a prioritised, costed remediation plan.
Overview
Image
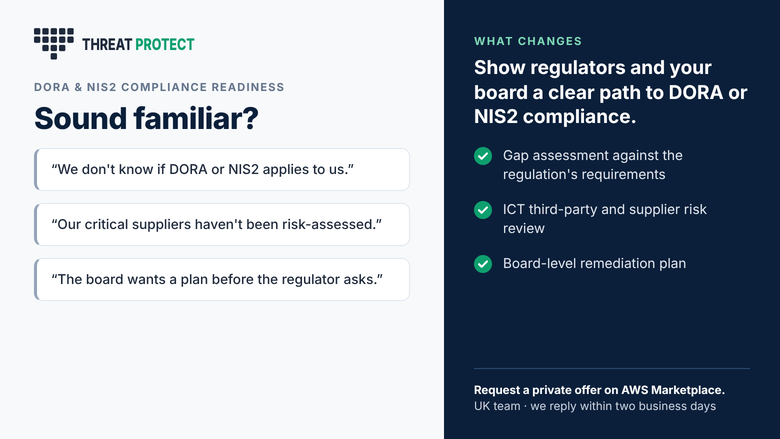
DORA and NIS2: the problems we solve
Image
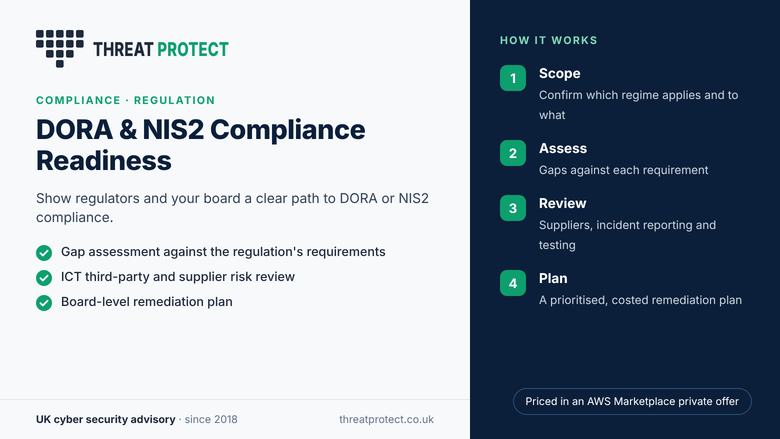
DORA and NIS2: how it works
Show regulators and your board a clear path to DORA or NIS2 compliance. Threat Protect is a UK cyber security advisory firm, founded in 2018, that helps IT and security leaders decide what to buy, renew, certify or stop, then runs it and evidences it for their auditors.
What's included
- Gap assessment against DORA or NIS2 requirements
- ICT third-party and supplier risk review
- Incident reporting and resilience testing review
- Prioritised remediation plan for the board
How it works
- Scope: confirm which regime applies and to what.
- Assess: gaps against each requirement.
- Review: suppliers, incident reporting and testing.
- Plan: a prioritised, costed remediation plan.
Who this is for
Financial entities in scope of DORA, and essential or important entities in scope of NIS2, including UK firms serving EU markets.
Why Threat Protect
- Independent: we compare products across vendors and recommend what fits your risk.
- Accountable after go-live: one point of contact for the whole service.
- Audit-ready: every control is mapped so the work doubles as evidence.
Related AWS services and AWS Marketplace products
Controls for workloads on AWS are evidenced with AWS Audit Manager and AWS Security Hub, and resilience reviewed with AWS Resilience Hub.
Getting started
Request a private offer on this page. We reply within two business days, hold a scoping call, then send an offer that sets out scope, timeline, deliverables and anything we need from you.
Pricing
Fixed price or monthly, set in a private offer.
Highlights
- Gap assessment against the regulation's requirements: a clear view of where you comply today and where you don't.
- ICT third-party and supplier risk review: the supplier oversight both regulations expect, assessed and documented.
- Board-level remediation plan: prioritised and costed, so leadership can approve the work with confidence.
Details
Sold by
Categories
Delivery method
Deployed on AWS
New
Introducing multi-product solutions
You can now purchase comprehensive solutions tailored to use cases and industries.
Pricing
Custom pricing options
Pricing is based on your specific requirements and eligibility. To get a custom quote for your needs, request a private offer.
Legal
Content disclaimer
Vendors are responsible for their product descriptions and other product content. AWS does not warrant that vendors' product descriptions or other product content are accurate, complete, reliable, current, or error-free.
Resources
Vendor resources
Support
Vendor support
Contact Threat Protect at hello@threatprotect.co.uk or on +44 20 8146 0470, or book a call at https://www.threatprotect.co.uk/contact . We respond to every enquiry within two business days, and each engagement has a named senior lead as your single point of contact.
How engagements run: after your request we hold a scoping call, then send a private offer that sets out scope, timeline, deliverables and what we need from you, such as read-only access or a named contact. A named senior lead stays with you from scoping to sign-off, and the same contact details reach the team throughout.