Sold by: Aviatrix Systems, Inc.
Deployed on AWS
Aviatrix Clearance limits each cloud workload to the paths it needs, outbound and lateral, and enforces it without breaking production. Every policy runs in monitor mode first, shows what it would block, and backs out in one action. Free until May 1, 2027, with no workload cap. From May 1, 2027, list price per workload applies automatically.
Overview
Image
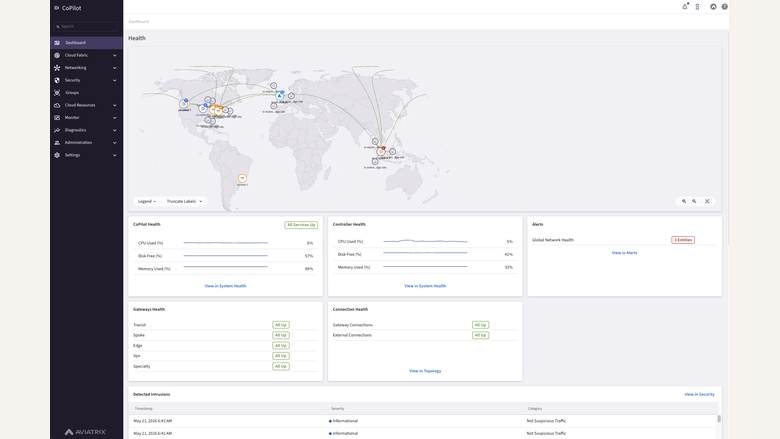
Health and operations across your entire fabric
Image
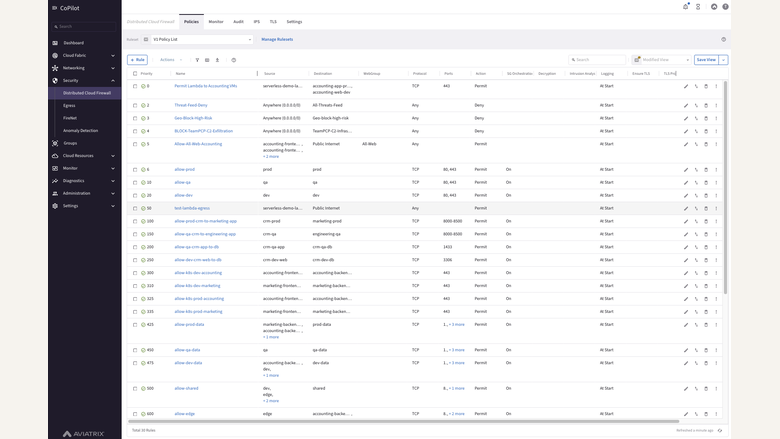
Distributed Cloud Firewall: policies and audit
Image
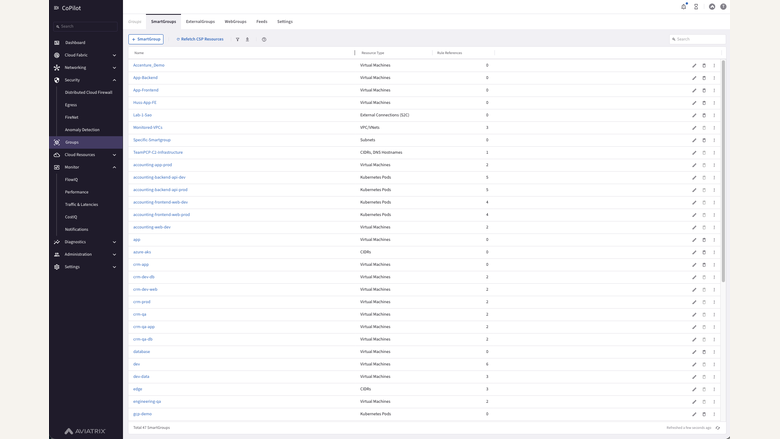
SmartGroups: identity aware policy targets
Image
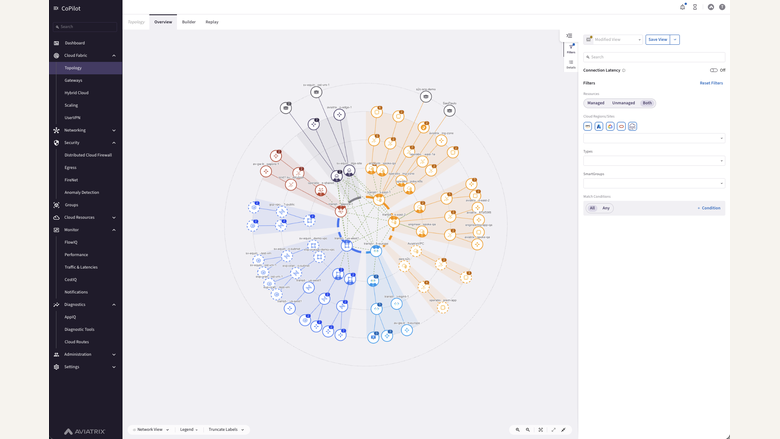
Live multicloud topology, managed and beyond

Video
Product video
Aviatrix Clearance is a new offering on the Aviatrix Containment Platform, built on the Cloud Native Security Fabric, delivered on Aviatrix Cloud and billed through AWS Marketplace. Clearance lets a security team limit each cloud workload to the paths it needs, outbound and lateral, and enforce that policy safely. Each policy runs in monitor mode first, shows what it would block before it blocks anything, and backs out in one action.
Clearance is two controls, with intrusion detection included, turned on one VPC at a time.
- Outbound Containment. A workload reaches only the outside destinations it is cleared for, named by domain rather than network address.
- Lateral Containment. On AWS, for VPCs attached to your own Transit Gateway, a workload reaches only the other workloads it is cleared for, by identity, down to a single container, serverless function, database or AI agent.
- Intrusion detection and TLS inspection are included. Intrusion detection reports known malicious traffic on the paths a workload is cleared for. It does not block traffic on its own.
Aviatrix Active Defense, the autonomous defense layer, is planned for Aviatrix Cloud and is not part of this listing.
Default deny without the outage. The control that limits damage when a patch is delayed is a default-deny policy, where a workload can connect only to what it needs. Teams delay enforcing it because a single wrong rule can take down a revenue application. Clearance runs every policy in monitor mode first, where the Shadow Rule Set evaluates it beside the live policy on real traffic and shows the connections the policy would have blocked, so teams clear the paths their applications need before enforcing. Enforcement is a single setting. Backout is a single action.
How it deploys. Clearance is delivered on Aviatrix Cloud. Aviatrix gateways run in your AWS account, in the VPCs you choose, one VPC at a time, with nothing installed on your workloads. AWS bills the gateways' compute, an estimated $78 per protected VPC per month at default sizes in us-east-1. It inserts into the network you already run, including an existing AWS Transit Gateway, and it is managed through the console.
Pricing. Aviatrix Clearance is priced per covered workload per month, with no platform fee and no fee per VPC. List prices are on the Aviatrix Clearance pricing page. Your AWS bill shows Aviatrix charges in ABUs (Aviatrix Billing Units) at $0.01 each, so $24 of usage appears as 2,400 ABUs. Annual commitments and volume pricing are available by private offer.
Begin with the free Containment Assessment at aviatrix.ai/containment-assessment. It installs nothing and returns your Blast Radius, the set of things a compromised workload can still reach, in about five minutes.
Need transit, a connection to a data center, or another cloud? Contact Aviatrix.
About Aviatrix. Aviatrix® is the network containment company. The Aviatrix Containment Platform sets what every cloud workload may reach before any attack, so a compromised workload does not become a company-wide breach. Built on the Cloud Native Security Fabric, it enforces that policy in the network, at every workload and in every cloud, with nothing to install and nothing to detect first, and encrypts the traffic it allows. It is simpler, safer, faster and less costly than the firewalls and agents it replaces. The Cloud Native Security Fabric is quantum safe. Trusted by more than 500 of the world's leading enterprises. For more information, visit aviatrix.ai.
Highlights
- Two controls, with intrusion detection included, turned on one VPC at a time. Outbound Containment, a workload reaches only the outside destinations it is cleared for, named by domain rather than network address. Lateral Containment, on AWS through your own Transit Gateway, a workload reaches only the other workloads it is cleared for, by identity, down to a container, serverless function, database or AI agent.
- Default deny without the outage. Every policy runs in monitor mode first. The Shadow Rule Set evaluates it beside your live policy on real traffic and shows every connection it would have blocked, so you clear the paths your applications need before anything is denied. Enforcement is one setting. Backout is one action. Nothing is installed on your workloads.
Details
Sold by
Categories
Delivery method
Deployed on AWS
New
Introducing multi-product solutions
You can now purchase comprehensive solutions tailored to use cases and industries.

Features and programs
Financing for AWS Marketplace purchases
AWS Marketplace now accepts line of credit payments through the PNC Vendor Finance program. This program is available to select AWS customers in the US, excluding NV, NC, ND, TN, & VT.

Pricing
Pricing is based on actual usage, with charges varying according to how much you consume. Subscriptions have no end date and may be canceled any time.
Additional AWS infrastructure costs may apply. Use the AWS Pricing Calculator to estimate your infrastructure costs.
Dimension | Description | Cost/unit |
|---|---|---|
ABU | Aviatrix Billing Unit | $0.01 |
Dimensions summary
This listing uses a single usage-based dimension billed in ABU, the Aviatrix Billing Unit. You pay based on usage measured in these units rather than a fixed subscription or per-seat charge. The product's containment capabilities are priced per workload, so your costs scale with the number of cloud workloads you protect. You can adopt the two controls and the autonomous defense layer together or in any order, and consumption determines the ABU total. There are no instance-size tiers or separate add-on dimensions here; your bill reflects the measured units you consume.
Top-of-mind questions for buyers
Pricing is measured per workload. A workload can be a virtual machine, a Kubernetes pod, a serverless function, a database, or an AI agent. Each item gets its own clearance policy. AI agent discovery and containment runs inside both controls at the agent grain, so agents count individually.
No. All usage rolls into the single ABU dimension. You can adopt the two controls and the autonomous defense layer together or in any order. Your ABU total reflects the workloads you protect across whichever controls you turn on, billed as one combined usage metric.
Because pricing is per workload measured in ABU, your usage rises as you protect more workloads and falls when you protect fewer. You can turn on containment one VPC at a time, so consumption grows with the workloads you enroll rather than a fixed upfront count.
aviatrix.ai+1
Helpful?
Vendor refund policy
Please contact support@aviatrix.com

Legal
Vendor terms and conditions
Upon subscribing to this product, you must acknowledge and agree to the terms and conditions outlined in the vendor's End User License Agreement (EULA) .
Content disclaimer
Vendors are responsible for their product descriptions and other product content. AWS does not warrant that vendors' product descriptions or other product content are accurate, complete, reliable, current, or error-free.
Delivery details
Software as a Service (SaaS)
SaaS delivers cloud-based software applications directly to customers over the internet. You can access these applications through a subscription model. You will pay recurring monthly usage fees through your AWS bill, while AWS handles deployment and infrastructure management, ensuring scalability, reliability, and seamless integration with other AWS services.
Resources
Support
Vendor support
Aviatrix Basic support is included with every subscription. Open a case on the Support Portal .
Product documentation is at https://docs.aviatrix.com/docs/cloud/getting-started .
For a private offer, annual commitment or volume pricing, contact your Aviatrix account team or salesops@aviatrix.com . To stop, cancel the subscription in AWS Marketplace and remove the Aviatrix gateways from your VPCs.
AWS infrastructure support
AWS Support is a one-on-one, fast-response support channel that is staffed 24x7x365 with experienced and technical support engineers. The service helps customers of all sizes and technical abilities to successfully utilize the products and features provided by Amazon Web Services.
Similar products

Aviatrix Enterprise provides advanced cloud networking solutions for enterprise environments.

Why just detect when you can prevent? Aviatrix's in-line managed security platform stops breaches in real-time by embedding dynamic, policy-driven control directly into the data path of all workload communication designed to enforce a zero trust posture within modern cloud environments, effectively stopping the lateral movement of attackers, preventing accidental data exfiltration from human error or misconfigurations, securing the network complexities of Kubernetes, and allows you to see, segment, and secure communications from autonomous agents and AI-generated code, often referred to as "Shadow AI."
The Aviatrix Cloud Network Controller is a tool that manages gateways, coordinates the connectivity of cloud and hybrid networks, and automates routing on a large scale. The Aviatrix Terraform Provider works with the controller to automate the setup and configuration of network infrastructure wherever it is needed by the enterprise.

The Aviatrix Cloud Network License Service provides the customer IDs (licenses) that are needed to access the Aviatrix Cloud Network Controller and Aviatrix Cloud Network CoPilot. This service also calculates Aviatrix bills based on usage, which are then sent to AWS Marketplace for customer billing purposes. Customers can view their Aviatrix bill detail in the Aviatrix Cloud Network CoPilot. This service includes a free trial.
Customer reviews
No customer reviews yet
Be the first to review this product . We've partnered with PeerSpot to gather customer feedback. You can share your experience by writing or recording a review, or scheduling a call with a PeerSpot analyst.