
Sold by: Proxylity
Deployed on AWS
Free Trial
AWS Free Tier
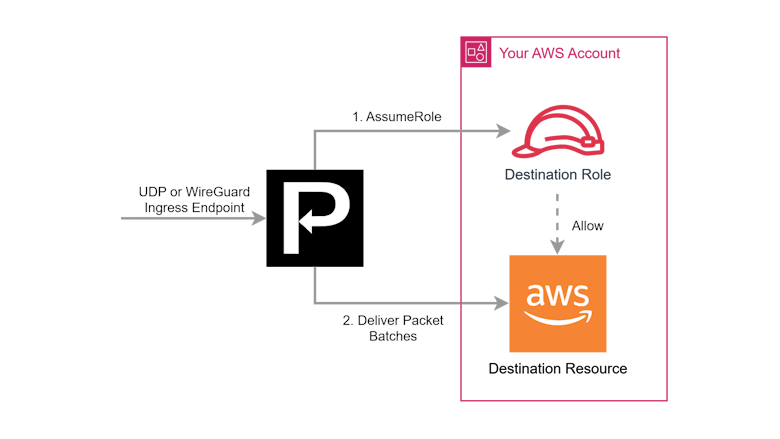
Proxylity UDP Gateway is a fully managed serverless solution that terminates UDP, DTLS and WireGuard connections and directs packet data to AWS Lambda functions, Step Functions, SNS, SQS, Kinesis, Location Service, DynamoDB, S3, CloudWatch and more AWS services.
Built for developers who need datagram protocol backends without managing servers. Our gateway eliminates the operational overhead of traditional UDP infrastructure.
Implement RADIUS authentication, syslog collection, IoT device communication, and other UDP transport based workloads with serverless scalability and pay-per-use pricing. Deploy services in minutes using infrastructure-as-code, with global low-latency routing and built-in high availability (>99.99%) across AWS regions.
Overview
Image
How UDP Gateway Works
Image
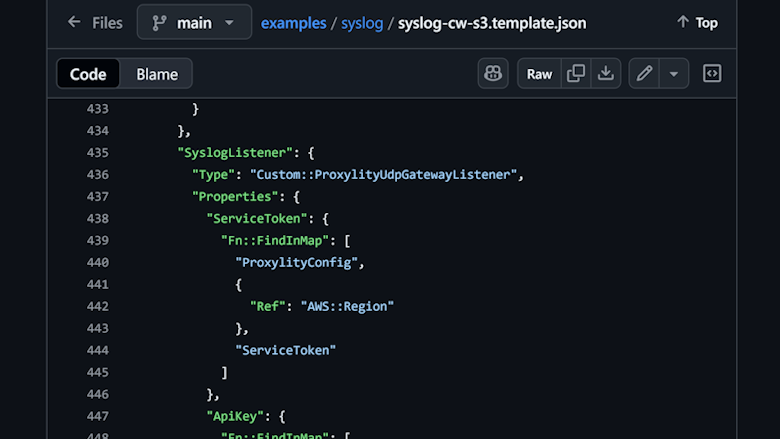
Infrastructure as Code Workflow
Image
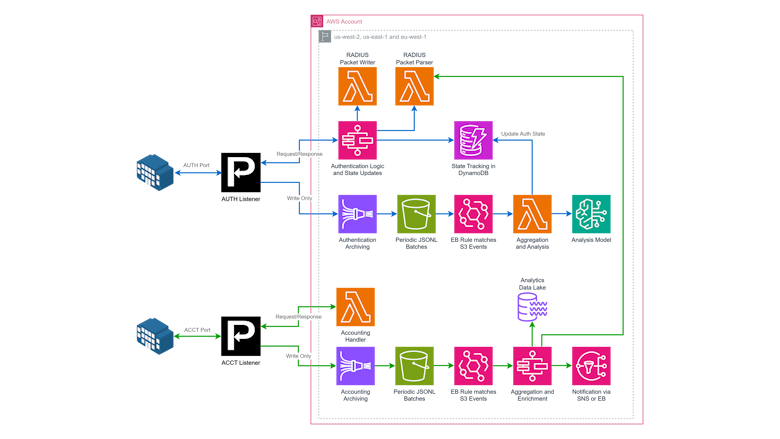
Use Case: RADIUS Authentication and Accounting
Image
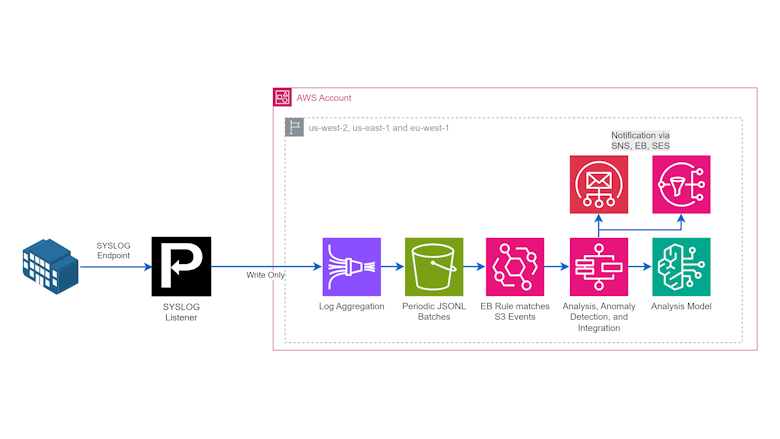
Use Case: Centralize Logging
Image
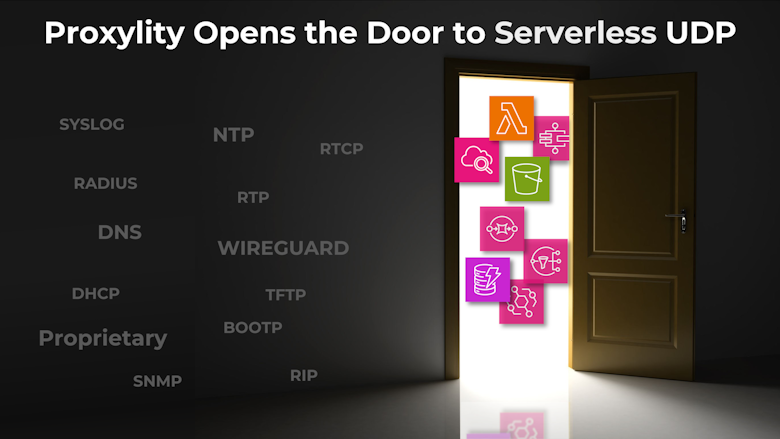
The Door is Open to Serverless UDP

Video
Product video
Proxylity UDP Gateway is a fully managed serverless solution that terminates UDP, DTLS and WireGuard connections and integrates directly with AWS Lambda, IoT Core, CloudWatch Logs, S3, DynamoDB, Step Functions, SNS, SQS, Kinesis, EventBridge, and API Gateway without managing UDP servers.
UDP Gateway eliminates backend operational overhead for IoT device connectivity, syslog collection, CoAP APIs, DNS services, network monitoring, real-time gaming, and many more protocols and use case integrations. Supports DTLS 1.2 and 1.3, and WireGuard for modern protection of data in transit.
Infrastructure-as-Code Native Design
Deploy production-ready UDP and WireGuard listeners in under 5 minutes using AWS CloudFormation or Terraform. CloudFormation templates define listeners, destinations, IAM roles, client IP restrictions, and batching policies. Official Terraform module available in HashiCorp Registry. Enables GitOps workflows and repeatable deployments.
Direct Integration with AWS Services
** AWS Lambda Integration for Flexible Data Processing **
Process UDP packets with Lambda business logic instead of managing EC2 instance fleets. Delivers packets as JSON objects with source IP, port numbers, timestamps, peer/client key and raw payloads. Lambda response streaming enables real-time protocols by sending reply packets progressively throughout execution. Supports all AWS runtimes (Node.js, Python, Java, Go, .NET). Multi-tenant isolation with dynamic tenant ID extraction using Binary Range Expressions. .NET SDK and dotnet templates available. Configurable batching reduces Lambda invocations.
AWS IoT Core Integration for Connected Devices
Bridge remote devices directly to AWS IoT Core infrastructure without protocol translation servers. Dynamic topic routing publishes to unique MQTT topics based on device identifiers extracted from datagram payloads, enabling per-device subscriptions, Thing Shadow updates, and Rules Engine integration. Static mode wraps packets in JSON; dynamic mode preserves raw binary payloads. Ideal for industrial sensors, cellular gateways, energy management, connected vehicles, and legacy modernization.
Centralized Syslog Collection and Security Logging
Replace syslog servers with direct CloudWatch Logs integration. Publishes syslog messages (RFC3164, RFC5424, RFC6587) to CloudWatch log groups. Composite destinations route logs to CloudWatch for monitoring with metric filters and alarms, S3 via Firehose for compliance archival (SOC 2, PCI-DSS, HIPAA, FedRAMP), and Lambda for security event processing to AWS Security Hub. Integrates with SIEM platforms (Splunk, Sumo Logic, Datadog) via CloudWatch subscriptions.
*Expansive AWS Service Integrations
- AWS Lambda: Request/response and streaming, tenant isolation
- Step Functions: EXPRESS or STANDARD workflow orchestration
- API Gateway: Third-party HTTP/HTTPS webhook integration
- EventBridge: Event-driven routing patterns
- SQS: Standard and FIFO queues with dynamic message group IDs
- SNS: Fan-out notification patterns
- DynamoDB: Real-time storage with dynamic attribute mapping
- S3: Direct object storage for archival
- Kinesis Data Streams: Real-time streaming with partition keys
- Kinesis Data Firehose: High-volume delivery to S3, Redshift, OpenSearch
- CloudWatch Logs: Centralized logging
- Location Service: Fleet, package and cold chain tracking
- AWS IoT Core: MQTT topic publishing
Security and Compliance
Zero-trust architecture with IAM role assumption. Client IP restrictions using CIDR notation. All API calls auditable via CloudTrail. Encryption at rest. Compliance-ready for SOC 2, PCI-DSS, HIPAA, FedRAMP with S3 Object Lock. Multi-region deployment supports data residency and GDPR.
Common Use Cases
RADIUS authentication with Lambda querying DynamoDB or RDS. IoT connectivity bridging CoAP to AWS IoT Core. Syslog routing to CloudWatch and Security Hub. DNS filtering with Lambda. Real-time gaming with DynamoDB. SNMP trap collection. Legacy modernization without firmware changes.
Transparent Pricing and Free Tier
1 million packets free monthly. Pay only for delivered traffic with no minimums or contracts. Pricing: $1.25 per million (1-100M) to $0.60 (1T+). Port-hours: $0.00139/hour. Compatible with AWS credits. Batching reduces API calls by 90%. Automatic scaling to zero, no idle costs.
Deploy in under 5 minutes at proxylity.com/docs. Free trial available through AWS Marketplace.
Highlights
- Global, high availability architecture delivers UDP, DTLS and WireGuard traffic to AWS Lambda, Step Functions, SNS, SQS, DynamoDB, and S3 with tunable latency. Deploy in multiple AWS regions for compliance and performance, with automatic high availability and failover.
- Simple, transparent usage-based pricing with 1 million packets free per month. Pay only for actual traffic processed. No minimum fees, long-term contracts, or infrastructure costs. Includes generous free tier for development and testing.
- Deploy services seamlessly using infrastructure-as-code (Terraform, CloudFormation). Eliminate server maintenance, patching, and scaling concerns. Focus on business logic while we handle network protocols, security, and global infrastructure management.
Details
Sold by
Delivery method
Deployed on AWS
New
Introducing multi-product solutions
You can now purchase comprehensive solutions tailored to use cases and industries.

Features and programs
Financing for AWS Marketplace purchases
AWS Marketplace now accepts line of credit payments through the PNC Vendor Finance program. This program is available to select AWS customers in the US, excluding NV, NC, ND, TN, & VT.

Pricing
Free trial
Try this product free according to the free trial terms set by the vendor.
Pricing is based on actual usage, with charges varying according to how much you consume. Subscriptions have no end date and may be canceled any time.
Additional AWS infrastructure costs may apply. Use the AWS Pricing Calculator to estimate your infrastructure costs.
Dimension | Description | Cost/unit |
|---|---|---|
First 1M Packets | 0-1M Packets (Free Tier) | $0.00 |
Next 99M Packets | 1-100M Packets (per million) | $1.25 |
Next 900M Packets | 100M-1B Packets (per million) | $1.12 |
Next 10,000M Packets | 1B-10B Packets (per million) | $0.99 |
Next 90,000M Packets | 10B-100B Packets (per million) | $0.86 |
Next 900,00M Packets | 100B-1T Packets (per million) | $0.73 |
Above 1T Packets | > 1T Packets (per million) | $0.60 |
UDP Listener | per port-hour | $0.00139 |
Free UDP Listener | Included in Subscription or Free Tier | $0.00 |
Dimensions summary
You pay for two things: packets delivered and listener port-hours. Packet pricing uses progressive tiers by monthly volume. The first million packets each month are free. Beyond that, packets are billed per million across seven volume bands, and the per-million rate steps down as your monthly volume climbs. Only packets within each band pay that band's rate. For listeners, your first listener is included free in the subscription or free tier. Each additional listener is billed per port-hour, whether or not it receives traffic.
Top-of-mind questions for buyers
Both inbound datagrams delivered to your destinations and replies sent back to clients count. A receive-only protocol pays for inbound only. Each inbound packet counts once per destination on the listener. Packets up to 1 KB count as one; larger packets count by size, rounded up. Blocked or filtered traffic is never charged.
Your first listener is included free. Each additional listener is billed per port-hour whether or not it receives traffic. Hours are not pro-rated, so any part of an hour is a full hour. Deleting a listener stops charges after the current hour ends.
No. Tiers are progressive, so only the packets within each band pay that band's rate. Crossing into a higher band does not reprice packets already counted in lower bands. The transition happens automatically as your monthly volume grows, with no upgrade step required.
proxylity.com
Helpful?
Vendor refund policy
Refunds will not be provided for past usage. Credits may be applied at discretion of our team. To discuss a credit request, please contact your service representative or reach out to billing@proxylity.com .

Legal
Vendor terms and conditions
Upon subscribing to this product, you must acknowledge and agree to the terms and conditions outlined in the vendor's End User License Agreement (EULA) .
Content disclaimer
Vendors are responsible for their product descriptions and other product content. AWS does not warrant that vendors' product descriptions or other product content are accurate, complete, reliable, current, or error-free.
Delivery details
Software as a Service (SaaS)
SaaS delivers cloud-based software applications directly to customers over the internet. You can access these applications through a subscription model. You will pay recurring monthly usage fees through your AWS bill, while AWS handles deployment and infrastructure management, ensuring scalability, reliability, and seamless integration with other AWS services.
Resources
Vendor resources
Support
Vendor support
Questions about Proxylity or UDP Gateway? Reach out to support@proxylity.com or visit the website at
AWS infrastructure support
AWS Support is a one-on-one, fast-response support channel that is staffed 24x7x365 with experienced and technical support engineers. The service helps customers of all sizes and technical abilities to successfully utilize the products and features provided by Amazon Web Services.
Similar products
Secure WireGuard VPN Gateway on Ubuntu with automatic first-boot configuration, encrypted VPN tunnels, easy client provisioning, QR code generation, and support from Meyi Cloud for fast and reliable remote access.
The product has charges associated with it for support, maintenance, and pre-configuration to be instantaneously deployed on AWS Marketplace with all security and enterprise standards. The WireGuard VPN Server on Ubuntu 22.04 LTS offers a cost-effective, scalable, and secure solution.
WireGuard VPN Server on Debian for Internet access for computers and mobile devices. Additionally, it contains a Pi-Hole proxy DNS server that blocks advertising DNS requests. Thus, this VPN server allows clients to surf the web and significantly reduce the amount of advertising displayed. It is easy to use: after launching, it is immediately fully operational without the need for any setup. WireGuard technology is quite modern; it offers data transfer speeds through VPN tunnels that are higher than those using IKEv2 and significantly higher than the OpenVPN protocol. This server provides a stable VPN connection at the highest possible speed. The server has a convenient and intuitive web control panel. Suitable for both individual users and companies offering VPN services.
AppGate ZTNA, an industry-leading Zero Trust Network Access (ZTNA) solution, puts your people first with simple, fast, secure connections to multi-cloud, on-prem, or legacy applications - from anywhere. AppGate ZTNA is a cloud-native, unified, API-enabled solution which delivers valuable security, efficiency and user experience benefits. Each user has a one-to-one encrypted network segment to each location where resources have been explicitly granted. Developers enjoy concurrent and automated access to multiple, disparate environments without waiting for manual access approvals. Admins can easily ensure that users have access to necessary resources, regardless of physical location or virtual segmentation.
Customer reviews
No customer reviews yet
Be the first to review this product . We've partnered with PeerSpot to gather customer feedback. You can share your experience by writing or recording a review, or scheduling a call with a PeerSpot analyst.