Sold by: ChangeGuard AI
Deployed on AWS
Free Trial
AWS Free Tier
Should this production change happen? ChangeGuard AI answers before anything runs. It judges each proposed change to your Amazon EKS environments against live state and returns SHIP, HOLD or BLOCK with the reasons and evidence. If you grant execution authority, an approved change runs only under a single-use Permit signed in AWS KMS, the Executor performs only that action, and ChangeGuard marks the result VERIFIED only when fresh evidence confirms it. Built for platform engineering and SRE teams whose changes come from engineers, CI/CD pipelines, GitOps and AI agents. Read-only by default, with nothing installed in your clusters for the standard path. Available through AWS Marketplace and successfully passed the AWS Foundational Technical Review. Start a 14-day free trial to evaluate ChangeGuard on up to 10 EKS environments before purchasing.
Overview
Video
ChangeGuard product demo (3 minutes)
Image
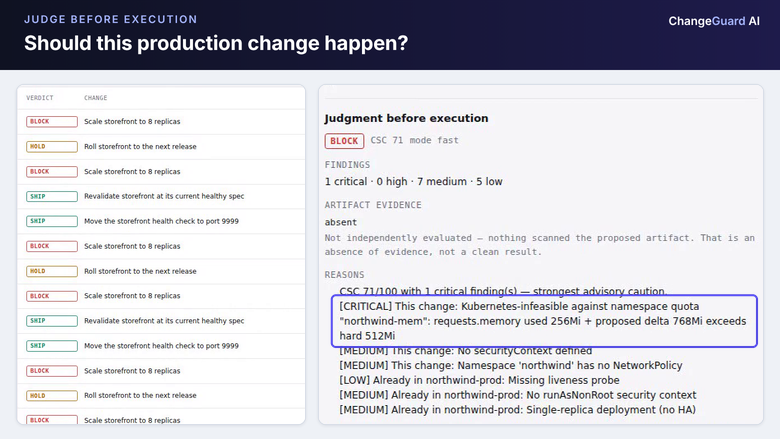
SHIP, HOLD or BLOCK before execution
Image
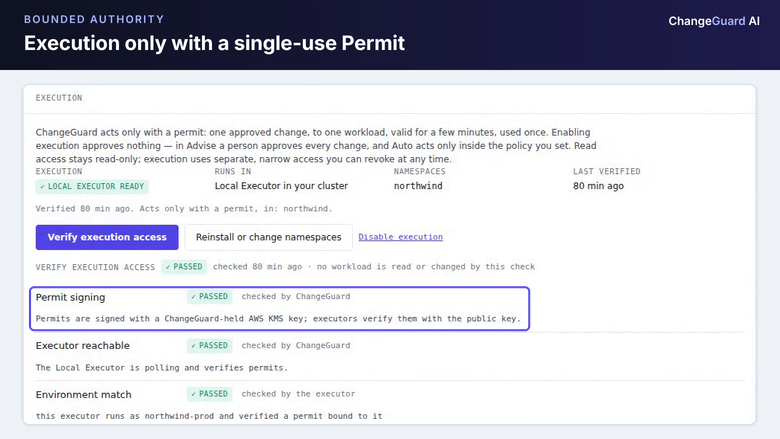
Permit: bounded execution authority
Image
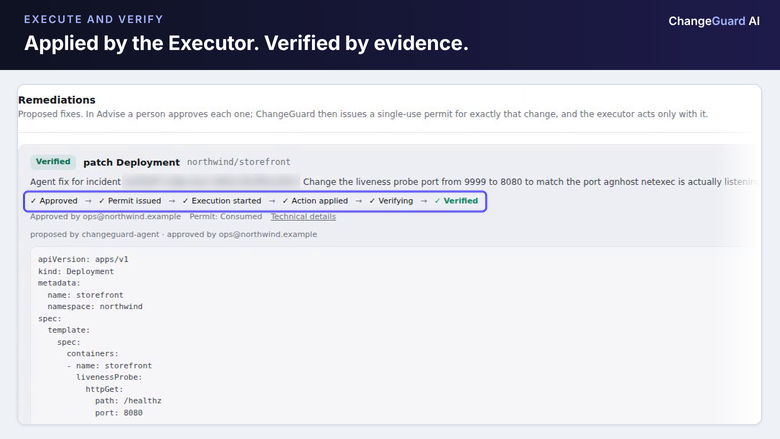
Applied by the Executor, then VERIFIED
Image
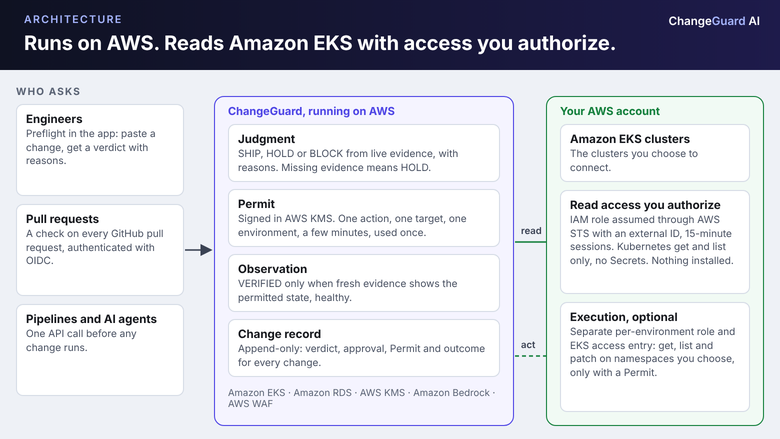
Architecture on AWS and Amazon EKS
Image
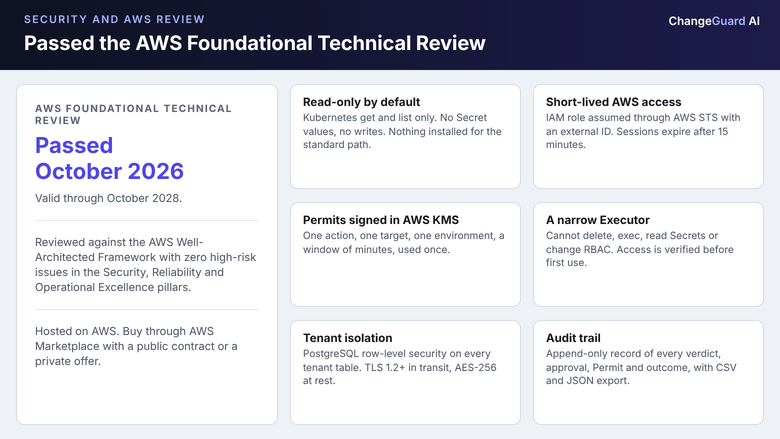
Passed the AWS Foundational Technical Review
Should this production change happen?
AI agents, CI/CD pipelines and GitOps controllers now change production faster than people can review each change. IAM and RBAC decide who may act. Linters and admission policies check whether a manifest is valid. ChangeGuard AI answers the question in between: should this exact change happen in this environment, right now?
How it works
- Judge. Every proposed change is checked against the live state of the target Amazon EKS environment (what is running, quotas, health and history) and gets SHIP, HOLD or BLOCK with the reasons and evidence. When evidence is missing or stale, the verdict is HOLD and the reason says so. ChangeGuard never guesses.
- Permit. If you grant execution authority, an approved change runs only under a Permit signed in AWS KMS: one action, one target, one environment, valid for minutes and used once. Advise mode, the default, waits for a person to approve each change. Auto mode acts only inside a policy you write.
- Execute. The Executor performs only the permitted action, through a separate per-environment identity limited to get, list and patch on the namespaces you choose. It cannot delete, create, exec into pods, read Secrets or change RBAC.
- Verify. ChangeGuard watches the environment and marks the change VERIFIED only when fresh evidence shows the permitted state, healthy. Every verdict, approval, Permit and outcome is kept in an append-only change record.
Who it is for
Platform engineering, SRE and DevOps teams running Amazon EKS who want every production change, whether it comes from an engineer, a pipeline or an AI agent, judged against what is actually running before it ships.
Where it fits
- Preflight in the app: paste a change and get a verdict in seconds
- A check on every GitHub pull request, authenticated with GitHub OIDC, with no secret to paste
- One API call from any pipeline or AI agent
- Argo CD and Flux sync gates
Getting started after you subscribe
- Subscribe in AWS Marketplace and choose Set up your account. You land in ChangeGuard, sign in or create your workspace, and your subscription is applied to it.
- In AWS Account Center, add your AWS account by creating one IAM role from the template ChangeGuard shows you (CloudFormation, Terraform or AWS CLI). The role can only list and describe EKS clusters, and only ChangeGuard can assume it, with your unique external ID.
- Verify the connection and discover your EKS clusters.
- Select the environments to connect and apply the generated read-only access (an EKS access entry with get and list, no Secrets) with your own credentials.
- Within about a minute the environment reads Ready. Run your first judgment in Preflight or on a pull request.
- Optional: enable execution for an environment with the Cloud Executor (nothing installed) and choose Advise or Auto.
ChangeGuard Edge, an optional in-cluster collector, adds runtime and node evidence where local presence is needed. It is never required for judgment or execution.
Security
- Read-only by default, with nothing installed in your clusters for the standard path
- AWS sessions created per operation through AWS STS with an external ID, expiring after 15 minutes; no long-lived customer keys are stored
- Tenant isolation enforced with PostgreSQL row-level security
- TLS 1.2 or higher in transit and AES-256 at rest
- Hosted on AWS: Amazon EKS, Amazon RDS, AWS KMS, Amazon Bedrock and AWS WAF
- Successfully passed the AWS Foundational Technical Review in October 2026
- Security documentation: https://docs.changeguard.ai/security/architecture
Evaluate and buy
- 14-day free trial: evaluate ChangeGuard on up to 10 EKS environments before purchasing. The trial ends after 14 days and does not become a paid subscription, and execution stays off unless you set it up.
- Watch the 3-minute product demo: https://demo.changeguard.ai
- Book a live demo: https://calendly.com/changeguard-sales/30min
- Start free at https://app.changeguard.ai with Preflight, pull request verdicts and the API, with nothing connected. Connecting live environments is part of the paid plan.
- Public offer: 12-month contract for Enterprise, up to 10 connected environments, production or non-production
- Private offers for custom terms, multi-year contracts or more environments: kristopher.white@changeguard.ai
- Support: support@changeguard.ai , Monday to Friday, 09:00 to 18:00 US Eastern Time, with emergency escalation for critical issues
Highlights
- Judge before execution: every proposed change, from an engineer, a CI/CD pipeline, a GitOps controller or an AI agent, is judged against the live state of your Amazon EKS environment and gets SHIP, HOLD or BLOCK with the reasons and evidence, in Preflight, on every GitHub pull request or through one API call. Missing or stale evidence returns HOLD, never a guess.
- Safely execute approved fixes, then verify: an approved change runs only under a single-use Permit signed in AWS KMS, bound to one action, one target and one environment for a few minutes. The Executor performs only that action, with no delete, exec, Secret or RBAC rights, and ChangeGuard marks it VERIFIED only when fresh evidence confirms the result. Advise by default; Auto only inside a policy you write.
- Built for AWS, ready for procurement: available through AWS Marketplace and successfully passed the AWS Foundational Technical Review. Runs on AWS and connects to Amazon EKS with read-only access you authorize, with nothing installed for the standard path. Evaluate ChangeGuard on up to 10 EKS environments before purchasing with a 14-day free trial, then buy the public 12-month contract or request a private offer for custom terms, multi-year contracts or more environments.
Details
Sold by
Delivery method
Deployed on AWS
New
Introducing multi-product solutions
You can now purchase comprehensive solutions tailored to use cases and industries.
Features and programs
Financing for AWS Marketplace purchases
AWS Marketplace now accepts line of credit payments through the PNC Vendor Finance program. This program is available to select AWS customers in the US, excluding NV, NC, ND, TN, & VT.

Pricing
Free trial
Try this product free according to the free trial terms set by the vendor.
Pricing is based on the duration and terms of your contract with the vendor. This entitles you to a specified quantity of use for the contract duration. If you choose not to renew or replace your contract before it ends, access to these entitlements will expire.
Additional AWS infrastructure costs may apply. Use the AWS Pricing Calculator to estimate your infrastructure costs.
Dimension | Description | Cost/12 months |
|---|---|---|
Enterprise, up to 10 connected environments | Annual subscription covering up to 10 connected environments, production or non-production (for example QA or preprod): SHIP, HOLD or BLOCK judgment, Permit-governed execution with the Cloud or Local Executor, verified outcomes and the audit trail. For more environments or custom terms, request a private offer. | $120,000.00 |
Dimensions summary
This listing offers one pricing option: an Enterprise annual subscription. You pay a yearly fee covering up to 10 connected environments. These can be production or non-production, such as QA or preprod. The subscription includes SHIP, HOLD, or BLOCK judgment on changes, Permit-governed execution through the Cloud or Local Executor, verified outcomes, and an audit trail. Pricing does not scale by usage within this tier; the environment count is the main boundary. If you need more than 10 environments or custom terms, you request a private offer instead.
Top-of-mind questions for buyers
A connected environment is one Kubernetes cluster you authorize ChangeGuard to read. The same cluster seen by both Fleet and Edge resolves to one canonical identity, not two. Each environment can be production or non-production, such as QA or preprod. You can connect up to 10 under this subscription.
No. This is a flat annual subscription. The fee covers judgment, Permit-governed execution, verified outcomes, and the audit trail across up to 10 environments. Volume of changes, pull requests, or executions does not add charges. The environment count is the boundary, not usage within it.
The subscription covers up to 10 environments. For more environments or custom terms, you request a private offer rather than adding capacity automatically. The 10-environment count is the boundary of this tier, so going beyond it requires a separate arrangement with the vendor.
changeguard.ai
Helpful?
Vendor refund policy
ChangeGuard AI reviews refund requests case by case. To request a refund, email support@changeguard.ai with your AWS account ID and AWS Marketplace agreement ID and the reason for the request. Approved refunds are issued through AWS Marketplace.
Legal
Vendor terms and conditions
Upon subscribing to this product, you must acknowledge and agree to the terms and conditions outlined in the vendor's End User License Agreement (EULA) .
Content disclaimer
Vendors are responsible for their product descriptions and other product content. AWS does not warrant that vendors' product descriptions or other product content are accurate, complete, reliable, current, or error-free.
Delivery details
Software as a Service (SaaS)
SaaS delivers cloud-based software applications directly to customers over the internet. You can access these applications through a subscription model. You will pay recurring monthly usage fees through your AWS bill, while AWS handles deployment and infrastructure management, ensuring scalability, reliability, and seamless integration with other AWS services.
Support
Vendor support
Vendor support is by email, and every message is answered by a person.
Contact
- Product, billing, access and AWS Marketplace setup: support@changeguard.ai
- Suspected vulnerabilities or security incidents: security@changeguard.ai
- Private offers and enterprise terms: kristopher.white@changeguard.ai
Hours: Monday to Friday, 09:00 to 18:00 US Eastern Time, excluding US public holidays.
First-response targets (targets, not contractual service levels unless your agreement sets them)
- Critical (ChangeGuard unavailable, a suspected security issue, or an Executor acting unexpectedly): 1 hour during business hours, with updates every 2 hours while active
- High (a major feature degraded with no workaround): 4 business hours
- Normal (a workaround exists, or a question is blocking onboarding): 1 business day
- Low (general questions and feature requests): 3 business days
Emergency escalation: outside business hours, ChangeGuard production alerts and email to security@changeguard.ai reach the founder's phone at any hour, and Critical issues are handled best effort, typically within a few hours. ChangeGuard does not offer 24x7 staffed support, phone or chat.
Planned changes with customer-visible effect are announced at least 3 business days ahead.
Resources
- Product demo (3 minutes): https://demo.changeguard.ai
- Book a live demo: https://calendly.com/changeguard-sales/30min
- Documentation: https://docs.changeguard.ai
Setup guides, security details and the API reference are in the documentation.
AWS infrastructure support
AWS Support is a one-on-one, fast-response support channel that is staffed 24x7x365 with experienced and technical support engineers. The service helps customers of all sizes and technical abilities to successfully utilize the products and features provided by Amazon Web Services.
Similar products
The AI Runtime Security Discovery Workshop is a structured engagement designed to help organizations identify and prioritize security risks in AI-powered applications, including LLM, RAG, and agent-based architectures. It provides threat modelling, control gap analysis, and mapping of runtime protection capabilities such as Lakera to real-world use cases. The result is a clear, low-risk pathway to implementing AI runtime security through a defined pilot and adoption plan.
The Lakera Implementation Accelerator is a structured engagement designed to help organizations deploy and operationalize AI runtime protection across LLM, RAG, and agent-based applications. It enables integration of Lakera with application architectures, APIs, and infrastructure while configuring runtime security policies and observability. The result is a controlled, low-risk path from pilot to production-ready AI security.
PointGuard AI's integration with AWS AI (Bedrock, SageMaker) significantly enhances the security and governance of AI applications built on AWS AI (Bedrock, SageMaker). PointGuard AI's solutions provide guardrails and policy enforcement across the entire AI lifecycle, from data ingestion to model deployment. By combining AWS AI's powerful data processing capabilities with PointGuard AI's robust security measures, organizations can accelerate their AI initiatives while maintaining a strong security posture, ensuring that sensitive data and AI models are protected from evolving threats.

An exec‑ready, architecture‑anchored threat modelling engagement that evaluates Kubernetes and EKS security posture across clusters, delivering mapped threats, trust boundaries, and prioritised technical recommendations to harden environments, and guide security roadmaps.
Customer reviews
No customer reviews yet
Be the first to review this product . We've partnered with PeerSpot to gather customer feedback. You can share your experience by writing or recording a review, or scheduling a call with a PeerSpot analyst.