Sold by: CoreNova Intelligence Limited
Deployed on AWS
CoreNova SSM EKS Admin Bastion AMI (Amazon Linux 2023, Graviton ARM64): private Amazon EKS administration bastion for teams replacing public SSH jump hosts. Includes AWS CLI v2, Session Manager Plugin, kubectl version selector, Helm, eksctl, k9s, IAM examples, and AL2023 hardening.
Overview
Image
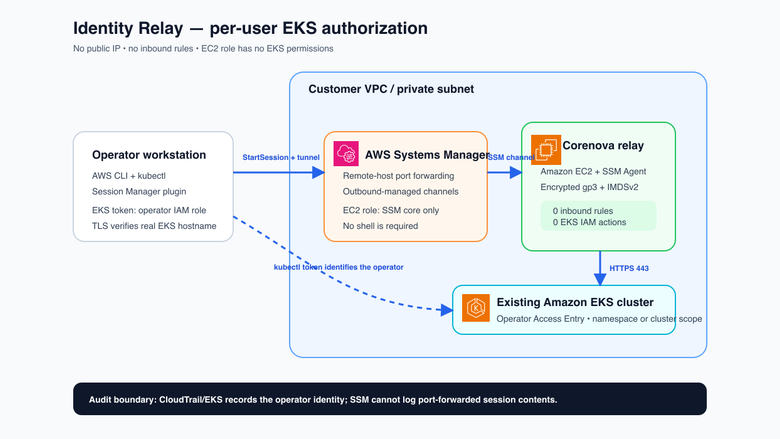
Identity Relay architecture
Image
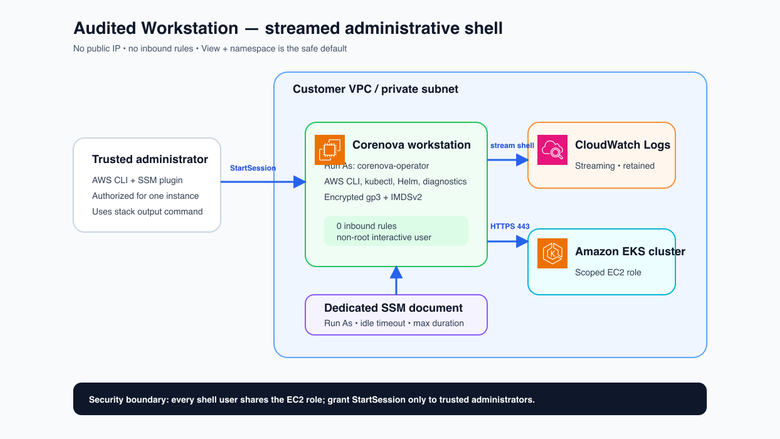
Audited Workstation architecture
Deploy CoreNova SSM EKS Admin Bastion AMI (Amazon Linux 2023, Graviton ARM64) as a private administration host for Amazon EKS.
CoreNova SSM EKS Admin Bastion is a private, SSM-first Amazon EKS administration workstation packaged as an Amazon Machine Image. It gives platform engineers, DevOps teams, MSPs, and startup CTOs a controlled EC2 host for kubectl, Helm, eksctl, and k9s without building or maintaining a public SSH jump box.
This is an administration and bastion AMI, not an EKS worker node image. Use it to operate existing or newly created EKS clusters from a private subnet with IAM and Kubernetes RBAC controlled by the buyer.
What you get
- Amazon Linux 2023 hardened base maintained by CoreNova
- SSM-first access model with Amazon SSM Agent and Session Manager Plugin
- SSH key-only fallback with root login and password authentication disabled
- AWS CLI v2 and kubectl multi-version selector for supported EKS minor versions
- Helm, eksctl, k9s, kubectx, kubens, jq, yq, git, tmux, and troubleshooting utilities
- EKS Access Entry example and least-privilege IAM policy templates
- Tool inventory at /etc/corenova/eks-admin-bastion/tool-versions.txt
- Quickstart and examples under /opt/corenova/eks
Best for
- Private EKS administration from a controlled EC2 instance
- Replacing public SSH bastion hosts with Session Manager access
- Standardized kubectl and Helm workstation for platform teams
- MSP or consultant access host in customer AWS accounts
- Security-conscious EKS troubleshooting and cluster inspection
Recommended deployment model
Launch into a private subnet, attach an IAM role with AmazonSSMManagedInstanceCore and your required EKS access policy, and connect with AWS Systems Manager Session Manager. Do not open inbound SSH unless your organization explicitly requires SSH fallback.
Security model
The AMI ships without hardcoded passwords, private keys, AWS credentials, kubeconfigs, or customer data. Buyers control IAM permissions, EKS Access Entries, Kubernetes RBAC, network access, logging retention, and secrets handling in their own AWS accounts.
Architecture and pricing
ARM64 / Graviton. Recommended instance type: t4g.small.
Software fee: $0.04/hour for supported EC2 instance types. This product has charges associated with CoreNova packaging, maintenance, documentation, and seller support. AWS infrastructure costs such as EC2, EBS, NAT gateway, VPC endpoints, public IPv4, and data transfer are billed separately by AWS.
Related CoreNova listings
- Amazon Linux 2023 Hardened AMI: https://aws.amazon.com/marketplace/pp/prodview-gricbzzlztsae
- Full CoreNova AWS Marketplace catalog: https://aws.amazon.com/marketplace/seller-profile?id=seller-kbf3ztbtbdc5o
Support: support@corenovacloud.com
Highlights
- Private SSM-first EKS admin bastion for kubectl, Helm, eksctl, and k9s; no public SSH required in the recommended deployment.
- Amazon Linux 2023 baseline with SSH key-only fallback, root/password login disabled, logging, time sync, and tool inventory.
- Includes EKS Access Entry guidance, least-privilege IAM examples, Session Manager checks, and operator quickstart files.
Details
Categories
Delivery method
Delivery option
Identity Relay - per-user AWS identity
Audited Workstation - streamed shell logs
64-bit (Arm) Amazon Machine Image (AMI)
Latest version
Operating system
AmazonLinux Amazon Linux 2023
Deployed on AWS
New
Introducing multi-product solutions
You can now purchase comprehensive solutions tailored to use cases and industries.
Features and programs
Financing for AWS Marketplace purchases
AWS Marketplace now accepts line of credit payments through the PNC Vendor Finance program. This program is available to select AWS customers in the US, excluding NV, NC, ND, TN, & VT.

Pricing
Pricing is based on actual usage, with charges varying according to how much you consume. Subscriptions have no end date and may be canceled any time.
Additional AWS infrastructure costs may apply. Use the AWS Pricing Calculator to estimate your infrastructure costs.
Dimension | Cost/hour |
|---|---|
t4g.small Recommended | $0.02 |
t4g.micro | $0.02 |
t4g.medium | $0.02 |
t4g.large | $0.02 |
t4g.xlarge | $0.02 |
m6g.medium | $0.02 |
m6g.large | $0.02 |
m6g.xlarge | $0.02 |
m7g.medium | $0.02 |
m7g.large | $0.02 |
Dimensions summary
You pay an hourly software fee for each running instance, billed by the hour. The 17 dimensions map to Graviton ARM64 instance sizes across three EC2 families: t4g burstable, m6g and m7g balanced compute, and c6g and c7g compute-focused. Within each family, sizes step up from medium through xlarge (plus micro and small for t4g). Larger sizes give more CPU and memory. You pick the instance size that fits your workload; the hourly rate reflects that choice. AWS infrastructure charges like EC2, EBS, and networking are billed separately by AWS.
Top-of-mind questions for buyers
The hourly fee covers the management host software running on your chosen instance. AWS bills EC2, EBS storage, NAT Gateway, VPC endpoints, and data transfer separately. You pay both the software fee and the underlying AWS infrastructure charges for each running instance.
The software fee meters per running instance per hour. A stopped instance does not accrue the software fee. Stopped instances may still incur AWS storage charges for attached EBS volumes, but those are billed by AWS, not as the software fee.
Each dimension maps to a Graviton ARM64 instance size and family. Pick t4g for light, bursty admin sessions. Choose m6g or m7g for balanced CPU and memory. Choose c6g or c7g when your tasks need more compute. The hourly rate follows the instance size you select.
www.corenovacloud.com
Helpful?
Vendor refund policy
30-day refund on Marketplace software fees for verified technical issues. AWS infrastructure charges are billed by AWS and are not refundable by the seller.
Legal
Vendor terms and conditions
Upon subscribing to this product, you must acknowledge and agree to the terms and conditions outlined in the vendor's End User License Agreement (EULA) .
Content disclaimer
Vendors are responsible for their product descriptions and other product content. AWS does not warrant that vendors' product descriptions or other product content are accurate, complete, reliable, current, or error-free.
Delivery details
64-bit (Arm) Amazon Machine Image (AMI)
Amazon Machine Image (AMI)
An AMI is a virtual image that provides the information required to launch an instance. Amazon EC2 (Elastic Compute Cloud) instances are virtual servers on which you can run your applications and workloads, offering varying combinations of CPU, memory, storage, and networking resources. You can launch as many instances from as many different AMIs as you need.
Version release notes
CoreNova SSM EKS Admin Bastion AMI (Amazon Linux 2023, Graviton ARM64)
Version: v20260910
This release adds the Identity Relay and Audited Workstation deployment modes while retaining the standalone AMI delivery option for compatibility.
Baseline:
- Amazon Linux 2023 hardened base with current upstream security updates at build time.
- SSH key-only access, root login disabled, auditd, rsyslog, chrony, firewalld, and AIDE baseline.
- Amazon SSM Agent enabled for Session Manager access.
- Non-root corenova-operator Run As account and read-only corenova-eks-doctor diagnostics.
- EKS administration tools installed: AWS CLI v2, kubectl multi-version selector, Helm, eksctl, k9s, kubectx, kubens, jq, and yq.
- EKS helper scripts and starter IAM / Access Entry examples installed under /opt/corenova/eks; buyers must review and scope them.
- Cloud-init cleaned before image capture.
- Marketplace checks require unencrypted EBS snapshots and no existing product codes.
Architecture: arm64 Storage layout: root-xfs Filesystem: xfs Source AMI: ami-0a157bd98d97a9589 (us-east-1) AMI: ami-0e82526311527a78e (us-east-1)
Security note: Identity Relay keeps EKS authorization on each operator identity. Audited Workstation streams standard shell sessions to CloudWatch Logs but uses a shared EC2 role. Session Manager cannot log port-forwarded session contents. Keep inbound SSH closed unless your organization explicitly requires fallback.
Additional details
Usage instructions
Overview
CoreNova SSM EKS Admin Bastion AMI (Amazon Linux 2023, Graviton ARM64) is an Amazon Linux 2023 EKS administration bastion AMI built by CoreNova Intelligence Limited.
Recommended instance type: t4g.small. AMI: ami-0e82526311527a78e (us-east-1).
Recommended launch model
For versions that display CloudFormation delivery options in AWS Marketplace, choose Identity Relay for per-user EKS authorization or Audited Workstation for a streamed administrative shell. AWS Marketplace opens CloudFormation directly.
For the standalone AMI compatibility path:
- Subscribe in AWS Marketplace, then launch in the supported Region.
- Place the instance in a private subnet where it can reach AWS APIs.
- Attach AmazonSSMManagedInstanceCore and only reviewed, scoped EKS permissions.
- Keep inbound SSH closed and use AWS Systems Manager Session Manager.
- Review AWS infrastructure, logging, networking, and software charges.
First connection with Session Manager
Install AWS CLI v2 and the Session Manager plugin on the operator workstation.
aws ssm start-session --target YOUR_INSTANCE_ID
Optional SSH fallback
The standalone launcher requires a security-group recommendation, limited here to private RFC1918 sources. Remove inbound TCP 22 when using Session Manager. If SSH fallback is required, select a key pair and allow only trusted admin CIDRs.
ssh -i your-key.pem ec2-user@YOUR_PRIVATE_IP
EKS setup
aws eks update-kubeconfig --region YOUR_REGION --name YOUR_CLUSTER_NAME kubectl auth can-i get pods --namespace YOUR_NAMESPACE kubectl get pods --namespace YOUR_NAMESPACE corenova-eks-check corenova-eks-doctor --cluster YOUR_CLUSTER_NAME --region YOUR_REGION
Installed tools
AWS CLI v2, SSM Agent, multiple kubectl clients, Helm, eksctl, k9s, kubectx, kubens, jq, yq, git, tmux, and troubleshooting utilities are included. Review and scope the IAM and EKS Access Entry examples under /opt/corenova/eks.
Post-launch local diagnostics
systemctl is-active amazon-ssm-agent systemctl is-active rsyslog systemctl is-active chronyd sudo sshd -T | grep -E 'permitrootlogin|passwordauthentication' corenova-eks-check
Expected SSH settings are permitrootlogin no and passwordauthentication no.
Security boundaries
The AMI has no hardcoded passwords, private keys, AWS credentials, kubeconfigs, or customer data. Buyer-created credentials and data remain in the buyer account.
Anyone who can start a shell on this host can use its shared EC2 instance-role credentials and inherits that role's EKS permissions. Treat Session Manager access as a trusted-administrator boundary; the AMI does not provide per-user EKS identity isolation.
Identity Relay instead keeps EKS permissions on the operator identity. Session Manager cannot record port-forwarded content; use Audited Workstation when recorded shell commands are required.
Encryption
The Marketplace source uses unencrypted snapshots for ingestion. Buyers can launch or copy it with encrypted EBS volumes under their account policy.
Service quotas and costs
Check regional EC2, Systems Manager, and EKS quotas before launch. EC2, EBS, networking, logging, data transfer, and Marketplace software are billed separately.
Support
Email: support@corenovacloud.com Web: https://www.corenovacloud.com/en/support/
Include Region, AMI and Instance IDs, instance type, EKS version, command output, and reproduction steps.
Resources
Support
Vendor support
Email: support@corenovacloud.com
Web: https://www.corenovacloud.com/
CoreNova supports AMI launch, AWS Systems Manager Session Manager access, EKS administration tool checks, Marketplace AMI metadata, and documented hardening behavior. Include AWS Region, AMI ID, EC2 Instance ID, instance type, EKS cluster version, tool output, and steps to reproduce.
Refund: 30-day refund on Marketplace software fees for verified technical issues. AWS infrastructure charges are billed by AWS and are not refundable by the seller.
AWS infrastructure support
AWS Support is a one-on-one, fast-response support channel that is staffed 24x7x365 with experienced and technical support engineers. The service helps customers of all sizes and technical abilities to successfully utilize the products and features provided by Amazon Web Services.
Similar products
CoreNova SSM EKS Admin Bastion AMI (Amazon Linux 2023, x86_64): private Amazon EKS administration bastion for teams replacing public SSH jump hosts. Includes AWS CLI v2, Session Manager Plugin, kubectl version selector, Helm, eksctl, k9s, IAM examples, and AL2023 hardening.
This product has charges associated with it for CoreNova hardening, maintenance, validation notes, and seller support. AlmaLinux 9 Hardened Graviton AMI (ARM64, LVM, XFS) provides a hardened AlmaLinux 9 EC2 baseline with SSH lockdown, audit logging, AIDE, firewall controls, and buyer-side OpenSCAP notes.
This product has charges associated with it for CoreNova hardening, maintenance, validation notes, and seller support. Amazon Linux 2023 Graviton Hardened (ARM64, 64K-Page) provides a hardened Amazon Linux 2023 EC2 baseline with SSH lockdown, audit logging, AIDE, firewall controls, and buyer-side OpenSCAP notes.
This product has charges associated with it for CoreNova hardening, maintenance, validation notes, and seller support. Debian 12 Bookworm Hardened Graviton (ARM64, LVM) provides a hardened Debian 12 Bookworm EC2 baseline with SSH lockdown, audit logging, AIDE, firewall controls, and buyer-side OpenSCAP notes.
Customer reviews
No customer reviews yet
Be the first to review this product . We've partnered with PeerSpot to gather customer feedback. You can share your experience by writing or recording a review, or scheduling a call with a PeerSpot analyst.