Sold by: Secure Blink Inc
Deployed on AWS
Free Trial
AWS Free Tier
ThreatSpy is an autonomous DAST and API security testing platform for teams that need continuous coverage without adding headcount. It scans web applications and APIs (REST, GraphQL, OpenAPI), detects BOLA, and maps findings to the OWASP Top 10, OWASP API Security Top 10, and SANS CWE 25. Native CI/CD integrations, reachability-based prioritization, and stack-oriented remediation guidance help engineers fix issues faster.
Overview
Image
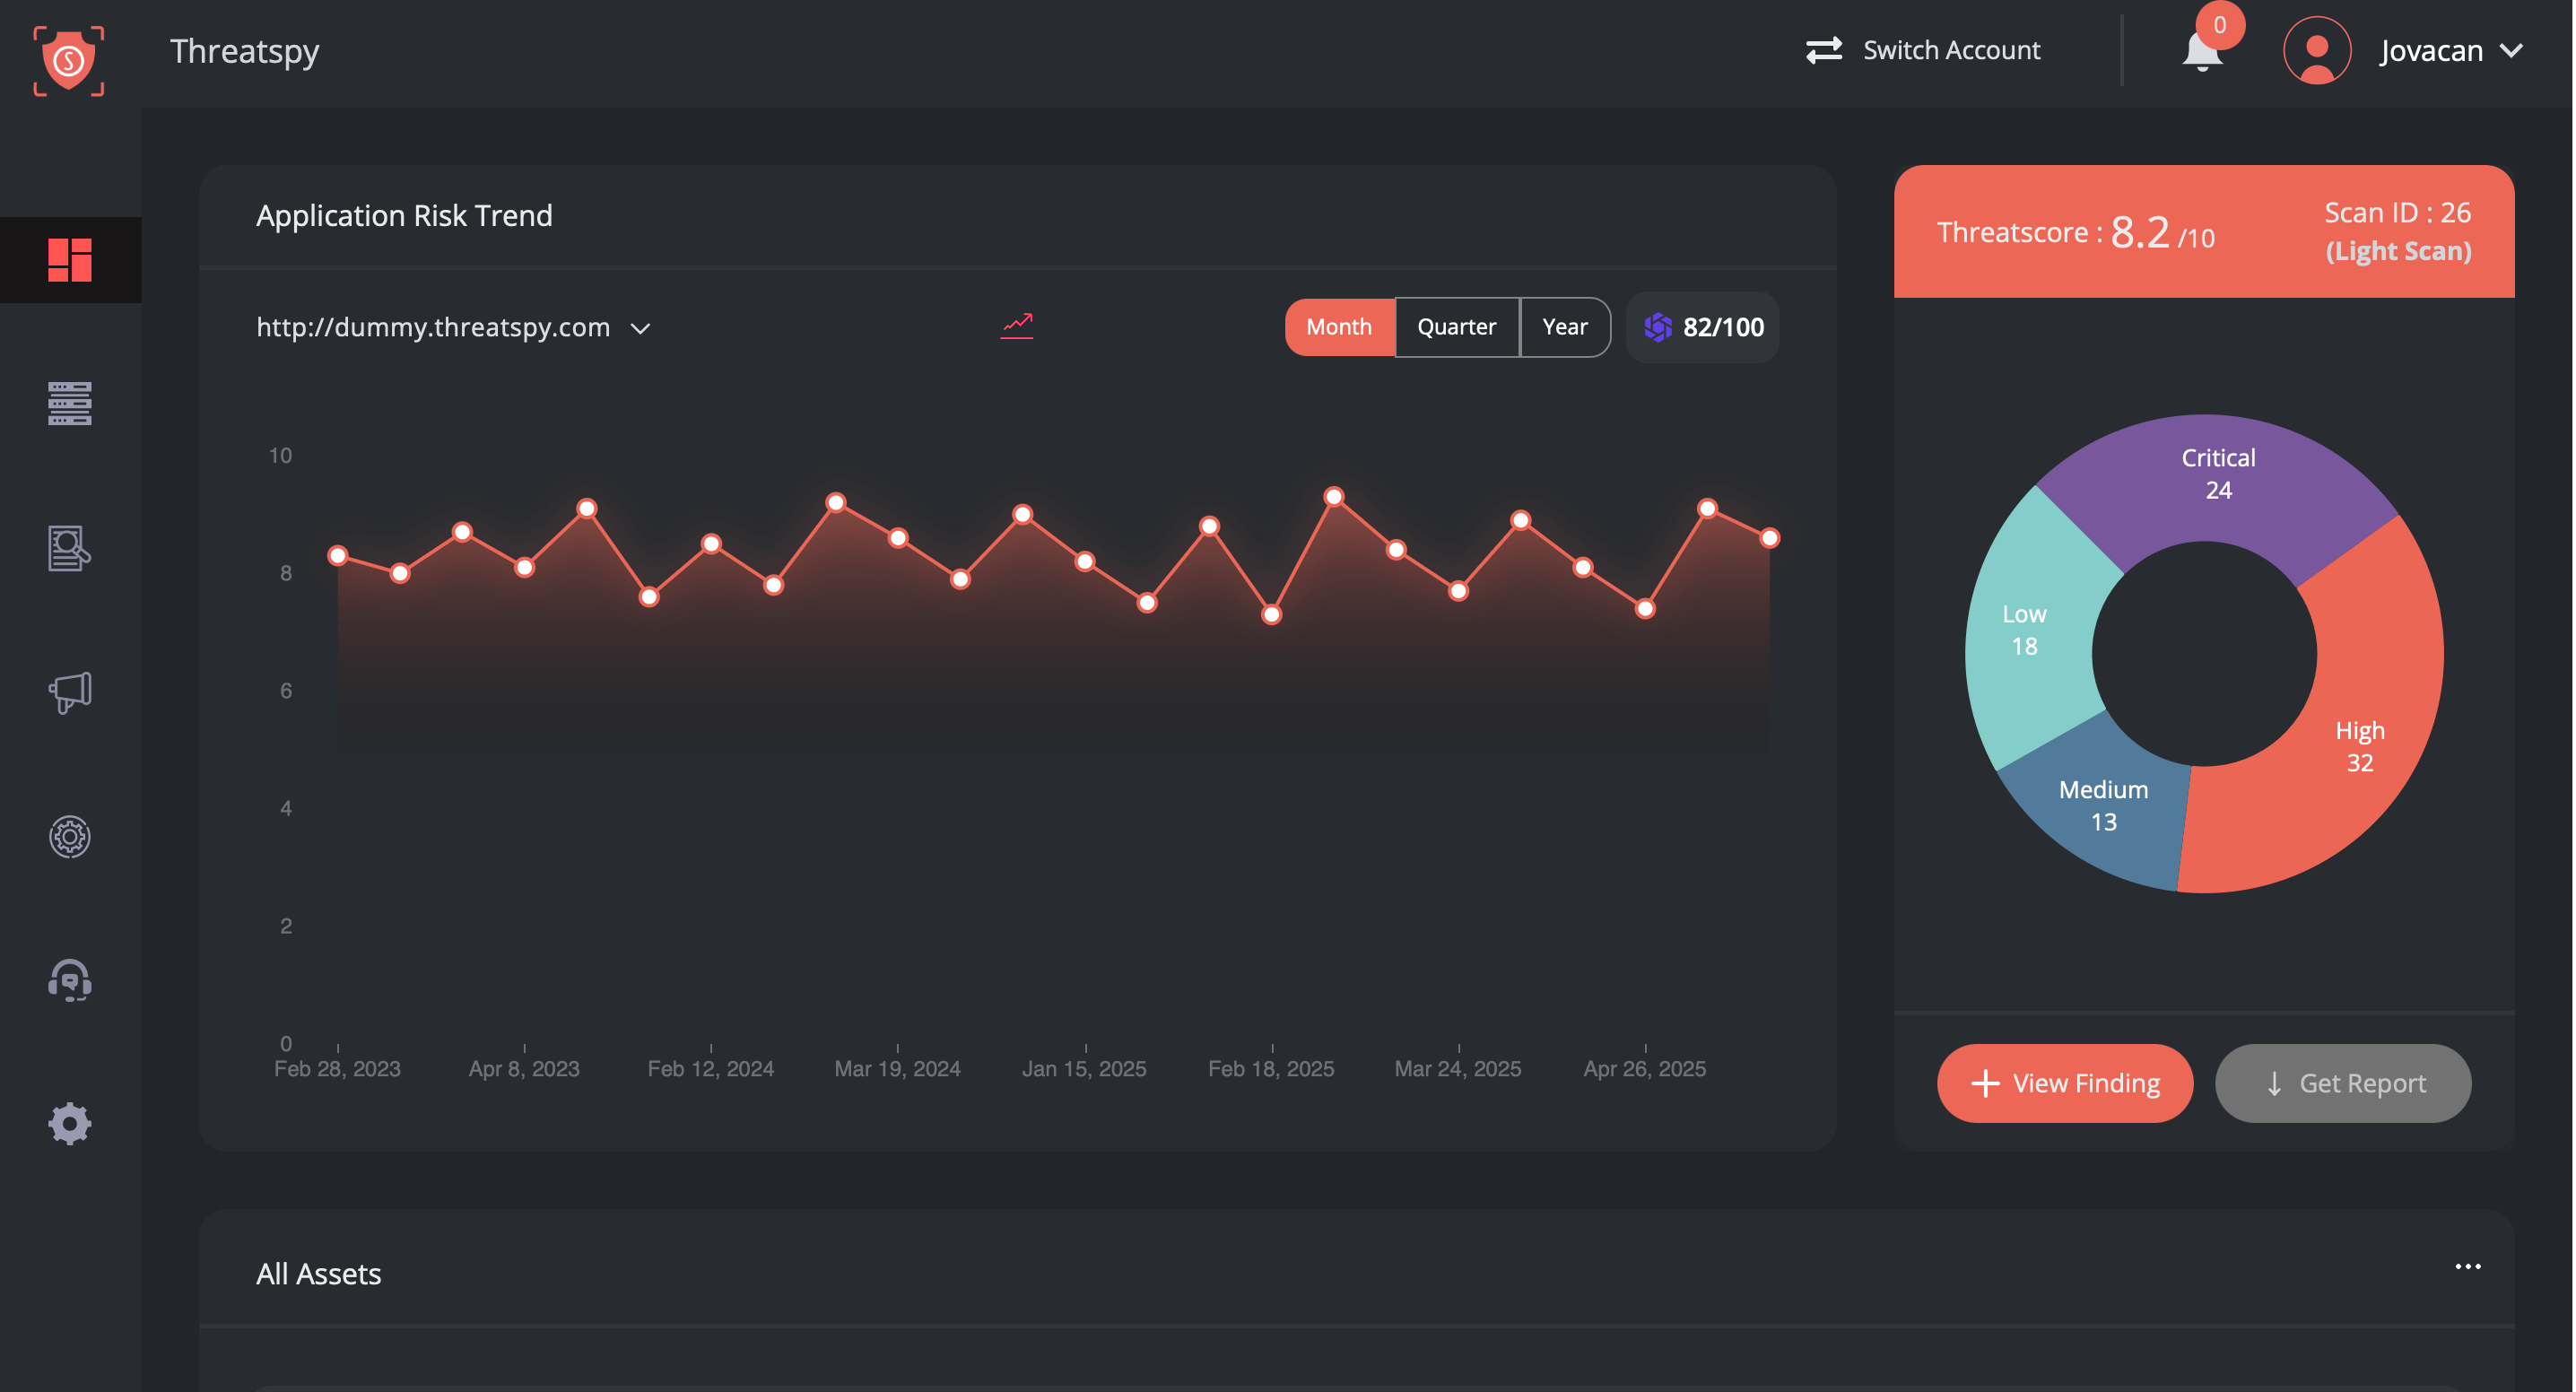
Dashboard: Application Risk at a Glance
Image
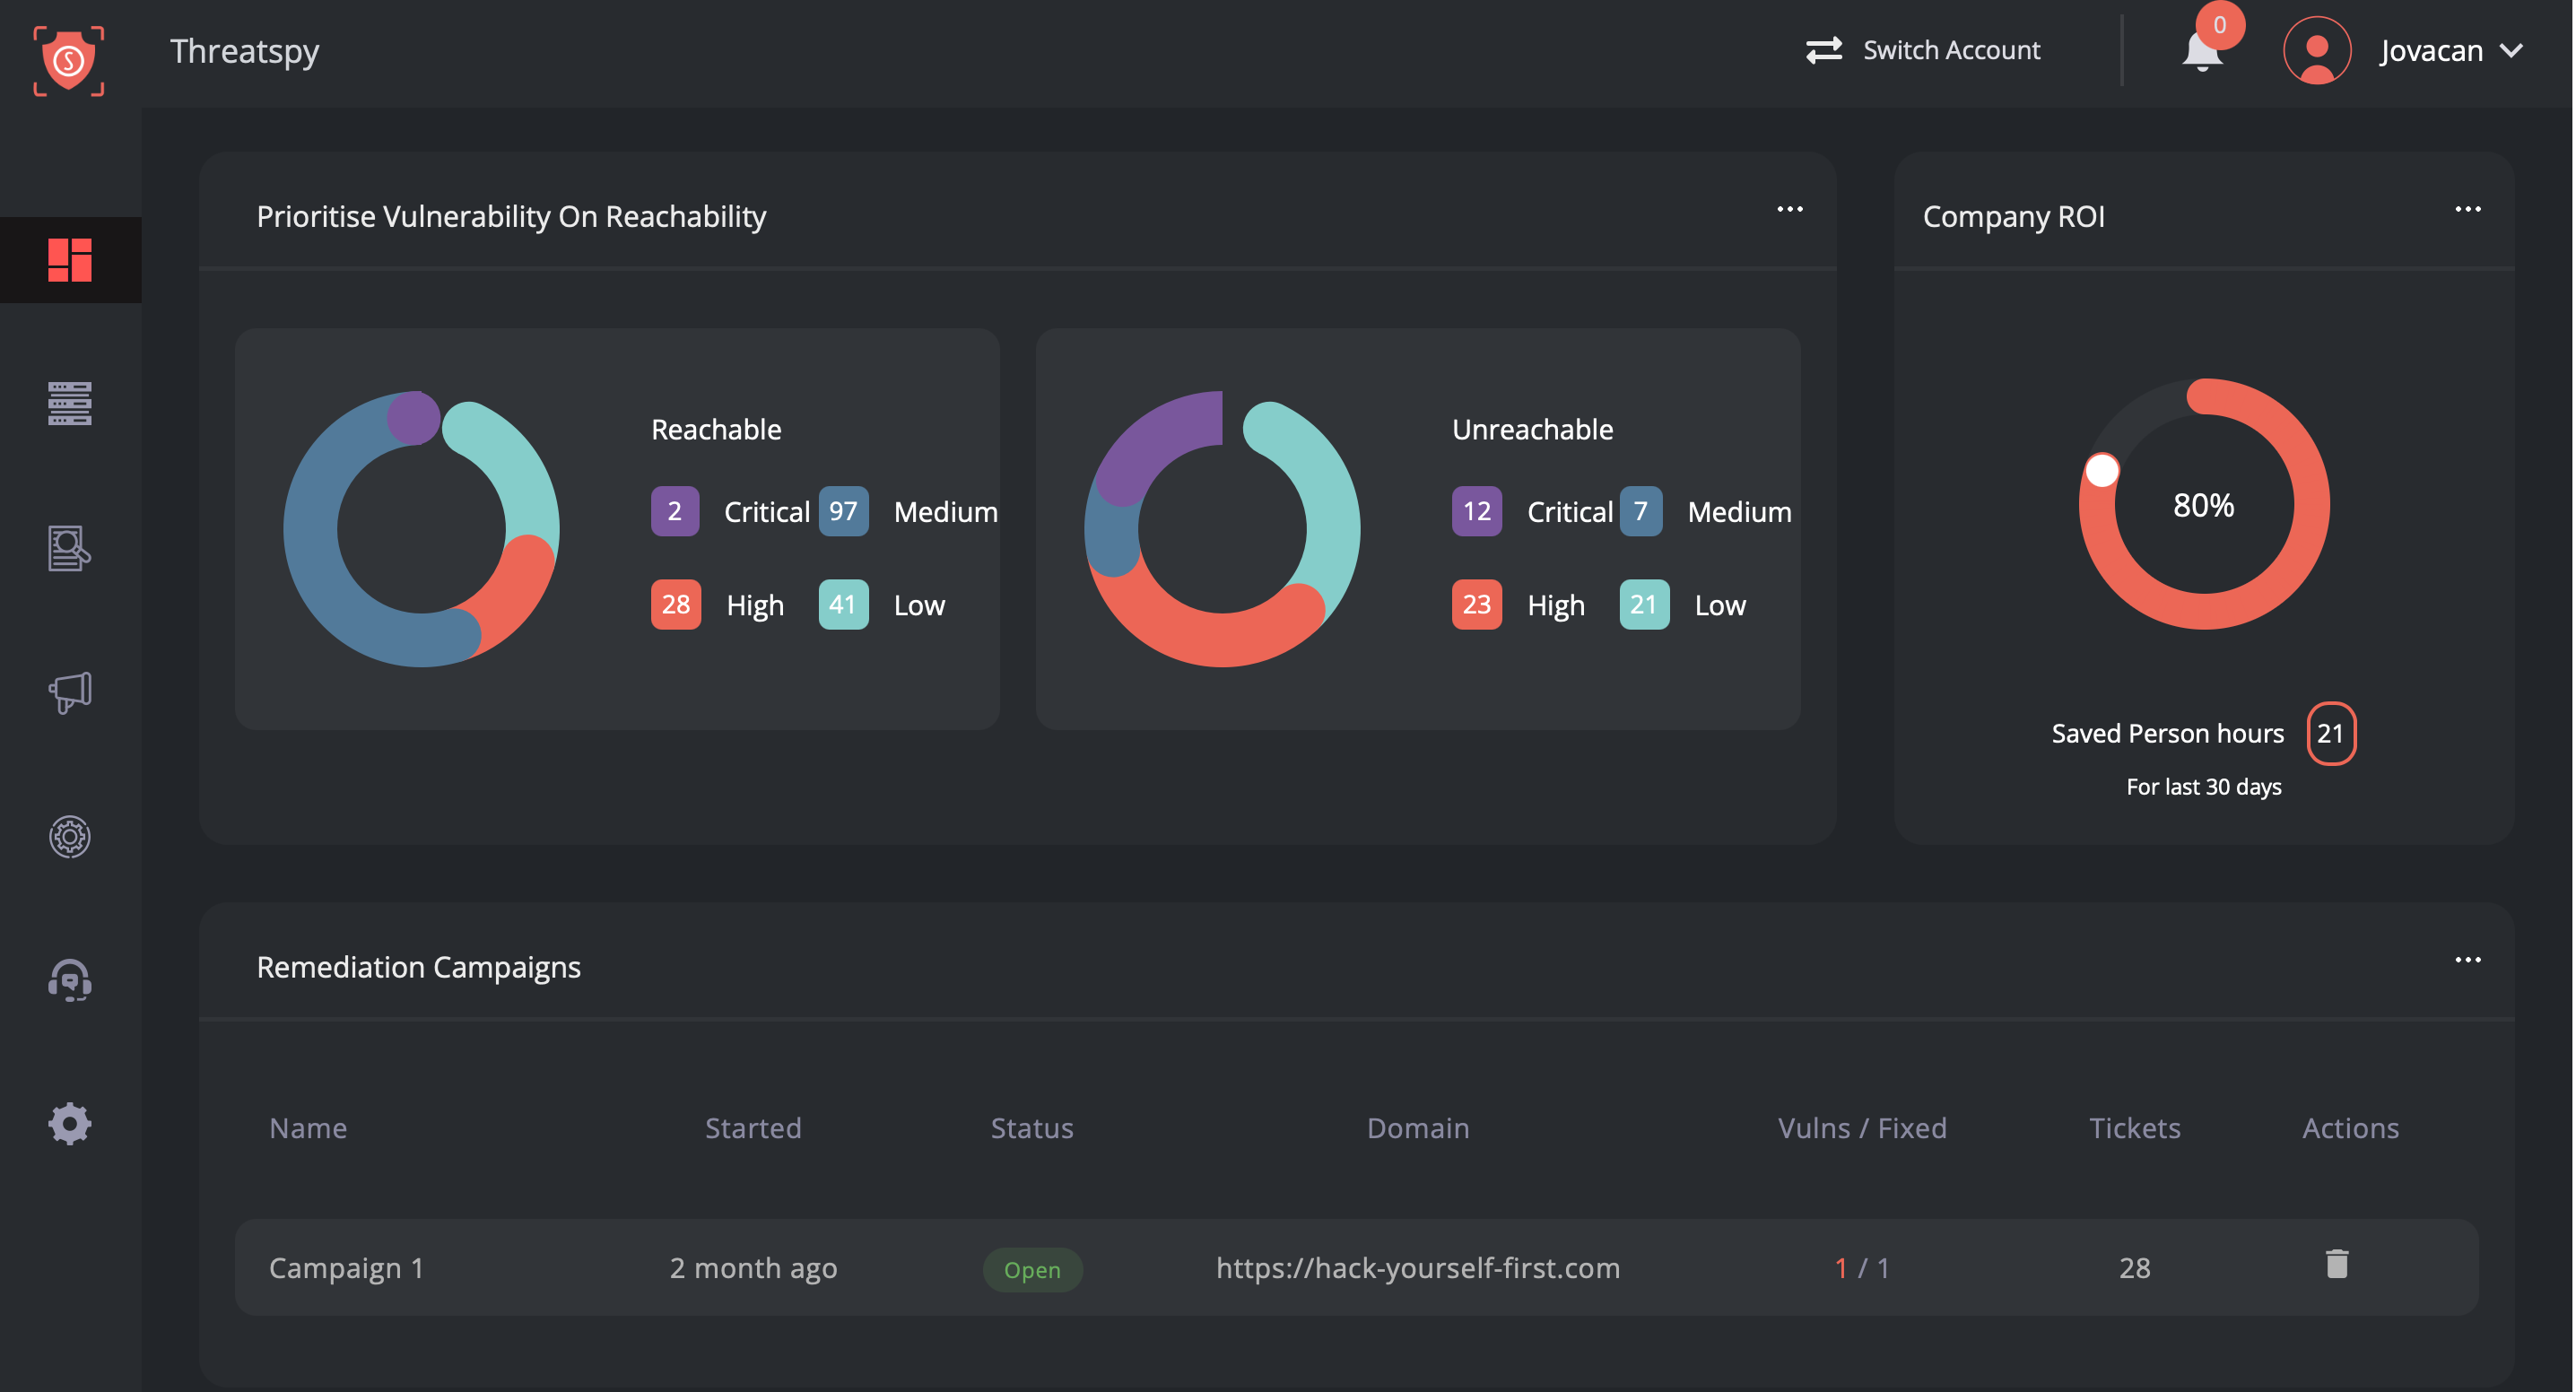
Prioritize by Reachability, ROI, and Campaigns
Image
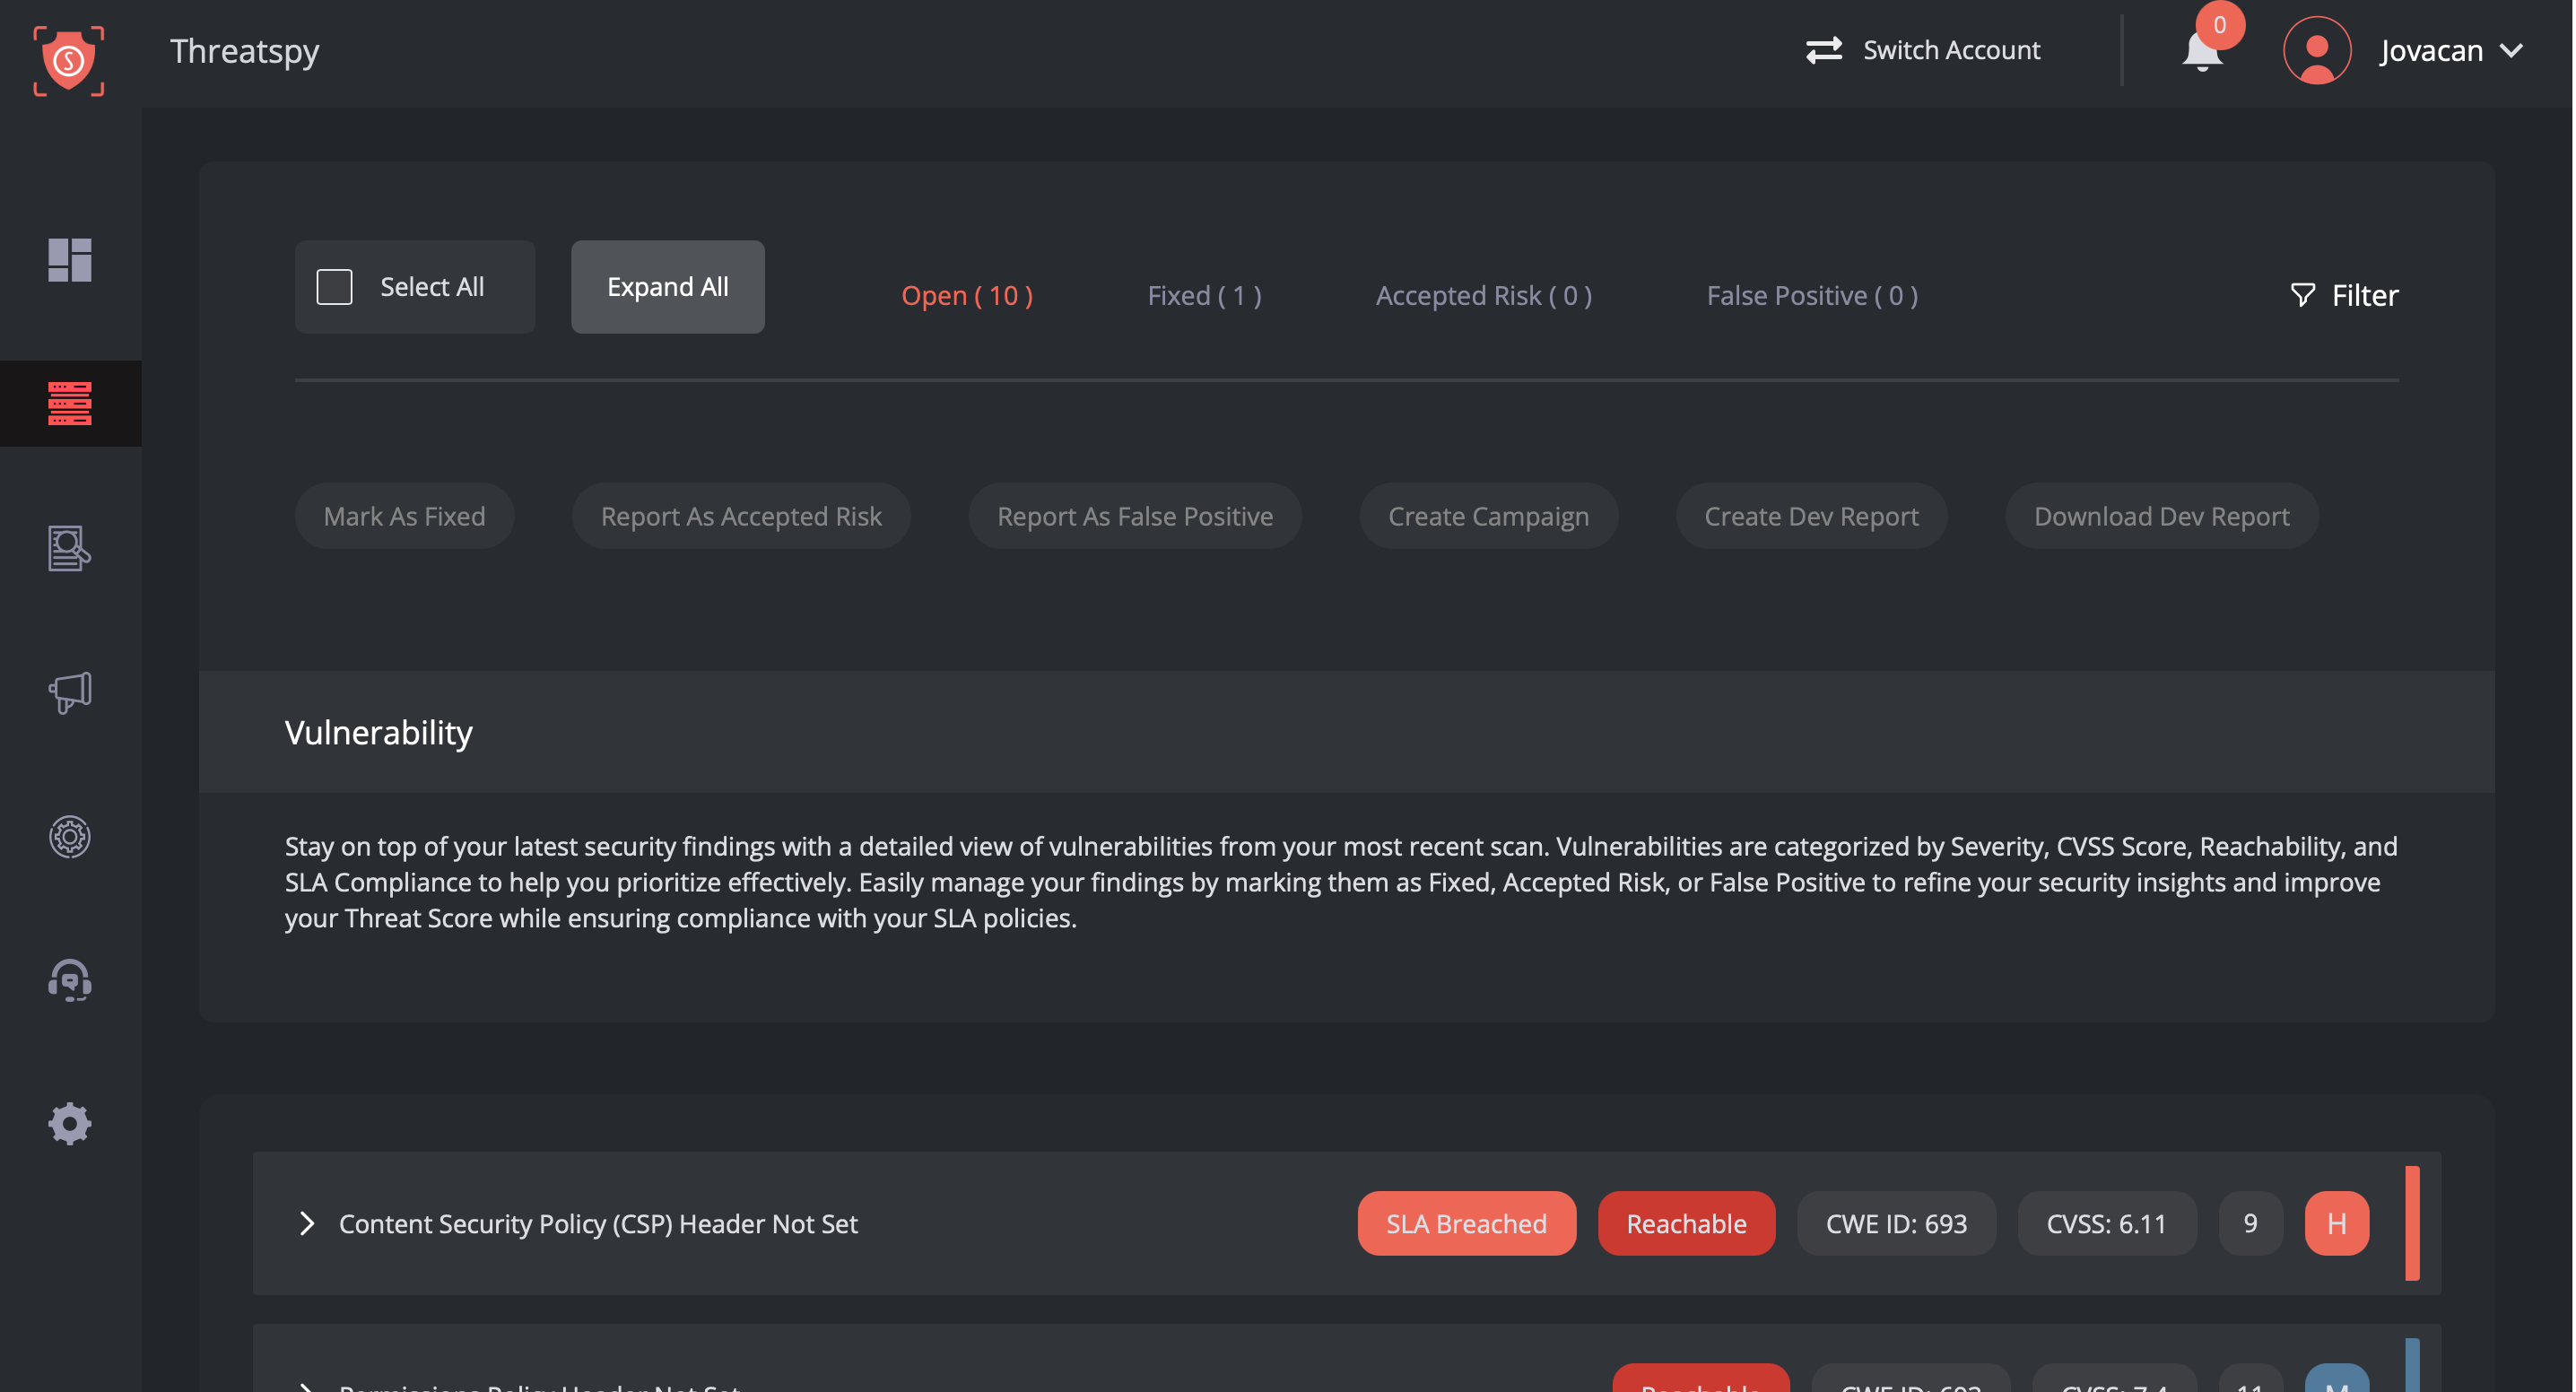
Detailed Findings with AI Remediation and Review
Your apps change every week. Your security testing should keep up. ThreatSpy is built for that pace.
ThreatSpy is an autonomous DAST and API security testing platform for security and engineering teams that need continuous coverage without adding headcount. It scans web applications and APIs (REST, GraphQL, and OpenAPI), authenticated or unauthenticated, maps findings to the OWASP Top 10, OWASP API Security Top 10, and SANS CWE 25, tests APIs for BOLA (Broken Object Level Authorization), and gives stack-oriented remediation guidance so engineers can fix issues instead of debating them.
What you get with ThreatSpy
-
Autonomous DAST and API security testing. Continuous, 24x7 scanning of web applications and APIs, with authenticated and unauthenticated modes. Coverage includes the OWASP Top 10, OWASP API Security Top 10, SANS CWE 25, plus CORS, DNS, and cloud storage bucket misconfiguration checks. Pro adds light and deep scan types.
-
BOLA detection. ThreatSpy tests for Broken Object Level Authorization, the number one risk in the OWASP API Security Top 10. These are the cases where one user can reach another user's data by changing an object identifier in a request.
-
Less noise, faster fixes. Heuristic detection keeps findings focused on what matters. Customers report 95% fewer false positives and 85% faster remediation, and resolve 89% of critical vulnerabilities within SLA.
-
Security that ships with your code. Native CI/CD integrations (Jenkins, GitHub, GitLab, and more) bring testing into every build. Stack-oriented remediation guidance, automated remediation playbooks, and remediation campaigns turn findings into fixes.
-
Built for small teams. Pro adds AI Review to help triage and explain findings, plus workflows that route issues to Slack, Jira, Trello, Splunk, PagerDuty, or webhooks. PDF reports make it easy to share results with stakeholders.
-
Plans that fit. Starter covers one application with a daily scan. Pro covers ten applications with unlimited scans, AI-powered features, and both authenticated and unauthenticated scanning. Customers report an average of $1.2M in annual savings and an 80x return on investment.
ThreatSpy is built by Secure Blink. It received the GrindStone Award at the Global Cyber Startup Showcase at the Global CISO Summit (RSA Conference 2026) and was named a Top 3 Cybersecurity Startup and Scaleup Finalist at Nexus Luxembourg 2026.
For custom pricing, larger deployments, or MSSP terms, email sales@secureblink.com and we will put together a private offer.
Highlights
- Autonomous DAST and API security testing, including BOLA. ThreatSpy detects Broken Object Level Authorization (BOLA), the number one risk in the OWASP API Security Top 10, and continuously scans web applications and APIs (REST, GraphQL, OpenAPI), authenticated or unauthenticated, with coverage across the OWASP Top 10 and SANS CWE 25. Customers report 95% fewer false positives and 85% faster remediation.
- Security that ships with your code. ThreatSpy plugs into your CI/CD pipeline (Jenkins, GitHub, GitLab, and more), gives stack-oriented remediation guidance, and runs automated remediation playbooks and campaigns, so fixing becomes part of the build process instead of an afterthought. Customers resolve 89% of critical vulnerabilities within SLA.
- Built for small security teams. Pro adds AI Review to help triage and explain findings, plus workflows that route issues to Slack, Jira, Trello, Splunk, PagerDuty, or webhooks. Customers report an average of $1.2M in annual savings and an 80x return on investment.
Details
Sold by
Categories
Delivery method
Deployed on AWS
New
Introducing multi-product solutions
You can now purchase comprehensive solutions tailored to use cases and industries.
Features and programs
Financing for AWS Marketplace purchases
AWS Marketplace now accepts line of credit payments through the PNC Vendor Finance program. This program is available to select AWS customers in the US, excluding NV, NC, ND, TN, & VT.

Pricing
Free trial
Try this product free according to the free trial terms set by the vendor.
Pricing is based on the duration and terms of your contract with the vendor. This entitles you to a specified quantity of use for the contract duration. If you choose not to renew or replace your contract before it ends, access to these entitlements will expire.
Additional AWS infrastructure costs may apply. Use the AWS Pricing Calculator to estimate your infrastructure costs.
Dimension | Description | Cost/12 months |
|---|---|---|
ThreatSpy Starter -1 App, 1 Scan/Day (12-Month) | Includes 1 application (FQDN) license, 1 admin/analyst user, and 1 scan per day for a 12-month term. Covers OWASP Top 10 (limited scope), dashboard-only analytics, executive and developer reporting, and Standard (Silver) support - 5 days a week, 9 hours a day. Best suited for startups and small teams securing a single web application or API. | $8,399.00 |
ThreatSpy Pro -10 Apps, Unlimited Scans (12-Month) | Includes 10 application (FQDN) licenses, up to 10 users (3 admin/analyst seats), and unlimited scans for a 12-month term. Covers full OWASP Top 10 and API Security Top 10, authenticated and unauthenticated scanning across REST, GraphQL, and OpenAPI, up to 8 active automated remediation playbooks, customizable analytics with 90-day data retention, unlimited workflow integrations (Slack, Jira, Trello, Splunk, PagerDuty, webhooks), and Premium (Gold) support - 6 days a week, 12 hours a day. Built for growing engineering and AppSec teams needing continuous, collaborative security coverage. | $18,999.00 |
Vendor refund policy
All Subscription Fees are non-refundable, including for early cancellation or partial usage of a billing period. Refunds are considered only for duplicate charges, SLA-based service credits, uncured material breach by Secure Blink, or unauthorized transactions - see full policy for details. To request a refund, email billing@secureblink.com with subject "Refund Request - Account/Order ID". Full policy: secureblink.com/refund-policy
Legal
Vendor terms and conditions
Upon subscribing to this product, you must acknowledge and agree to the terms and conditions outlined in the vendor's End User License Agreement (EULA) .
Content disclaimer
Vendors are responsible for their product descriptions and other product content. AWS does not warrant that vendors' product descriptions or other product content are accurate, complete, reliable, current, or error-free.
Delivery details
Software as a Service (SaaS)
SaaS delivers cloud-based software applications directly to customers over the internet. You can access these applications through a subscription model. You will pay recurring monthly usage fees through your AWS bill, while AWS handles deployment and infrastructure management, ensuring scalability, reliability, and seamless integration with other AWS services.
Support
Vendor support
Secure Blink provides 24x7 support for critical and high-priority issues, with business-hours support (Mon-Fri, 09:00-18:00 IST) for all other requests.
Response times by priority:
P1 (Critical/outage): 1-hour response, 4-hour target resolution P2 (High/major impairment): 2-hour response, 12-hour target resolution P3 (Medium): 4-hour response, resolved in next scheduled release P4 (Low/general inquiries): 12-hour response, best effort
ThreatSpy maintains a 99.9% monthly uptime commitment with service credits for verified SLA breaches. Enterprise customers get a dedicated Slack channel and emergency hotline for P1 issues.
Support channels: email and in-product support portal (24x7 for P1/P2). Real-time status: status.secureblink.com. Full SLA: secureblink.com/service-level-agreement
AWS infrastructure support
AWS Support is a one-on-one, fast-response support channel that is staffed 24x7x365 with experienced and technical support engineers. The service helps customers of all sizes and technical abilities to successfully utilize the products and features provided by Amazon Web Services.
Similar products
XBOW is an autonomous offensive security platform that delivers AI pentesting on-demand. Get the depth and results of a premium pentesting engagement in a fraction of the time.

Equixly is an AI-powered API security testing platform.
Contrary to other testing platforms that primarily rely on fuzzing - a process of sending random data to APIs to detect vulnerabilities - Equixly stands out by excelling in identifying logic vulnerabilities, focusing on complex business logic security issues that are often overlooked by other tools.
Test your network the way an attacker would, as often as you need. Threat Protect runs autonomous penetration tests across your internal and external networks on a schedule, shows the attack paths an attacker could actually use, ranks fixes by real exploitability and re-runs tests to prove each fix worked.
Find and fix flaws in your web apps, APIs and code before release. Threat Protect reviews your applications and delivery pipeline, selects SAST, DAST and dependency scanning tools across vendors, integrates them into your build pipeline with agreed fail thresholds, and adds tester-led web application and API testing.
Customer reviews
No customer reviews yet
Be the first to review this product . We've partnered with PeerSpot to gather customer feedback. You can share your experience by writing or recording a review, or scheduling a call with a PeerSpot analyst.