AWS Security Blog
Category: Security, Identity, & Compliance
How to use Amazon Verified Permissions for authorization
Applications with multiple users and shared data require permissions management. The permissions describe what each user of an application is permitted to do. Permissions are defined as allow or deny decisions for resources in the application. To manage permissions, developers often combine attribute-based access control (ABAC) and role-based access control (RBAC) models with custom code […]
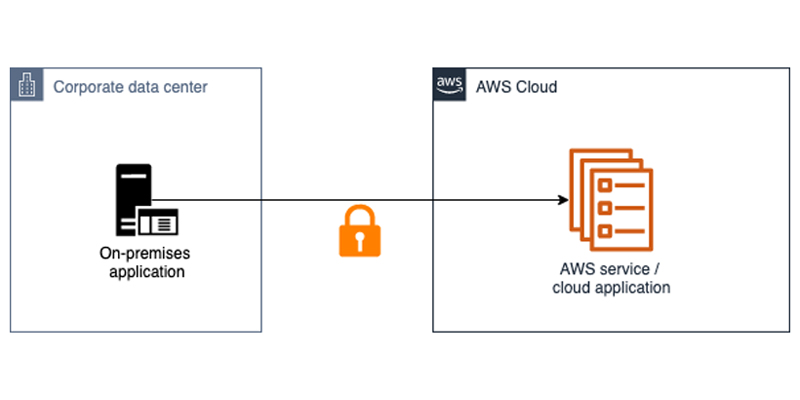
Approaches for authenticating external applications in a machine-to-machine scenario
December 8, 2022: This post has been updated to reflect changes for M2M options with the new service of IAMRA. This blog post was first published November 19, 2013. August 10, 2022: This blog post has been updated to reflect the new name of AWS Single Sign-On (SSO) – AWS IAM Identity Center. Read more […]

How to secure your SaaS tenant data in DynamoDB with ABAC and client-side encryption
If you’re a SaaS vendor, you may need to store and process personal and sensitive data for large numbers of customers across different geographies. When processing sensitive data at scale, you have an increased responsibility to secure this data end-to-end. Client-side encryption of data, such as your customers’ contact information, provides an additional mechanism that […]

How to investigate and take action on security issues in Amazon EKS clusters with Amazon Detective – Part 2
March 15, 2023: We’ve updated this post to incorporate a section to investigate VPC flow logs. In part 1 of this of this two-part series, How to detect security issues in Amazon EKS cluster using Amazon GuardDuty, we walked through a real-world observed security issue in an Amazon Elastic Kubernetes Service (Amazon EKS) cluster and […]

How to use Amazon Macie to preview sensitive data in S3 buckets
February 13, 2024: We’ve updated this post to show you how to configure Macie to assume an IAM role when you configure Macie to preview sensitive data in findings. Security teams use Amazon Macie to discover and protect sensitive data, such as names, payment card data, and AWS credentials, in Amazon Simple Storage Service (Amazon […]
Use Amazon Macie for automatic, continual, and cost-effective discovery of sensitive data in S3
Customers have an increasing need to collect, store, and process data within their AWS environments for application modernization, reporting, and predictive analytics. AWS Well-Architected security pillar, general data privacy and compliance regulations require that you appropriately identify and secure sensitive information. Knowing where your data is allows you to implement the appropriate security controls which […]
Get the best out of Amazon Verified Permissions by using fine-grained authorization methods
With the release of Amazon Verified Permissions, developers of custom applications can implement access control logic based on caller and resource information; group membership, hierarchy, and relationship; and session context, such as device posture, location, time, or method of authentication. With Amazon Verified Permissions, you can focus on building simple authorization policies and your applications—instead […]

Deploy AWS Organizations resources by using CloudFormation
May 20, 2026: We updated the SCP quotas. AWS recently announced that AWS Organizations now supports AWS CloudFormation. This feature allows you to create and update AWS accounts, organizational units (OUs), and policies within your organization by using CloudFormation templates. With this latest integration, you can efficiently codify and automate the deployment of your resources in AWS […]

AWS Digital Sovereignty Pledge: Control without compromise
French | German | Indonesian | Italian | Japanese | Korean | Portuguese | Spanish | Arabic We’ve always believed that for the cloud to realize its full potential it would be essential that customers have control over their data. Giving customers this sovereignty has been a priority for AWS since the very beginning when […]

Establishing a data perimeter on AWS: Allow only trusted identities to access company data
November 13, 2024: This post has been updated with guidance on how to use resource control policies (RCPs) and the aws:SourceOrgID condition key to establish your organization’s identity perimeter. As described in an earlier blog post, Establishing a data perimeter on AWS, Amazon Web Services (AWS) offers a set of capabilities you can use to […]