AWS Storage Blog
Category: AWS Key Management Service
How Proscia built unlimited observability with Amazon S3 and the Altinity Kubernetes Operator
Observability can claim a growing share of IT budgets. Learn how Proscia, a pathology AI company, built a self-hosted observability platform on Amazon S3, Amazon EKS, and ClickHouse managed by the Altinity Kubernetes Operator, achieving unlimited telemetry retention at object-storage cost under HIPAA, GDPR, and data-residency requirements.
Updating encryption on existing Amazon S3 objects with S3 Batch Operations
Large organizations accumulate billions of Amazon S3 objects under different encryption configurations. Learn how to use S3 Batch Operations with the new UpdateObjectEncryption API to standardize encryption across an entire bucket at scale. The approach moves objects from SSE-S3 to SSE-KMS in place, with no data movement and without breaking S3 Lifecycle policies.

Query Amazon S3 access logs instantly with CloudWatch and S3 Tables
Knowing who accessed your data, when, and how is the foundation for security investigations, compliance audits, cost attribution, and performance troubleshooting. Detailed access logs capture every request: who made it, which resource was accessed, and what response was returned. In practice, though, they arrive as semi-structured records spread across different locations. Turning them into actionable […]
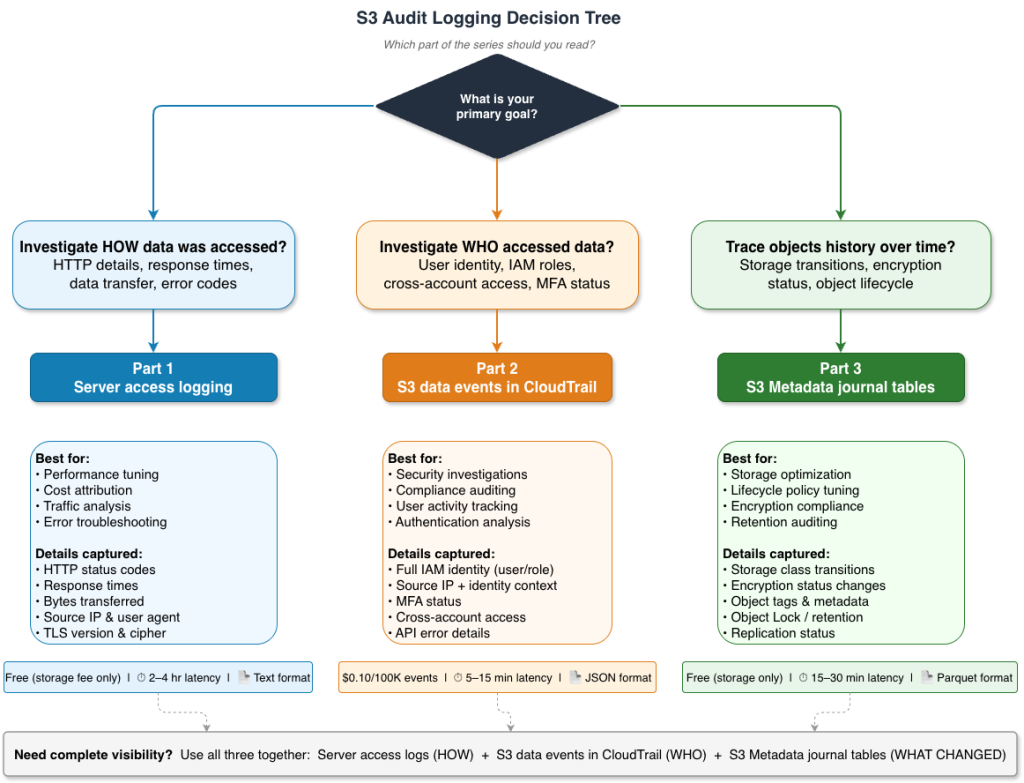
Amazon S3 audit logging, Part 3: Analyzing S3 Metadata journal tables for object lifecycle tracking
This is Part 3 of our three-part series on Amazon S3 audit logging. In Part 1, we covered server access logs for HTTP-level requests and performance analysis. In Part 2, we covered S3 data events in AWS CloudTrail for identity-focused security investigations. As data volumes grow and storage costs become a significant line item, organizations […]

Applying Amazon S3 Object Lock at scale for petabytes of existing data
Organizations with petabytes of data in the cloud need a way to apply immutable storage protections to data that’s already been stored—whether for regulatory compliance or cyber resilience. Although you can enable write-once-read-many (WORM) controls for newly created storage, applying these protections to existing enterprise data at scale requires a systematic approach. Regulated industries have […]
Building an open warehouse architecture: Supabase’s integration with Amazon S3 Tables
As applications scale, developers face a persistent challenge: analytical queries that slow down transactional databases, force them to copy data across multiple proprietary tools, and create disconnected data silos. For the 5 million developers building on Supabase, an open source Postgres development platform, this tension between operational and analytical workloads has become increasingly critical. The […]

Advanced notice: Amazon S3 to disable the use of SSE-C encryption by default for all new buckets and select existing buckets in April 2026
Starting on April 6, 2026, we will be changing how server-side encryption with customer-provided keys (SSE-C) is enabled for Amazon S3 buckets. With this change, SSE-C will be disabled by default on all new S3 general purpose buckets. Furthermore, SSE-C will also be disabled for all existing buckets in Amazon Web Services (AWS) Accounts that […]

Encrypt AWS Backup logically air-gapped vaults with customer-managed keys
Organizations in regulated industries often mandate control over encryption keys when storing data in the cloud to meet compliance requirements. Although AWS Backup logically air-gapped vault provides secure, isolated backup storage, these customers have needed the ability to use their own AWS Key Management Service (AWS KMS) customer-managed keys (CMKs) to provide greater control of […]
Cross-account Amazon S3 bulk transfers with enhanced AWS KMS support
Cross-account Amazon S3 bulk transfers with enhanced AWS Key Management Service (AWS KMS) support become increasingly critical as organizations grow and accumulate vast amounts of digital assets across their enterprise. Managing millions or even billions of files presents unique challenges, especially when these files need to be moved securely between different AWS accounts. Operations such […]
Build centralized cross-Region backup architecture with AWS Control Tower
Managing data protection at scale is a critical challenge for the modern enterprise. As organizations grow, their data becomes increasingly distributed, making it difficult to implement consistent backup policies that ensure comprehensive coverage. IT teams must balance competing needs of compliance requirements, resource protection, and operational efficiency – all while struggling to validate and orchestrate […]