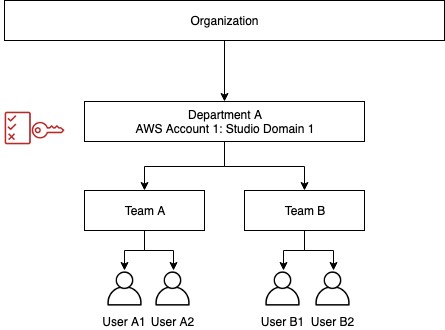
, attach the following policy to role that the user assumes after federation:
{
   "Version": "2012-10-17",
   "Statement": [
       {
           "Sid": "AmazonSageMakerPresignedUrlPolicy",
           "Effect": "Allow",
           "Action": [
                "sagemaker:CreatePresignedDomainUrl"
           ],
           "Resource": "*",
           "Condition": {
                  "StringEquals": {
                      "sagemaker:ResourceTag/studiouserid": "${aws:PrincipalTag/studiouserid}"
                 }
            }
      }
  ]
}
Add the following statement to this policy in the Trust Relationship section. This statement defines the allowed transitive tag. See Chaining roles with session tags for more information on role chaining and passing tags to subsequent sessions.
"Statement": [
     {
        --Existing statements
      },
      {
      "Sid": "IdentifyTransitiveTags",
      "Effect": "Allow",
      "Principal": {
        "Federated": "arn:aws:iam::<account id>:saml-provider/<identity provider>"
      },
      "Action": "sts:TagSession",
      "Condition": {
        "ForAllValues:StringEquals": {
          "sts:TransitiveTagKeys": [
            "studiouserid"
          ]
        }
      }
  ]
For users managed in IAM Identity Center, this policy is not required. IAM Identity Center performs the identity check.
Creating roles for the teams
To create roles for your teams, you must first create the policies. For simplicity, we use the same policies for both teams. In most cases, you just need one set of policies for all teams, but you have the flexibility to create different policies for different teams. In the second step, you create a role for each team, attach the policies, and tag the roles with appropriate team tags.
Creating the policies
Create the following policies. For this post, we split them into three policies for more readability, but you can create them according to your needs.
Policy 1: Amazon SageMaker read-only access
The following policy gives privileges to List and Describe Amazon SageMaker resources. You can customize this policy according to your needs.
{
    "Version": "2012-10-17",
    "Statement": [
        {
            "Sid": "AmazonSageMakerListandSearchOnlyPolicy",
            "Effect": "Allow",
            "Action": [
                "sagemaker:GetSearchSuggestions",
		"sagemaker:List*"
            ],
            "Resource": "*"
        },
        {
            "Sid": "AmazonSageMakerUIandMetricsOnlyPolicy",
            "Effect": "Allow",
            "Action": [
                "sagemaker:*App",
                "sagemaker:Search",
                "sagemaker:RenderUiTemplate",
                "sagemaker:BatchGetMetrics"
            ],
            "Resource": "*"
        },
        {
            "Sid": "AmazonSageMakerEC2ReadOnlyPolicy",
            "Effect": "Allow",
            "Action": [
                "ec2:DescribeDhcpOptions",
                "ec2:DescribeNetworkInterfaces",
                "ec2:DescribeRouteTables",
                "ec2:DescribeSecurityGroups",
                "ec2:DescribeSubnets",
                "ec2:DescribeVpcEndpoints",
                "ec2:DescribeVpcs"
            ],
            "Resource": "*"
        },
        {
            "Sid": "AmazonSageMakerIAMReadOnlyPolicy",
            "Effect": "Allow",
            "Action": [
                "iam:ListRoles"
            ],
            "Resource": "*"
        }
    ]
}
Policy 2: Amazon SageMaker access for supporting services
The following policy gives privileges to create, read, update, and delete access to Amazon Simple Storage Service (Amazon S3), Amazon Elastic Container Registry (Amazon ECR), and Amazon CloudWatch, and read access to AWS Key Management Service (AWS KMS). You can customize this policy according to your needs. Since source identity feature is enabled, you can use the aws:SourceIdentity condition key to restrict access to related services as well. For example, the following policy only allows write access to user’s own S3 prefixes by checking if the prefix is equal to the user profile name.
{
    "Version": "2012-10-17",
    "Statement": [
        {
            "Sid": "AmazonSageMakerS3ReadOnlyPolicy",
            "Effect": "Allow",
            "Action": [
                "s3:ListBucket",
                "s3:ListAllMyBuckets"
            ],
            "Resource": "*"
        },
        {
            "Sid": "AmazonSageMakerCRUDAccessS3Policy",
            "Effect": "Allow",
            "Action": [
                "s3:PutObject",
                "s3:GetObject",
                "s3:AbortMultipartUpload",
                "s3:DeleteObject",
                "s3:PutBucketCORS",
                "s3:GetBucketCORS",
                "s3:GetBucketLocation"
            ],
            "Resource": "arn:aws:s3:::<S3 BUCKET NAME>/${aws:SourceIdentity}/*"
        },
        {
            "Sid": "AmazonSageMakerReadOnlyAccessKMSPolicy",
            "Effect": "Allow",
            "Action": [
                "kms:DescribeKey",
                "kms:ListAliases"
            ],
            "Resource": "*"
        },
        {
            "Sid": "AmazonSageMakerCRUDAccessECRPolicy",
            "Effect": "Allow",
            "Action": [
                "ecr:Set*",
                "ecr:Batch*",
                "ecr:Upload*",
                "ecr:Put*",
                "ecr:Describe*",
                "ecr:Get*",
                "ecr:CompleteLayerUpload",
                "ecr:InitiateLayerUpload",
                "ecr:CreateRepository",
                "ecr:StartImageScan"
            ],
            "Resource": "*"
        },
        {
            "Sid": "AmazonSageMakerCRUDAccessCloudWatchPolicy",
            "Effect": "Allow",
            "Action": [
                "cloudwatch:Put*",
                "cloudwatch:Get*",
                "cloudwatch:List*",
                "cloudwatch:DescribeAlarms",
                "logs:Put*",
                "logs:Get*",
                "logs:List*",
                "logs:Describe*",
                "logs:CreateLogGroup",
                "logs:CreateLogStream",
                "logs:CreateLogDelivery",
                "logs:UpdateLogDelivery"
            ],
            "Resource": "*"
        }
    ]
}
Policy 3: Amazon SageMaker Studio developer access
The following policy gives privileges to create, update, and delete Amazon SageMaker Studio resources.
It also enforces the team and owner tags requirement during creation. In addition, it enforces describe actions on resources restricted only to the respective team members, and start, stop, update, and delete actions to only the resource owner.
{
    "Version": "2012-10-17",
    "Statement": [
        {
            "Sid": "AmazonSageMakerStudioCreateApp",
            "Effect": "Allow",
            "Action": [
                "sagemaker:CreateApp"
            ],
            "Resource": "*"
        },
        {
            "Sid": "AmazonSageMakerStudioIAMPassRole",
            "Effect": "Allow",
            "Action": [
                "iam:PassRole"
            ],
            	"Resource": "<SAGEMAKER_TRAINING_EXECUTION_ROLE_ARN>",
				"Condition": {
					"StringEquals": {
						"iam:PassedToService":"sagemaker.amazonaws.com"
					}
				}
			},
        {
            "Sid": "AmazonSageMakerInvokeEndPointRole",
            "Effect": "Allow",
            "Action": [
                "sagemaker:InvokeEndpoint"
            ],
            "Resource": "*"
        },
        {
            "Sid": "AmazonSageMakerAddTags",
            "Effect": "Allow",
            "Action": [
                "sagemaker:AddTags"
            ],
            "Resource": "*"
        },
        {
            "Sid": "AmazonSageMakerCreate",
            "Effect": "Allow",
            "Action": [
                "sagemaker:Create*"
            ],
            "Resource": "*",
            "Condition": {
                "ForAnyValue:StringEquals": {
                    "aws:TagKeys": [
                        "team",
                        "owner"
                    ]
                },
                "StringEqualsIfExists": {
                    "aws:RequestTag/team": "${aws:PrincipalTag/team}",
                    "aws:RequestTag/owner": "${aws:SourceIdentity}"
                }
            }
        },
        {
            "Sid": "AmazonSageMakerAllowTeamsReadOnly",
            "Effect": "Allow",
            "Action": [
                "sagemaker:Describe*"
            ],
            "Condition": {
                "StringEquals": {
                    "aws:PrincipalTag/team": "${sagemaker:ResourceTag/team}"
                }
            }
        },
        {
            "Sid": "AmazonSageMakerAllowUserUpdateModify",
            "Effect": "Allow",
            "Action": [
                "sagemaker:Delete*",
                "sagemaker:Stop*",
                "sagemaker:Update*",
                "sagemaker:Start*",
                "sagemaker:DisassociateTrialComponent",
                "sagemaker:AssociateTrialComponent",
                "sagemaker:BatchPutMetrics"
            ],
            "Resource": "*",
            "Condition": {
                "StringEquals": {
                    "${sagemaker:ResourceTag/owner}": "${aws:SourceIdentity}"
                }
            }
        }
    ]
}
Creating and configuring the roles
You can now create a role for each team with these policies. Tag the roles on the IAM console or with the CLI command. The steps are the same for all three authentication types. For example, tag the role for Team A with the tag key= team and value = “<Team Name>”.
Creating the Amazon SageMaker Studio user profile
In this step, we add the studiouserid tag when creating Studio user profiles. The steps are slightly different for each authentication type.
IAM users
For IAM users, you create Studio user profiles for each user by including the role that was created for the team the user belongs to. The following code is a sample CLI command. As of this writing, including a tag when creating a user profile is available only through AWS CLI.
aws sagemaker create-user-profile --domain-id <domain id> --user-profile-name <unique profile name> --tags Key=studiouserid,Value=<aws user name> --user-settings ExecutionRole=arn:aws:iam::<account id>:role/<Team Role Name>
AWS account federation
For AWS account federation, you create a user attribute (studiouserid) in an external IdP with a unique value for each user. The following code shows how to configure the attribute in Okta:
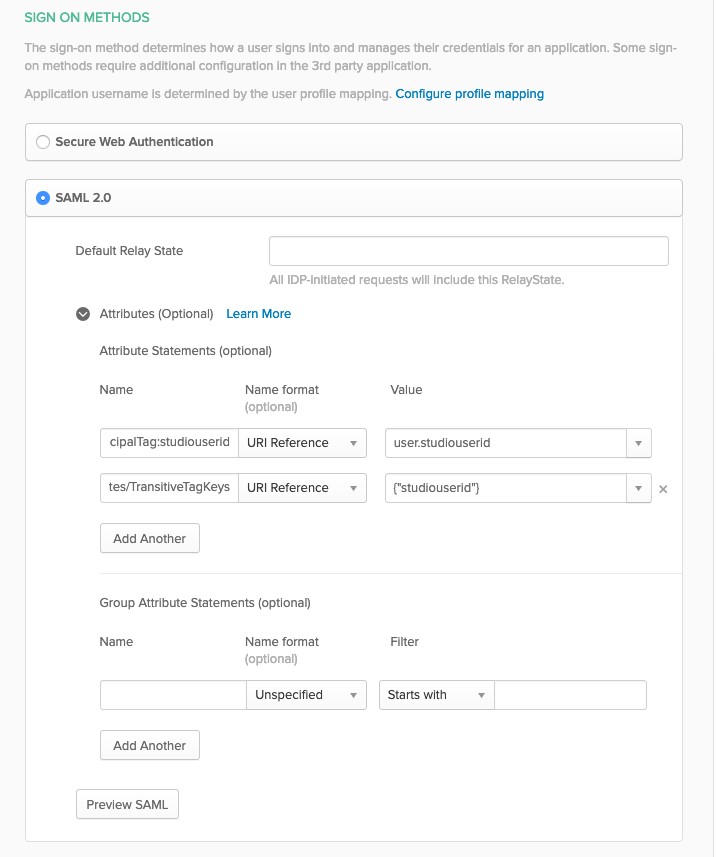
Example below shows how to add “studiouserid” attribute in OKTA. In OKTA’s SIGN ON METHODS screen, configure following SAML 2.0 attributes, as shown in the image below.

Attribute 1:
Name: https://aws.amazon.com/SAML/Attributes/PrincipalTag:studiouserid
Value: user.studiouserid

Attribute 2:
Name: https://aws.amazon.com/SAML/Attributes/TransitiveTagKeys
Value: {"studiouserid"}
The following screenshot shows the attributes on the Okta console.
Next, create the user profile using the following command. Use the user attribute value in the preceding step for the studiouserid tag value.
aws sagemaker create-user-profile --domain-id <domain id> --user-profile-name <unique profile name> --tags Key=studiouserid,Value=<user attribute value> --user-settings ExecutionRole=arn:aws:iam::<account id>:role/<Team Role Name>
IAM Identity Center
For instructions on assigning users in IAM Identity Center, see Onboarding Amazon SageMaker Studio with AWS SSO and Okta Universal Directory.
Update the Studio user profile to include the appropriate execution role that was created for the team that the user belongs to. See the following CLI command:
aws sagemaker update-user-profile --domain-id <domain id> --user-profile-name <user profile name> --user-settings ExecutionRole=arn:aws:iam::<account id>:role/<Team Role Name> --region us-west-2
Validating that only assigned Studio users can access their profiles
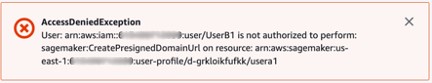
When a user tries to access a Studio profile that doesn’t have studiouserid tag value matching their user name, an AccessDeniedException error occurs. You can test this by copying the link for Launch Studio on the Amazon SageMaker console and accessing it when logged in as a different user. The following screenshot shows the error message.
Validating that only respective team members can access certain artifacts
In this step, we show how to configure Studio so that members of a given team can’t access artifacts that another team creates.
In our use case, a Team A user creates an experiment and tags that experiment with the team tag. This limits access to this experiment to Team A users only. See the following code:
import sys
!{sys.executable} -m pip install sagemaker
!{sys.executable} -m pip install sagemaker-experiments

import time
import sagemaker
from smexperiments.experiment import Experiment

demo_experiment = Experiment.create(experiment_name = "USERA1TEAMAEXPERIMENT1",
                                    description = "UserA1 experiment",
                                    tags = [{'Key': 'team', 'Value': 'TeamA'},
                                           {'Key': 'owner', 'Value': 'UserA1'}
])
If a user who is not in Team A tries to describe the experiment, Studio denies the action. See the following code:
#command run from TeamB User Studio Instance
import time
from smexperiments.experiment import Experiment
experiment_to_cleanup = Experiment.load(experiment_name="USERA1TEAMAEXPERIMENT1")
experiment_to_cleanup.describe()

[Client Error]
An error occurred (AccessDeniedException) when calling the DescribeExperiment operation: User: arn:aws:sts:: :<AWS Account ID>::assumed-role/ SageMakerStudioDeveloperTeamBRole/SageMaker is not authorized to perform: sagemaker:DescribeExperiment on resource: arn:aws:sagemaker:us-east-1:<AWS Account ID>:experiment/usera1teamaexperiment1
If a user in Team 1 other than the owner, i.e., User A1, tries to delete the experiment, Studio denies the action. See the following code:
#command run from TeamA User A2 Studio Instance
import time
from smexperiments.experiment import Experiment
experiment_to_cleanup = Experiment.load(experiment_name="USERA1TEAMAEXPERIMENT1")
experiment_to_cleanup.delete()

[Client Error]
An error occurred (AccessDeniedException) when calling the DeleteExperiment operation: User: arn:aws:sts:: :<AWS Account ID>::assumed-role/ SageMakerStudioDeveloperTeamARole/SageMaker is not authorized to perform: sagemaker:DeleteExperiment on resource: arn:aws:sagemaker:us-east-1:<AWS Account ID>:experiment/usera1teamaexperiment1
Conclusion
In this post, we demonstrated how to isolate Amazon SageMaker Studio access using the ABAC technique. We showcased three use cases: restricting access to a Studio profile to only the assigned user (using the studiouserid tag), restricting describe access to Studio artifacts to team members only, and restricting create, modify, update, delete access to Studio artifacts to resource owners only.. You can further customize policies by applying more tags to create more complex hierarchical controls.
Try out this solution for isolating resources by teams or groups in Amazon SageMaker Studio. For more information about using ABAC as an authorization strategy, see What is ABAC for AWS?
About the Authors
 Vikrant Kahlir is Senior Solutions Architect in the Solutions Architecture team. He works with AWS strategic customers product and engineering teams to help them with technology solutions using AWS services for Managed Databases, AI/ML, HPC, Autonomous Computing, and IoT.
 Rakesh Ramadas is an ISV Solution Architect at Amazon Web Services. His focus areas include AI/ML and Big Data.
 Rama Thamman is a Software Development Manager with the AI Platforms team, leading the ML Migrations team.
 Durga Sury is a ML Solutions Architect in the Amazon SageMaker Service SA team. She is passionate about making machine learning accessible to everyone. In her 3 years at AWS, she has helped set up AI/ML platforms for enterprise customers.